 #1
Tools for creating, managing, and analyzing fake login pages and email campaigns.
Kitploit recommended
 puliczek/cve-2021-21123-poc-google-chrome
🐱💻 👍 Google Chrome - File System Access API - vulnerabilities reported by Maciej Pulikowski | Total Bug Bounty Reward: $5.000 | CVE-2021-21123…
 openxp-research/cve-2022-2546
All-in-One WP Migration < 7.63 - Unauthenticated Reflected XSS + CSRF
 sanupl/cve-2021-46067
CVE-2021-46067 - In Vehicle Service Management System 1.0 an attacker can steal the cookies leading to Full Account Takeover.
 the-girl-who-lived/cve-2020-25498
Stored XSS via CSRF in Beetel 777VR1 Router
 mbadanoiu/cve-2020-13965
CVE-2020-13965: Cross-Site Scripting via Malicious XML Attachment in Roundcube Webmail
 oscarakaelvis/cve-2018-8062
Persistent XSS on Comtrend AR-5387un router
 mexeck88/csrf-via-stored-xss-for-privesc
Chamilo-LMS (v2.0) CVE-2025-26153
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
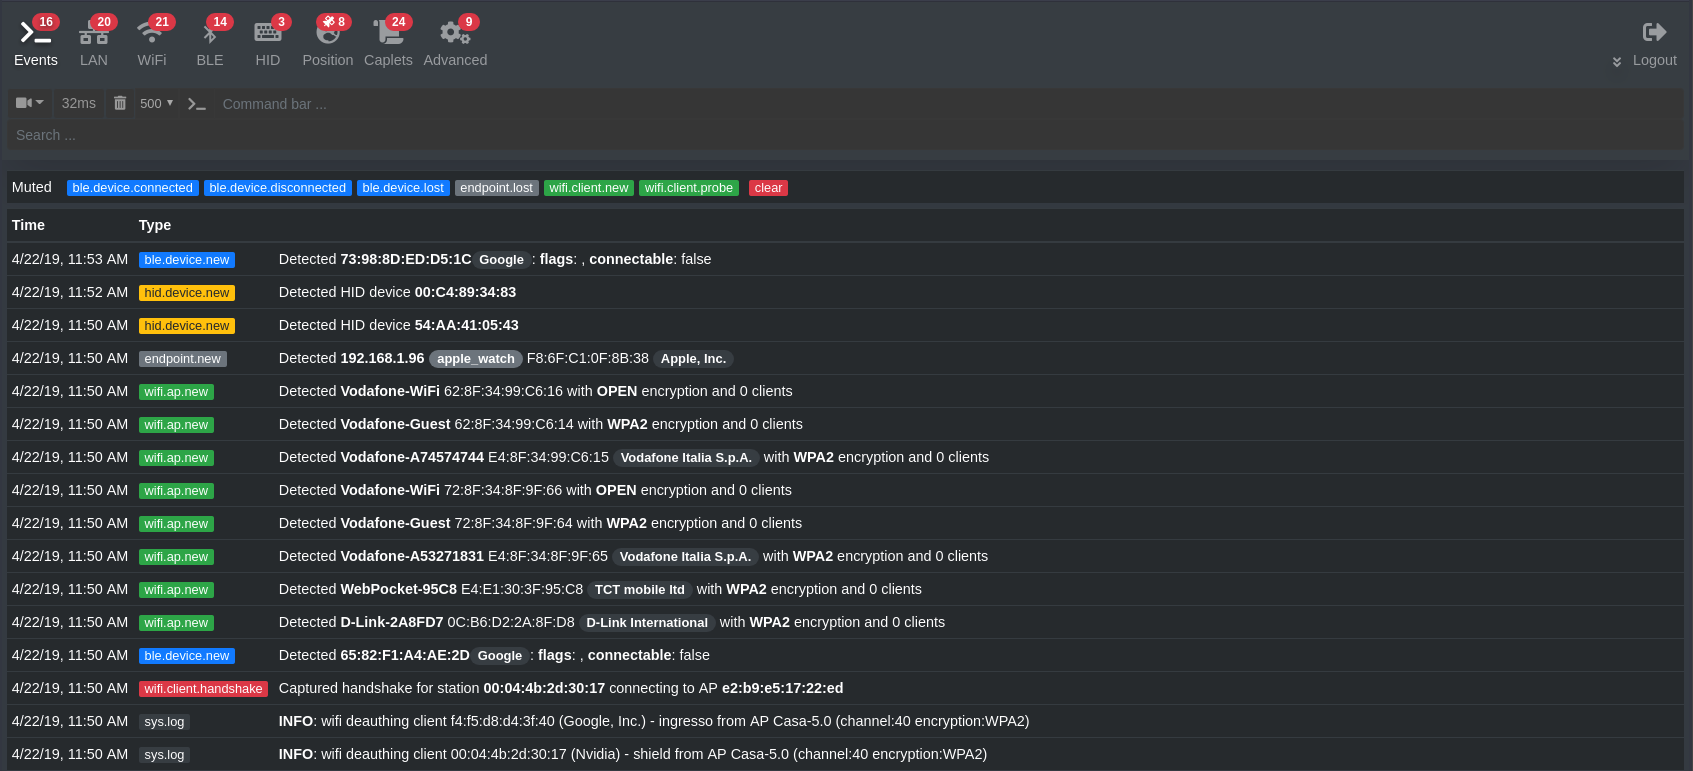 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
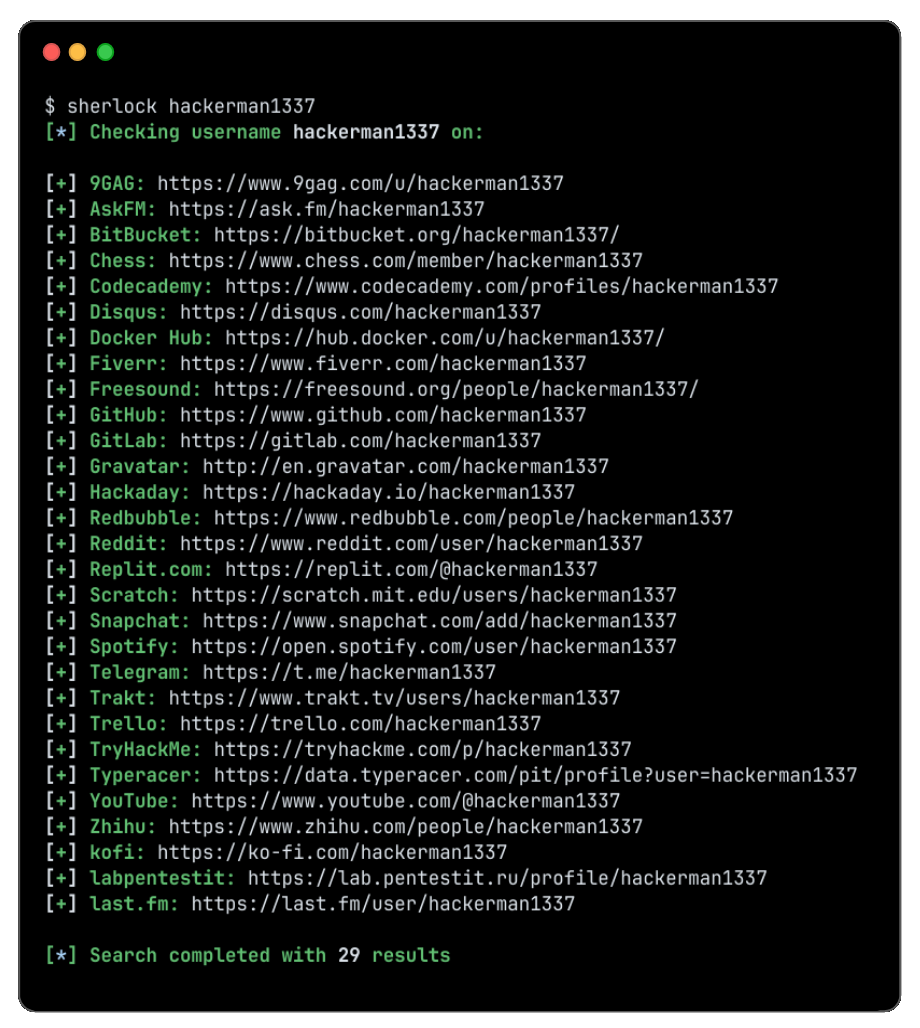 sherlock-project/sherlock
Hunt down social media accounts by username across social networks
 lewis-ricardo/amaranth-project
CVE-2025-8088 exploitation chain + Quasar C2 multi-stage payload delivery
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
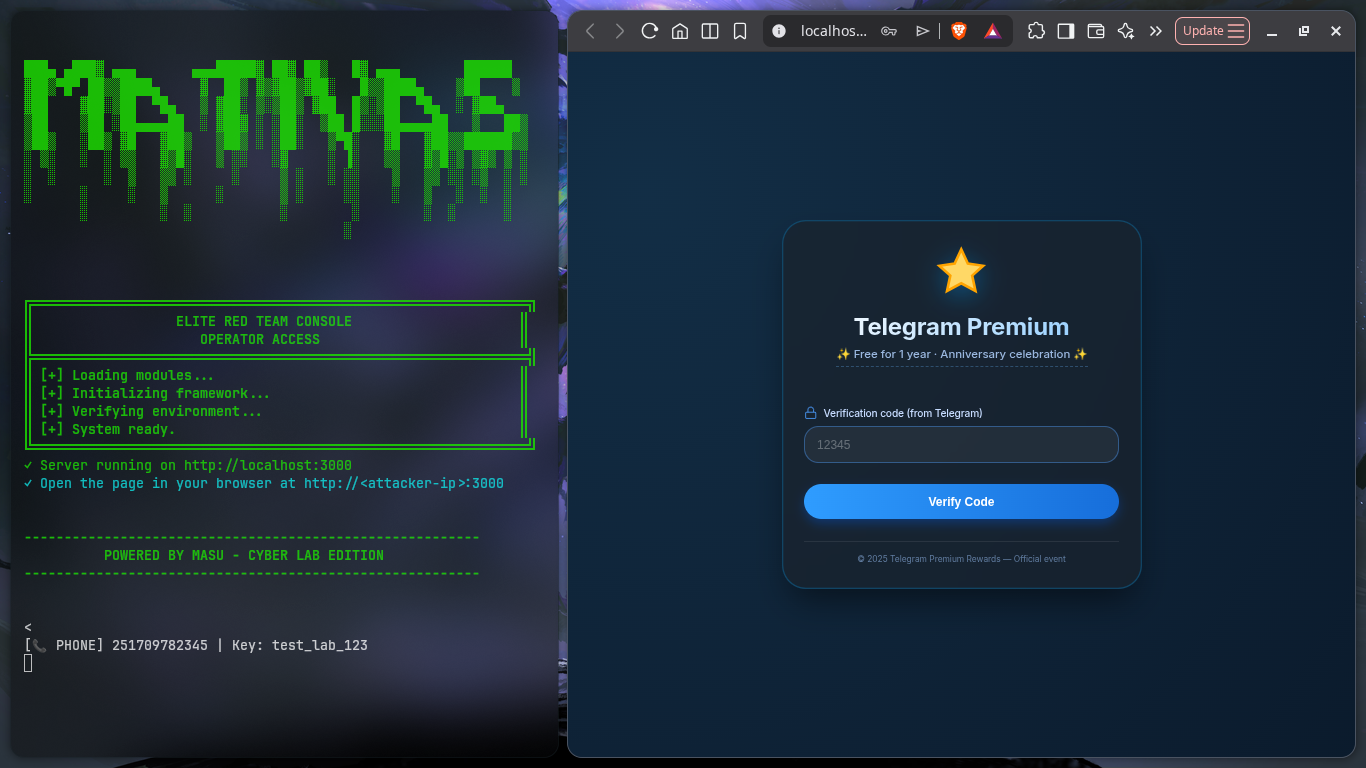 maty156/telegram-phish-simulator
Educational Telegram phishing simulation for cybersecurity training and awareness. Demonstrates credential harvesting via fake login pages in…
 malwaretech/exifsmugglingpoc
A Proof-of-Concept using Cache Smuggling + Exif data to passively download a second stage payload
 rootup/git-clean-filter
This is a proof-of-work for abusing git's clean filter against IDEs & Sublime.