
 #1
Tools for maintaining long-term access to compromised systems, even after reboots.
Kitploit recommended

 mertdas/redpersist
C# tool for establishing Windows persistence via multiple techniques including scheduled tasks, WMI events, startup folders, and registry hijacking,…
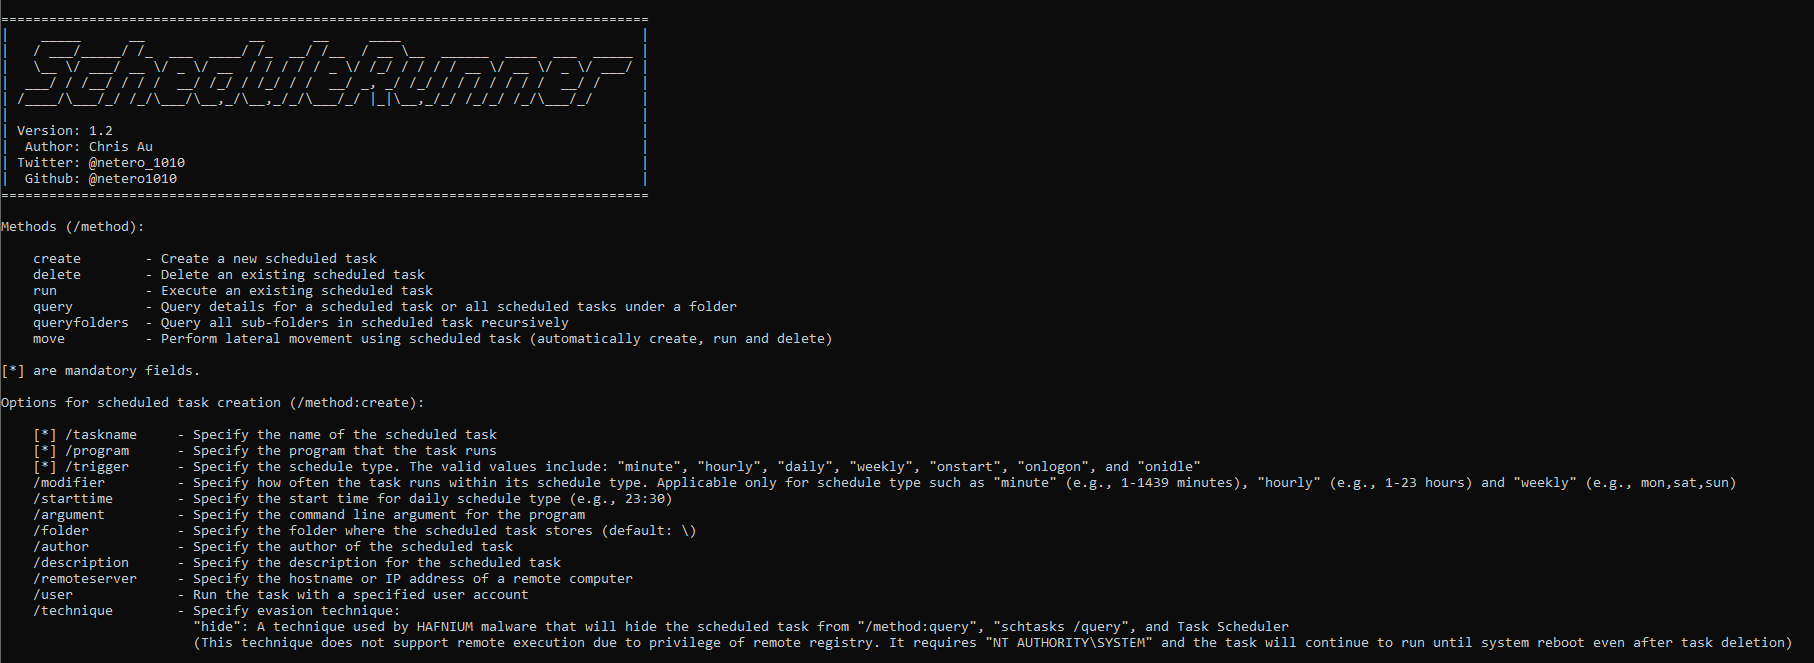 netero1010/schedulerunner
A C# tool with more flexibility to customize scheduled task for both persistence and lateral movement in red team operation
 m4sc3r4n0/spyrat
Python Remote Access Trojan
 trustedsec/specula
Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.
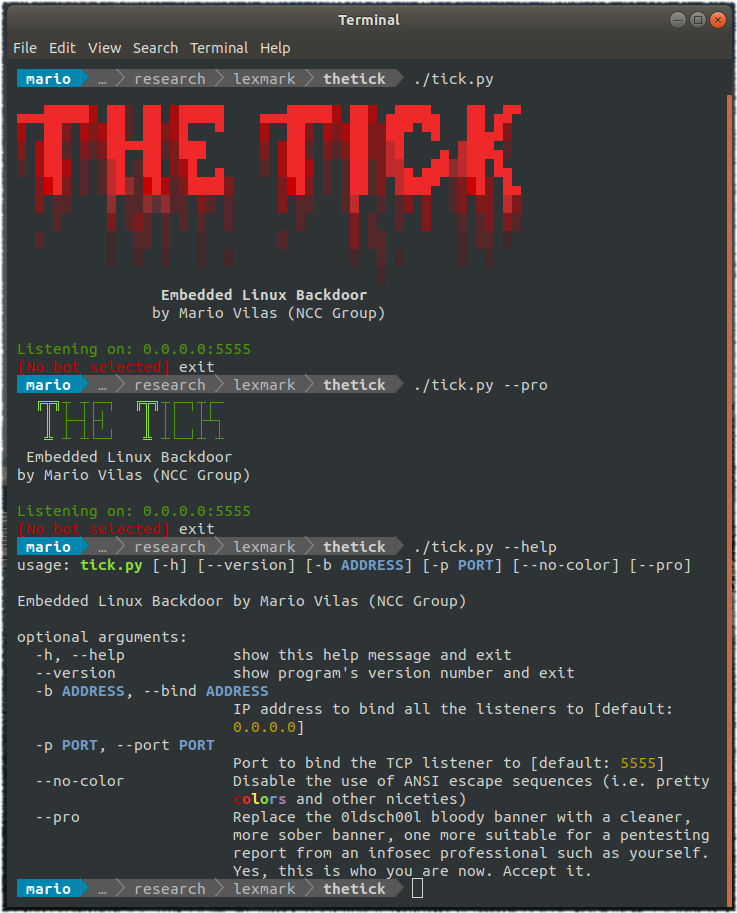 nccgroup/thetick
A simple embedded Linux backdoor.
 idov31/mrkaplan
PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
 n00py/norknork
Powershell Empire Persistence finder
 malwaretech/fakembr
TDL4 style rootkit to spoof read/write requests to master boot record
 alessandroz/pupy
Pupy is an opensource, multi-platform (Windows, Linux, OSX, Android), multi function RAT (Remote Administration Tool) mainly written in python. It…
 twosevenonet/edr-redir
Redirects EDR working folders using a Bind Filter (bindflt.sys) to bypass endpoint detection, corrupt EDR services, or replace with…
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 h4wkst3r/scmkit
Source Code Management Attack Toolkit
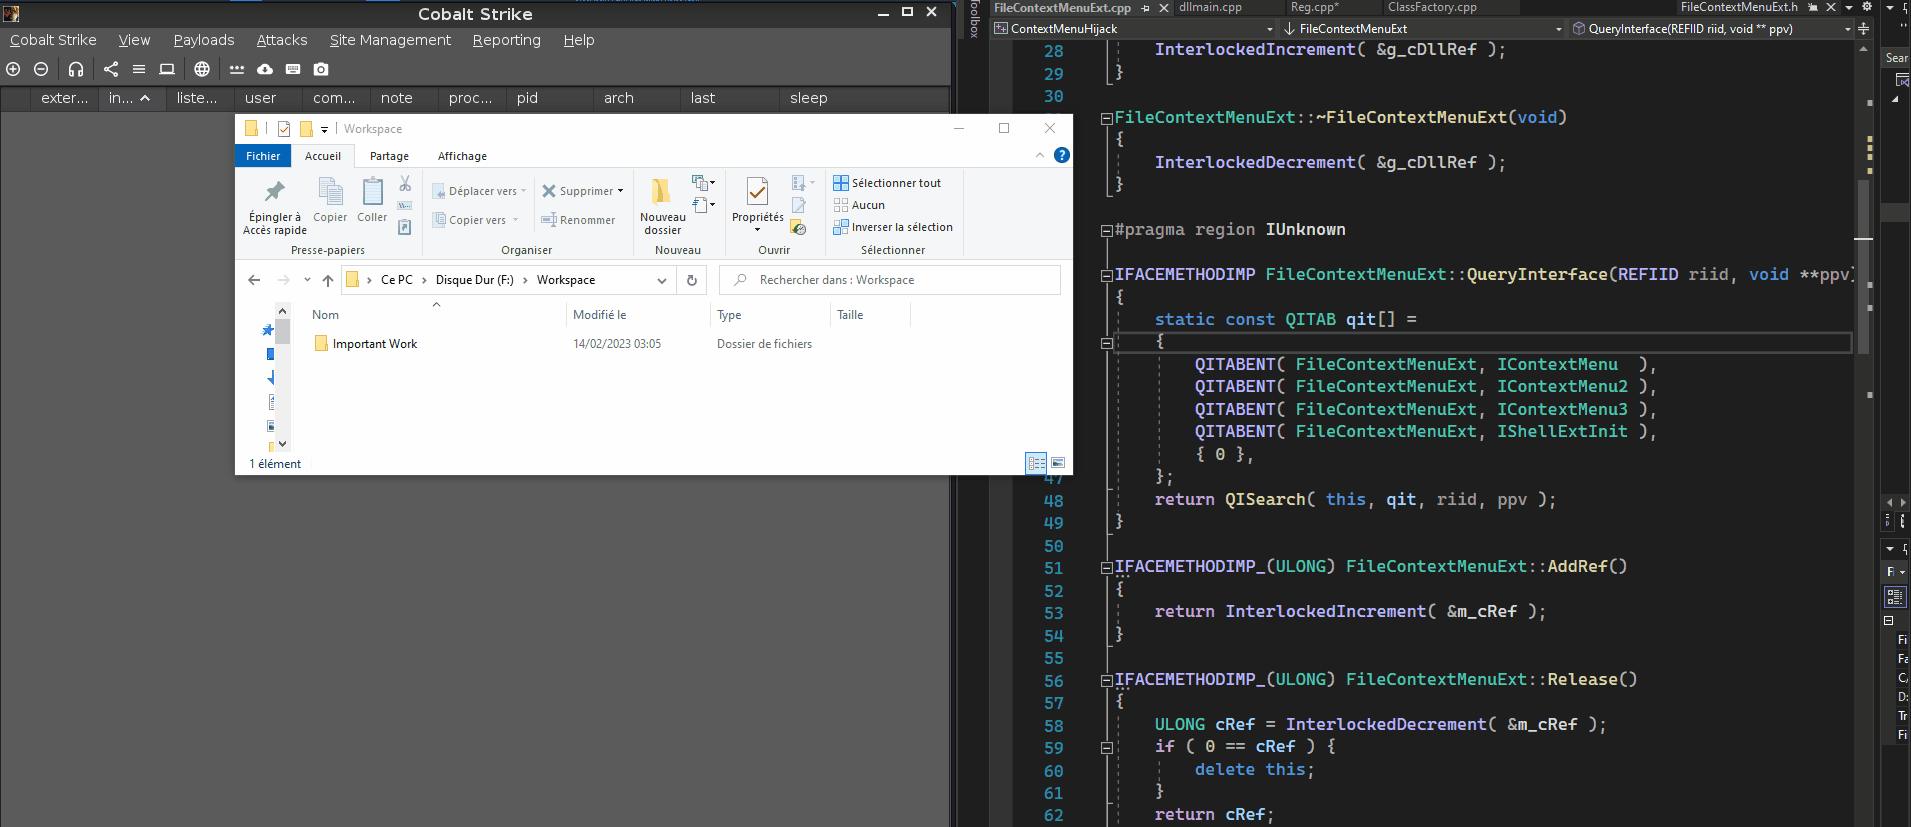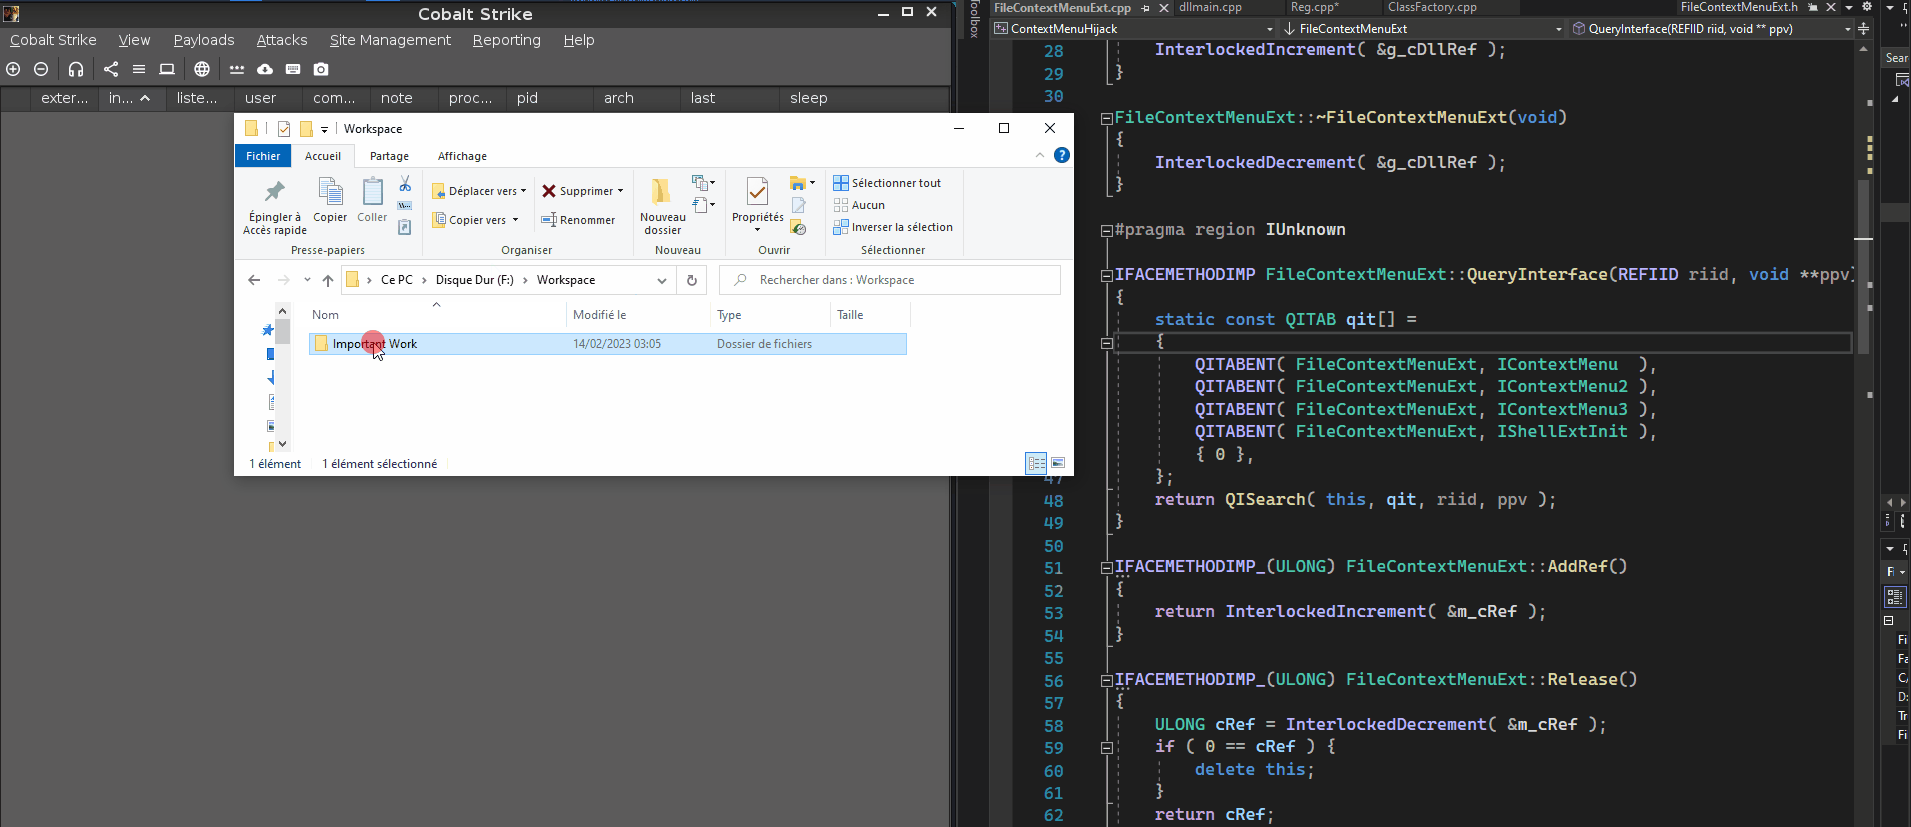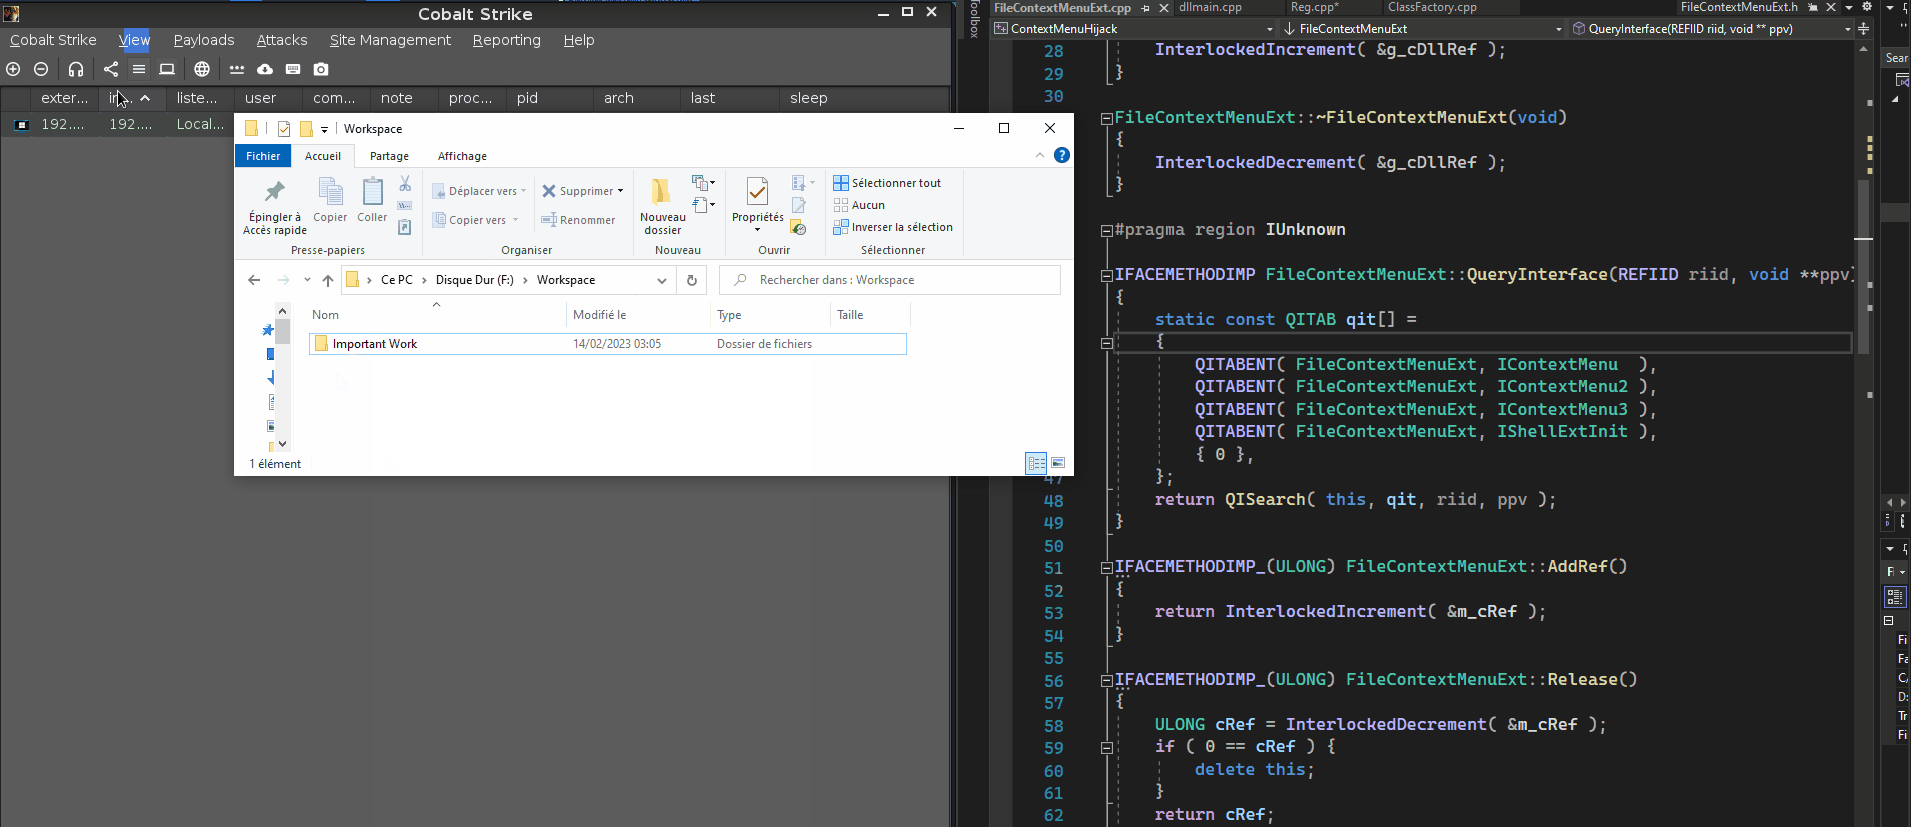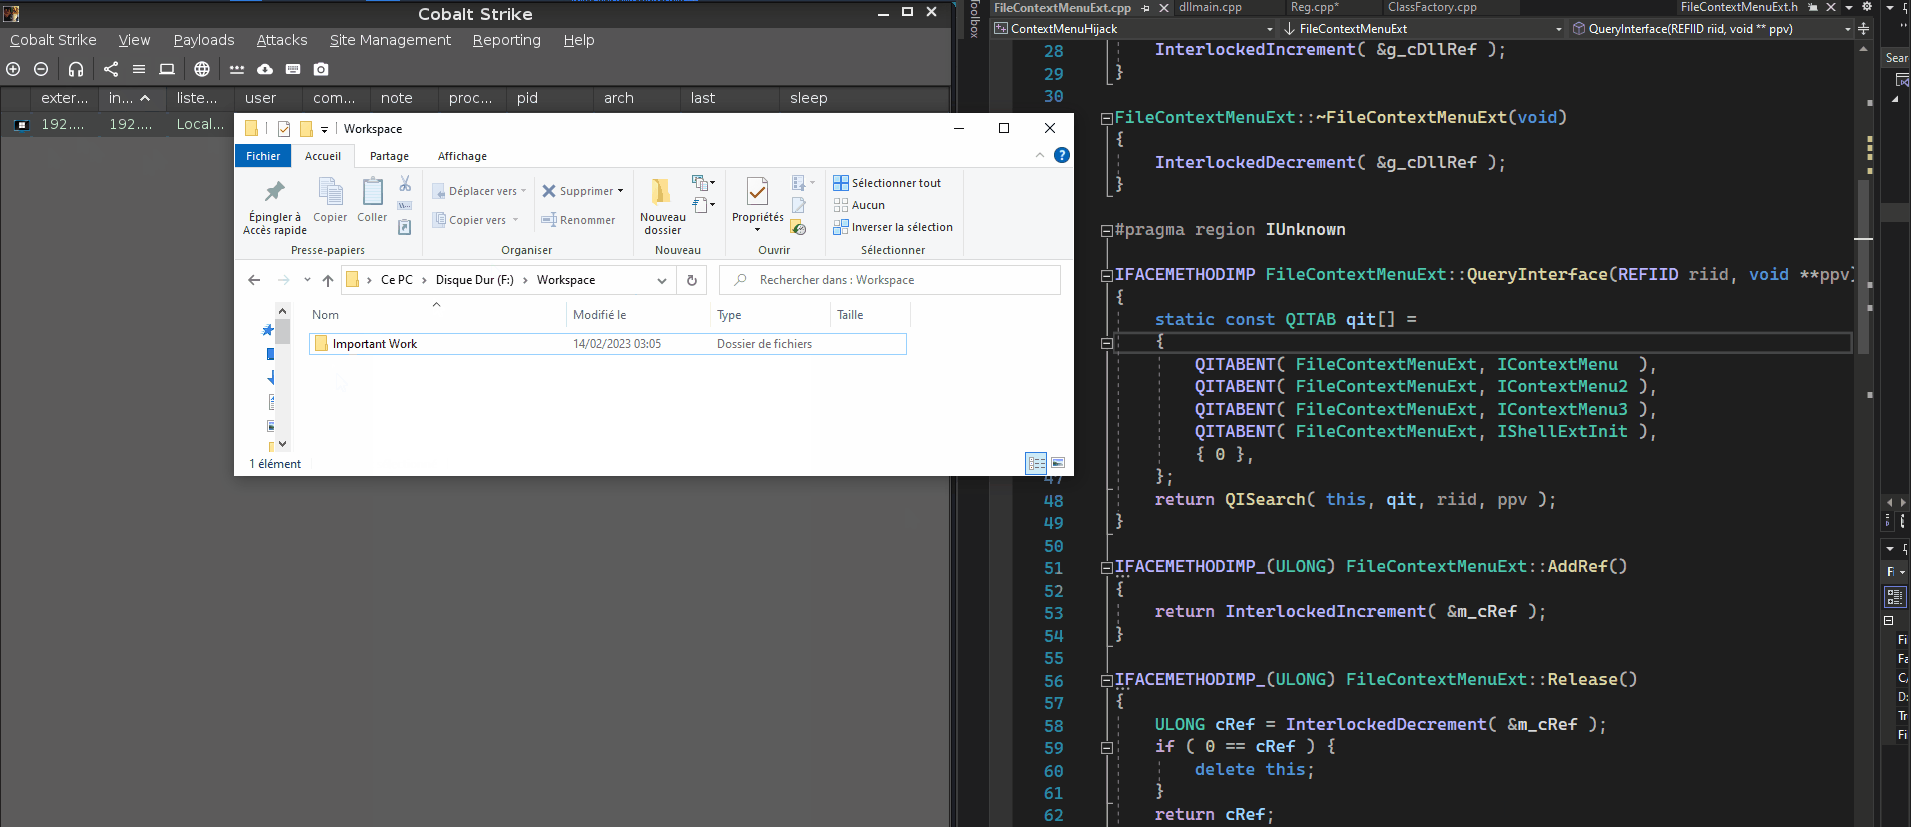 ristbs/contextmenuhijack
Execute a payload at each right click on a file/folder in the explorer menu for persistence
 nccgroup/gitpwnd
GitPwnd is a network penetration tool that lets you use a git repo for command and control of compromised machines
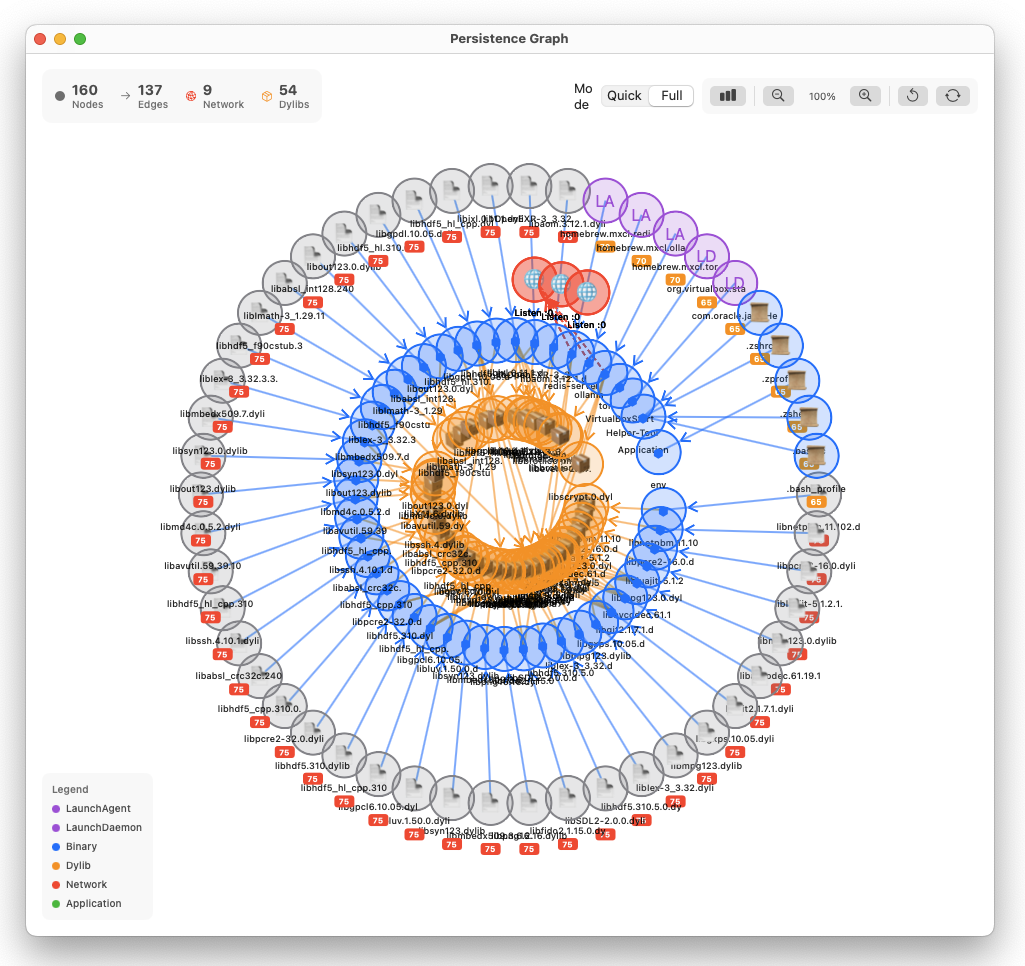 pinperepette/macpersistencechecker
macOS persistence mechanism scanner with code signature verification and timeline tracking.
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 ustayready/casperstager
PoC for persisting .NET payloads in Windows Notification Facility (WNF) state names using low-level Windows Kernel API calls.
 1135/1135-cobaltstrike-toolkit
about CobaltStrike








