
 #1
Penetration testing methodologies, frameworks, reporting, and automation tools.
Kitploit recommended

 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
 neex/phuip-fpizdam
Exploit for CVE-2019-11043
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
 bhavsec/reconspider
🔎 Most Advanced Open Source Intelligence (OSINT) Framework for scanning IP Address, Emails, Websites, Organizations.
 threatexpress/malleable-c2
Cobalt Strike Malleable C2 Design and Reference Guide
 calebstewart/pwncat
Post-exploitation platform automating enumeration, privilege escalation, persistence, and C2 operations via reverse/bind shells with cross-platform…
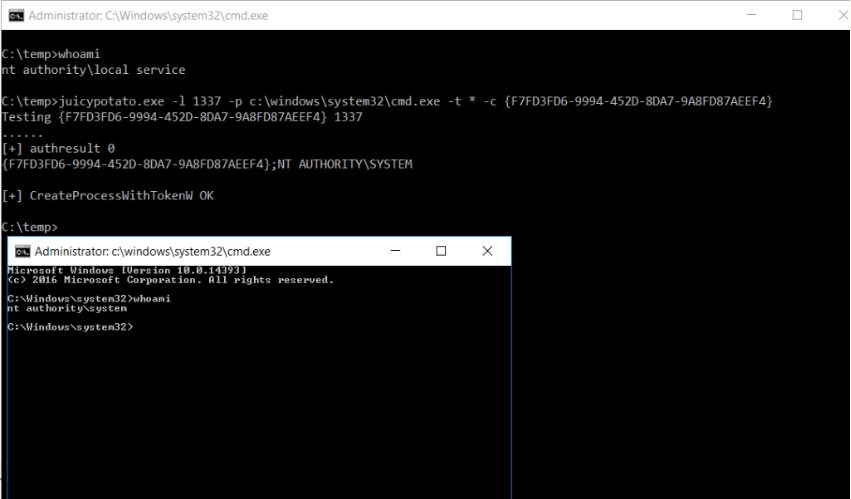 ohpe/juicy-potato
A sugared version of RottenPotatoNG, with a bit of juice, i.e. another Local Privilege Escalation tool, from a Windows Service Accounts to NT…
 hakluke/hakrevdns
Small, fast tool for performing reverse DNS lookups en masse.
 powershellempire/powertools
Collection of offensive PowerShell projects for reconnaissance, privilege escalation, and post-exploitation during penetration testing engagements.
 trimstray/htrace.sh
My simple Swiss Army knife for http/https troubleshooting and profiling.
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
 nextronsystems/aptsimulator
A toolset to make a system look as if it was the victim of an APT attack
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
 nfcgate/nfcgate
An NFC research toolkit application for Android
 0xsteph/pentest-ai-agents
Turn Claude Code into your offensive security research assistant. Specialized AI subagents for authorized penetration testing plan engagements,…
 rhinosecuritylabs/cves
Proof-of-Concept exploits for CVEs found by the team at Rhino Security Labs
 xalgord/xalgorix
Open-source AI penetration testing agent that exploit-verifies every finding. Autonomous 22-phase pentests of web apps & APIs with CVSS-scored PDF…








