
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended
 magicpipersec/wps-cve-2022-24934
PoC exploit server for CVE-2022-24934 that delivers a malicious payload via a fake WPS Update Server, targeting the wpsupdate.exe process for…
 r0lh/cve-2020-7247
Proof Of Concept Exploit for CVE-2020-7247 (Remote Execution on OpenSMTPD < 6.6.2
 bcdannyboy/cve-2023-50164
A scanning utility and PoC for CVE-2023-50164
 huowen/cve-2019-11043
Python exp for CVE-2019-11043
 haxorstars/cve-2025-54068
A tool designed to exploit CVE-2025-54068 and Remote Command Execution of the Livewire project.
 m0n1x90/cve-2026-41096
Proof-of-concept exploit for CVE-2026-41096: heap overflow in Windows DNS Client's DnsRawTruncateMessageForUdp(). Includes rogue DNS server and…
 lazarusreborn/docx-exploit-2021
This docx exploit uses res files inside Microsoft .docx file to execute malicious files. This exploit is related to CVE-2021-40444
 gutierre0x80/cve-2026-59827
Technical analysis and proof of concept for CVE-2026-59827, a critical unsafe Java deserialization vulnerability in Metabase leading to remote code…
 groppoxx/cve-2023-52076-poc
PoC exploit for CVE-2023-52076 - zip-slip path traversal in Atril/Xreader (MATE/Cinnamon) enabling arbitrary file write and RCE via crafted EPUB.…
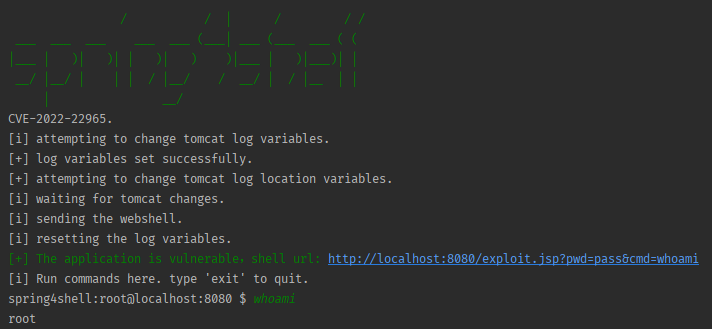 mariomamo/cve-2022-22965
Proof-of-concept exploit for CVE-2022-22965 (Spring4Shell) with a vulnerable Spring Boot application, Python exploit script, and Docker-based lab…
 lp008/cve-2019-10758
CVE-2019-10758
 geniuszly/cve-2022-45701
it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…
 eh-amish/cve-2026-64638-xss-to-shell-poc
Validates pre-authentication reflected XSS in WordPress, fingerprints vulnerable versions, checks payload reflection and JSONP, and generates…
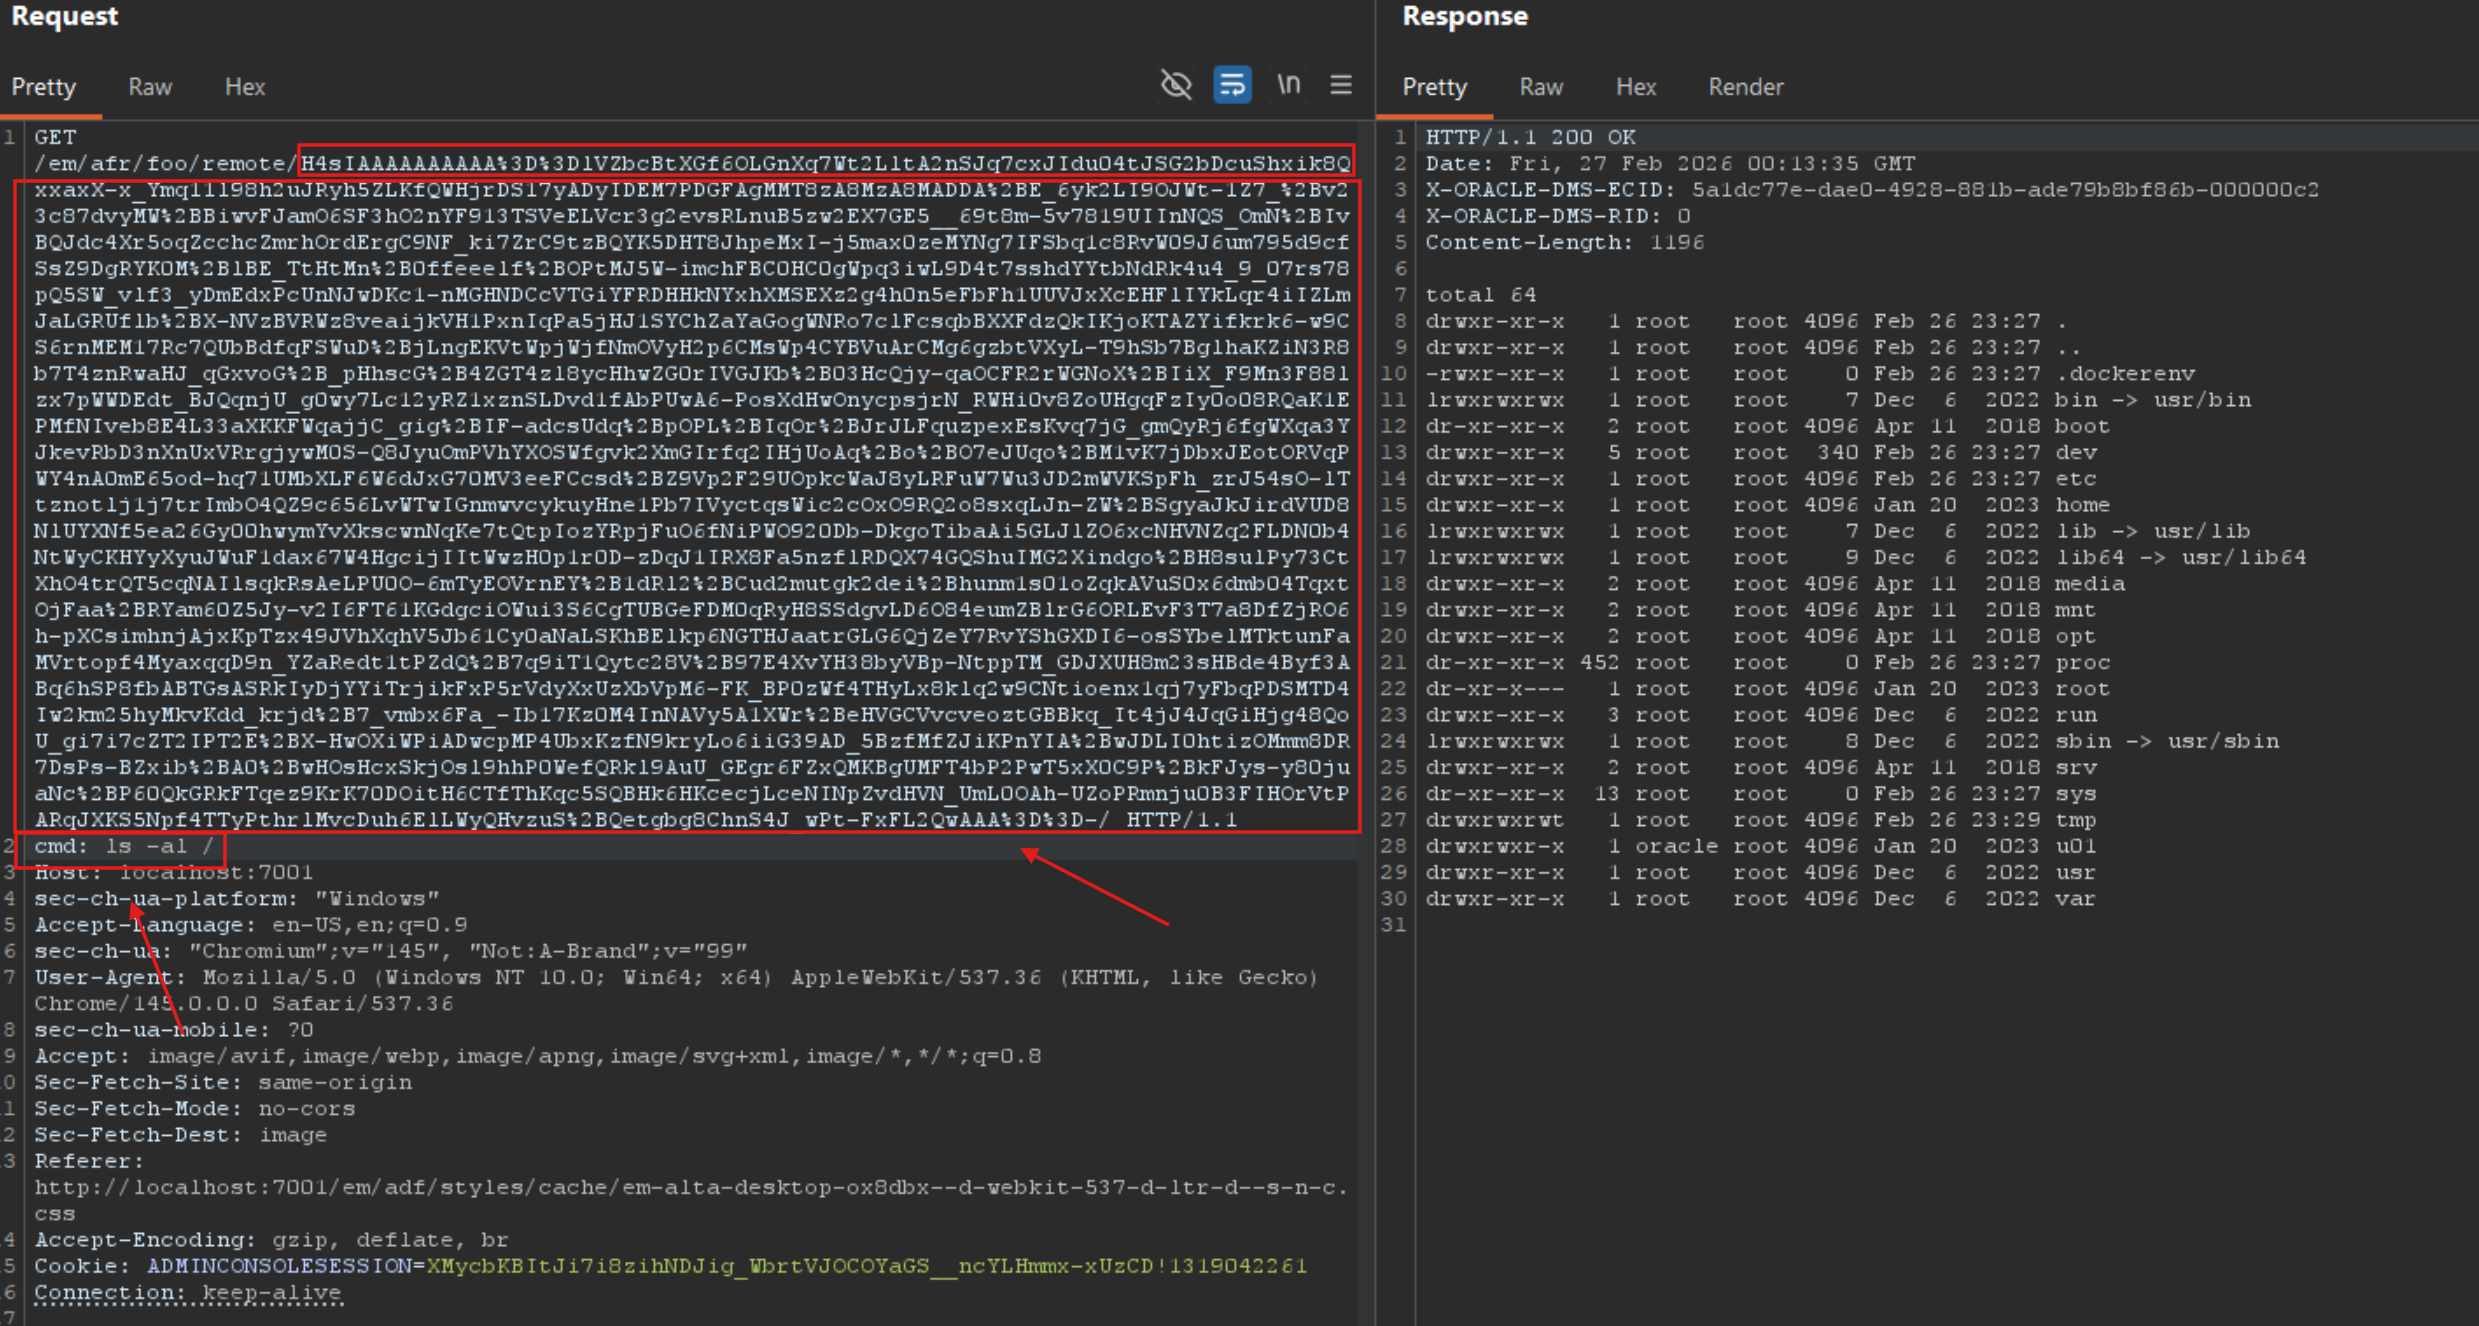 necr00/cve-2022-21445
Exploit for CVE-2022-21445 of Oracle Weblogic 12.2.1.X
 1337kid/cve-2023-38836
PoC exploit for file upload vulnerability in BoidCMS version <=2.0.0
 infinit3i/cve-2025-24893
PoC exploits CVE-2025-24893 , a remote code execution (RCE) vulnerability in XWiki caused by improper sandboxing in Groovy macros rendered…
 yucaerin/cve-2025-47577
WordPress TI WooCommerce Wishlist Plugin <= 2.9.2 Arbitrary File Upload
 andreiverse/shlol
do common hacking tasks with a simple menu








