
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended

 smallfunction/cve-2019-0708-poc
Working proof of concept for CVE-2019-0708, spawns remote shell.
 sh4den/cve-2022-46169
Cacti Unauthenticated Command Injection
 nxploited/cve-2025-8723
Cloudflare Image Resizing <= 1.5.6 | Unauthenticated Remote Code Execution
 rubikcuv5/cve-2023-30253
Dolibarr before 17.0.1 allows remote code execution by an authenticated user via an uppercase manipulation: <?PHP instead of <?php in injected data.
 mbanyamer/msc-eviltwin-local-privilege-escalation
CVE-2025-26633 (CVSS 7.8) – Zero-day MMC .msc EvilTwin LPE actively exploited by Water Gamayun APT. PoC creates local admin via malicious MSC file on…
 y3a/cve-2021-4034
Self-contained bash script that exploits CVE-2021-4034 (PwnKit) for local privilege escalation on vulnerable Linux systems.
 crackercat/cve-2021-44228-log4j-payloads
Collection of payloads for exploiting the Log4j remote code execution vulnerability (CVE-2021-44228), including JNDI injection strings and bypass…
 farinap5/a-xex
This project is part of a school work focusing on network security.
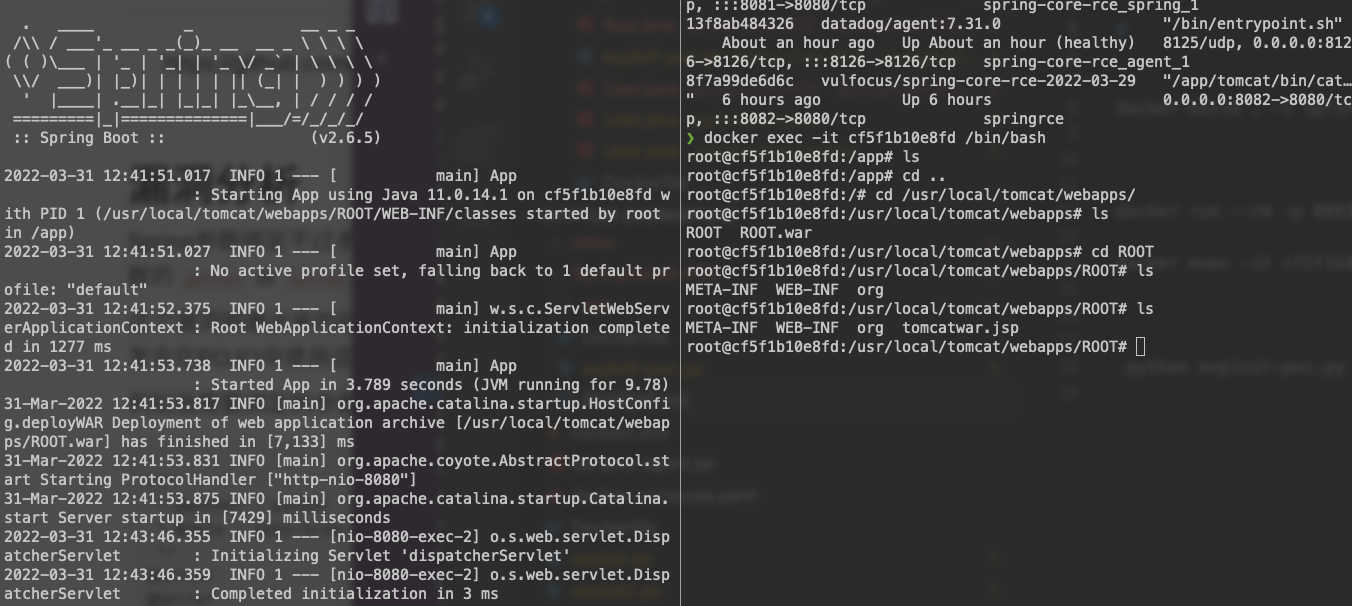 netcode/spring4shell-cve-2022-22965-poc
Another spring4shell (Spring core RCE) POC
 daniellowrie/cve-2024-36401-poc
Proof-of-Concept Exploit for CVE-2024-36401 GeoServer 2.25.1
 cyy95/cve-2019-0232-exp
Exploit for Apache Tomcat CGI Servlet command injection (CVE-2019-0232) enabling remote code execution via crafted HTTP requests on affected versions.
 sakura-501/cve-2020-24186-exploit
CVE-2020-24186的攻击脚本
 m00zh33/cve-2018-3191
Proof-of-concept exploit for CVE-2018-3191 targeting WebLogic Server via JNDI injection. Delivers a JAR payload to trigger remote code execution…
 u238/tomcat-cve_2025_24813
A playground to test the RCE exploit for tomcat CVE-2025-24813
 zephrfish/cve-2024-3400-canary
Have we not learnt from HoneyPoC?
 dragonked2/cve-2024-50379-poc
This repository contains a Python script designed to exploit CVE-2024-50379, a vulnerability that allows attackers to upload a JSP shell to a…
 charis3306/cve-2022-22963
spring cloud function 一键利用工具! by charis 博客https://charis3306.top/
 grampae/mqxss
Hooked browser communication over MQTT








