
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended
 corneacristian/log4j-cve-2021-44228-rce
Log4J (CVE-2021-44228) Exploit with Remote Command Execution (RCE)
 aeroot/wp-gdpr-compliance-plugin-exploit
Exploit of the privilege escalation vulnerability of the WordPress plugin "WP GDPR Compliance" by "Van Ons"…
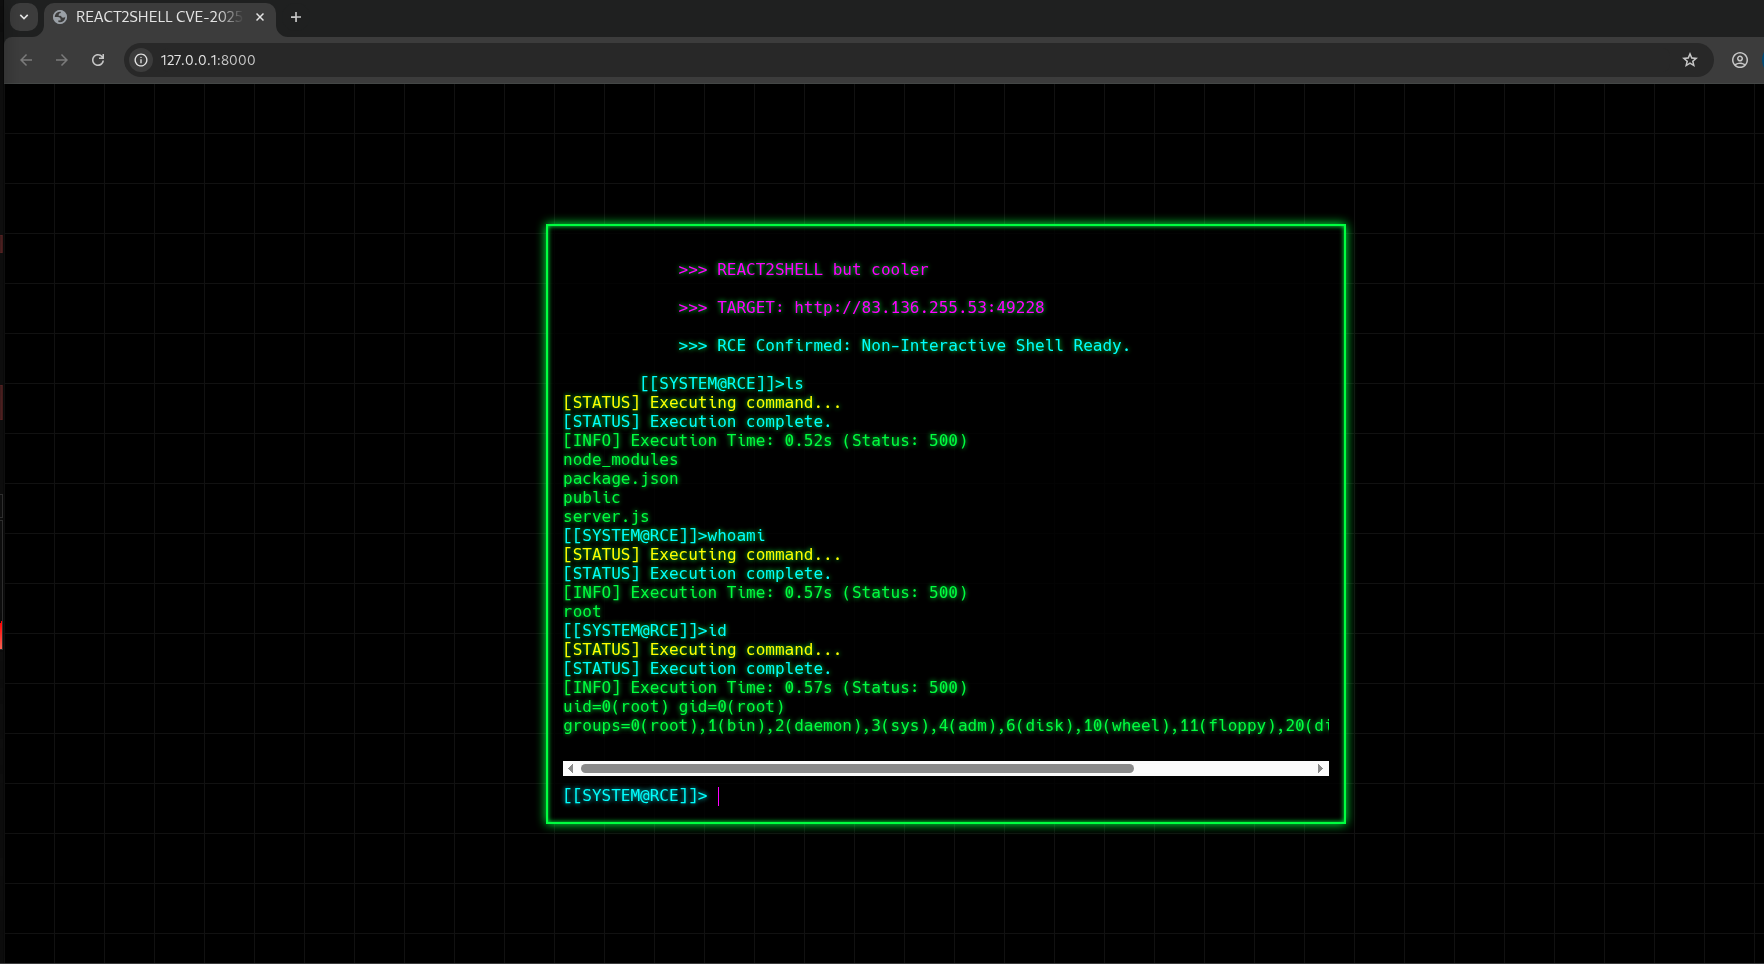 raivenlockdown/web-cli_rce_react2shell
WEB-CLI_RCE_React2Shell is an educational PoC exploit tool for CVE-2025-55182, a critical Prototype Pollution flaw in Next.js applications using…
 yuaneuro/cve-2021-2109_poc
weblogic CVE-2021-2109批量验证poc
 ireshchaminda1/android-privilege-escalation-remote-access-vulnerability-cve-2015-1805
AndroRAT is a capability that can be used to inject a root exploit as a silent installation to perform a malicious task on the device. This AndroRAT…
 geniuszly/cve-2024-24919
Proof-of-concept exploit script for CVE-2024-24919 that scans target URLs via HTTP POST requests, analyzes responses for unauthorized access or data…
 atithkhawas/autoblue
AutoBlue - Automated EternalBlue (CVE-2017-0144 / MS17-010) exploitation tool leveraging Nmap and Metasploit for ethical hacking, penetration…
 0xpthree/cve-2025-32433
Python exploit for CVE-2025-32433 targeting Erlang OTP SSH server. Sends crafted SSH packets to open a reverse shell and gain root access.
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 cirqueiradev/massexploit-cve-2024-4577
CVE-2024-4577 Mass Scanner & Exploit Tool
 9lyph/cve-2019-12836
CVE-2019-12836
 lennertdefauw/cve-2025-8088
WinRAR < 7.13 path traversal for persistency
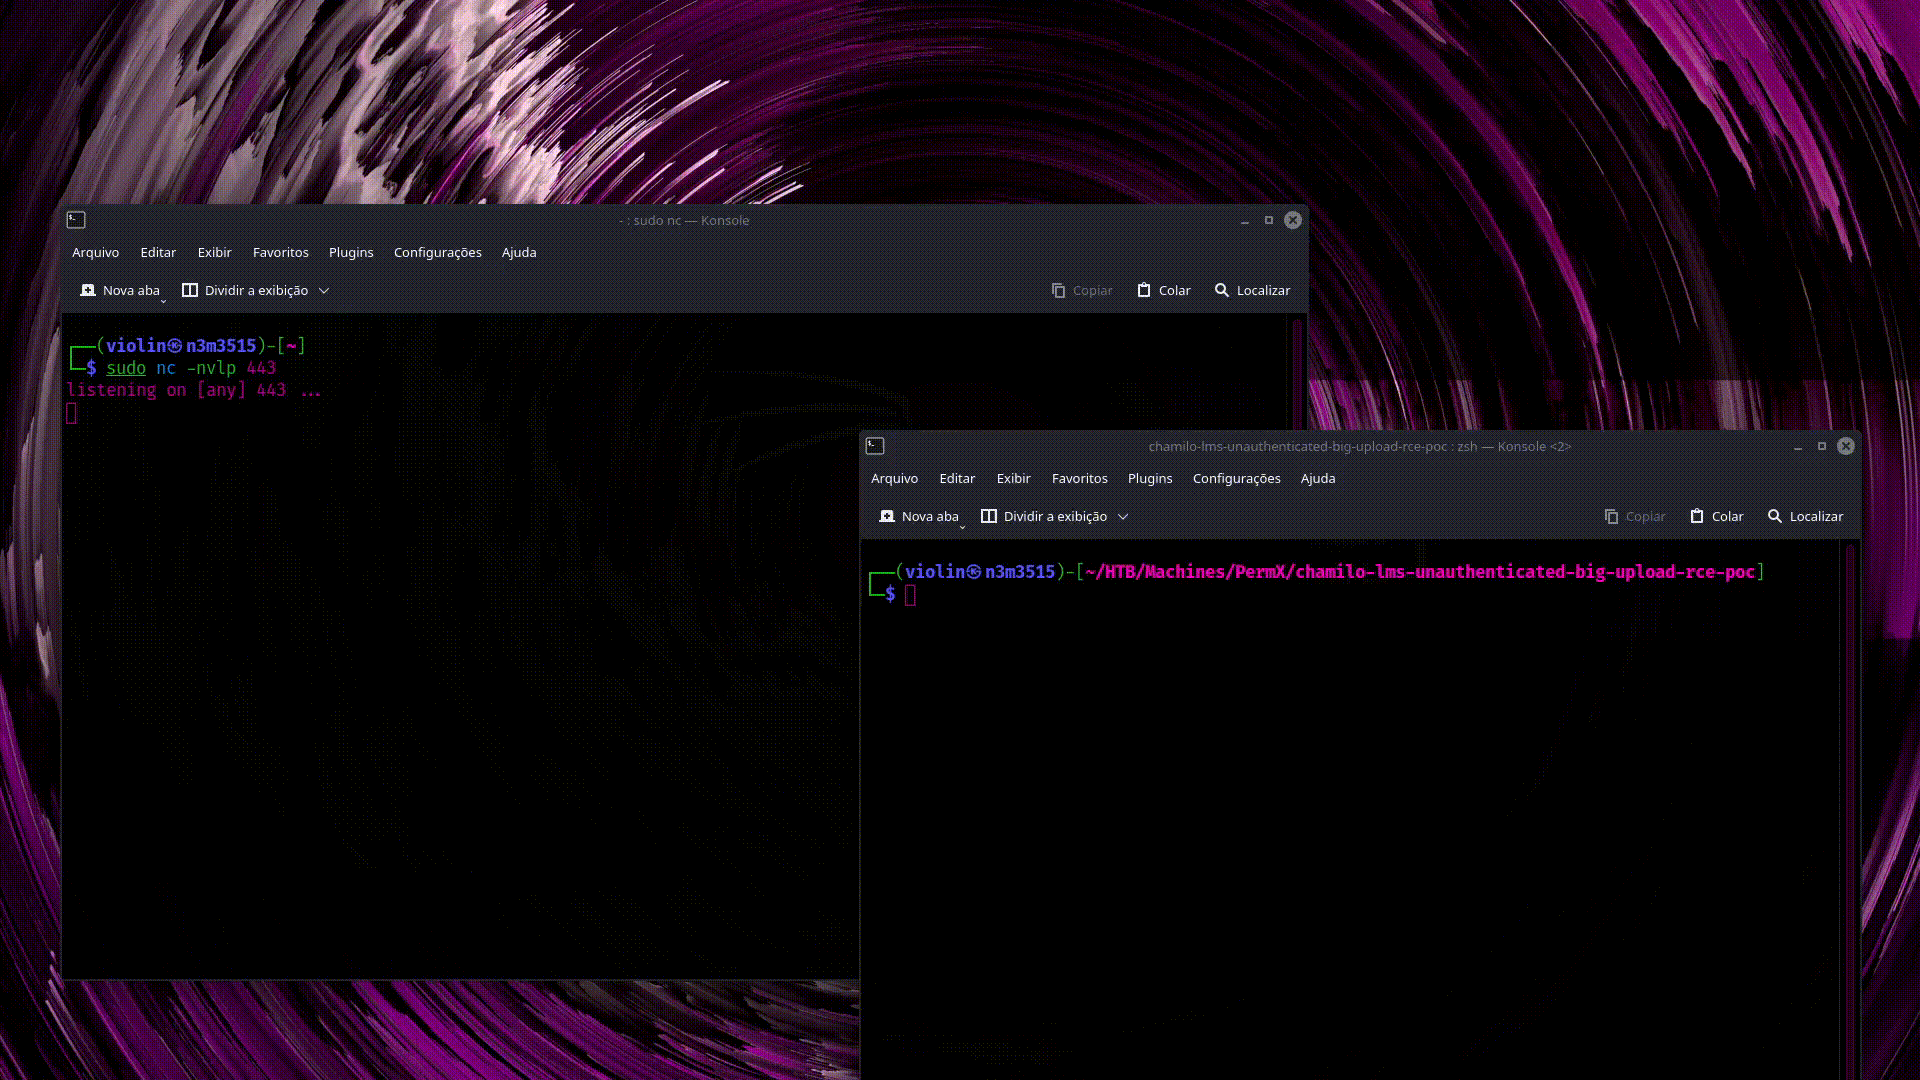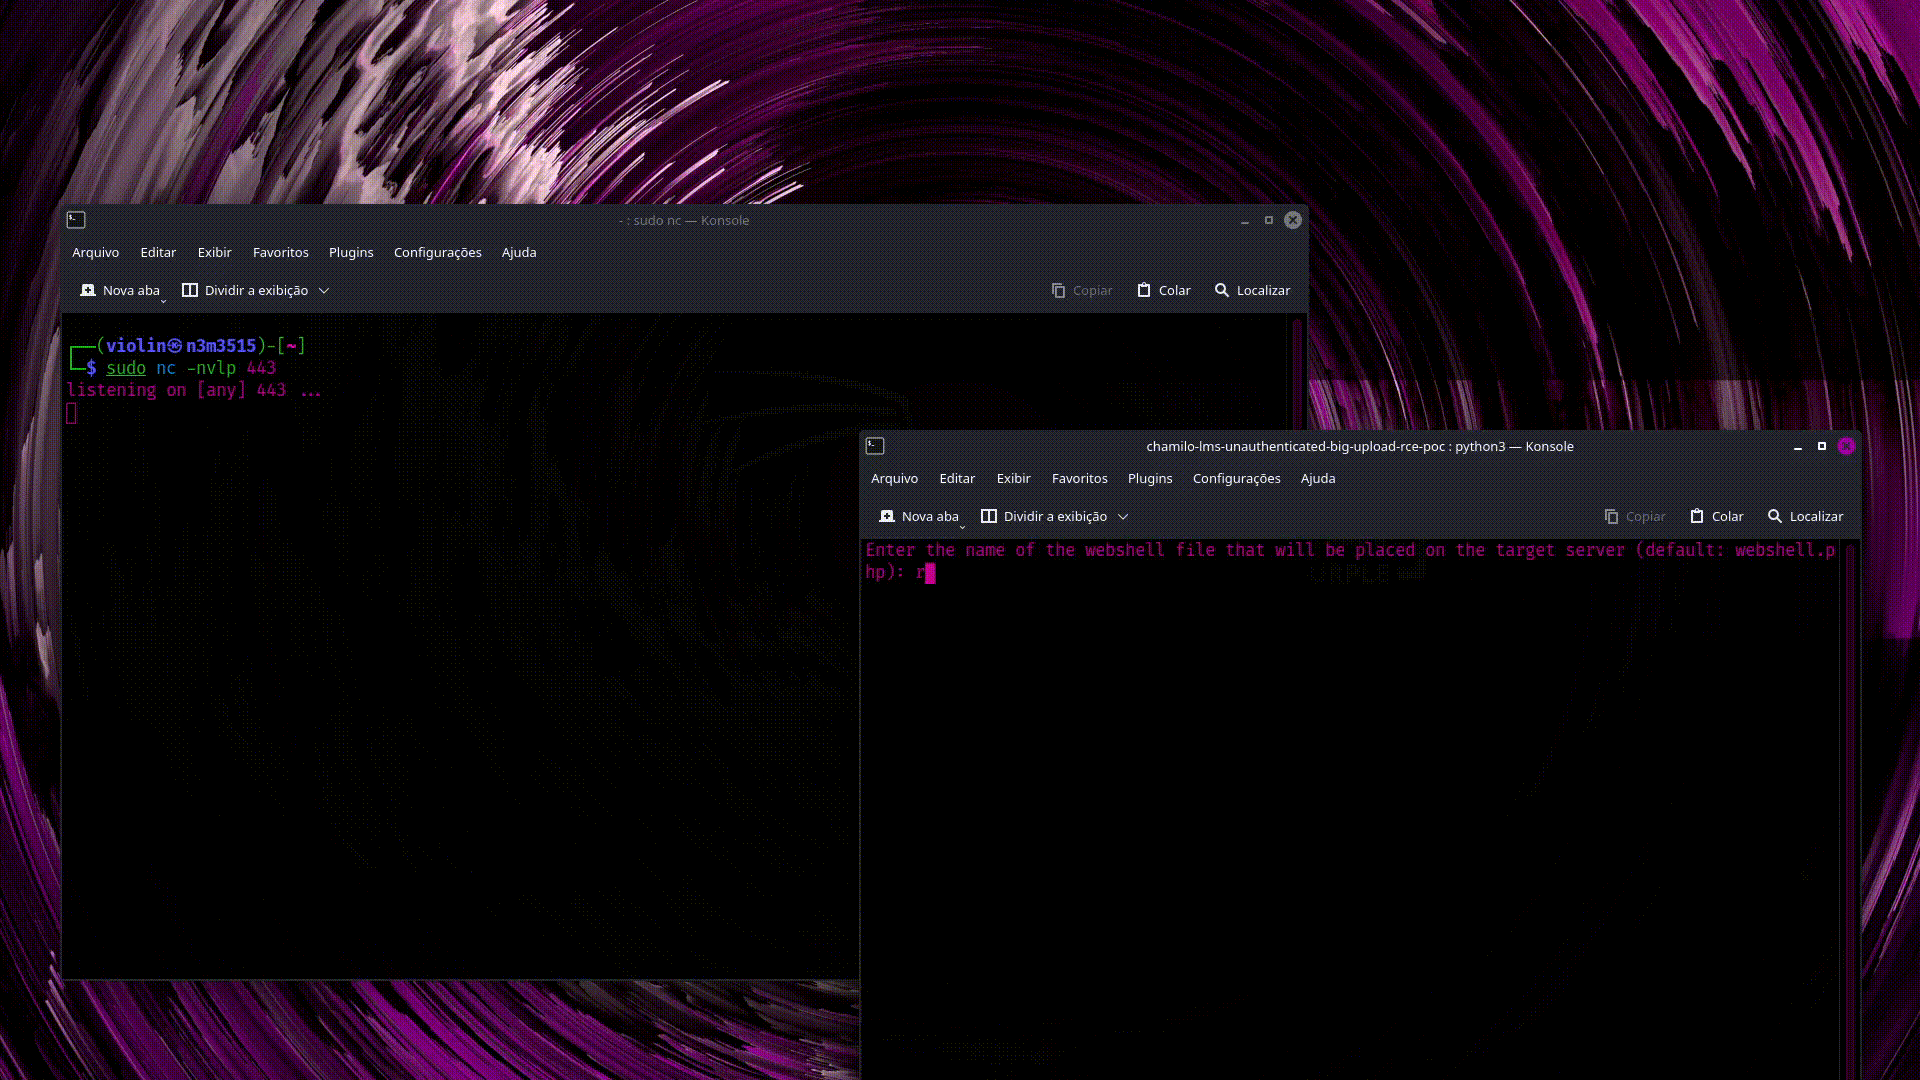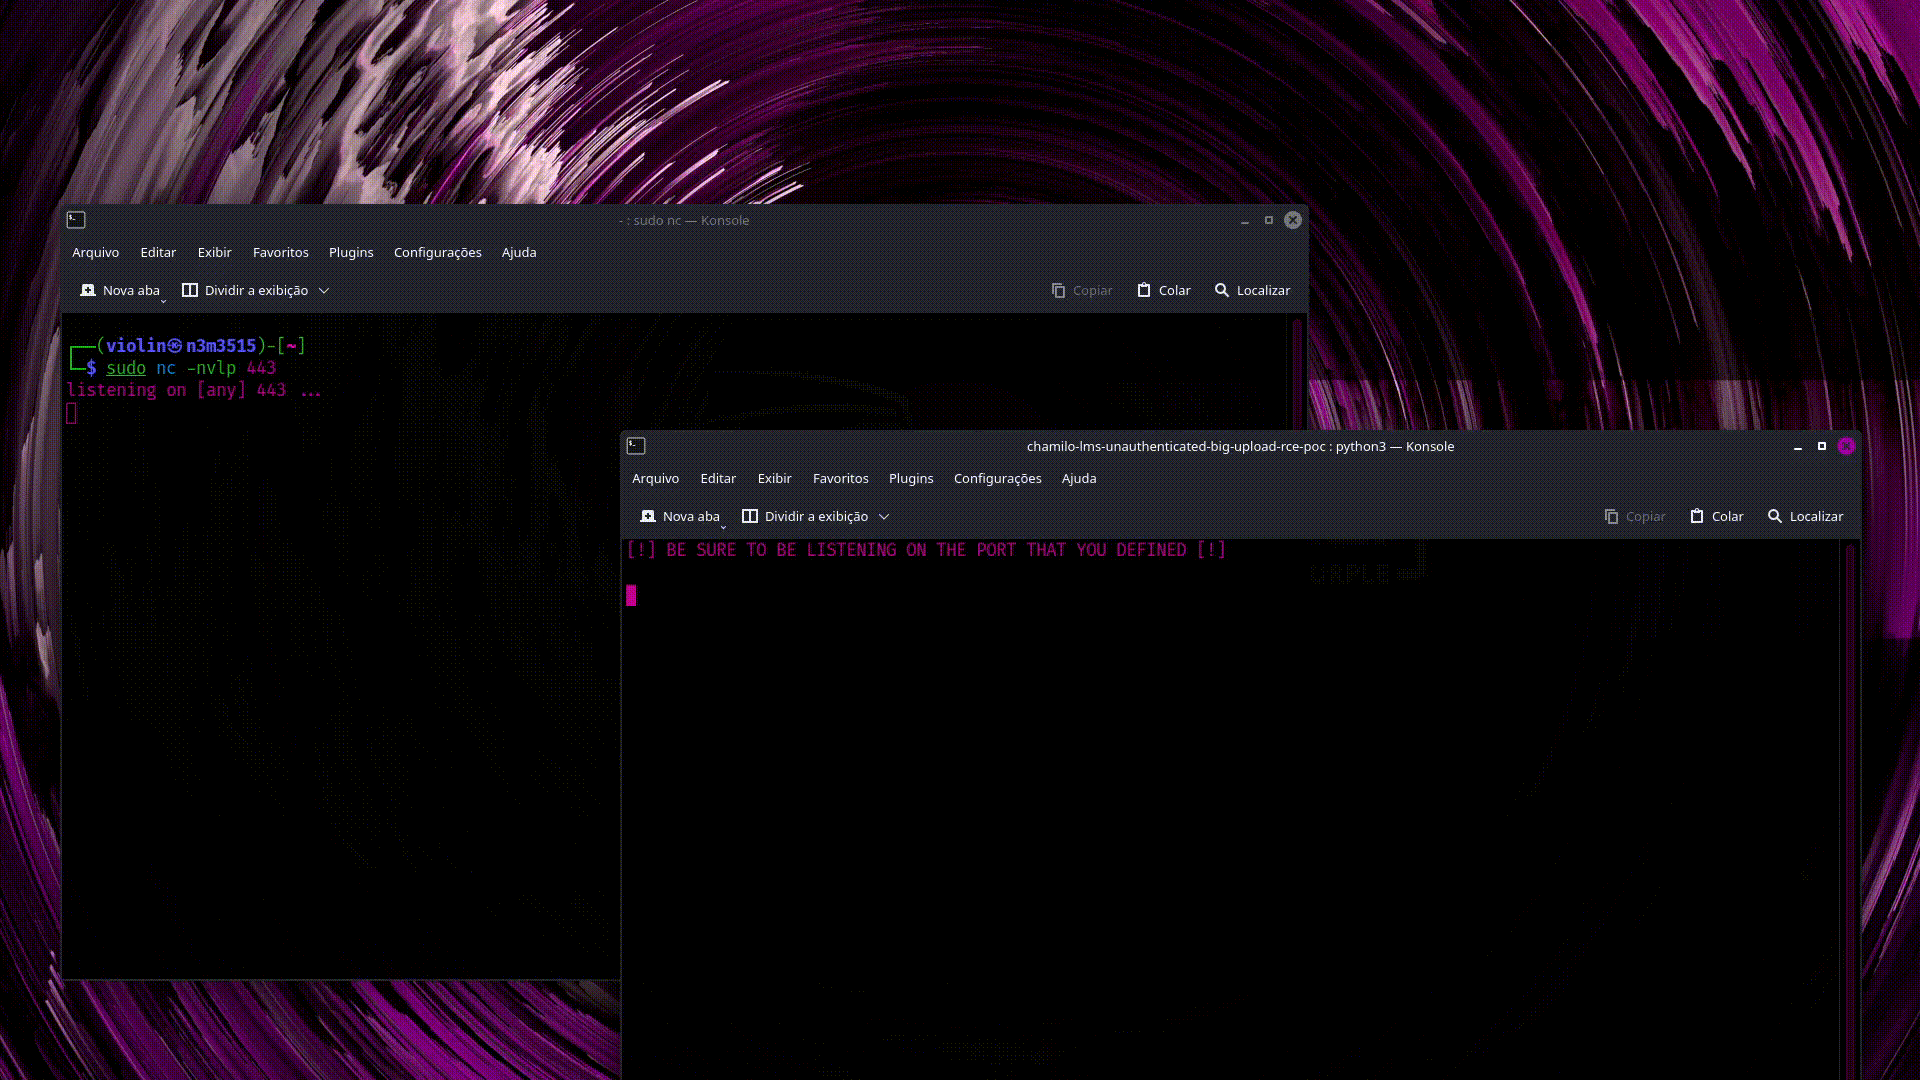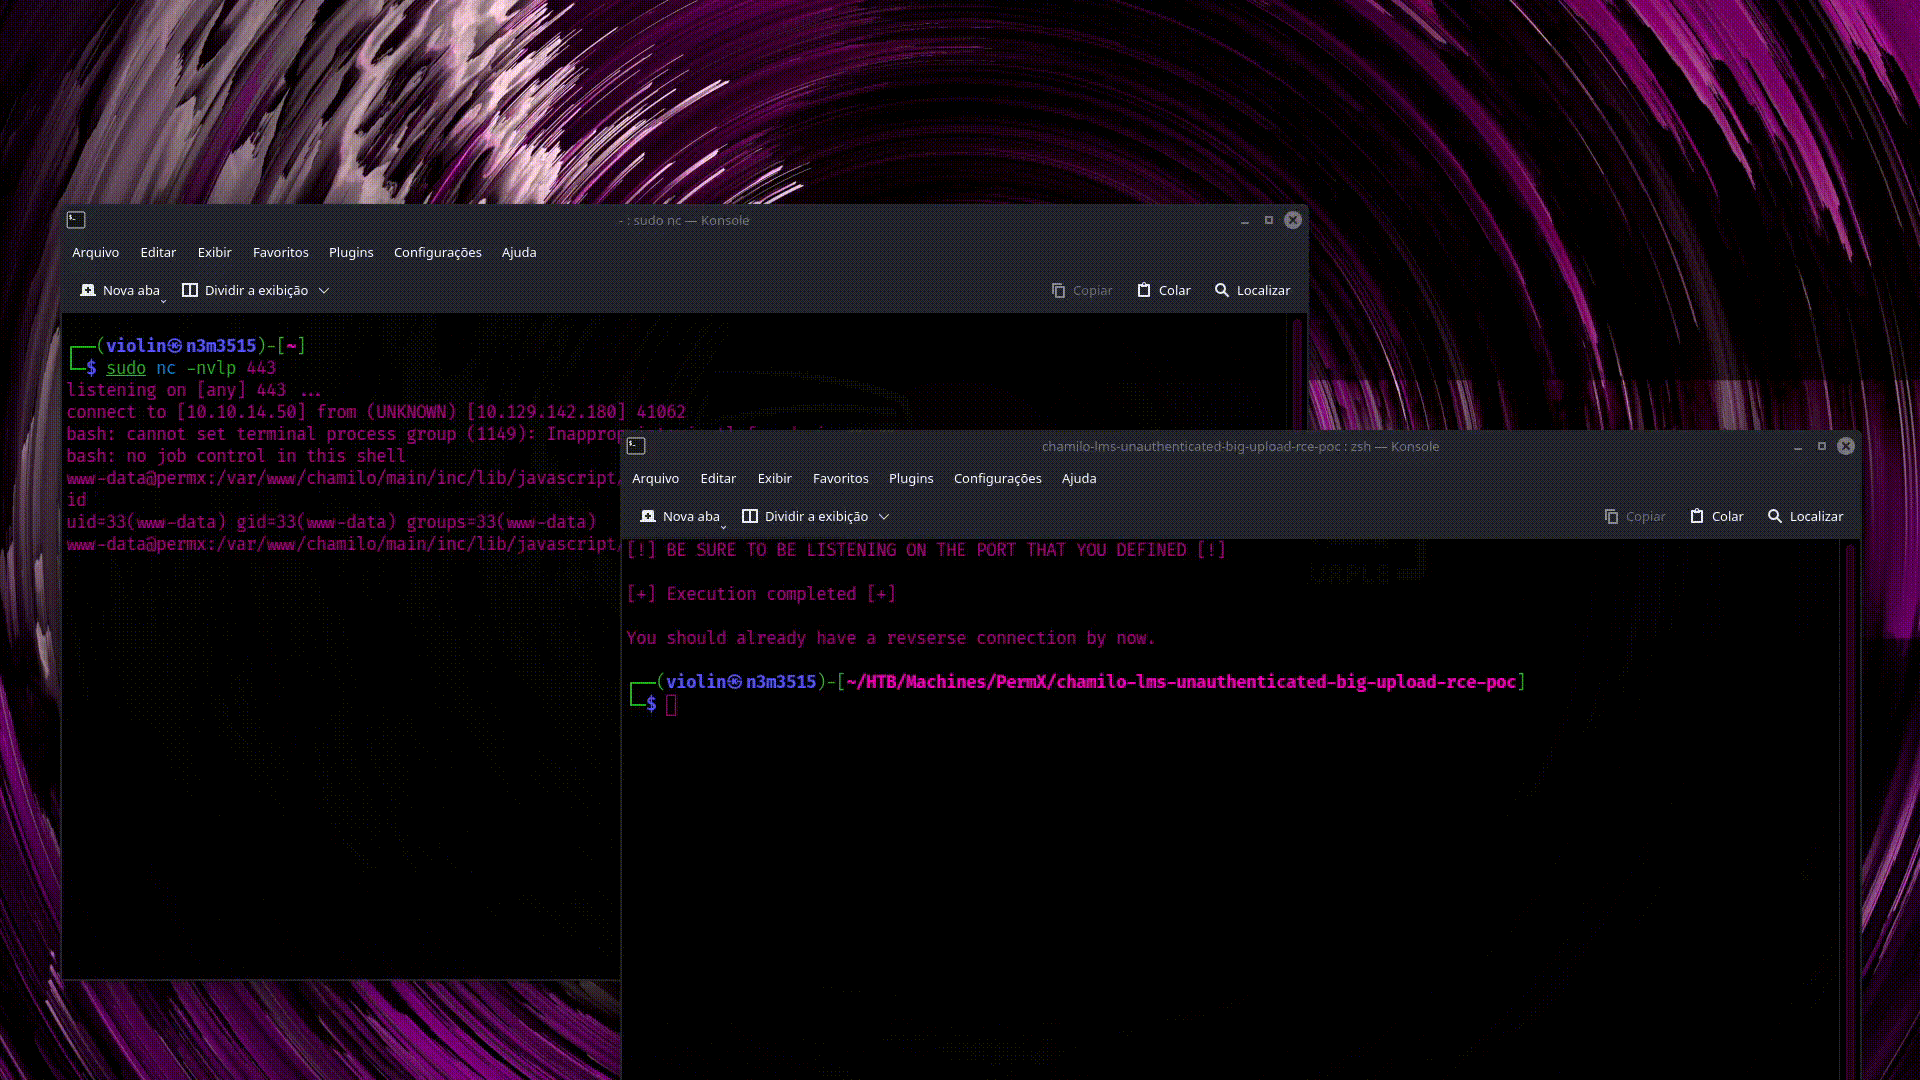 rai2en/cve-2023-4220-chamilo-lms
This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220
 noraj/openemr-rce
OpenEMR <= 5.0.1 - (Authenticated) Remote Code Execution
 lightsey/cve-2015-1592
Metasploit modules and payload generation files from my Houston Perl Mongers talk about this vulnerability.
 ardakocadoru/xss-cheatsheet
Comprehensive XSS reference covering reflected, stored, DOM and blind payloads, filter bypass, WAF evasion, CSP bypass, mXSS, and real-world CVE case…
 stuub/sglang-0.5.9-rce
Proof of Concept exploitation of CVE-2026-5760 - RCE in SGLang 0.5.9 via malicious GGUF
 pankass/cve-2024-37032_cve-2024-45436
CVE-2024-45436








