
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended
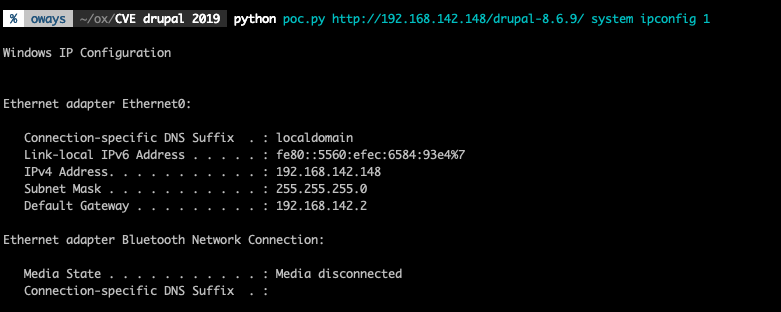
 oways/cve-2019-6340
CVE-2019-6340 POC Drupal rce
 amitr12/cybersec
Single-file HTML cheat sheet for red teamers and pentesters with auto-injecting attacker/target variables, OS-aware reverse shell generator, and…
 stephenbradshaw/cve-2022-46164-poc
Basic POC exploit for CVE-2022-46164
 kobs0n/cve-2019-11581
Proof-of-concept exploit for CVE-2019-11581 targeting Atlassian Jira Server and Data Center. Demonstrates unauthenticated remote code execution via…
 subc0ol/apache-struts2-rce-exploit-v2-cve-2017-5638
Automated remote code execution exploit for Apache Struts2 (CVE-2017-5638) with auto-exploitation capabilities for penetration testing and…
 crusoe112/dirtypipepython
A Python-based DirtyPipe (CVE-2022-0847) POC to pop a root shell
 dor-tumarkin/cve-2019-17564-fastjson-gadget
Basic code for creating the Alibaba FastJson + Spring gadget chain, as used to exploit Apache Dubbo in CVE-2019-17564 - more information available at…
 misterxid/watchguard_cve-2022-26318
Proof-of-concept exploit for CVE-2022-26318, a remote code execution vulnerability in WatchGuard XTM and FireWare OS, delivering a reverse shell via…
 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 faisalfs10x/log4j2-cve-2021-44228-revshell
Log4j2 CVE-2021-44228 revshell, ofc it suck!!
 qtranspose/cve-2020-7247-exploit
OpenSMTPD 6.4.0 - 6.6.1 Remote Code Execution PoC exploit
 ma1dong/vcenter_rce
漏洞利用,Vmware vCenter 6.5-7.0 RCE(CVE-2021-21972),上传冰蝎3,getshell
 mansk1es/caboom
A malicious .cab creation tool for CVE-2021-40444
 garvitv14/cve-2025-59287
Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…
 watchtowrlabs/watchtowr-vs-watchguard-cve-2025-9242
Python-based detection artifact generator and exploit for WatchGuard Fireware OS CVE-2025-9242, an unauthenticated IKEv2 out-of-bounds write…
 shauntdergrigorian/cve-2006-6184
This is a python-based standalone exploit for CVE-2006-6184. This exploit triggers a stack-based buffer overflows in Allied Telesyn TFTP Server…
 thel1ghtvn/cve-2022-30333-poc
Proof-of-concept exploit for CVE-2022-30333, a path traversal vulnerability in unrar used by Zimbra, demonstrating arbitrary file write via crafted…
 jasperla/cve-2017-9101
Authenticated remote code execution exploit for PlaySMS 1.4 via CSV phonebook upload. Provides single-command and interactive shell modes for…








