
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended

 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!
 ycdxsb/cve-2020-0668
Make CVE-2020-0668 exploit work for version < win10 v1903 and version >= win10 v1903
 r3kind1e/log4shell-obfuscated-payloads-generator
Generate primary obfuscated or secondary obfuscated CVE-2021-44228 or CVE-2021-45046 payloads to evade WAF detection.
 murataydemir/cve-2017-9822
[CVE-2017-9822] DotNetNuke Cookie Deserialization Remote Code Execution (RCE)
 amoloht/cve-2022-33891
「💥」CVE-2022-33891 - Apache Spark Command Injection
 securelayer7/wordpresshell
Pre-auth RCE PoC for CVE-2026-63030 / CVE-2026-60137 (WordPress core)

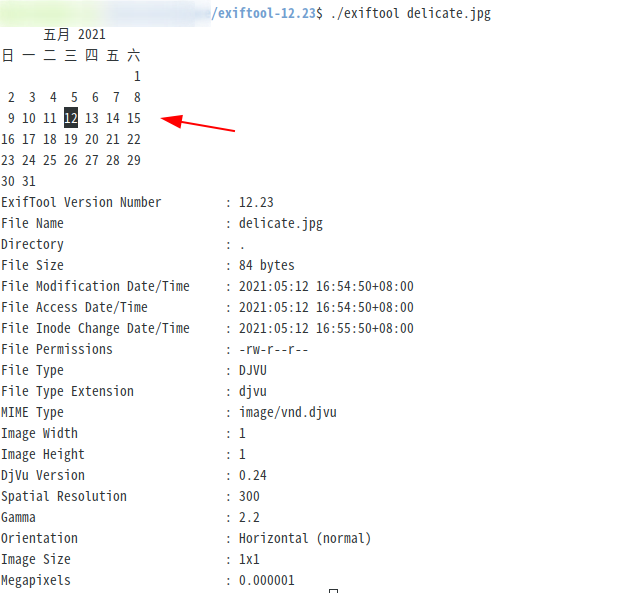 se162xg/cve-2021-22204
exiftool arbitrary code execution vulnerability
 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
 noxtal/follina
All about CVE-2022-30190, aka follina, that is a RCE vulnerability that affects Microsoft Support Diagnostic Tools (MSDT) on Office apps such as…
 eversinc33/nimnightmare
CVE-2021-1675 LPE PoC in Nim (PrintNightmare Local Privilege Escalation)
 leviticus-triage/cerebro-red-v2
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
 vulnbe/burpsuite-copy-as-xmlhttprequest
BurpSuite extension that converts HTTP requests into JavaScript XMLHttpRequest code for streamlined XSS proof-of-concept generation and web…
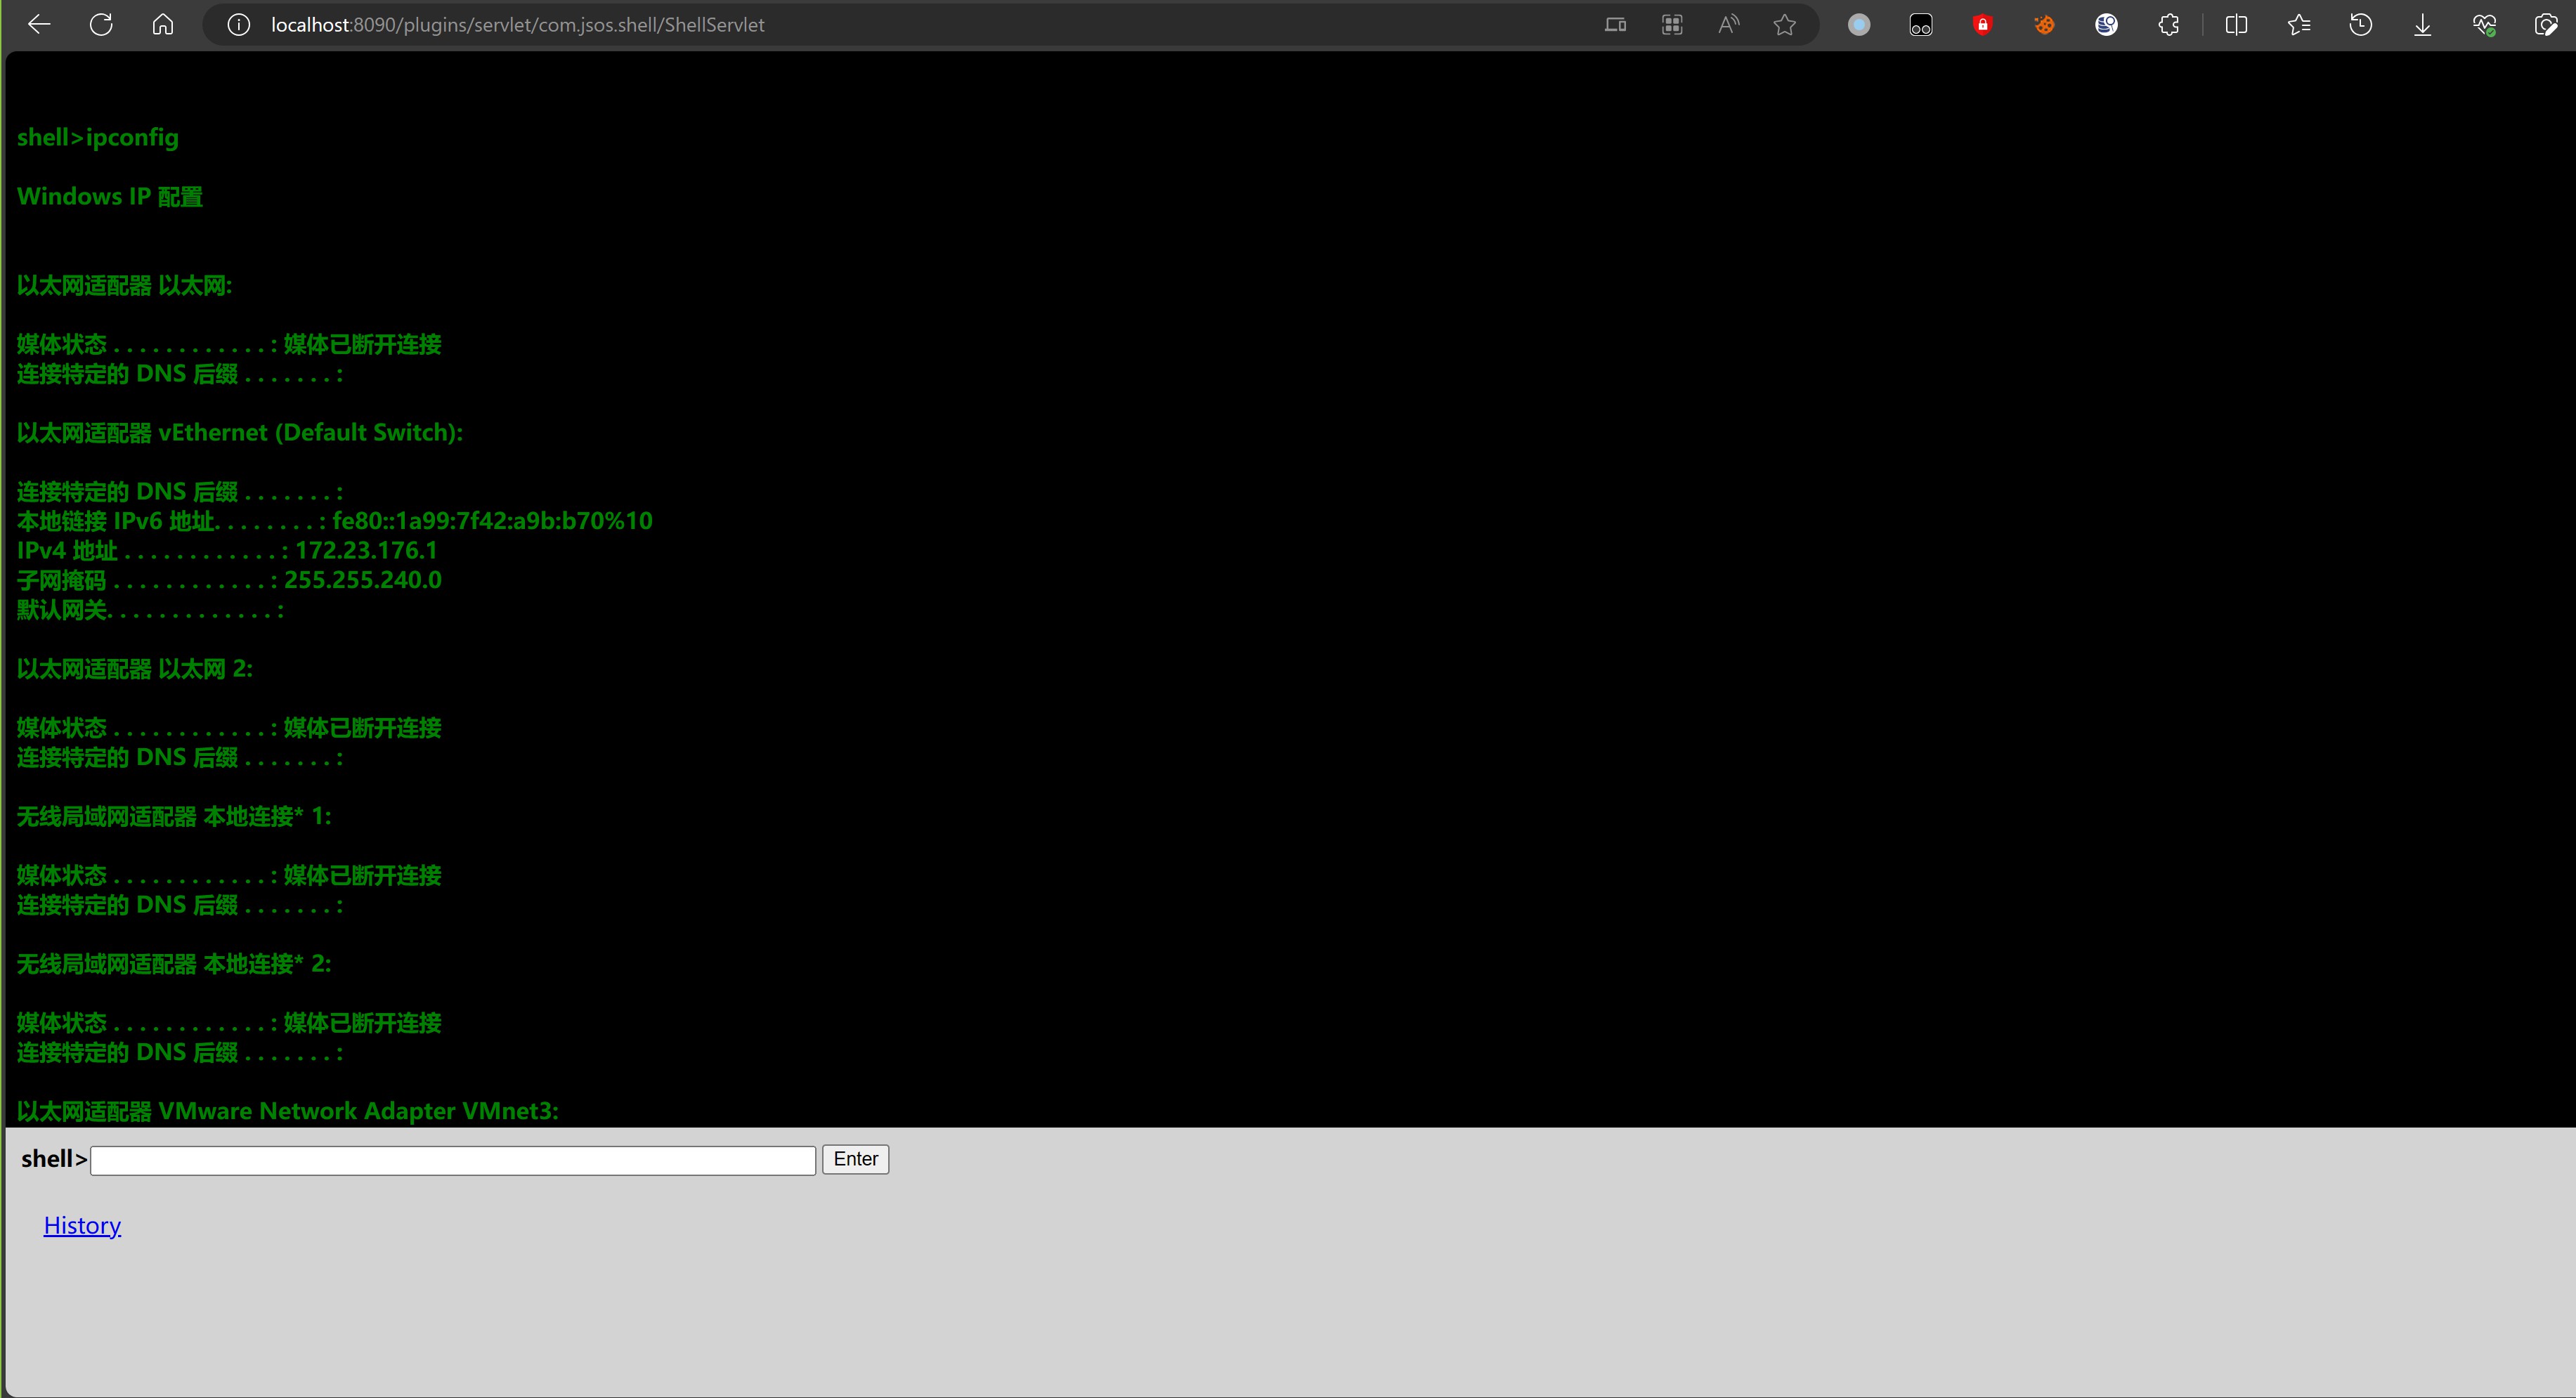 youcannotseemeagain/cve-2023-22515_rce
Confluence后台rce
 0x00-0x00/-cve-2017-9805
Exploit script for Apache Struts2 REST Plugin XStream RCE (CVE-2017-9805)
 jas502n/java-compressed-file-security
java web 压缩文件 安全 漏洞
 lanzt/cve-2020-14321
Authenticated exploit for Moodle 3.9 that escalates teacher privileges to manager role and achieves remote code execution via malicious plugin upload.








