
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
 localh0ste/cve-2025-4138
Tarfile module directory traversal vulnerability ( with overflow crossed Directory ) --> Lead to Privilege escalation
 imohammed28/cve-2024-10220-test
Kubernetes gitRepo volume vulnerability (CVE-2024-10220) exploit for controlled HPC security research, demonstrating arbitrary command execution on…
 graypixel2121/cve-2025-61229
Technical analysis and proof-of-concept exploit for CVE-2025-61229, a local privilege escalation in SuperDuper! that allows arbitrary script…
 hyperps/cve-2026-0848
nltk.tokenize.StanfordSegmenter dynamically loads external Java .jar files without verification or sandboxing. If an attacker can supply or replace…
 1numak1/cve-2025-31337
CVE-2025-31337 Security Advisory - Critical Buffer Overflow in AI Chatbot Framework
 alimezar/cve-2026-27199-werkzeug-safe-join-bypass-poc
Proof-of-concept exploit for CVE-2026-27199, a Werkzeug safe_join() Windows device-name bypass, demonstrating path traversal and silent data discard.
 shaheeryasirofficial/cve-2025-8088
CVE-2025-8088 is a critical path traversal vulnerability in WinRAR 7.12
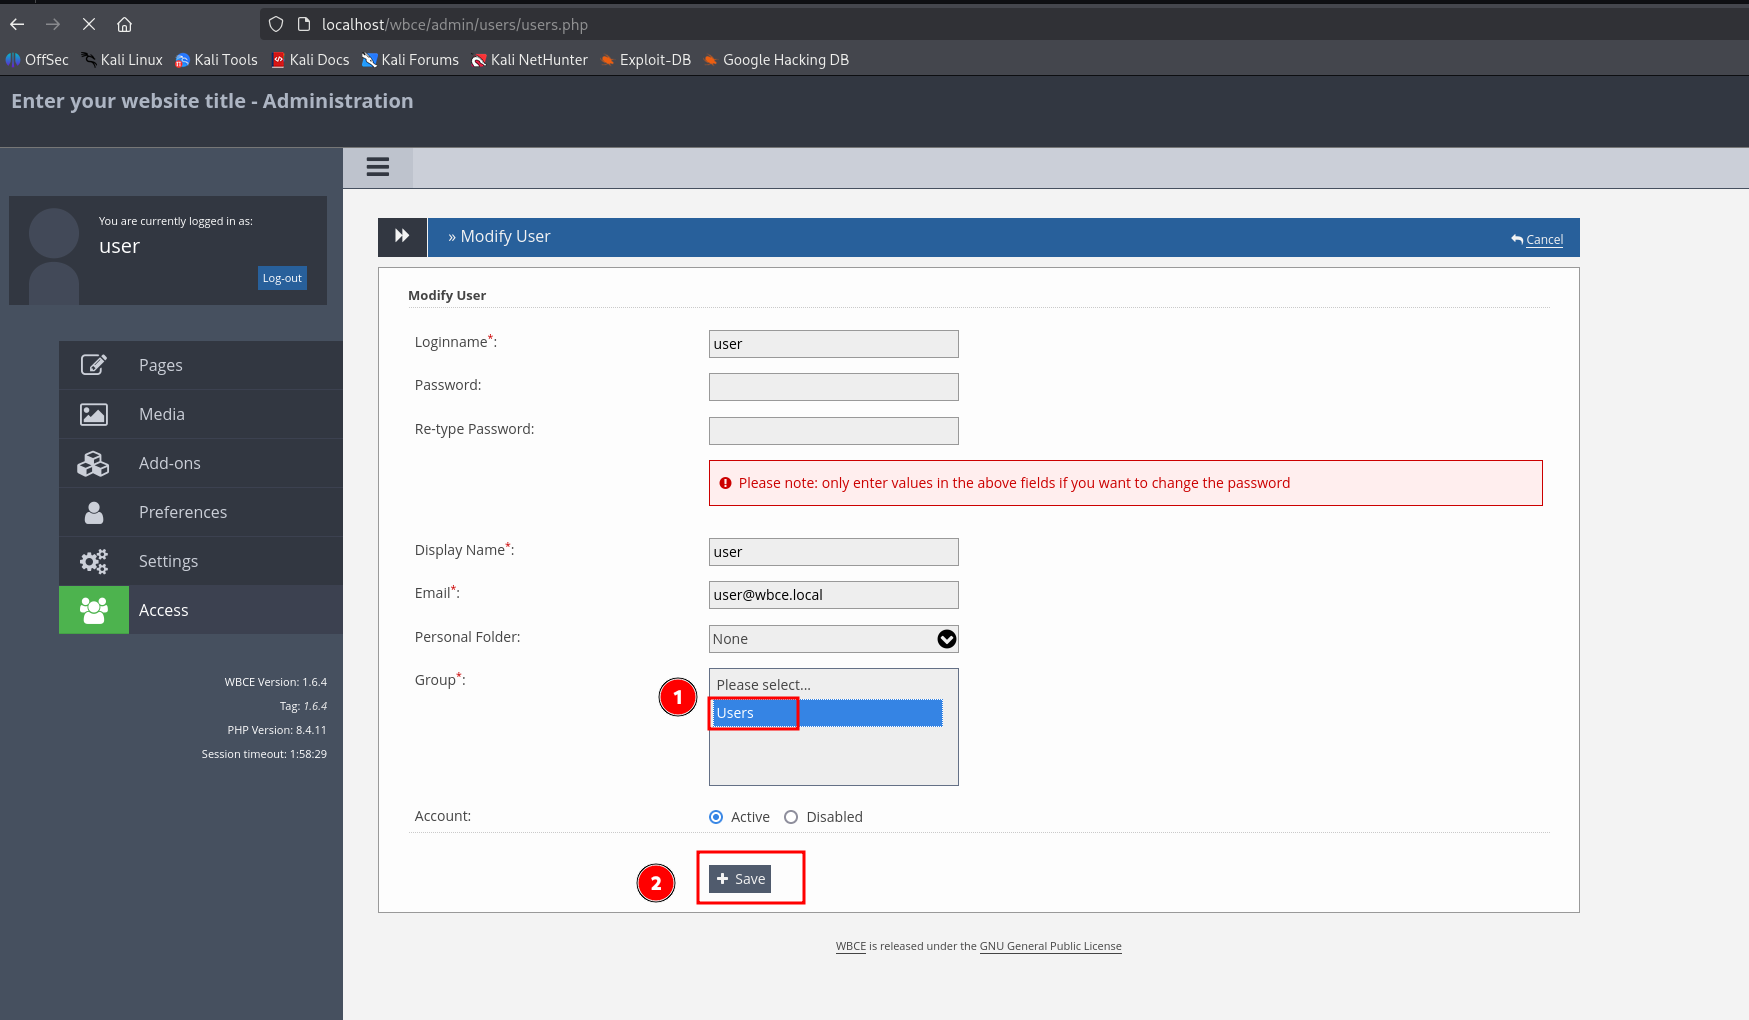 lukasz-rybak/cve-2025-65094
Proof-of-concept for CVE-2025-65094: privilege escalation via IDOR in WBCE CMS. Demonstrates group ID manipulation to gain admin access, with…
 joakimbulow/cve-2026-24688
Proof-of-concept exploit for CVE-2026-24688, a denial-of-service vulnerability in pypdf's outline parsing. Includes malicious PDF generator and…
 dotadrien/cve-2025-60654
Proof-of-concept for CVE-2025-60654: stored cross-site scripting (XSS) in Script Pag ad description field. Demonstrates filter bypass using HTML tags…
 gregk4sec/cve-2026-25854
Original security research and proof-of-concept for CVE-2026-25854, an open redirect vulnerability in Apache Tomcat cluster configurations, including…
 iteride/cve-2025-29927
In-depth analysis and PoC for CVE-2025-29927, a Next.js middleware authorization bypass via the x-middleware-subrequest header. Includes Nuclei…
 snorlyd/https-nj.gov---cve-2020-11023
Vulnearability Report of the New Jersey official site
 open-flaw/cve-2025-12758
Detailed CVE-2025-12758 disclosure with PoC demonstrating Unicode variation selector bypass in validator.js isLength(), including root cause…
 klassiker/cve-2025-55182
CodeQL-based analysis of CVE-2025-55182 prototype pollution vulnerability in React Server Components, with exploit POC and static detection queries…
 mishra0230/cve-2023-38831
CVE-2023-38831 - WinRAR
 azu/msgpack-cve-2021-23410-test
Test repository demonstrating a proof-of-concept for CVE-2021-23410 in msgpack, analyzing whether the reported deserialization vulnerability is…
 rickidevs/cve-2026-34070
I Found a Zero-Day Vulnerability in langchain — Here’s How It Went








