#1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 egorrsp/cve-2020-15368-asrdrv103-research
Reverse engineering research of ASRock AsrDrv103.sys (CVE-2020-15368), covering its driver interface, encrypted request protocol, and privileged…
 secprbench/secprbench
Benchmark of 265 real vulnerability-introducing code changes across nine C, C++, and Rust projects, with paired review tasks, Docker sandbox, judge,…
 4rdr/proofs
Collection of CVE findings, proof-of-concept references, and vulnerability research notes, including ExploitDB entries and credited security…
 n0n4m3x41/cve-2026-22738-poc
Proof-of-concept exploit for CVE-2026-22738, a critical SpEL injection RCE in Spring AI SimpleVectorStore, demonstrating unauthenticated OS command…
 patois/winmagic_sd
Technical Write-Up on and PoC Exploit for CVE-2020-11519 and CVE-2020-11520
 neurosaki987/qvm-tool
Static analysis and structure recovery toolkit for ACE .qvm0-protected PE images
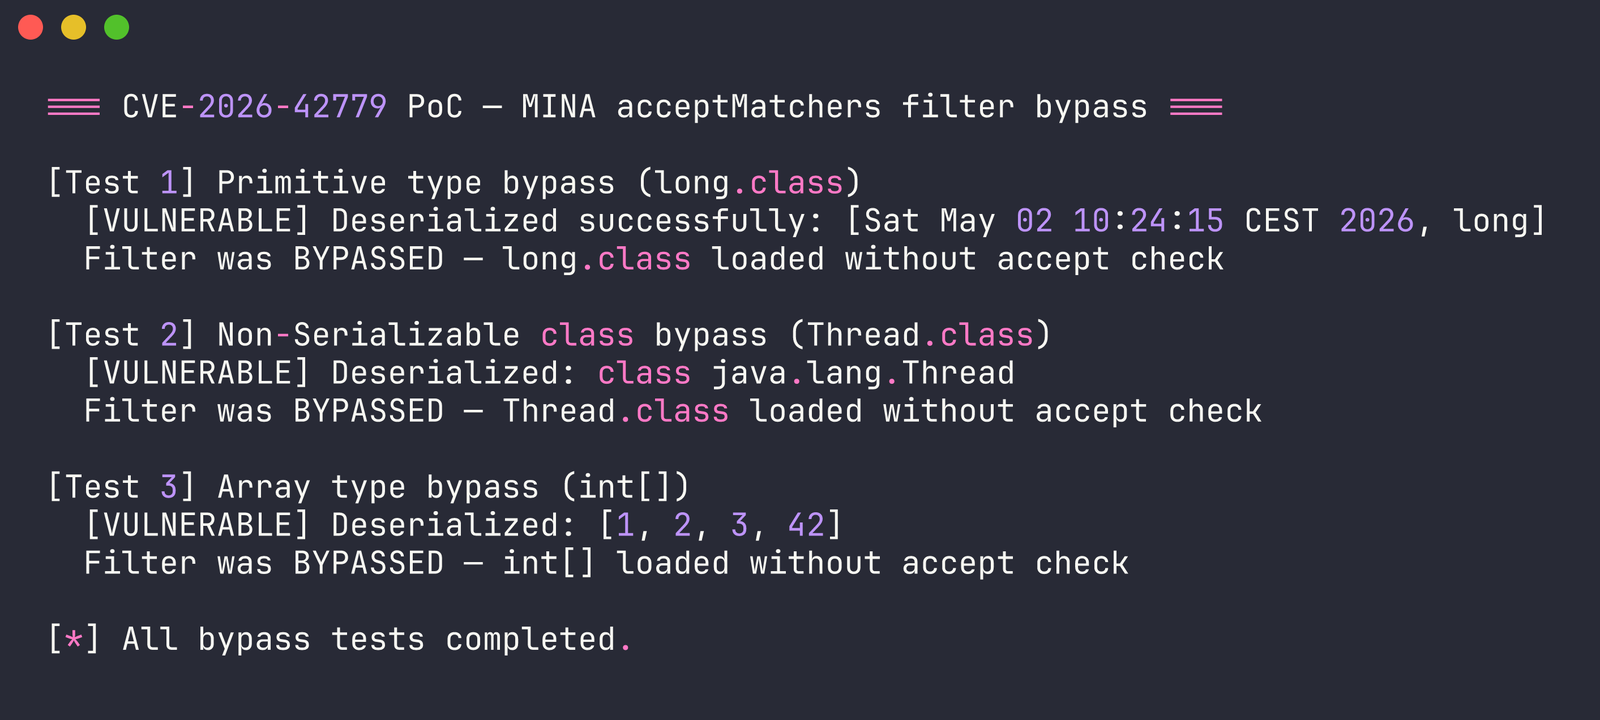 dinosn/cve-2026-42779
Proof-of-concept demonstrating a deserialization filter bypass in Apache MINA leading to remote code execution, with detailed root cause analysis,…
 stair-lab/certified-unlearning-neural-networks-icml-2025
Code for the paper Certified Unlearning for Neural Networks, ICML 2025
 lzty/cve-2026-94129
Proof-of-concept implementation for CVE-2026-94129, provided for study and research purposes.
 badkeys/debianopenssl
Private keys vulnerable to Debian OpenSSL bug (CVE-2008-0166)
 webraybtl/cve-2023-27363
福昕Foxit PDF远程代码执行漏洞CVE-2023-27363分析与复现
 wangs-official/opace6-cve-2026-64560
Temporary root tool for OnePlus Ace 6 that exploits the CVE-2026-64560 Linux kernel POSIX CPU timer use-after-free to gain root until reboot, without…
 nccgroup/setcookieanalysisinbrowsers
SetCookie Analysis in Browser Research Results
 werew/qsynth-artifacts
Benchmark datasets and synthesis artifacts for QSynth, containing Tigress-obfuscated C functions, x86_64 binaries, execution traces, ground truth,…
 decalage2/detect_cve-2026-86950
A python tool to detect PDF files exploiting CVE-2026-86950
 erberkan/cve-2026-42536-poc
Heap-based Buffer Overflow vulnerability in Apache HTTP Server with mod_xml2enc, xml2StartParse, and untrusted content
 azqzazq1/lid
LID — Linux Integrity Drift: Bypassing AppArmor via eBPF pathname rewriting. Pre-LSM syscall argument manipulation with zero audit footprint. "Linux…