
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 munshi007/aura-state
Python framework for building LLM workflows as state machines with formal verification via Z3 theorem proving, CTL model checking, and conformal…
 ethiack/cve-2023-29007
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation via crafted repository…
 knight0x07/winrar-code-execution-vulnerability-cve-2023-38831
Educational analysis of WinRAR code execution vulnerability CVE-2023-38831, covering exploitation mechanics and mitigation strategies through…
 divagr18/gpu-instance-fingerprint
Fingerprint the exact GPU you're running on, even among identical GPUs, from the order its atomic adds land in. 99.1% accuracy, survives reboots,…
 bitdefender/swapgs-attack-poc
This repository contains the sources and documentation for the SWAPGS attack PoC (CVE-2019-1125)
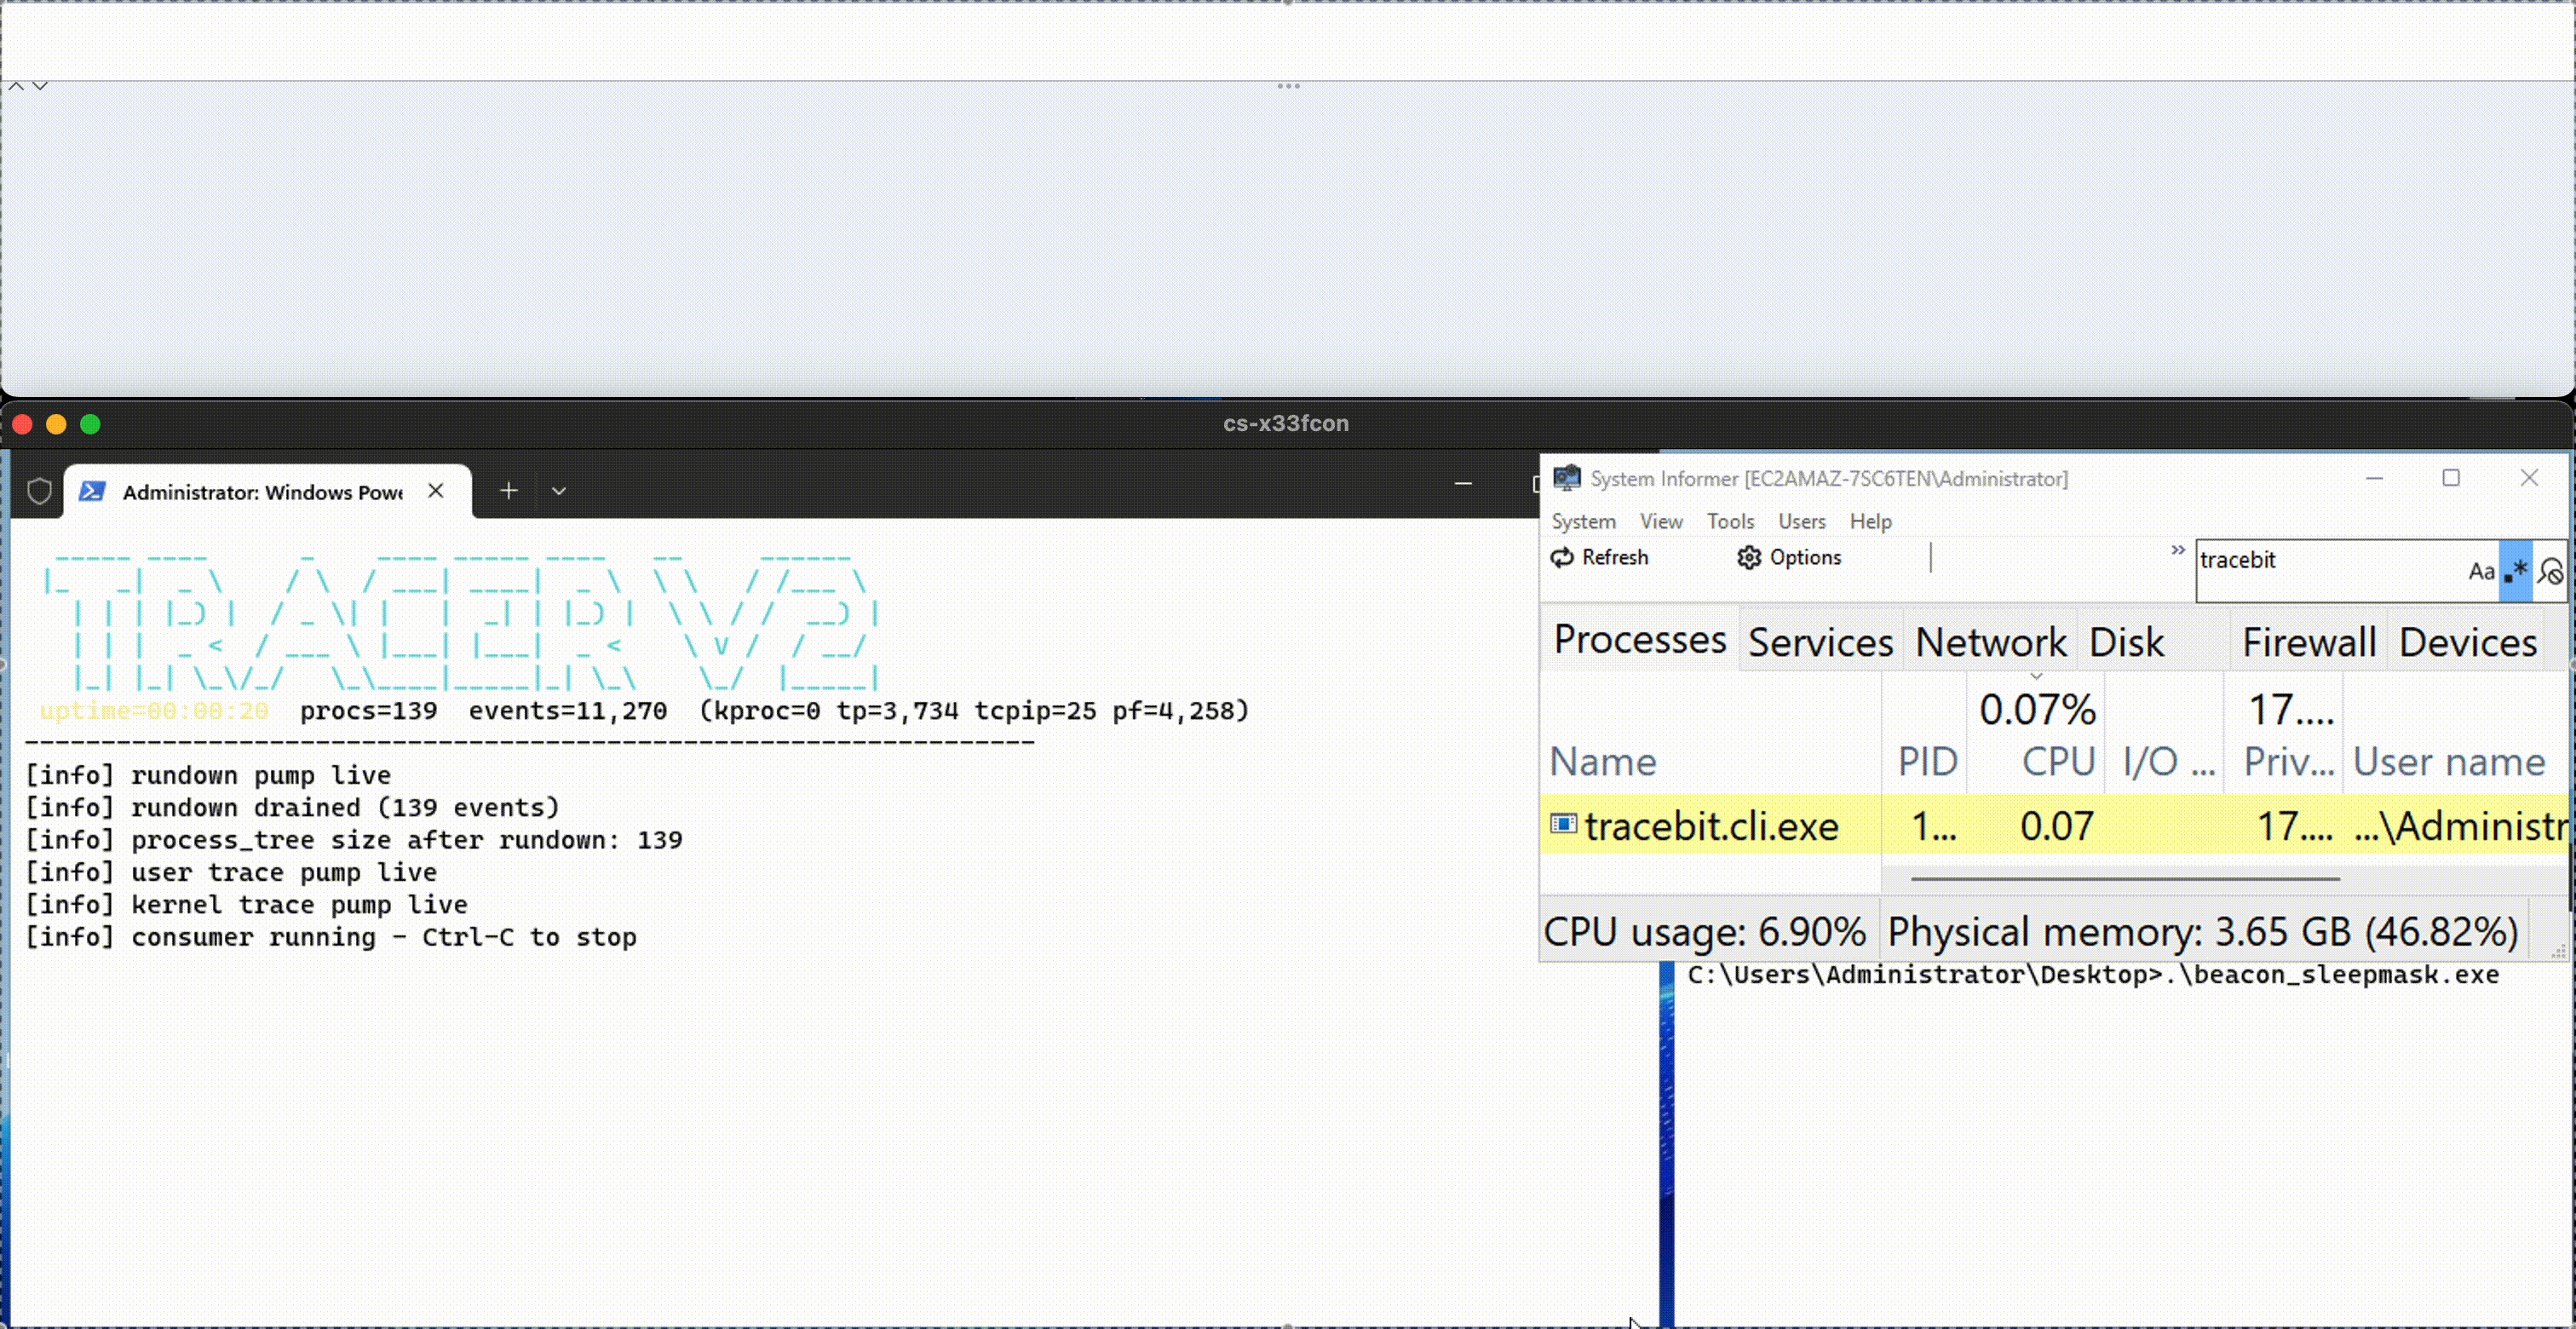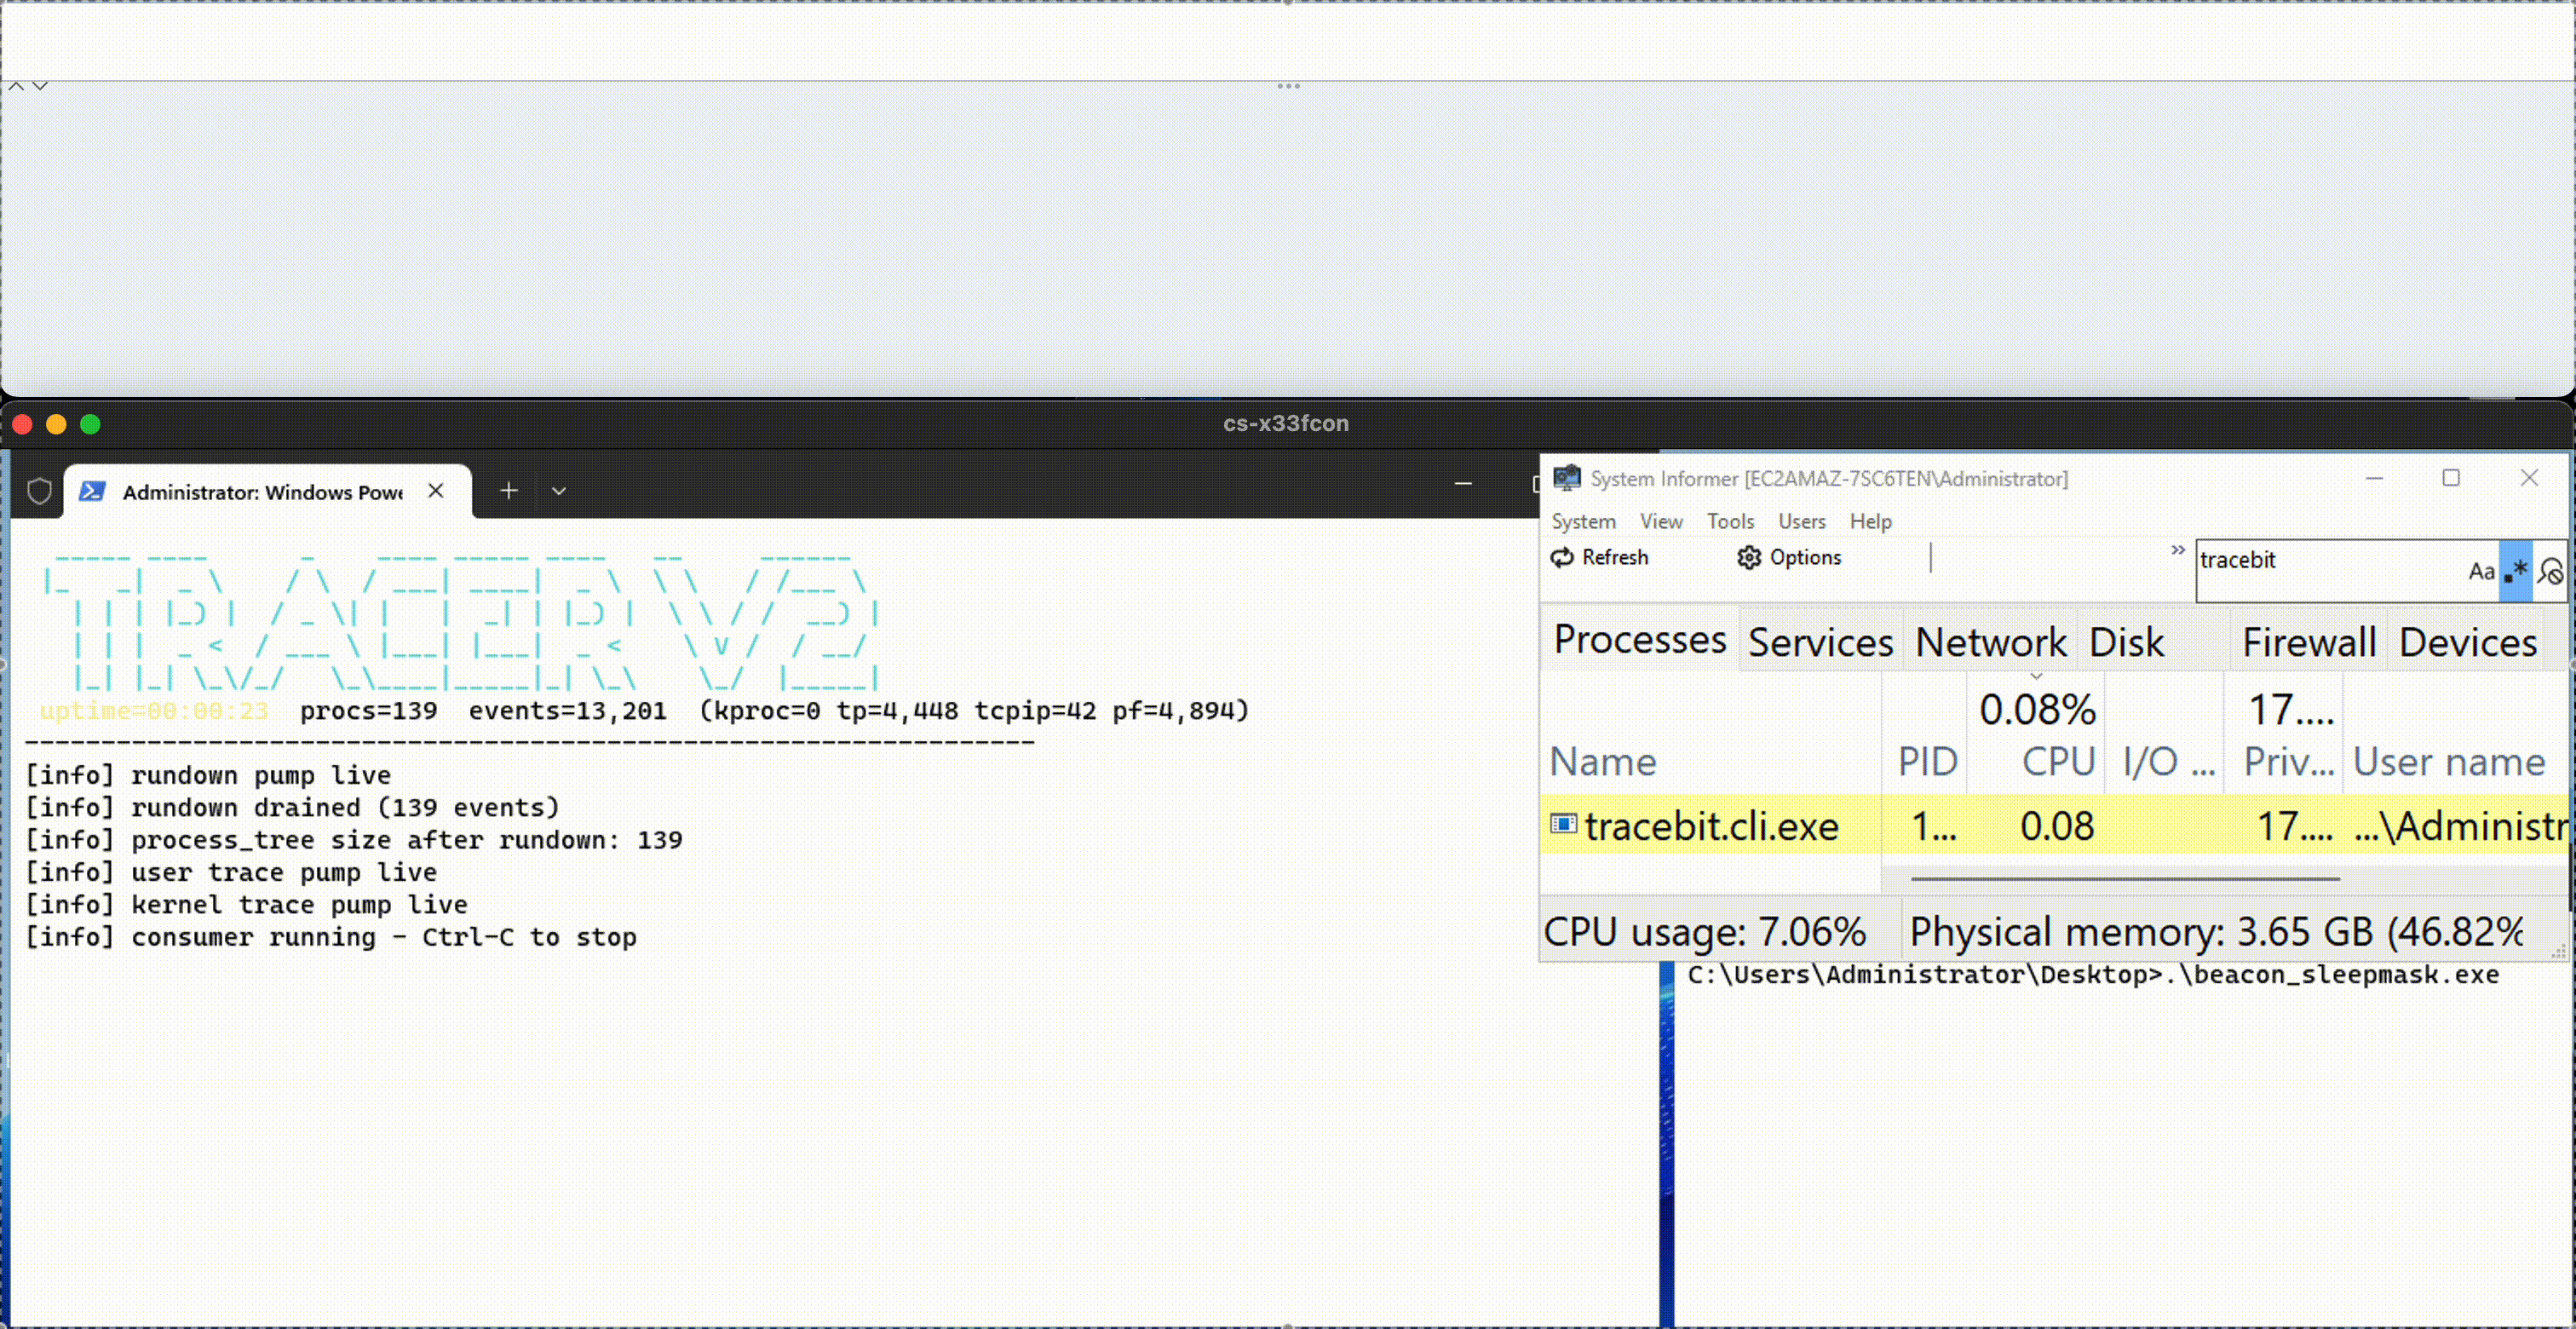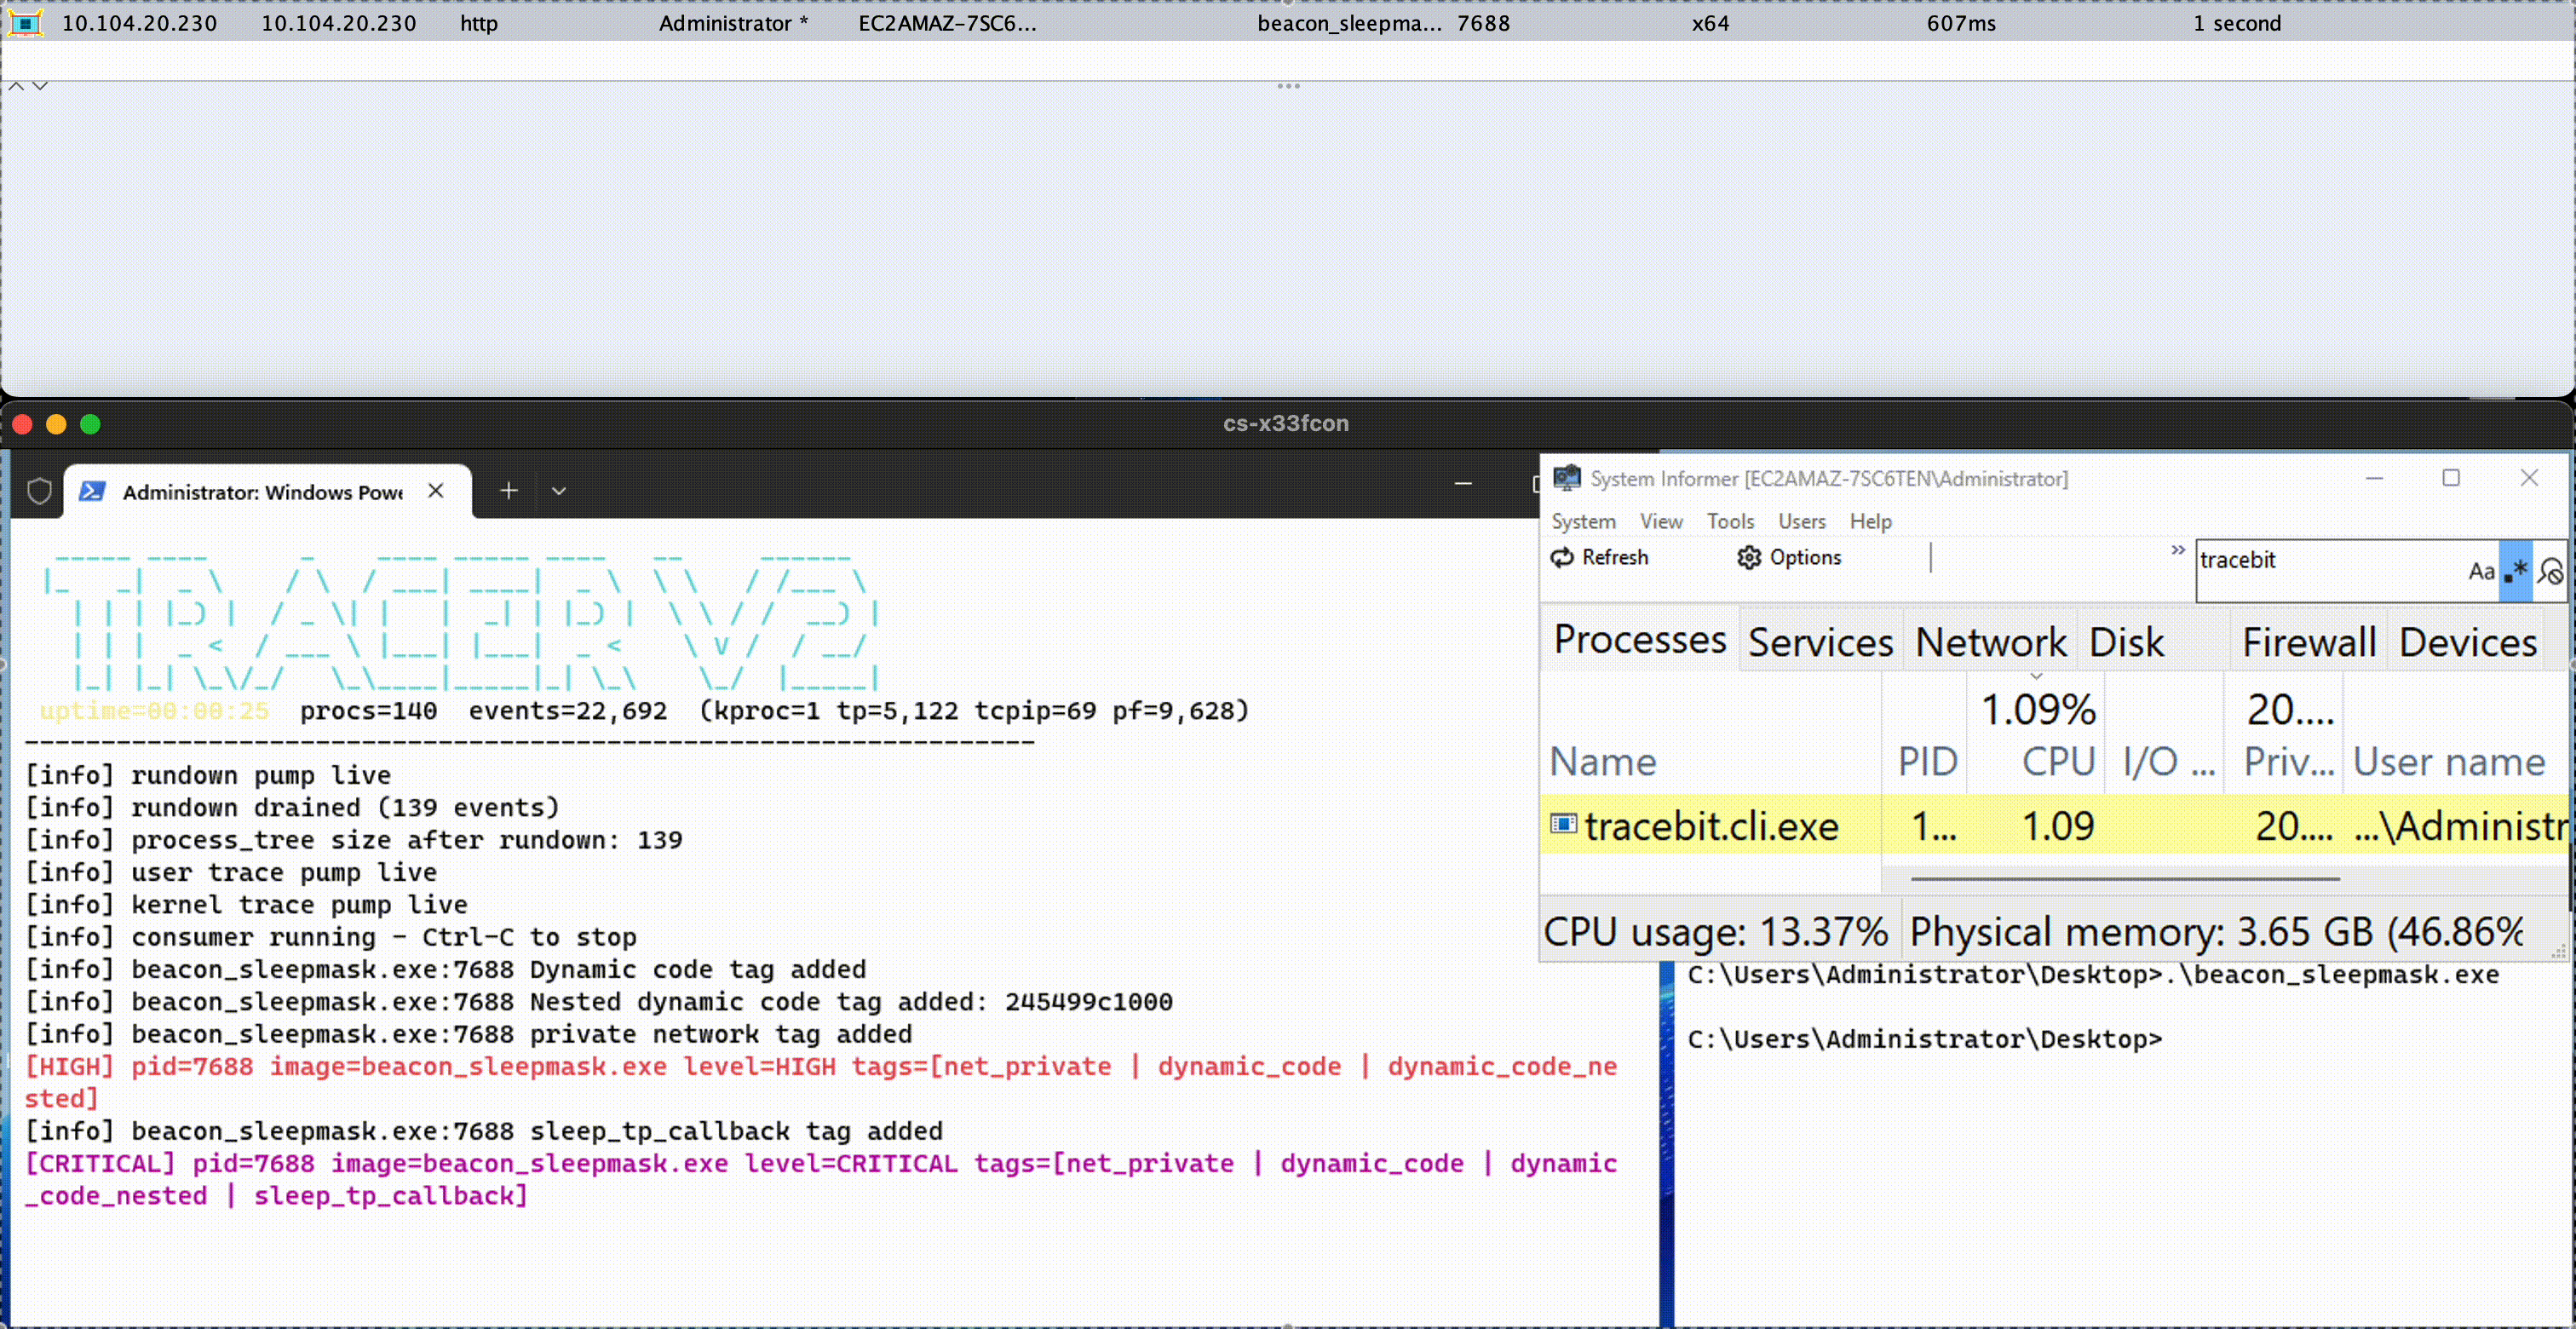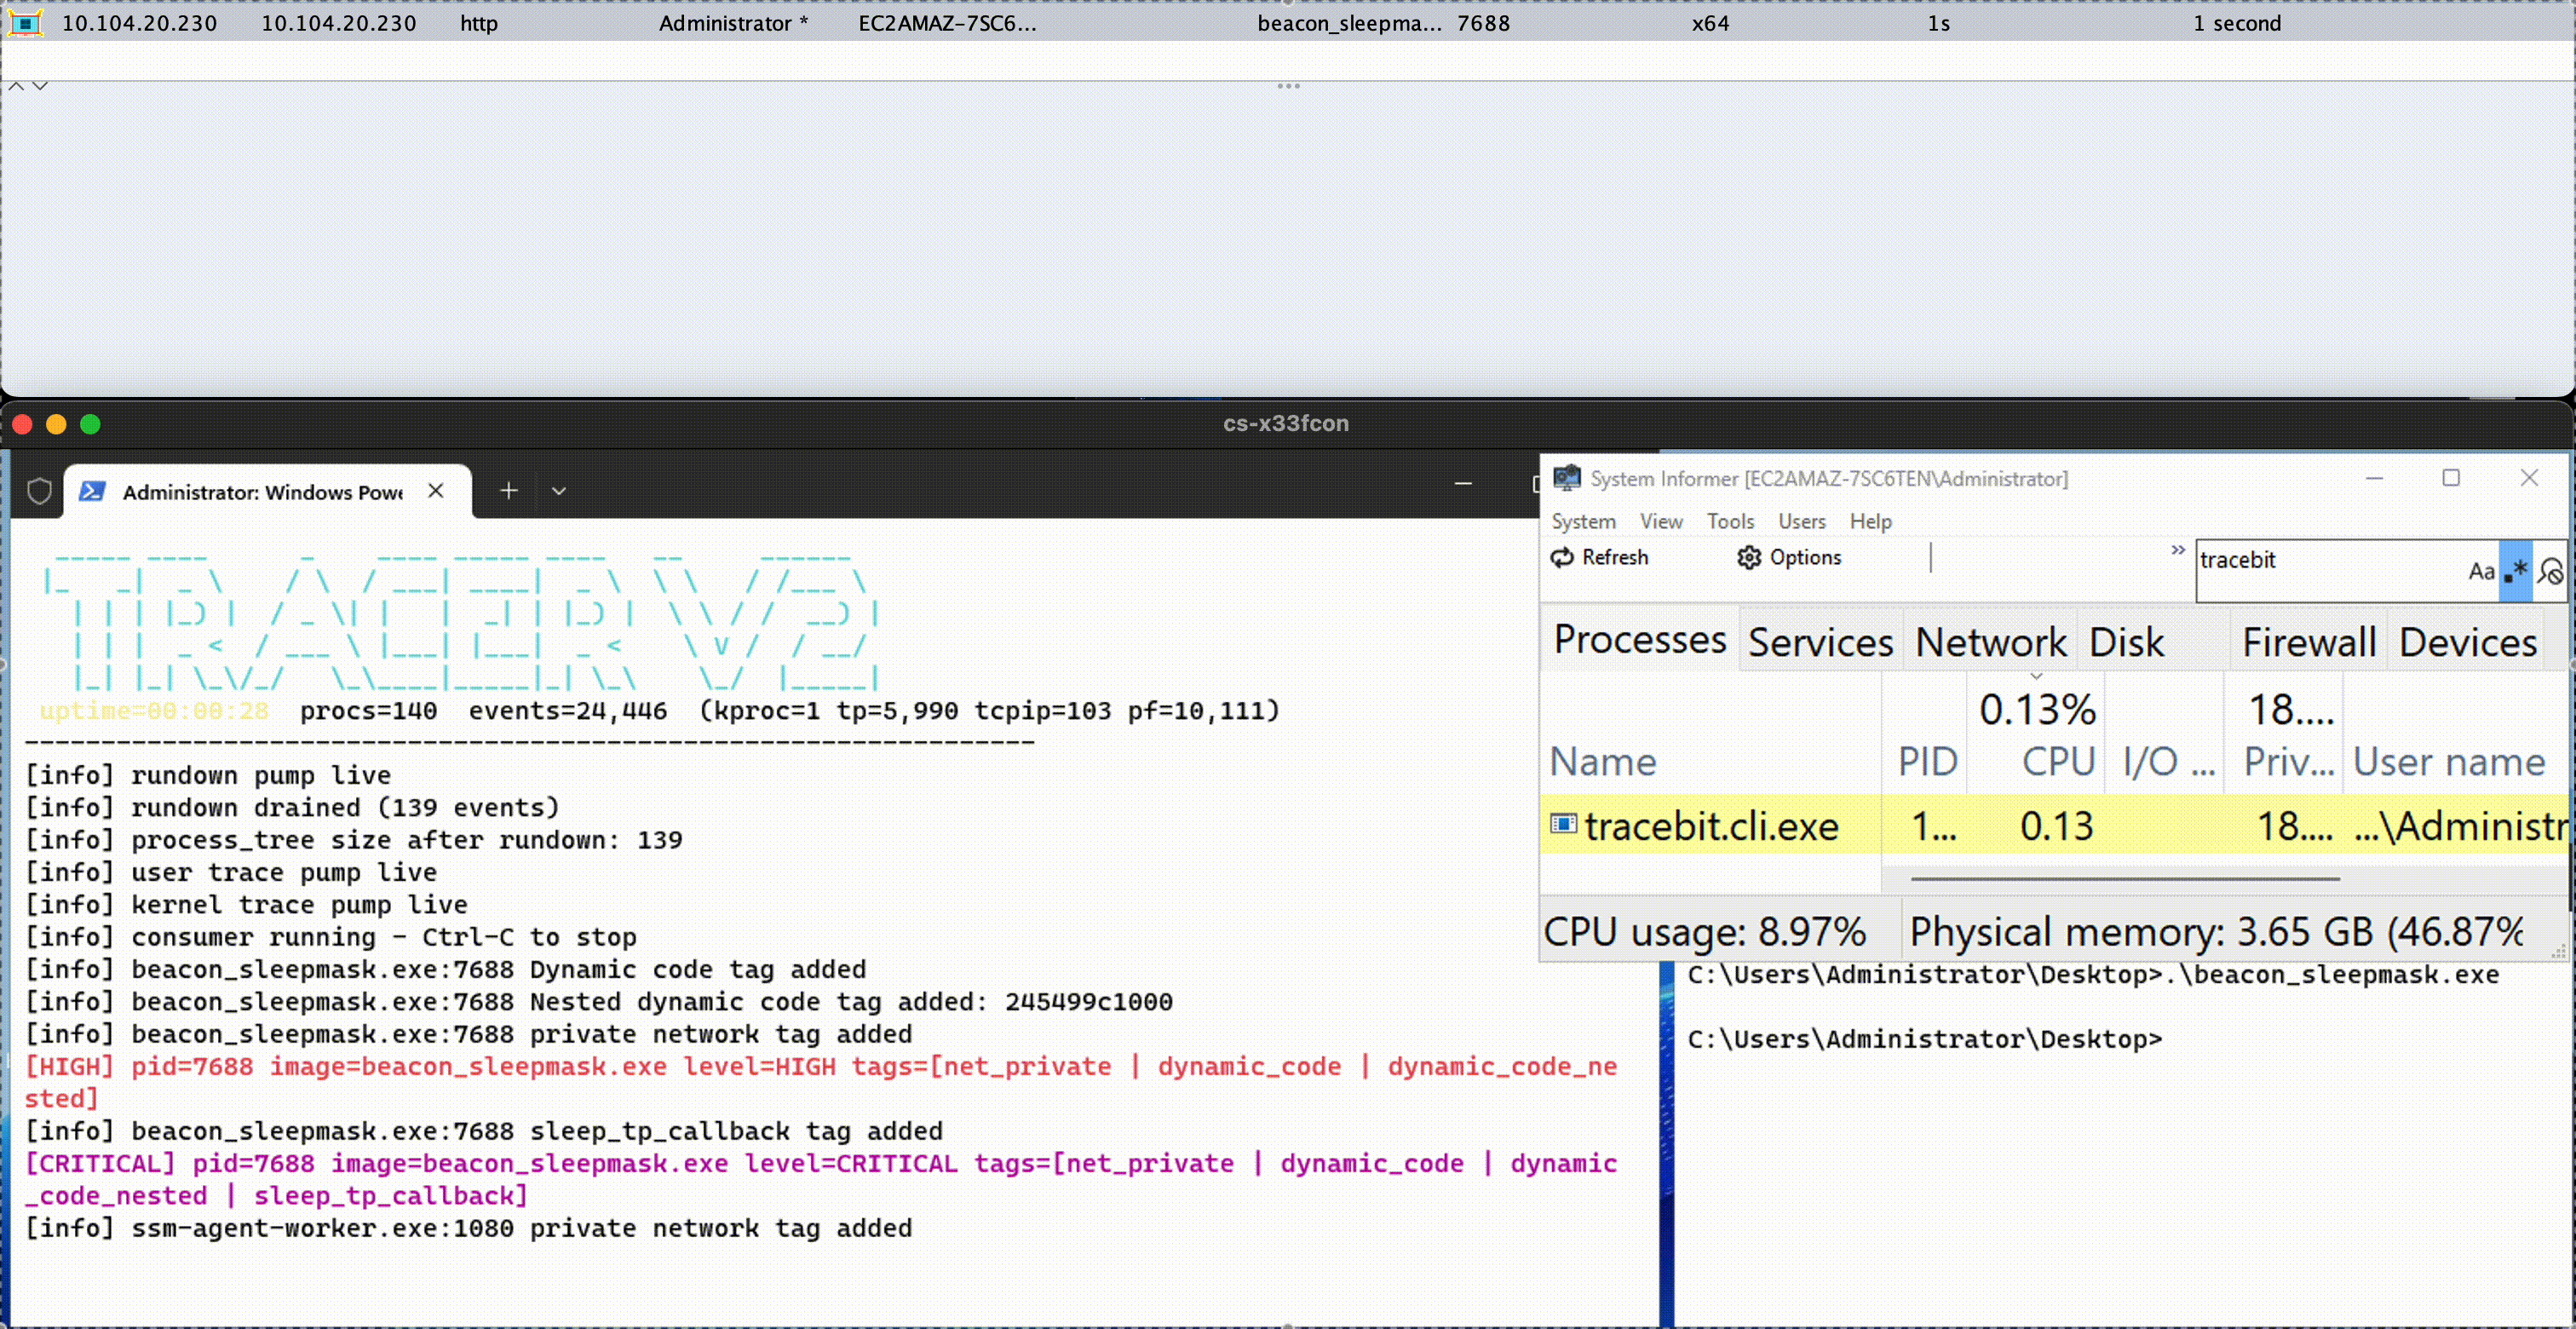 threathunters-io/kassandra_x33fcon_2026
This repository contains the research tool presented at x33fcon 2026, along with the associated presentation slides. The content is made available…
 bushidouk/abused-legitimate-services
Cloud, CDN, and marketing services leveraged by cybercriminals and APT groups
 synacktiv/windows_kernel_shadow_stack
Proof of concepts demonstrating some aspects of the Windows kernel shadow stack mitigation.

 owasp/pscf
OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
 nccgroup/royal_apt
Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research
 oritwoen/boha
Crypto bounties, puzzles and challenges data library
 he-wenjian/igpu-leak
[CVE-2019-14615] iGPU Leak: An Information Leakage Vulnerability on Intel Integrated GPU
 0xdea/raptor_infiltrate20
#INFILTRATE20 raptor's party pack.
 giancarlolelli/quantum
This repository contains the code and submission detail for the QDay prize challenge by https://www.projecteleven.com/
 gyaansastra/cve-2023-21716
A vulnerability within Microsoft Office's wwlib allows attackers to achieve remote code execution with the privileges of the victim that opens a…
 runzeroinc/vulns-2026-fatfs-chance
Documented security vulnerabilities in the FatFs embedded filesystem library with CVE details, fuzzing harness, exploit disk-image generator, and…
 gnoxter/mountain_goat
A PoC demonstrating techniques exploiting CVE-2016-5696 Off-Path TCP Exploits: Global Rate Limit Considered Dangerous








