
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
 colmmacc/cve-2022-3602
Technical deep-dive and anti-POC for CVE-2022-3602, a punycode buffer overflow in OpenSSL 3.0.x, with reproduction scripts, stack analysis, and…
 frenchyeti/rasputin
Ressources and papers related to my conferences and work on (un)RASPs. These work is in progress, please be patient :) Don't hesitate to contribute /…
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks

 4d4j/objdump-out-of-bounds-write
Proof of Concept (PoC) demonstrating the CVE-2026-18220, an out-of-bounds (OOB) write vulnerability in the DLX ELF backend of GNU binutils…
 0xmachos/apple-platform-security-guides
Every Apple Platform Security Guide
 packtpublishing/learning-linux-binary-analysis
Learning Linux Binary Analysis, published by Packt
 livecvebench/cve-factory
CVE-Factory
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
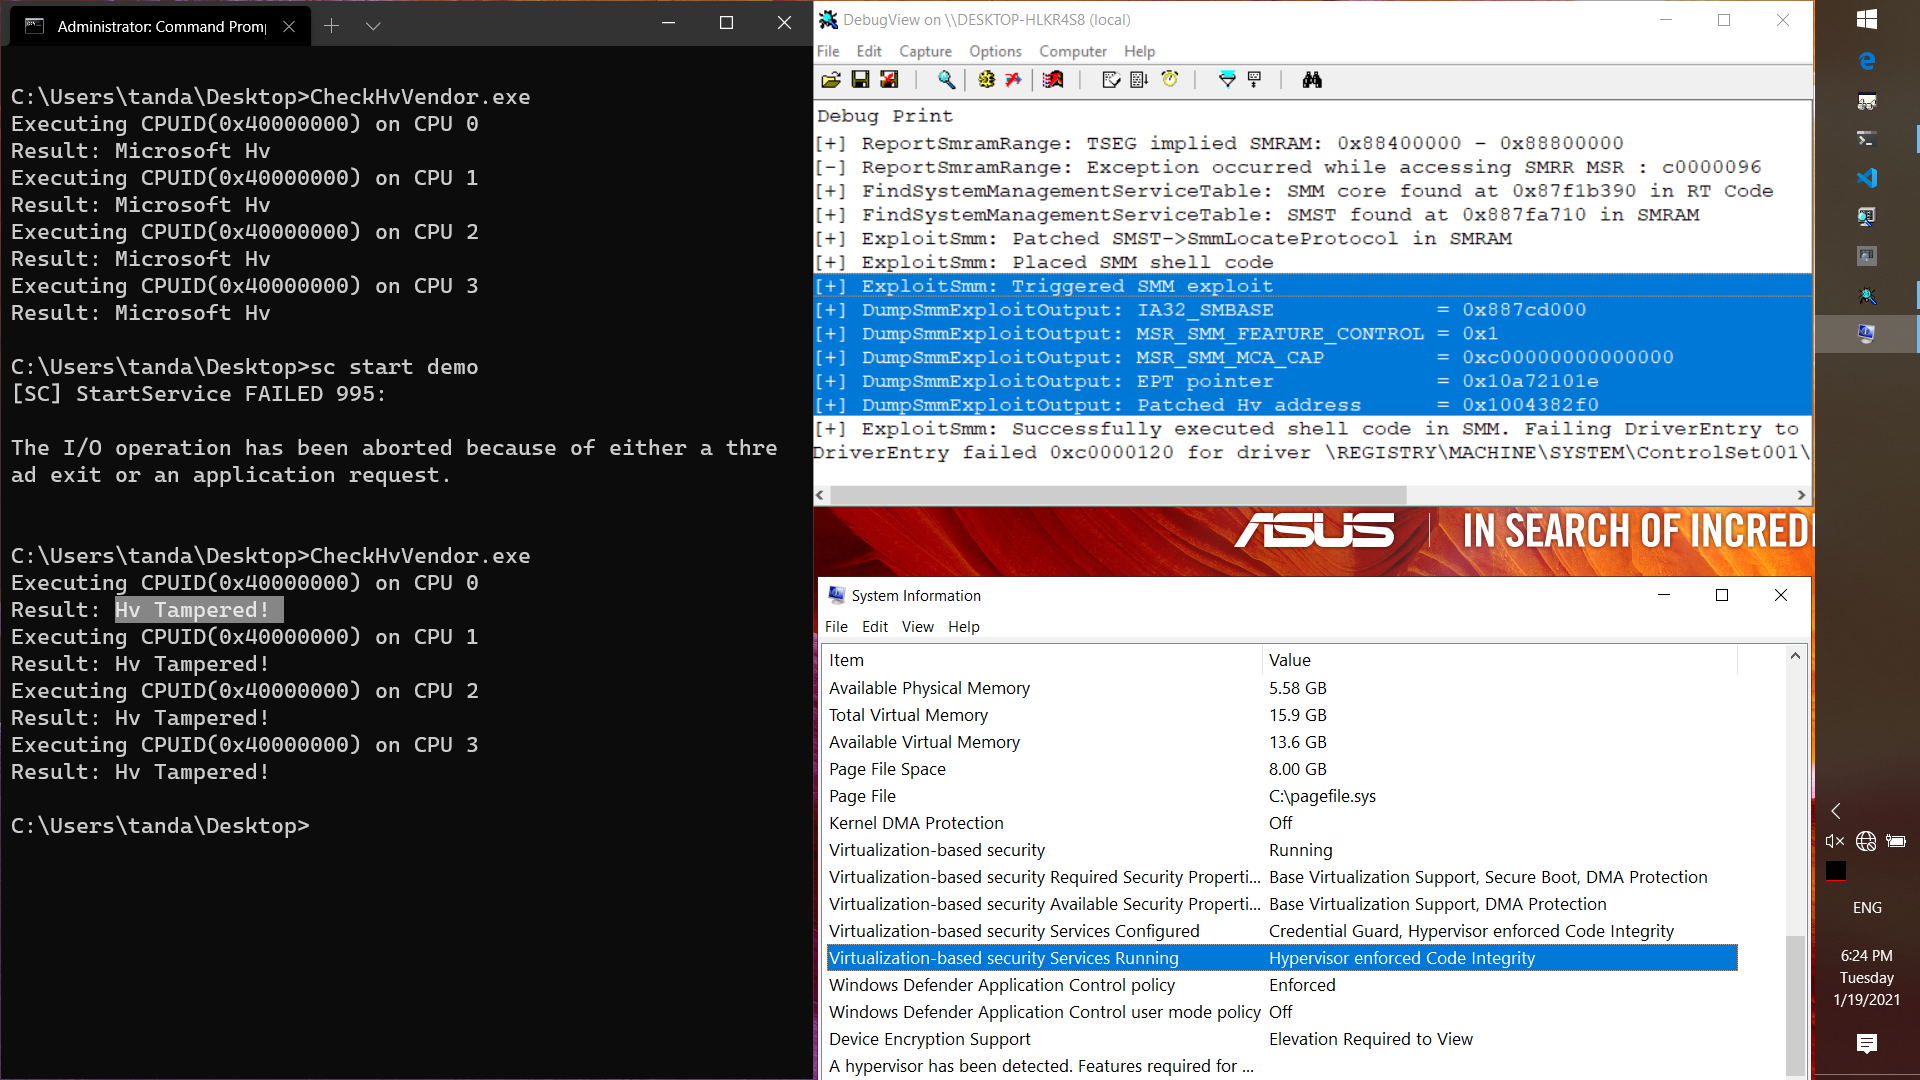 tandasat/smmexploit
The report and the exploit of CVE-2021-26943, the kernel-to-SMM local privilege escalation vulnerability in ASUS UX360CA BIOS version 303.
 mohshomis/modo
Curated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
 qiuhaoli/cve-2021-3929-3947
Recursive MMIO VM Escape PoC
 cosmosyi/autocontrol-arena
Automated framework for frontier AI safety evaluation that synthesizes executable, pressure-rich test environments to uncover latent risks in…
 portswigger/http-terminator
AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 movemaverick/move-vulnerability-database
Move Vulnerability Database
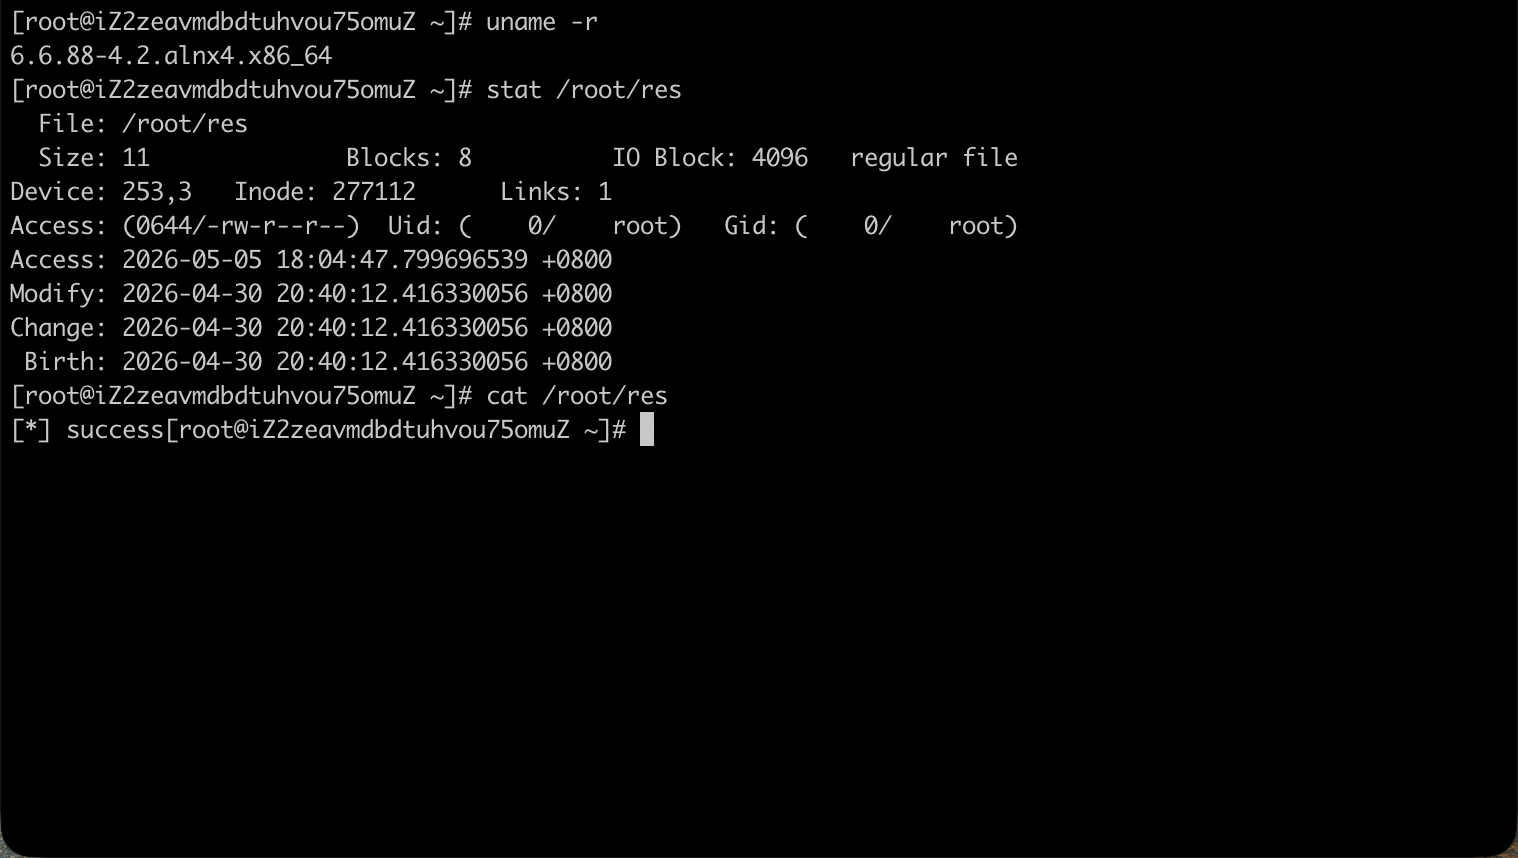 percivalll/copy-fail-cve-2026-31431-kubernetes-poc
PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…








