
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 wildwestcybersecurity/cve-2019-13288
Replicated using afl fuzzer instrumentation! Shoutz to antonio-morales.
 c2dc/anomaly-flow
Framework for implementing Network Intrusion Detection Systems (NIDS) aimed at identifying anomalies in network flows using Federated Learning models.
 seanheelan/o3_finds_cve-2025-37899
Artefacts for blog post on finding CVE-2025-37899 with o3
 serundengsapi/cve-2025-31200-ios-audioconverter-rce
Public disclosure of CVE-2025-31200 – Zero-click RCE in iOS 18.X via AudioConverterService and malicious audio file.
 synacktiv/windows_kernel_shadow_stack
Proof of concepts demonstrating some aspects of the Windows kernel shadow stack mitigation.
 missaels235/poc-cve-2025-24104-py
Proof-of-concept Python script demonstrating iOS file exfiltration via malicious symlink in device backup restoration, targeting the…
 taiyou-tw/cve-2024-40445_cve-2024-40446
This repository serves as the public reference for CVE-2024-40445 and CVE-2024-40446. Both vulnerabilities impact MimeTeX, an open-source software…
 mistymntncop/cve-2023-3079
Proof-of-concept exploit for CVE-2023-3079, a Chrome V8 type confusion vulnerability, with curated writeups and root cause analysis resources.
 andyshaw01/poisoncraft
This repository provides the official implementation of POISONCRAFT: Practical Poisoning of Retrieval-Augmented Generation for Large Language Models.
 migopp/cve-2024-44308
DFG register allocation bug in JavaScriptCore
 djjohnson565/cups-exploit
Heap-based buffer overflow example based on CVE-2023-4504
 gcatt-as/cve-2024-48591
Disclosure of a Cross-Site Scripting (XSS) vulnerability in Inflectra SpiraTeam 7.2.00 via malicious SVG file upload, with impact analysis and…
 carol-long/cc_watermark
Implementation of optimal coupling-based distortion-free text watermarking to embed detectable signals in LLM-generated text while preserving quality.
 0xbencantcode/cve-2025-43929
High severity vulnerability in KiTTY allowing for local executables to be ran without user confirmation under certain circumstances.
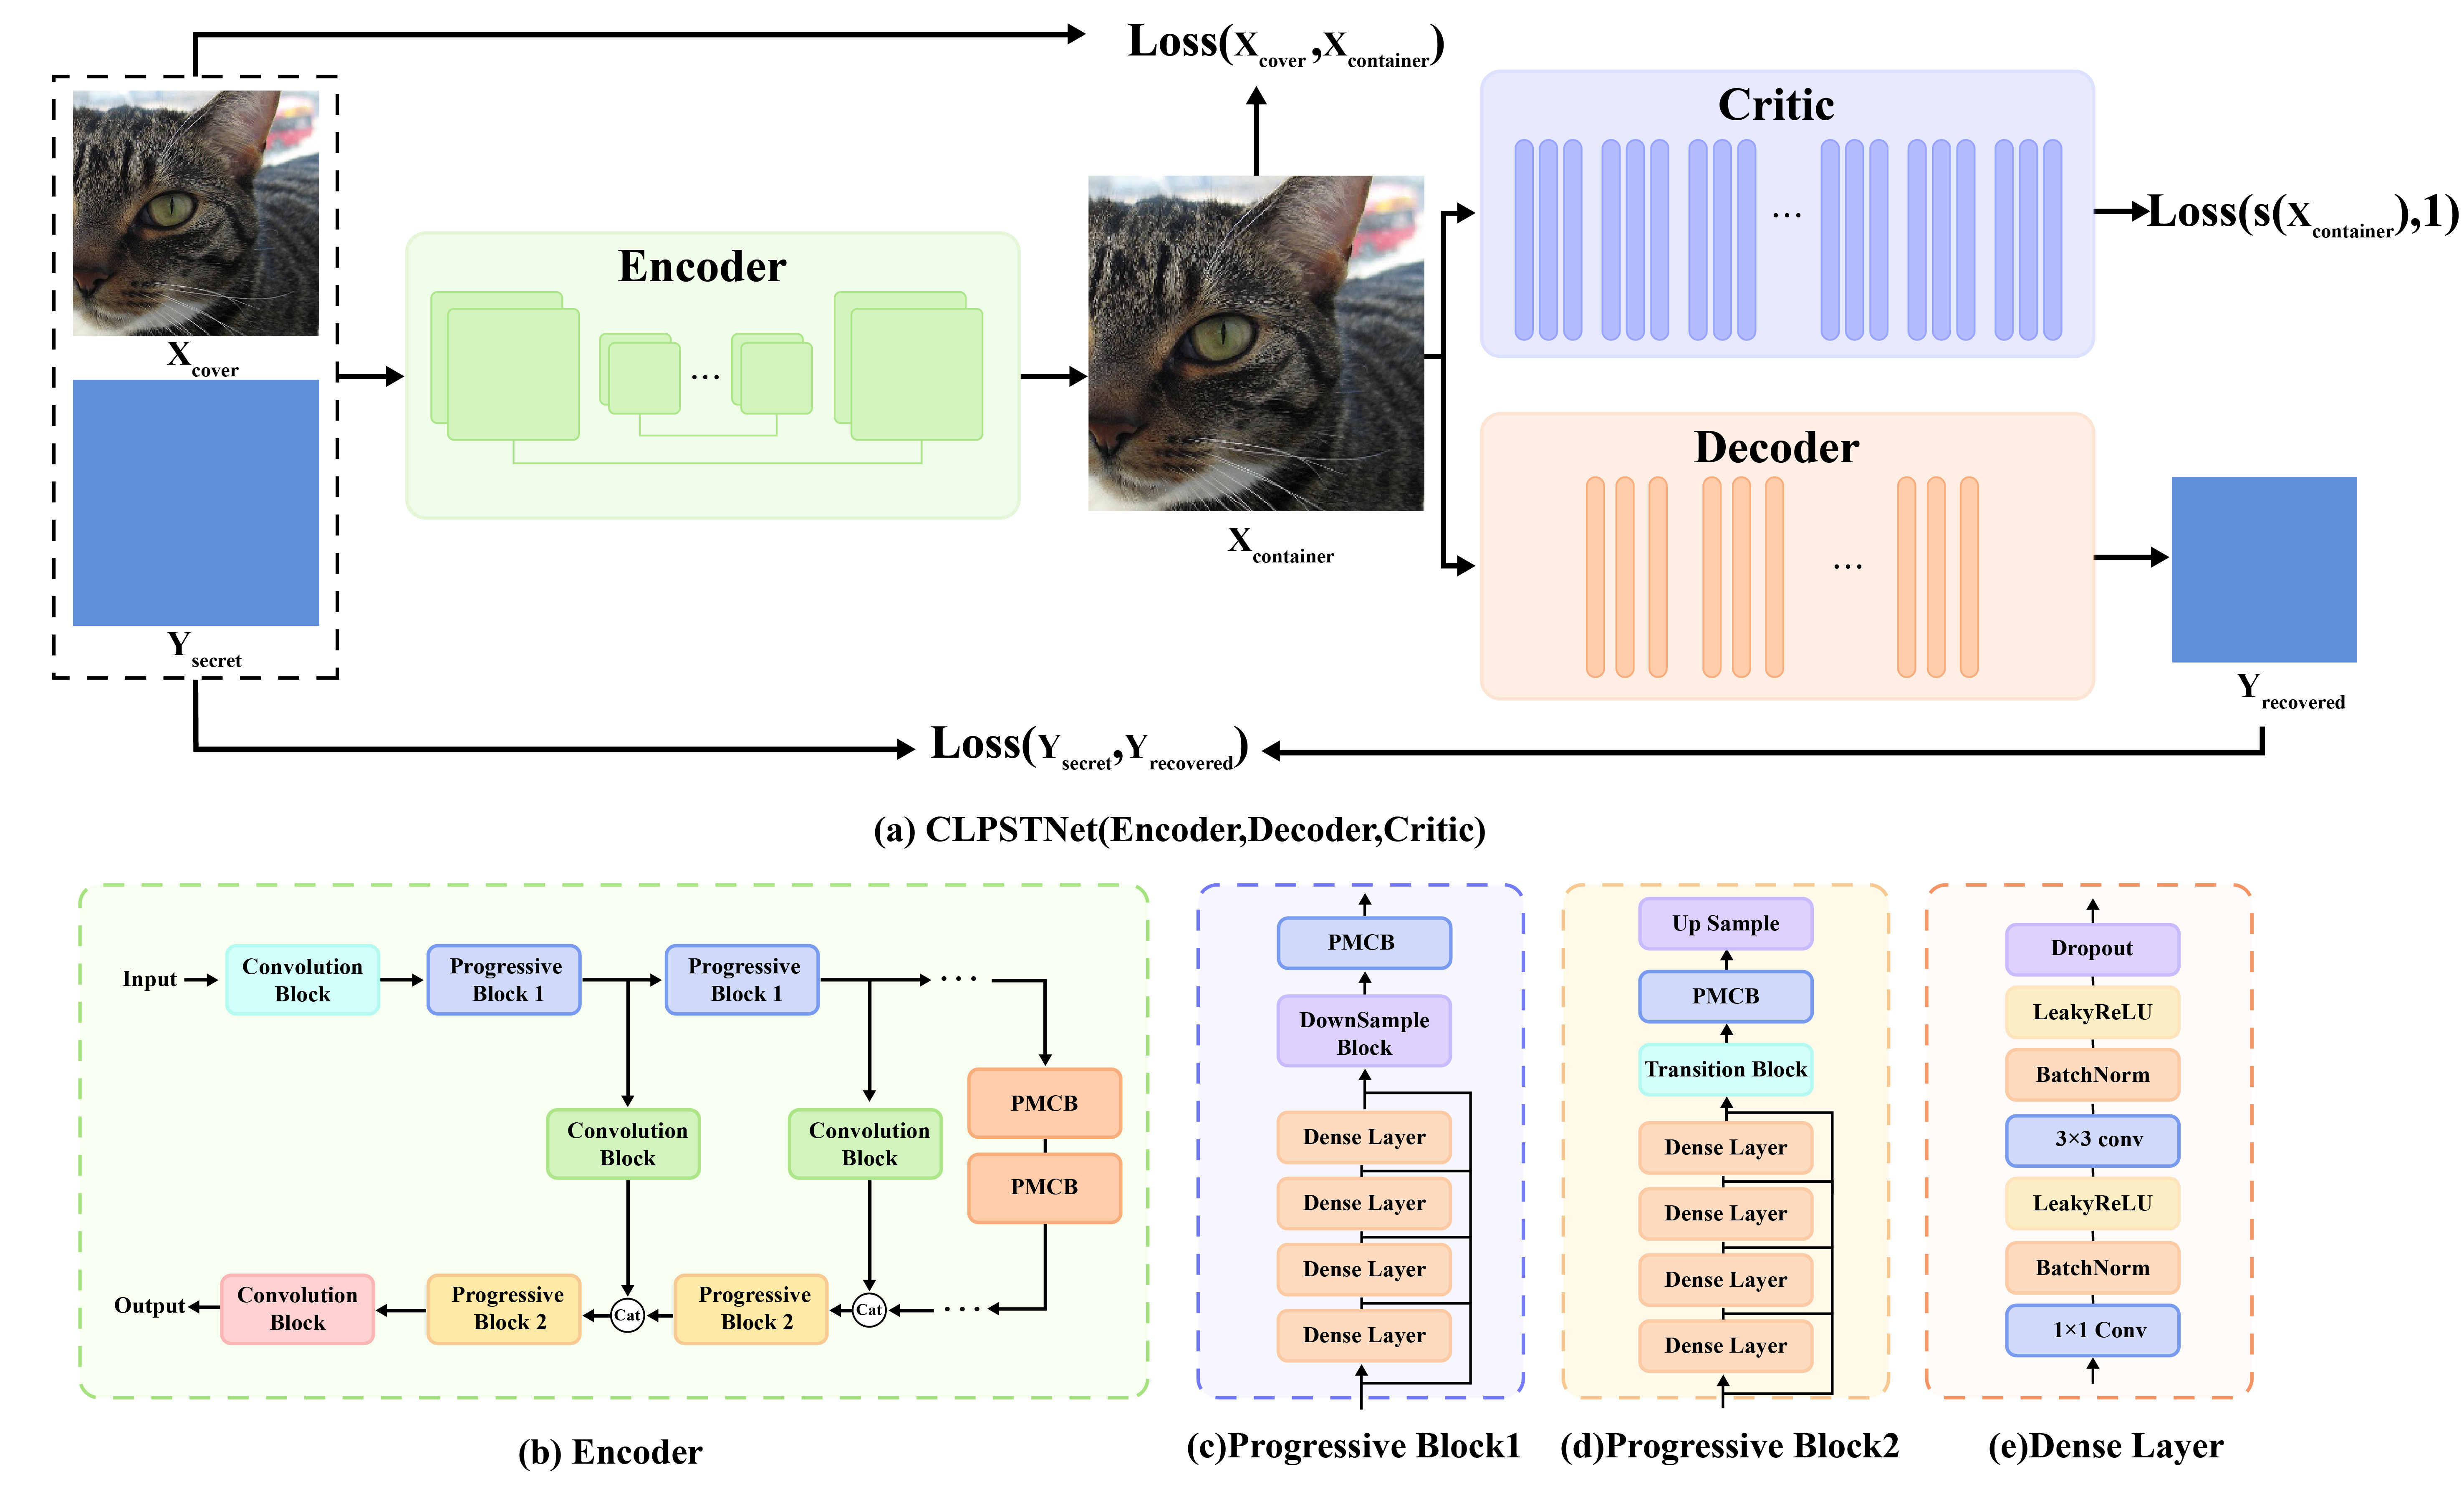 chaos-boops/clpstnet
CLPSTNet: A Progressive Multi-Scale Convolutional Steganography Model Integrating Curriculum Learning
 govolution/avet
AntiVirus Evasion Tool
 enablesecurity/vulnerability-disclosure-policy
How Enable Security handles security vulnerabilities
 spiralbl0ck/hackerlife.exe
Write up exploit failed chain and experience tryin to sell your first nday








