
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 vladko312/research_successful_errors
Whitepaper introducing Error-Based and Boolean Error-Based Blind techniques for SSTI and Code Injection, with universal payloads for six programming…
 alimezar/cve-2026-27199-werkzeug-safe-join-bypass-poc
Proof-of-concept exploit for CVE-2026-27199, a Werkzeug safe_join() Windows device-name bypass, demonstrating path traversal and silent data discard.
 sahiloj/cve-2023-33730
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…
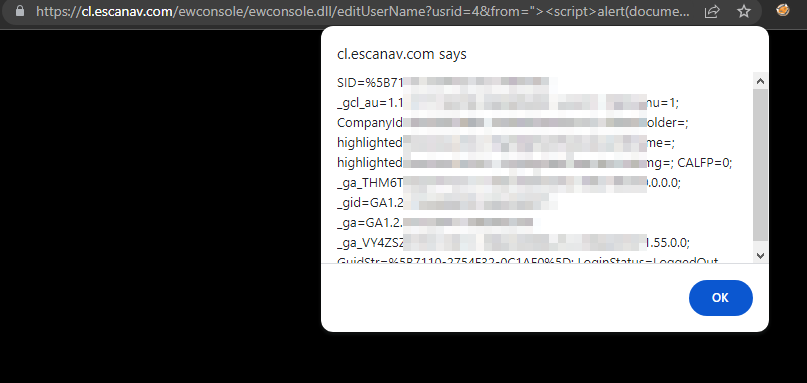 sahiloj/cve-2023-31703
A reflected Cross-Site Scripting (XSS) vulnerability exists in the Edit User functionality of the Microworld Technologies eScan Management Console…
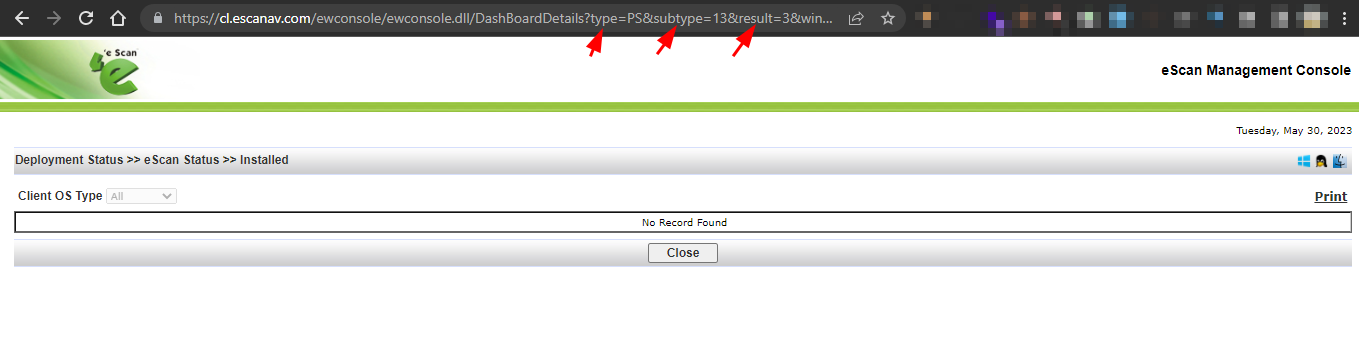 sahiloj/cve-2023-33731
A Reflected Cross-Site Scripting (XSS) vulnerability was discovered in the eScan Management Console (version 14.0.1400.2281) developed by Microworld…
 sahiloj/cve-2023-33732
CVE-2023-33732 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console, version…
 sahiloj/cve-2023-34835
A Reflected Cross-Site Scripting (XSS) vulnerability was discovered in the Microworld Technologies eScan Management Console, version 14.0.1400.2281.
 sahiloj/cve-2023-34836
A Reflected Cross-Site Scripting (XSS) vulnerability exists in Microworld Technologies eScan Management Console v14.0.1400.2281. The vulnerable…
 sahiloj/cve-2023-34837
CVE-2023-34837 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console version…
 sahiloj/cve-2023-34838
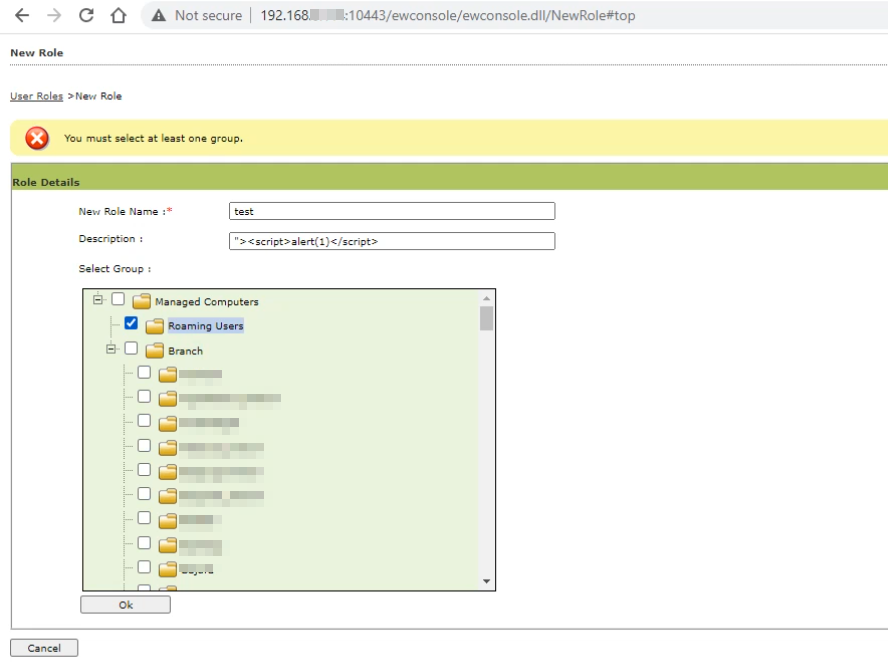
Microworld Technologies eScan Management Console version 14.0.1400.2281 is vulnerable to a Stored Cross-Site Scripting (XSS) attack.
 sahiloj/cve-2023-37190
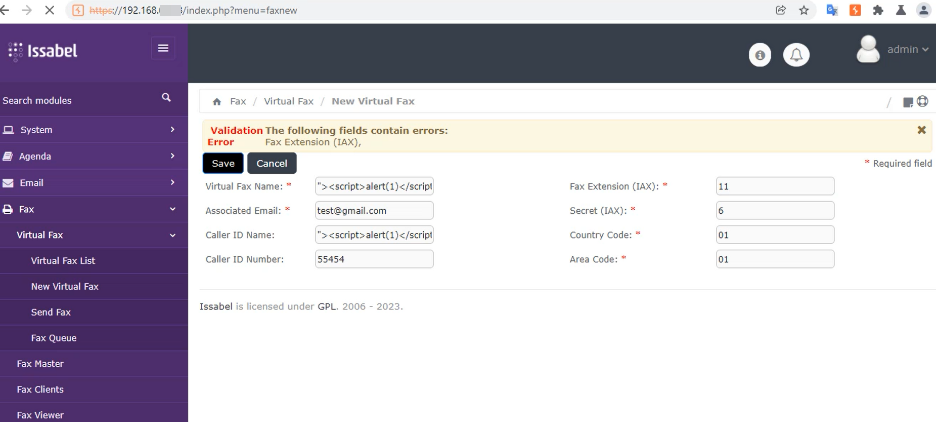
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…
 sahiloj/cve-2023-37597
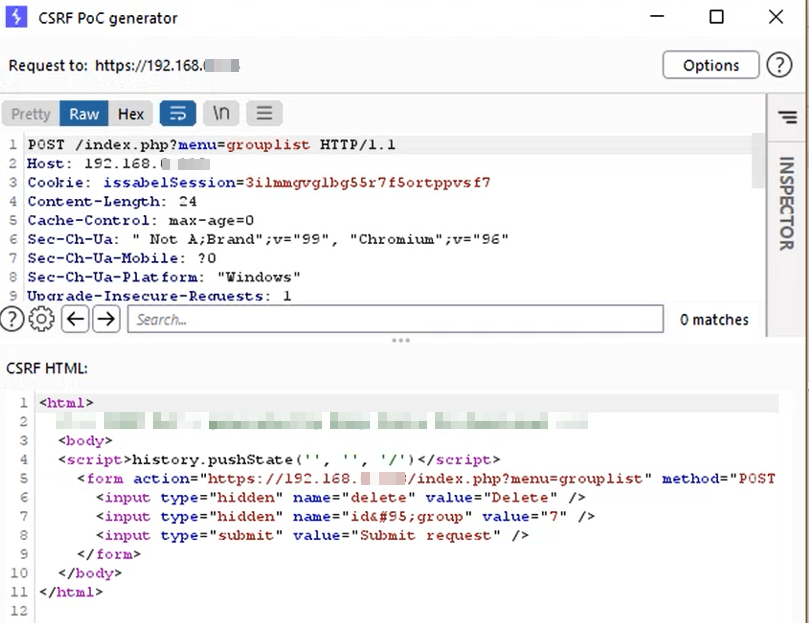
Issabel-pbx v 4.0.0-6 contains a Cross-Site Request Forgery (CSRF) vulnerability in its user group management functionality.
 sahiloj/cve-2023-37599
Issabel-pbx version 4.0.0-6 contains a Broken Access Control vulnerability that manifests as unauthenticated Directory Listing on the web interface.
 sahiloj/cve-2023-34839
CVE-2023-34839 is a Cross-Site Request Forgery (CSRF) vulnerability discovered in Issabel PBX version 4.0.0-6, a widely used open-source Unified…
 zdcslab/rubrics-as-an-attack-surface
Research code for Rubric-Induced Preference Drift (RIPD): evolutionary rubric search, benchmark-preserving selection, and DPO policy misalignment…
 simoesctt/-cve-2026-23829-ctt-mailpit-phase-reconstruction-
It's a CRLF injection in Mailpit's SMTP server — a classic data corruption vulnerability. But under CTT, it's not just a bug. It's a phase…
 iamwajd/cyber-attack-analysis
In-depth case study analyzing the 2020 Virgin Mobile KSA breach via CVE-2020-0688 exploitation, packet sniffing, and patch management failures, with…








