
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 amenti-labs/openentropy
Open-source entropy harvesting from unconventional hardware sources. Rust + Python SDK.
 d7ead/cve-2026-22722
A state-based logic vulnerability in VMWare Workstation Pro's Kernel NUIF
 0xblackash/cve-2014-6271
CVE-2014-6271
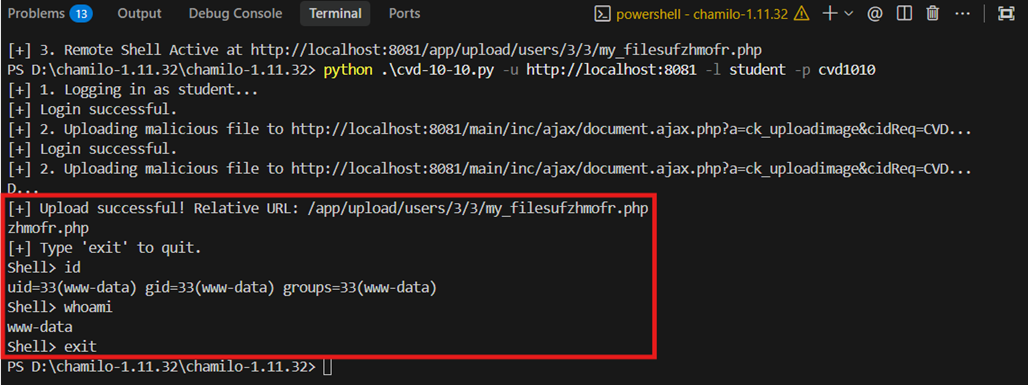 kx00007/cve-2026-29041
Hi, I’m K, This is my first CVE, which is a Remote Code Execution (RCE) vulnerability. It is the beginning of my journey as a security researcher.
 0xblackash/cve-2025-32463
CVE-2025-32463
 dwallener/entropicapublic
Public version of the Entropica repo
 knoveleng/redeval
[ICLR 2026] - Official repo for the paper: "RedBench: A Universal Dataset for Comprehensive Red Teaming of Large Language Models"
 jaycelation/cve-2026-25645
Insecure Temp File Reuse in extract_zipped_paths()
 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 d3b0j33t/cve-2026-2441-poc
Proof-of-concept for CVE-2026-2441, a Chrome CSS use-after-free leading to sandboxed renderer RCE. Includes three trigger methods, heap grooming, and…
 useaitechdad/openclaw-technical-analysis
This technical research and review is for educational purposes on public code and constitutes Fair Dealing under the Copyright Act (Canada).
 biranperetz/docling-core-cve-2026-24009
Technical write-up and PoC for CVE-2026-24009, demonstrating unsafe YAML loading in docling-core and practical mitigation paths.
 archana1122m/cve-disclosures
CVE-2026-3171 and CVE-2026-3170 vulnerability disclosure by Archana M
 airis101/cve-2025-55182-analysis
浅谈React Server Components RCE 漏洞分析
 canonicalmg/reverse-captcha-eval
Evaluation framework that tests whether large language models follow invisible Unicode-encoded instructions embedded in normal-looking text, with…
 facebookresearch/meta_secalign
Open-weight LLMs and training/evaluation code for defending against prompt injection attacks, with benchmarks for agentic tool-calling and…
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
 nullze/cve-2020-10558
Tesla Hack All Vehicles DoS Infotainment Touchscreen Interface CVE-2020-10558








