
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 valium007/cve-2026-56129
Proof-of-concept exploiting the Toshiba qiomem.sys driver to achieve arbitrary physical memory read/write from ring 3, with a companion writeup.
 mrk336/dns-mayhem-cve-2026-41096-deep-dive
In‑depth technical analysis of CVE‑2026‑41096, a critical heap overflow in Windows DNSAPI.dll enabling remote code execution via crafted DNS…
 bluedragonsecurity/cve-2026-23416-poc
POC for CVE-2026-23416 (linux kernel 6.17 – linux kernel 7 rc5) - vulnerability discovered by Antonius
 jlospinoso/gargoyle
Historical Windows temporal memory-state research artifact for studying time-bound memory observations, validation limits, and defensive visibility.
 chamsbouzaiene/ai-vuln-rediscovery-nginx-cve-2026-42945
Reproducible AI-assisted vulnerability rediscovery of CVE-2026-42945 in nginx, including technical analysis, PoC trigger, and patch validation for…
 0xblackash/cve-2026-42945
CVE-2026-42945
 memn0ps/illusion-rs
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)
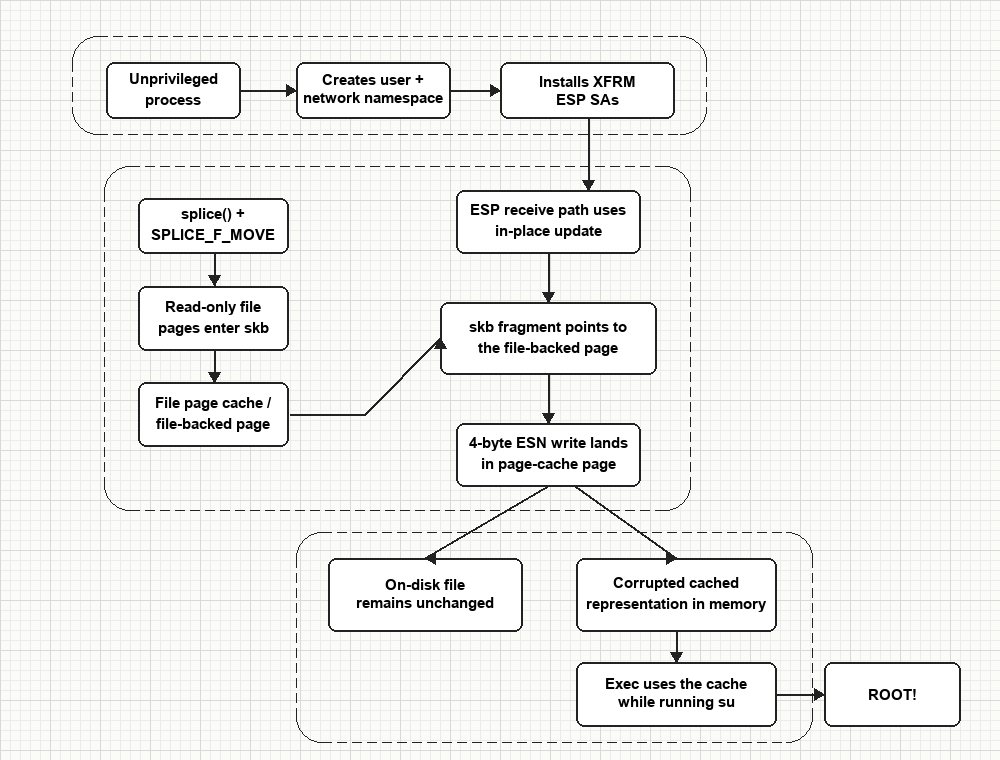 chernstepanov/dirtyfrag-for-dummies
Technical analysis and cleaned-up PoC for CVE-2026-43284 (Dirty Frag), a Linux kernel xfrm-ESP vulnerability enabling page cache corruption via…
 silverruler/copy-fail-cve-2026-31431
copy-fail-CVE-2026-31431
 linnemanlabs/dirtyfrag-arm64
arm64/aarch64 port of V4bel/dirtyfrag (CVE-2026-43284). ESP-only - rxrpc path kernel-oopses on arm64 due to flush_dcache_page
 azefzafyoussef/cve-2026-34621
Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…
 ard33/cve-2026-4255
Proof-of-concept for CVE-2026-4255, a DLL side-loading privilege escalation in Thermalright TR-VISION HOME, demonstrating PATH-based planting of…
 labrai/graphip-bench
Benchmark and library for evaluating model-extraction attacks and ownership defenses (watermarking, output perturbation, query detection) on graph…
 juanceresa/sift-kg
Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…
 meh098/cve-2026-24072-analysis
Technical analysis of CVE-2026-24072, a local privilege escalation in Apache HTTP Server mod_rewrite, including root cause, patches, and Dockerized…
 xrseccd/202605_dirty_frag
CVE-2026-43284 & CVE-2026-43500 discovered by Hyunwoo Kim
 olowostandard1/cve-2023-38831-winrar-vulnerability-analysis
This project is a cybersecurity research and analysis project focused on CVE-2023-38831, a critical WinRAR vulnerability that allows attackers to…
 canomer/cve-2025-54110-kernel-eop-poc
Project Date : Oct 2025 / PoC implementation for CVE-2025-54110 a Kernel-Level Integer Overflow Vulnerability in the Windows `NtQueryDirectoryObject`…








