
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 nishant-kumar-5173/cve-2024-5932
Proof-of-concept exploit for CVE-2024-5932, a PHP object injection vulnerability in the GiveWP WordPress plugin, enabling unauthenticated remote code…
 quangnh89/cve-2022-4262
Full technical analysis of CVE-2022-4262 including root cause identification, proof-of-concept exploit, and working exploit code for security…
 halcy0nic/cve-2022-36752
Proof of concept for CVE-2022-36752
 maherazzouzi/cve-2022-36162
Documentation of CVE-2022-36162: a local command injection vulnerability in hovacui PDF viewer 1.1.0 via the HOME environment variable and postsave…
 halcy0nic/cve-2022-34913
Proof of concept for CVE-2022-34913
 open-flaw/cve-2022-33171
CVE-2022-33171: TypeORM SQL Injection Vulnerability
 openxp-research/cve-2022-29380
2022-29380
 egebalci/cve-2022-29154
HIP2022 presentation materials.
 crackercat/cve-2022-26927
A proof-of-concept font with a write-up attached.
 privlabs/cve-2025-69690-cve-2025-69691
Authenticated RCE in Netgate pfSense CE 2.7.2 and 2.8.0
 nerowander/cve-2022-25845-exploit
Java-based exploit for CVE-2022-25845 (Fastjson auto-type bypass RCE) with accompanying analysis PDF and reference articles for educational study.
 jpeisach/cve-2022-24713-poc
Proof of Concept/Test for CVE-2022-24713 on Ubuntu
 seymanurmutlu/cve-2022-24086-cve-2022-24087
Educational analysis of Magento and Adobe Commerce RCE vulnerabilities CVE-2022-24086 and CVE-2022-24087, including technical write-up and…
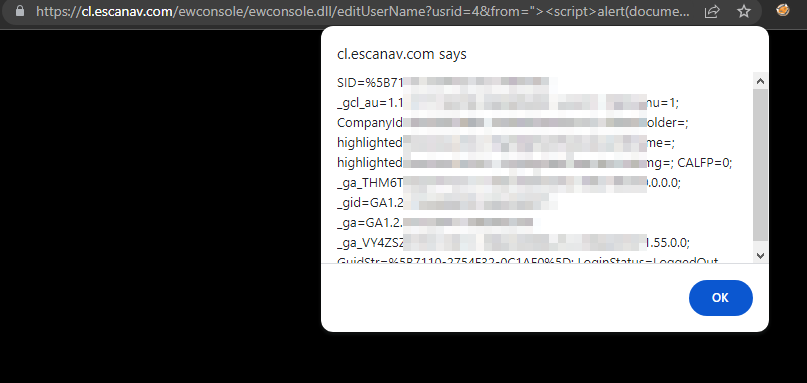 sahiloj/cve-2023-31703
A reflected Cross-Site Scripting (XSS) vulnerability exists in the Edit User functionality of the Microworld Technologies eScan Management Console…
 sahiloj/cve-2023-33730
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…
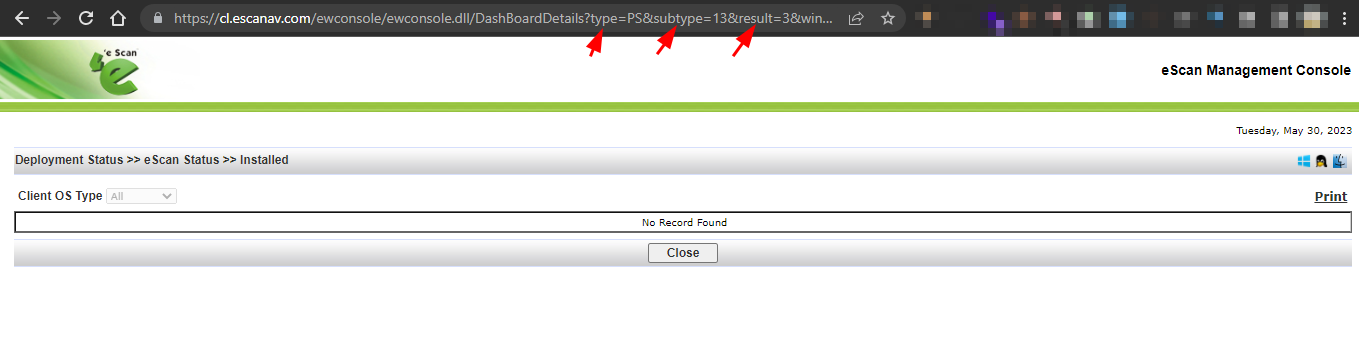 sahiloj/cve-2023-33731
A Reflected Cross-Site Scripting (XSS) vulnerability was discovered in the eScan Management Console (version 14.0.1400.2281) developed by Microworld…
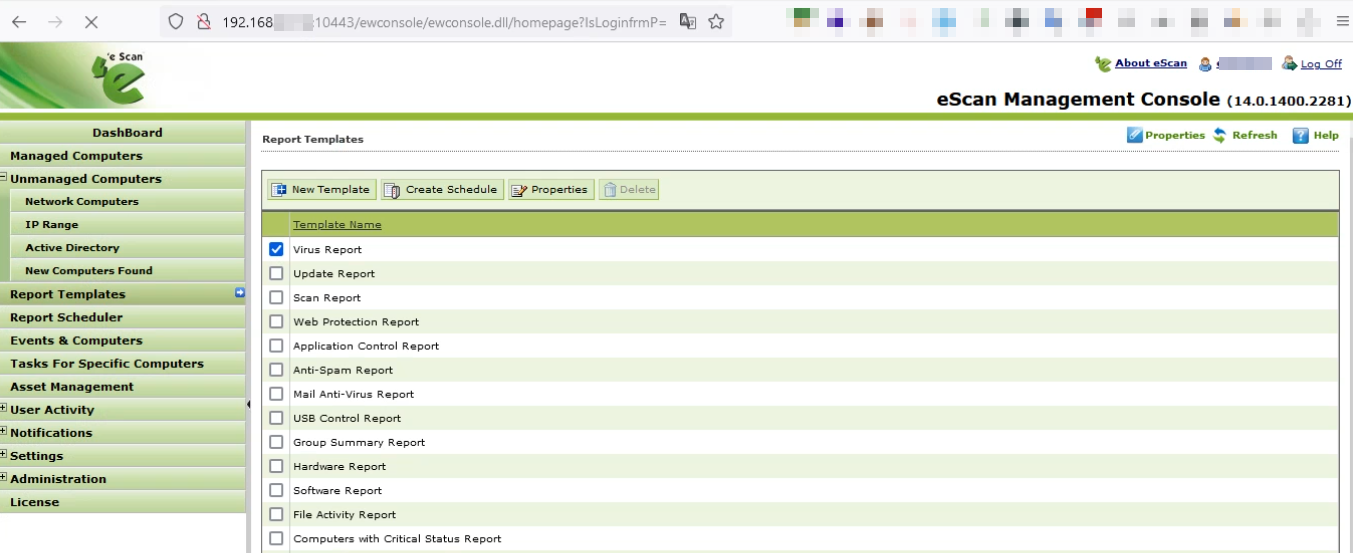 sahiloj/cve-2023-34835
A Reflected Cross-Site Scripting (XSS) vulnerability was discovered in the Microworld Technologies eScan Management Console, version 14.0.1400.2281.
 sahiloj/cve-2023-33732
CVE-2023-33732 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console, version…








