
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
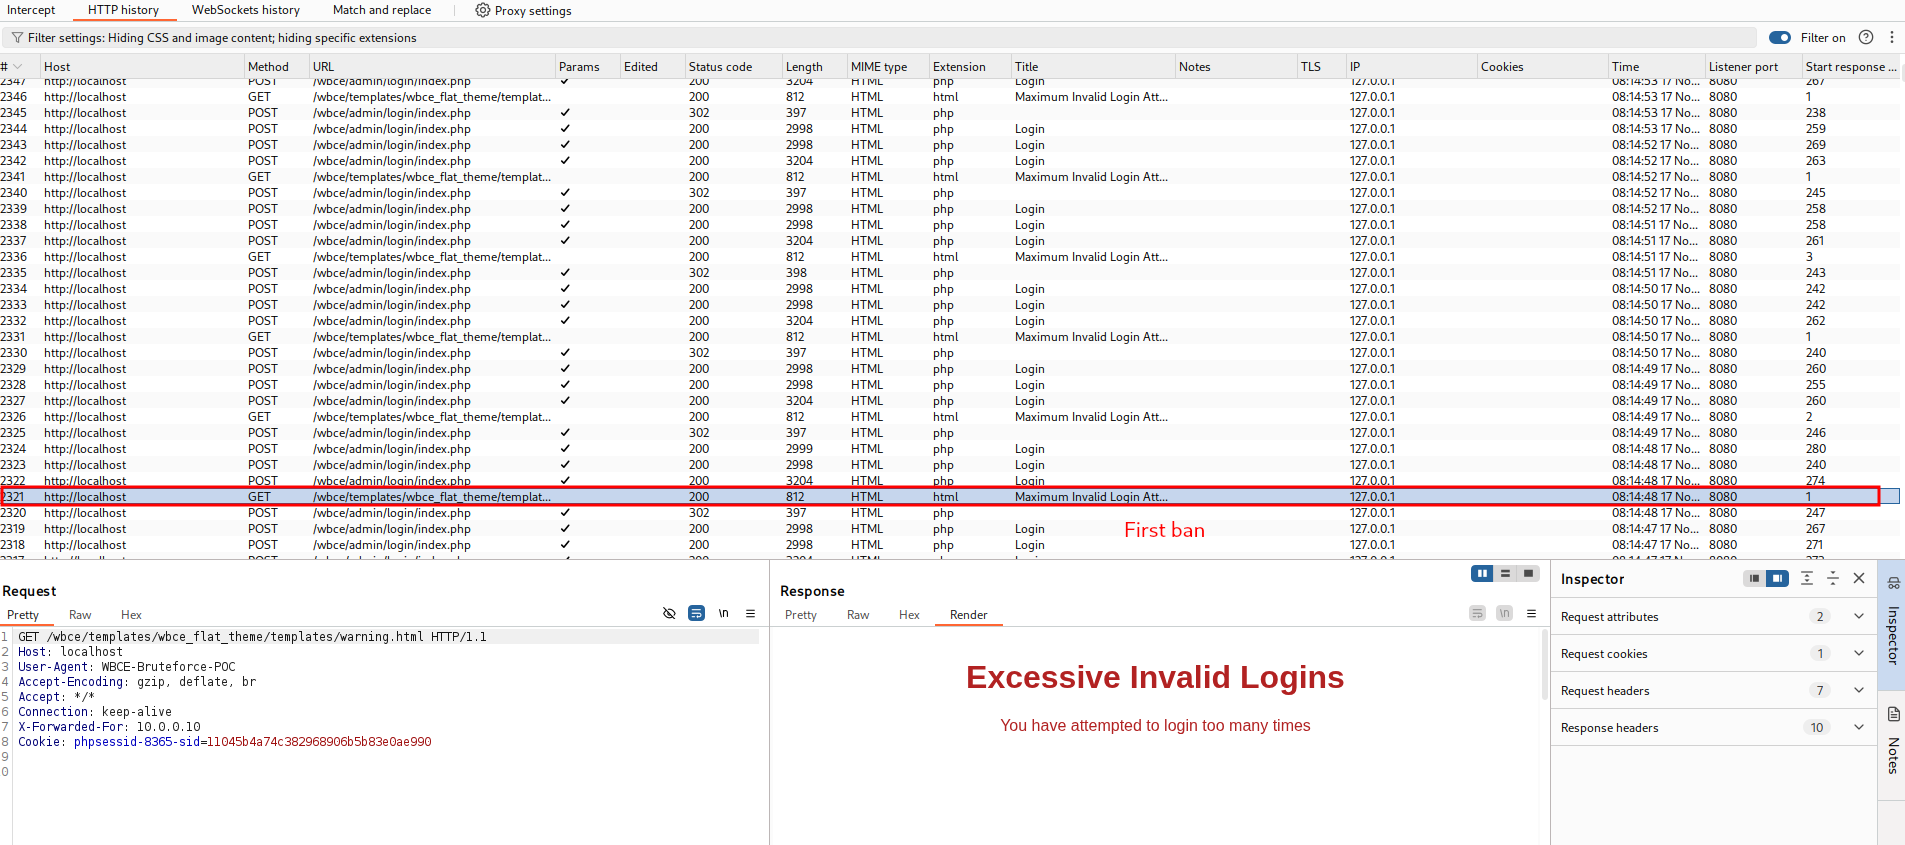
 lukasz-rybak/cve-2025-66204
Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…
 rishavand1/cve-2025-65791
CVE-2025-65791 — Command Injection in ZoneMinder
 vincenzo-emanuele/cve-2025-65640
Public advisory for CVE-2025-65640: Stored XSS vulnerability in Globe Document Intelligence.
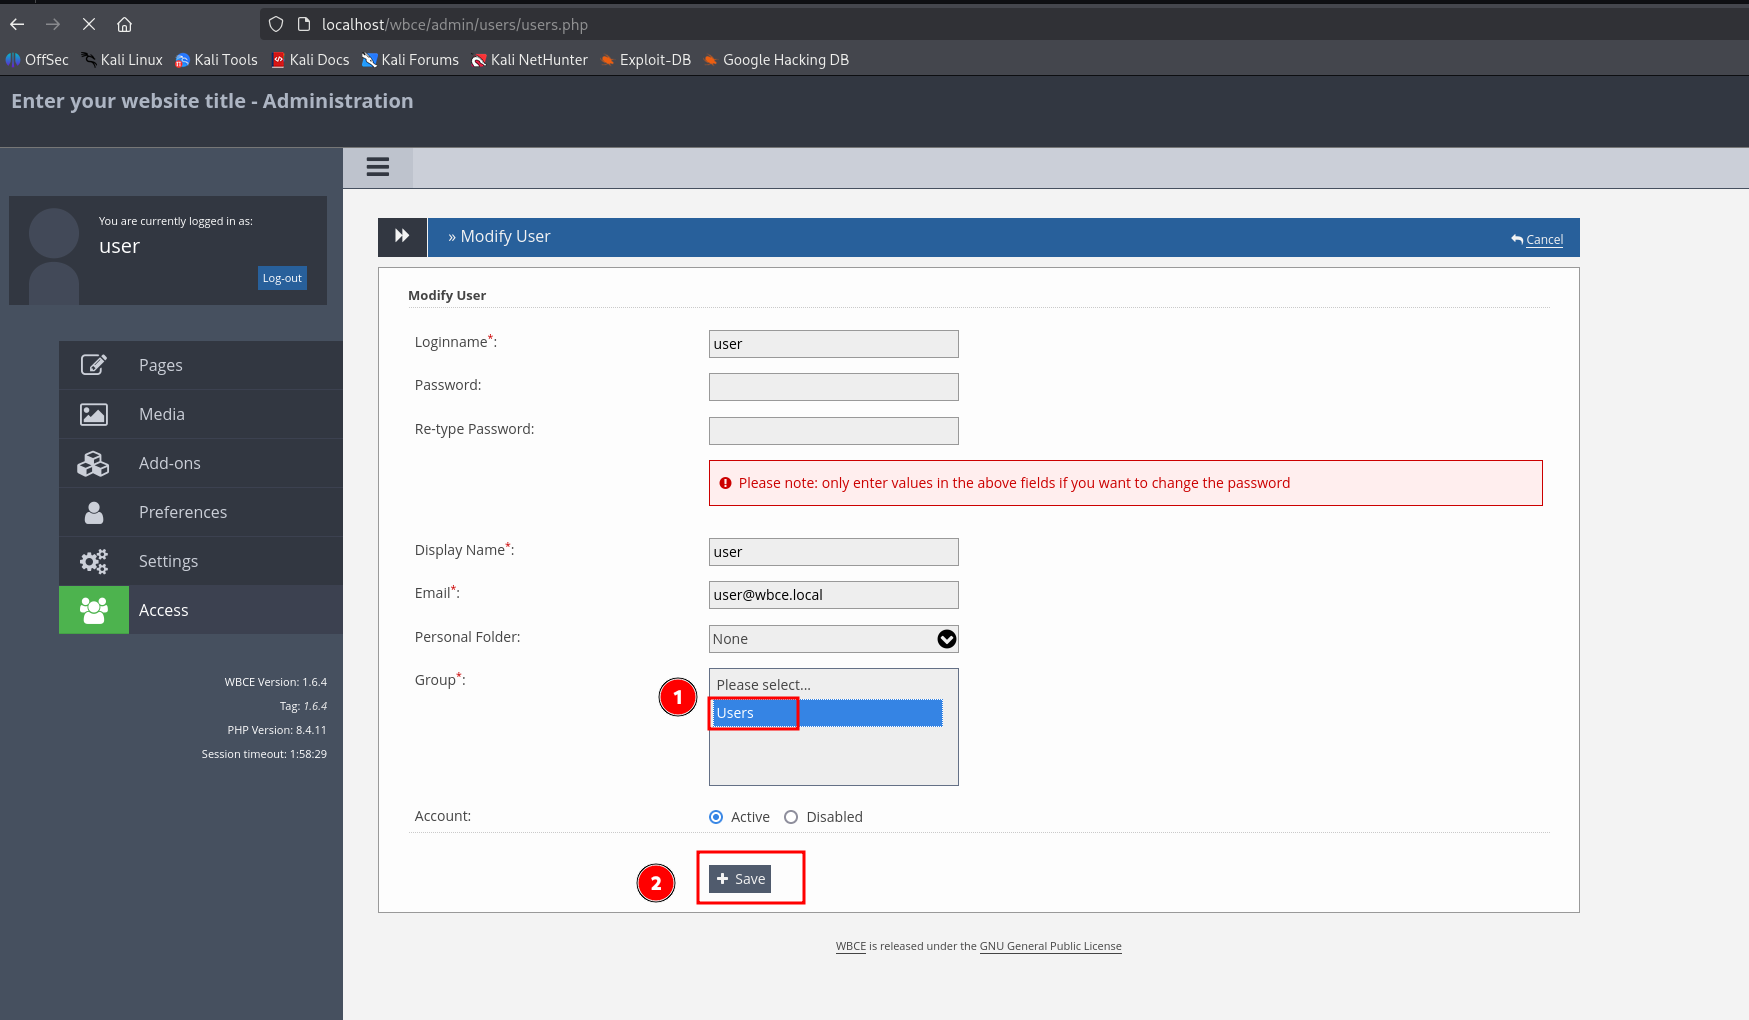 lukasz-rybak/cve-2025-65094
Proof-of-concept for CVE-2025-65094: privilege escalation via IDOR in WBCE CMS. Demonstrates group ID manipulation to gain admin access, with…
 pescada-dev/cve-2025-61505
Insecure Deserialization in e107 CMS install.php
 mrtiz/cve-2023-35671
Android App Pin Security Issue Allowing Unauthorized Payments via Google Wallet
 dotadrien/cve-2025-60654
Proof-of-concept for CVE-2025-60654: stored cross-site scripting (XSS) in Script Pag ad description field. Demonstrates filter bypass using HTML tags…
 dotadrien/cve-2025-60656
Stored XSS vulnerability proof-of-concept for Script Pag's 'Recent Ads' module, exploiting unsanitized double quotes in image URL fields to execute…
 h4zaz/cve-2025-60503
XSS vulnerability on ultimatefosters
 lytnc/cve-2025-59284-poc
Proof of concept for CVE-2025-59284 libarchive exploit
 psycho-prince/cve-2025-56513-nicehash-update-chain-compromise
Critical supply-chain vulnerability research on NiceHash QuickMiner update mechanism (CVE-2025-56513). Includes technical analysis, attack scenarios,…
 ocmenog/cve-2025-55998
Documented reflected XSS vulnerability (CVE-2025-55998) in Mezereon's Smart Search and Filter app for Shopify and BigCommerce, with proof-of-concept…
 wrathfuldiety/cve-2025-56311
CSRF vulnerability in FD602GW-DX-R410 router allows remote attackers to reboot the device via a crafted POST request to /boaform/admin/formReboot…
 ish2yu/cve-2025-55780
Null Pointer Dereference in MuPDF , First CVE discovered by me
 goldenticketlabs/cve-2025-55349
repo for CVE-2025-55349
 rat5ak/cve-2025-55182-react2shell-rce-poc
This repository documents research into deserialization behavior within Next.js React Server Components (RSC) using the Flight protocol. It focuses…
 porsellaj/cve-2025-55182-react2shell-analysis
Technical analysis of CVE-2025-55182 (React2Shell RCE vulnerability)
 orgito1015/cve-2025-55182-rce-exploit
More exploit-focused; great for security research repos.








