
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 wlibang/cve-2024-38077
CVE-2024-38077,本仓库仅用作备份,
 keraattin/cve-2026-35031
Critical path traversal to RCE vulnerability in Jellyfin Media Server (CVSS 9.9). Includes proof-of-concept exploit, technical analysis, and…
 n132/cve-2025-68325
PoC CVE-2025-68325
 h3raklez/cve-2025-14321
Proof-of-concept demonstrating a Use-After-Free vulnerability in Firefox's RTCEncodedFrameBase via WebRTC Encoded Transforms, enabling heap…
 halcy0nic/cve-2022-34913
Proof of concept for CVE-2022-34913
 quyt0/cve-2019-18935-exploit-study
In-depth study of CVE-2019-18935 affecting Telerik UI for ASP.NET AJAX. Covers .NET deserialization vulnerability, RadAsyncUpload handler, gadget…
 mrmtwoj/react2shell-cve-2025-55182
Educational / research tool related to React / Next.js vulnerability CVE‑2025‑55182 (“React2Shell”).
 hffaust/cve-2021-42574_and_cve-2021-42694
Demonstration and documentation of CVE-2021-42574 and CVE-2021-42694, Unicode bidirectional algorithm vulnerabilities enabling invisible source code…
 afine-com/cve-2022-35501
Stored Cross-site Scripting (XSS) in blog-post creation functionality in Amasty Blog Pro for Magento 2
 ard33/cve-2026-4255
Proof-of-concept for CVE-2026-4255, a DLL side-loading privilege escalation in Thermalright TR-VISION HOME, demonstrating PATH-based planting of…
 alyssa-o-herrera/cve-2018-7197
CVE-2018-7197 Write up
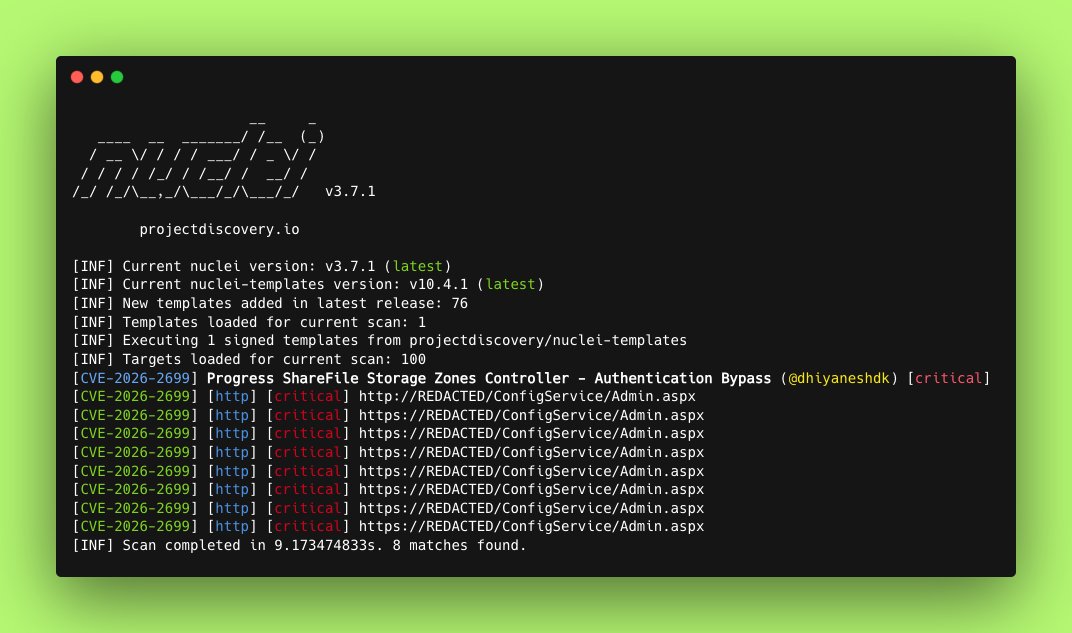 0xblackash/cve-2026-2699
CVE-2026-2699
 majdae/cve-2025-47812-research
Academic research repository analyzing CVE-2025-47812, a critical RCE vulnerability in Wing FTP Server via Lua injection, including static/dynamic…
 jeromeyoung/cve-2021-43141
Information about CVE-2021-43141, a reflected XSS in the plan_application section.
 vett3x/smb-linux-cve-2025-37899
Technical analysis of CVE-2025-37899: a use-after-free vulnerability in Linux kernel's ksmbd SMB module enabling remote code execution. Includes…
 oscerd/cve-2026-46590
Reproducer for CVE-2026-46590: Apache Camel camel-pqc key-lifecycle unsafe deserialization (FileBasedKeyLifecycleManager legacy .key migration via…
 oscerd/cve-2026-46584
Reproducer for CVE-2026-46584: Apache Camel camel-mail mail.smtp.* header injection enabling credential theft via on-path SOCKS interception (fixed…
 nanopathi/linux-4.19.72_cve-2020-29370
Linux kernel version 4.19.72 with a specific patch for CVE-2020-29370, intended for vulnerability analysis and exploitation research.








