
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
 lorenzofradeani/cve-2026-40776
CVE-2026-40776 — Broken Access Control + IDOR in WordPress Eventin (wp-event-solution) <= 4.1.8
 crackercat/cve-2021-26411
Proof-of-concept exploit for CVE-2021-26411, an Internet Explorer memory corruption vulnerability enabling remote code execution.
 weidongl74/cve-2015-2315-report
Simulation code and report for CVE-2015-2315, demonstrating the vulnerability exploitation scenario for educational analysis.
 izdiwho/cve-2022-40317
Stored XSS proof-of-concept for OpenKM notes section, demonstrating a javascript: bypass of sanitization rules, with CVSS 3.1 scoring and…
 amnsecurity/osticket-stored-xss-security-assessment
Professional vulnerability assessment report for osTicket stored cross-site scripting, including business impact, remediation, and mitigation…
 halcy0nic/cve-2023-38632
Proof of concept for CVE-2023-38632
 xyddnljydd/cve-2020-1066
Exploit code for CVE-2020-1066 with accompanying blog analysis, demonstrating a specific Windows privilege escalation vulnerability.
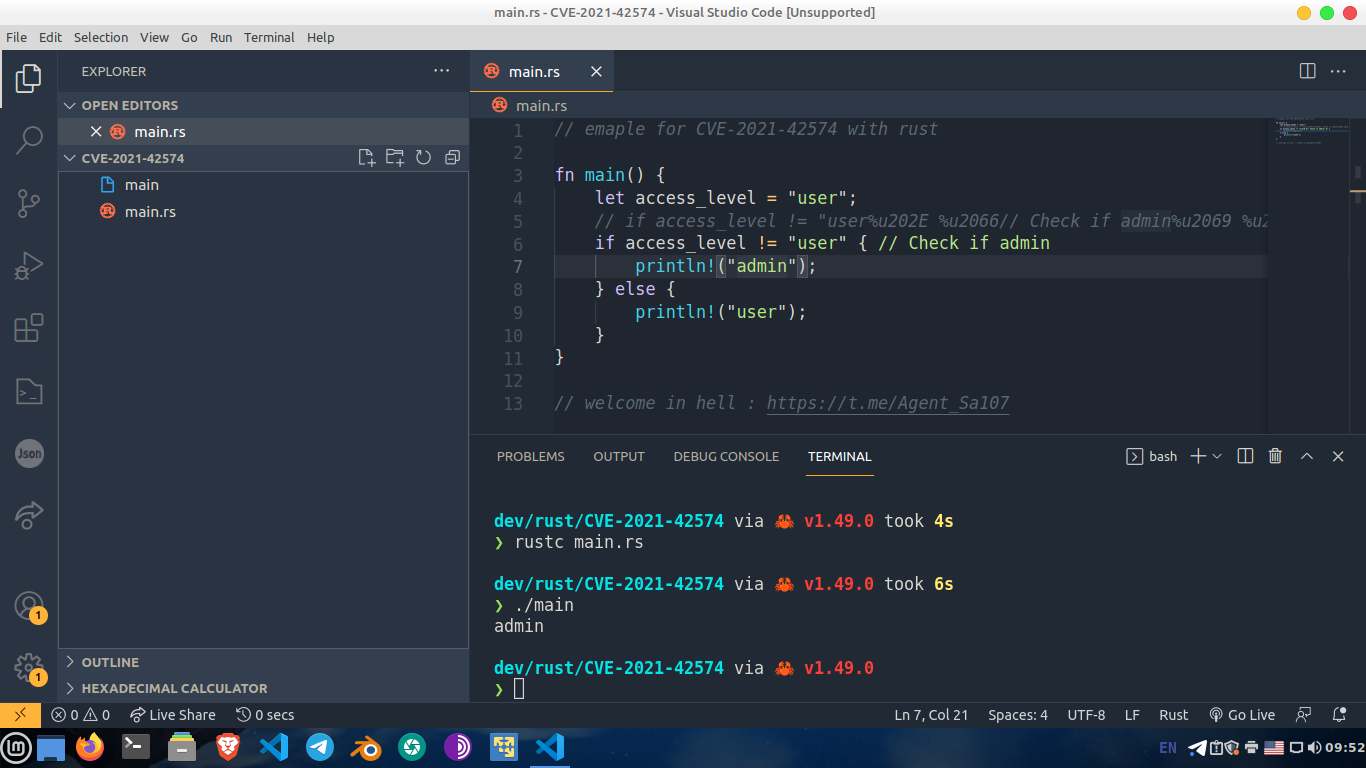 waseeld/cve-2021-42574
Demonstrates the Trojan Source vulnerability (CVE-2021-42574) by generating source code with invisible Unicode control characters that alter compiler…
 rarar0/kde_vuln
CVE-2018-6791 Troubleshooting
 r4bbit-r4/directus-preso
Presentation about CVE-2025-55746
 cuijiung/dubbo-cve-2023-23638
PoC exploit for Apache Dubbo CVE-2023-23638, a Hessian deserialization vulnerability enabling JNDI injection. Includes analysis articles and requires…
 zedocun/sharepoint-toolshell-cve-2025-53770-incident-analysis
Technical analysis of a SharePoint ToolShell (CVE-2025-53770) exploitation attempt involving RCE, webshell deployment, and MachineKey extraction.
 tfawnies/cve-2026-64633
Generated CVE-2026-64633 analysis payloads with treatment/control document variants and a manifest mapping IDs and pairs for reproducing the…
 theopaid/cve-2026-66754-remote-denial-of-service-via-reachable-assertion-in-url-prefix-handling-rouille-
Security Advisory: Remote Denial of Service via Reachable Assertion in URL Prefix Handling (rouille)
 zebberncve/cve-2026-26832
Advisory for node-tesseract-ocr ⌯⌲ 50 000 weekly downloads
 lukasz-rybak/cve-2026-23499
CVE-2026-23499 - Saleor vulnerable to stored XSS via Unrestricted File Upload
 abhinavagarwal07/abhinavagarwal07.github.io
RingWraith: CVE-2026-33150 and CVE-2026-33179 — Use-After-Free and NULL Dereference in libfuse io_uring
 mernjsb/cve-2024-55182
Detailed technical analysis of CVE-2025-55182 (React2Shell), a critical RCE vulnerability in React Server Components, including affected packages,…








