
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
 mmionf/copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel vulnerability affecting multiple distributions, with a technical writeup and tested…
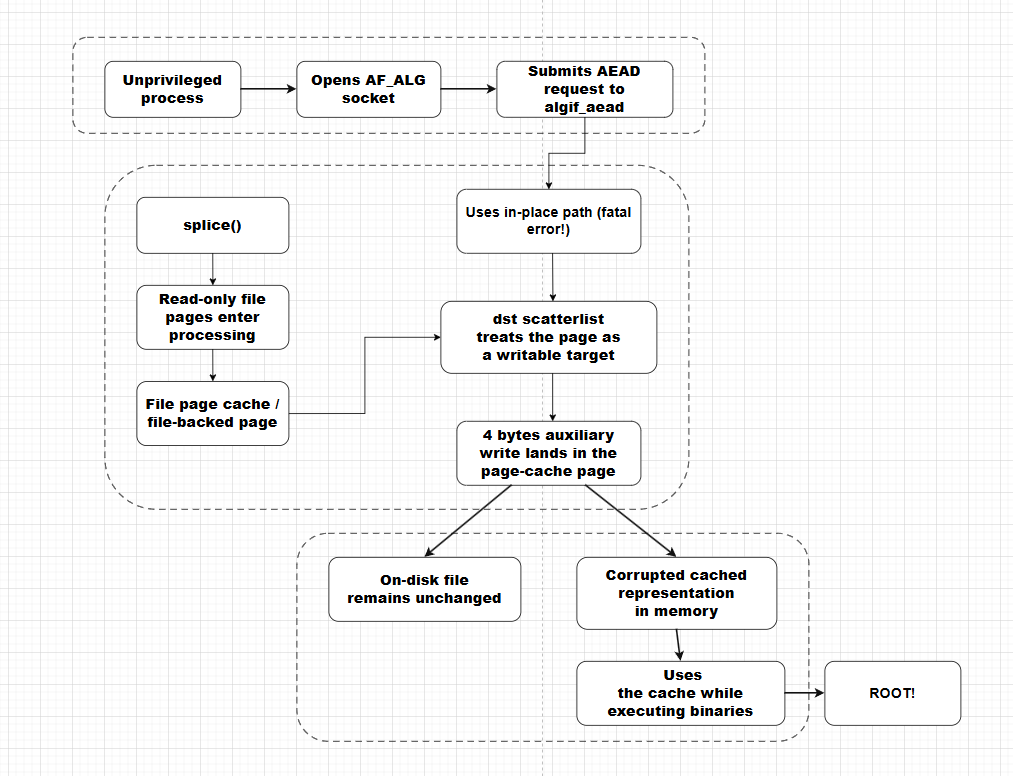 chernstepanov/copyfail-for-dummies
Research notes and proof-of-concept for Linux kernel CVE-2026-31431, documenting the AF_ALG splice() page cache corruption bug with source artifacts…
 frawlaboy/cve-2026-39973-poc
Proof of concept (builder) for CVE-2026-39973 (apktool)
 cesarbtakeda/pp_cve-2024-38998
Analyzes CVE-2024-38998, a prototype pollution vulnerability in requirejs 2.3.6, demonstrating how malicious config inputs can lead to DoS, RCE, or…
 biranperetz/docling-core-cve-2026-24009
Technical write-up and PoC for CVE-2026-24009, demonstrating unsafe YAML loading in docling-core and practical mitigation paths.
 oscerd/cve-2026-71300
Proof-of-concept reproducer for Apache Camel camel-atmosphere-websocket dispatch header injection (CVE-2026-71300), demonstrating how an injected…
 hatriot/token-priv
Token Privilege Research
 specterops/presentations
SpecterOps Presentations
 g4sp4rcs/cve-2026-42980-poc
Public exploit and research material for CVE-2026-42980, a Windows kernel WMI integer-underflow vulnerability enabling local privilege escalation to…
 yardenshafir/conference_talks
Slides from various conference talks
 ait-aecid/rootkit-detection-ebpf-time-trace
Detection of rootkit file hiding activities through analysis of shifts in kernel function execution times.
 00052/spectre-attack-example
2018年1月2日 (CVE-2017-5753 和 CVE-2017-5715) "幽灵" Spectre 漏洞利用
 passtheticket/vulnerability-research
 fs0c-sh/nagios-xi-5.7.5-bugs
Bugs reported to Nagios XI
 nishanthanand21/cve-2024-32002-poc
PoC of CVE-2024-32002 - Remote Code Execution while cloning special-crafted local repositories
 theethat-thamwasin/cve-2025-56399
An authenticated Remote Code Execution (RCE) vulnerability in laravel-file-manager v3.3.1 and below allows attackers with access to the file manager…
 askyeye/cve-2023-0045
PoC and write-up for CVE-2023-0045: bypasses Linux prctl/seccomp Spectre-BTI mitigations using BTB poisoning and Flush+Reload to leak process secrets.
 imxur/cve-2026-48908-joomla-sp-page-builder-rce
Technical analysis and advisory for CVE-2026-48908: Unauthenticated Arbitrary File Upload to RCE in JoomShaper SP Page Builder.








