
 #1
Tools for capturing, inspecting, and analyzing network traffic in real-time or from capture files.
Kitploit recommended

 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…
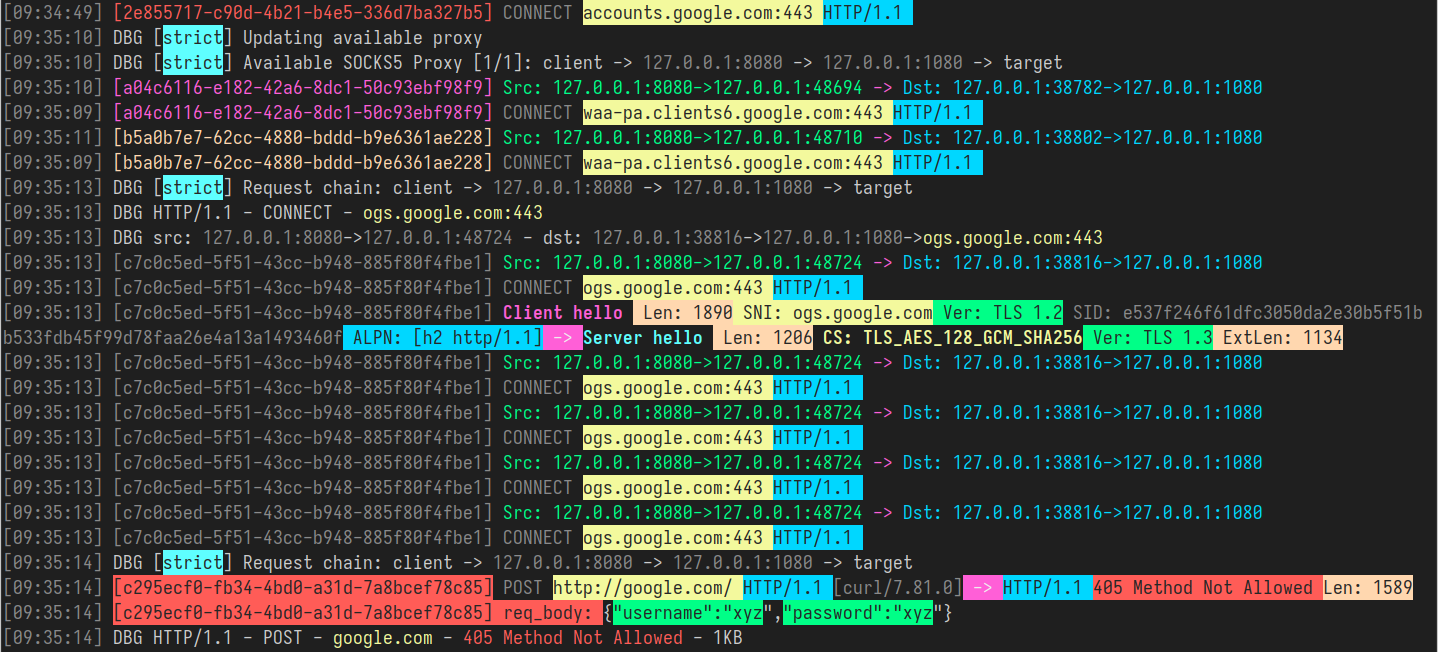 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
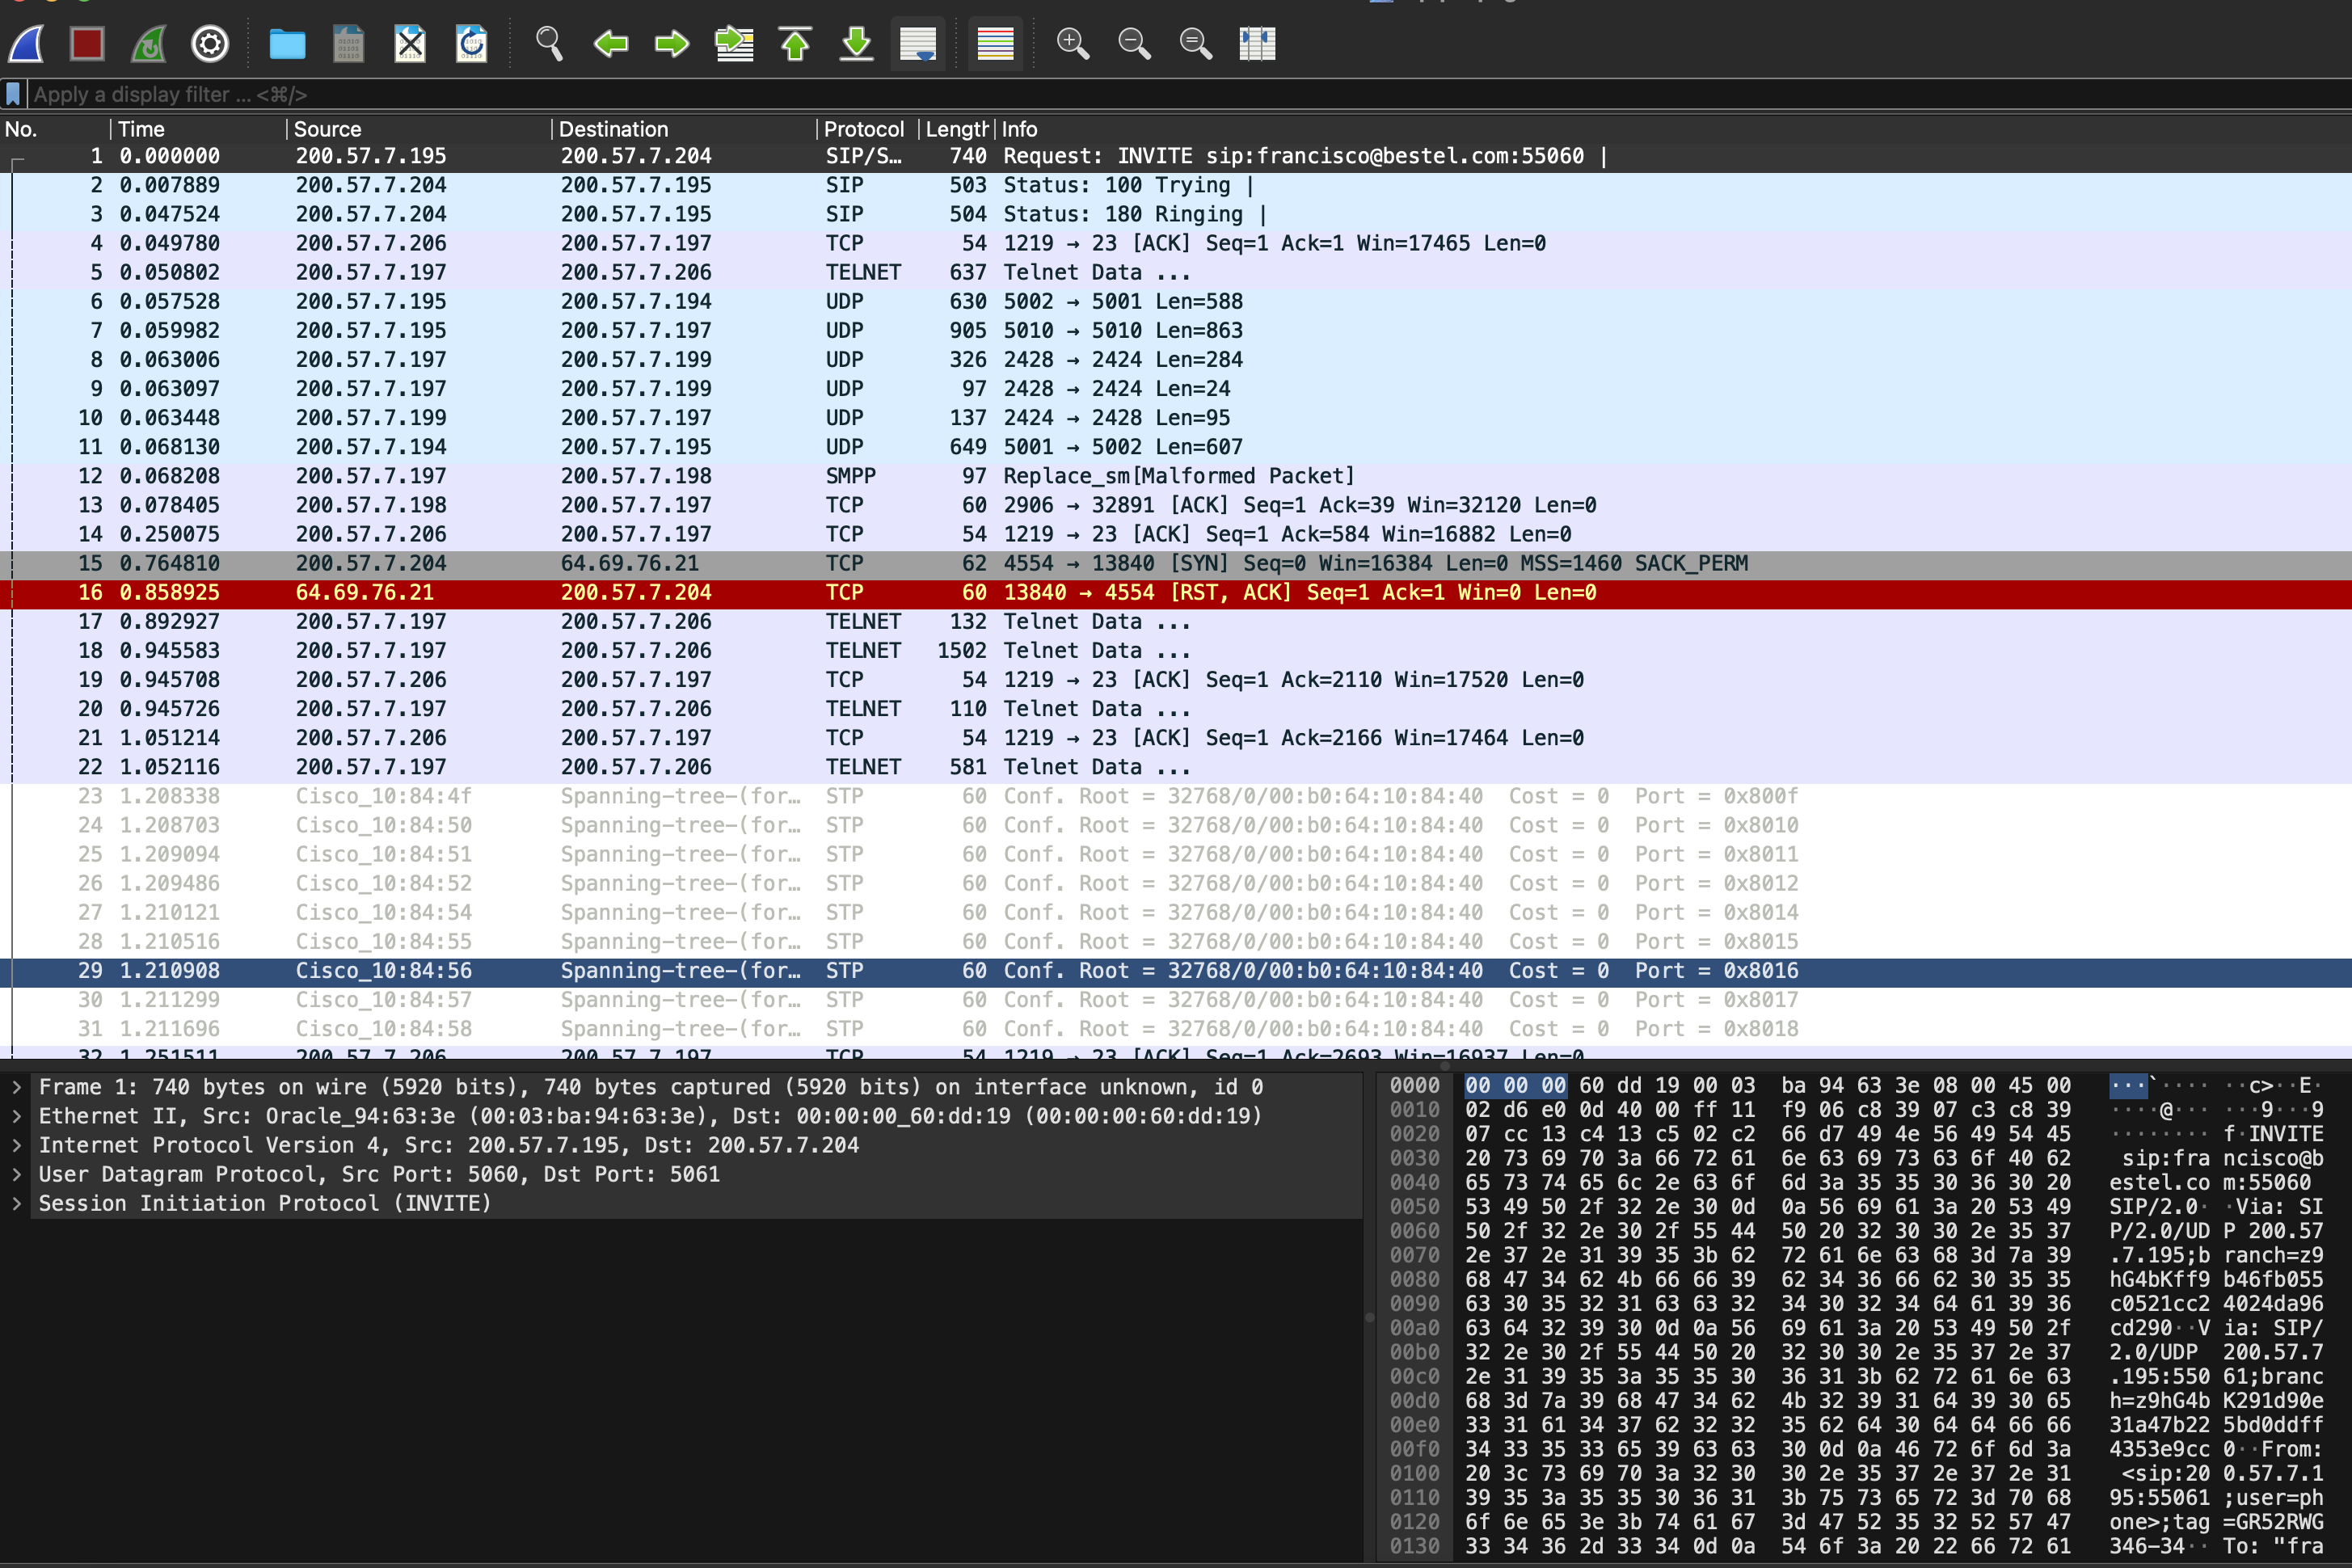 alperenugurlu/nac_bypass_agent
This function combines all the above functions and takes necessary information from the user to change the IP and MAC address, start the responder…
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
 eldraco/sapito
A mDNS sniffer and interpreter.
 cq674350529/pocs_slides
my advisory, poc, slides and scripts related to IoT/protocol security
 7etsuo/tetsuo-pulse
Tetsuo Socket Library
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
 onyks-os/transparenttorproxy
A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
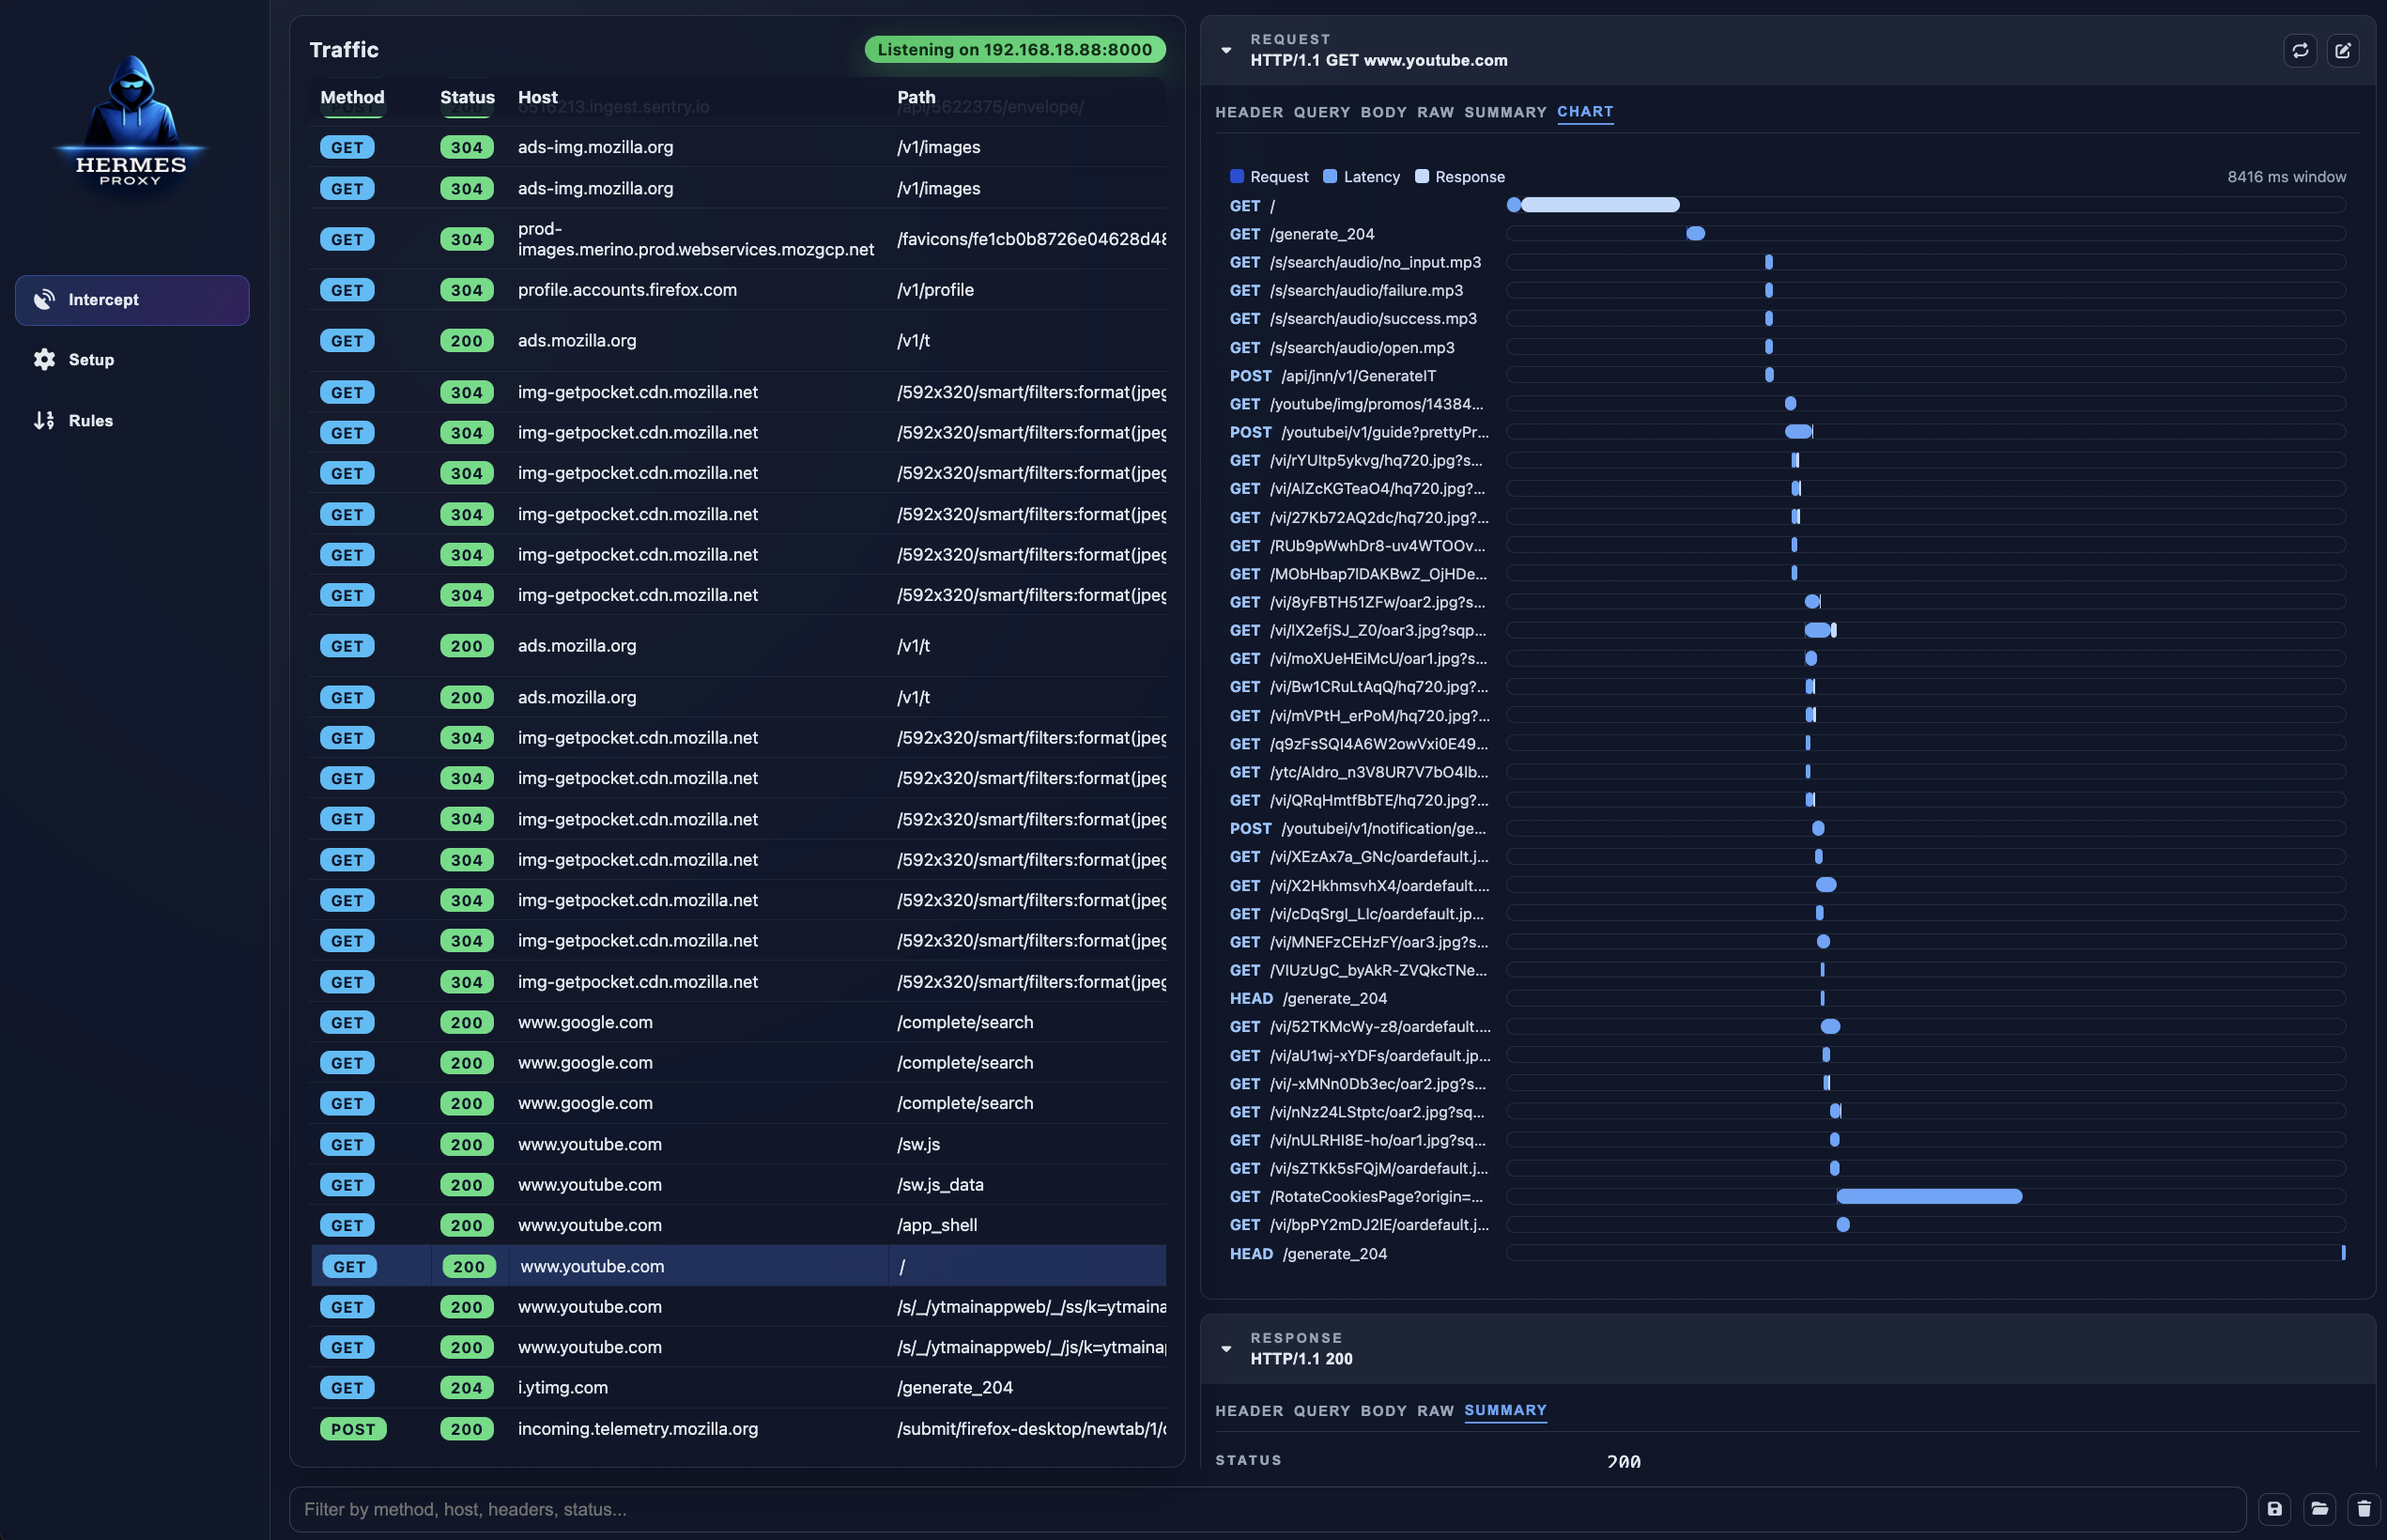 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
 husam212/mitmer
Automated man-in-the-middle attack tool.
 petabi/sniffles
Sniffles: Packet Capture Generator for IDS and Regular Expression Evaluation
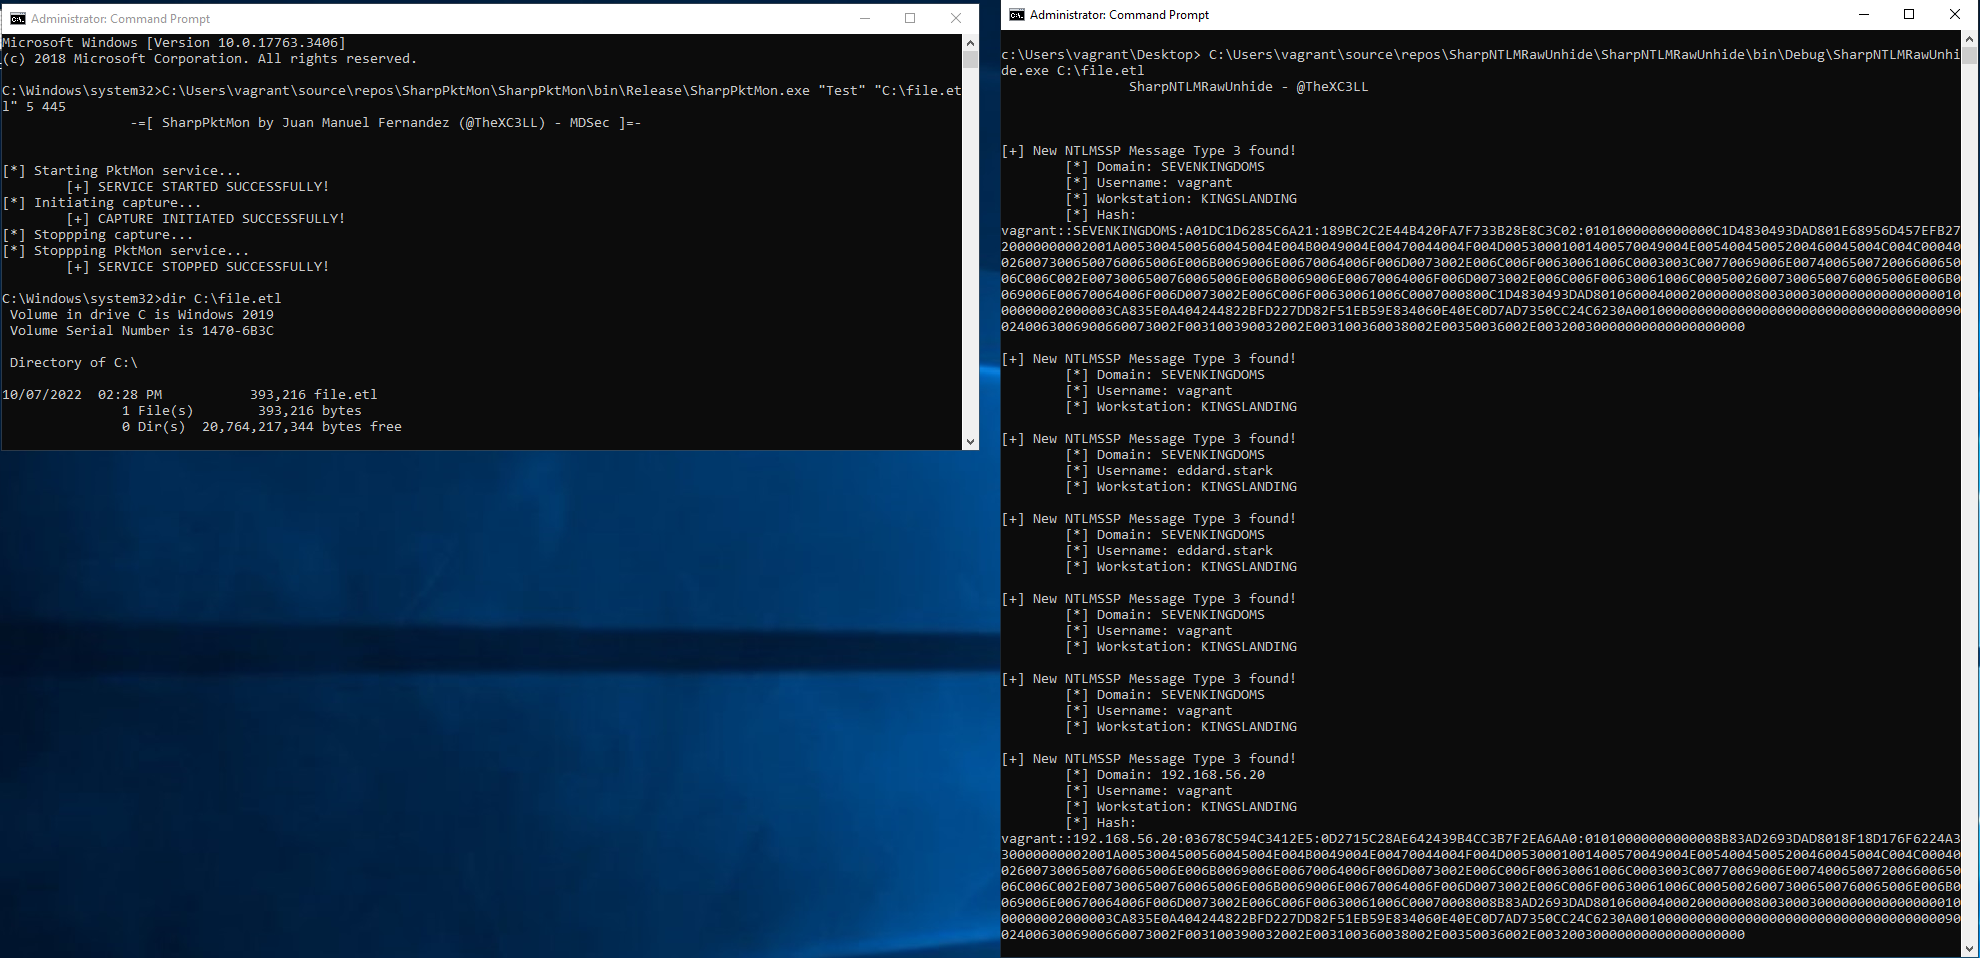 x-c3ll/sharpntlmrawunhide
C# version of NTLMRawUnHide
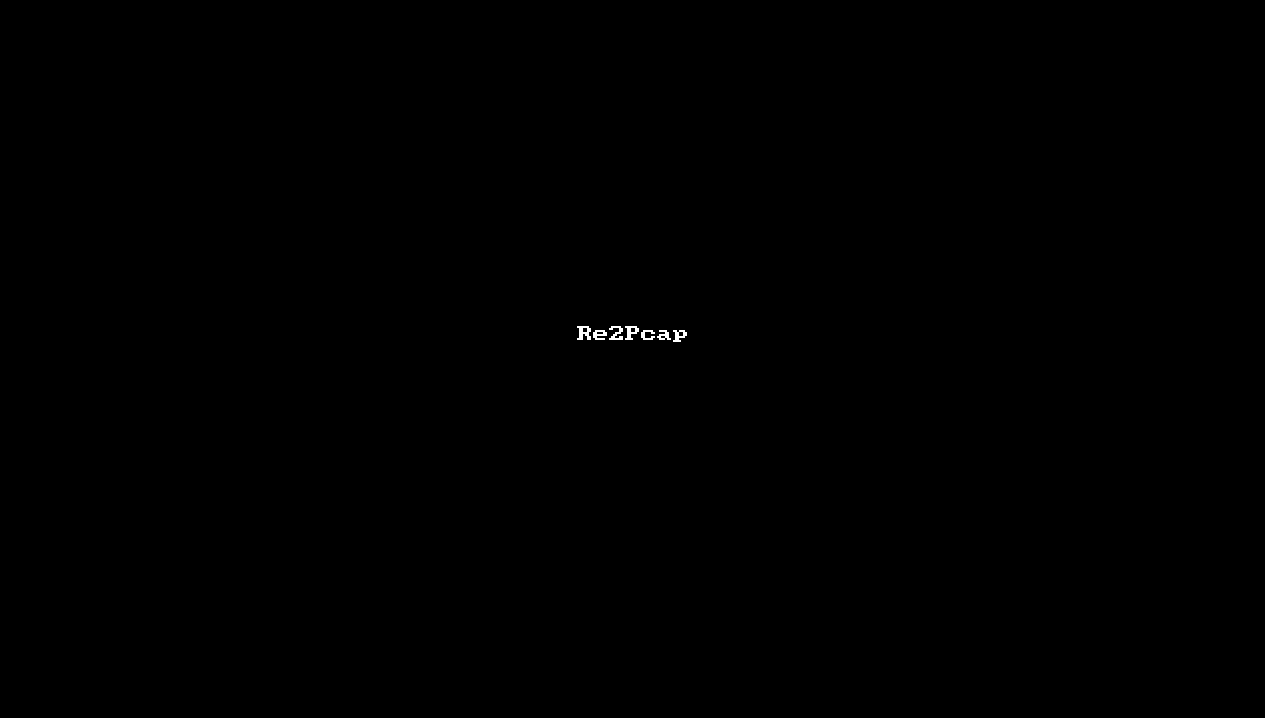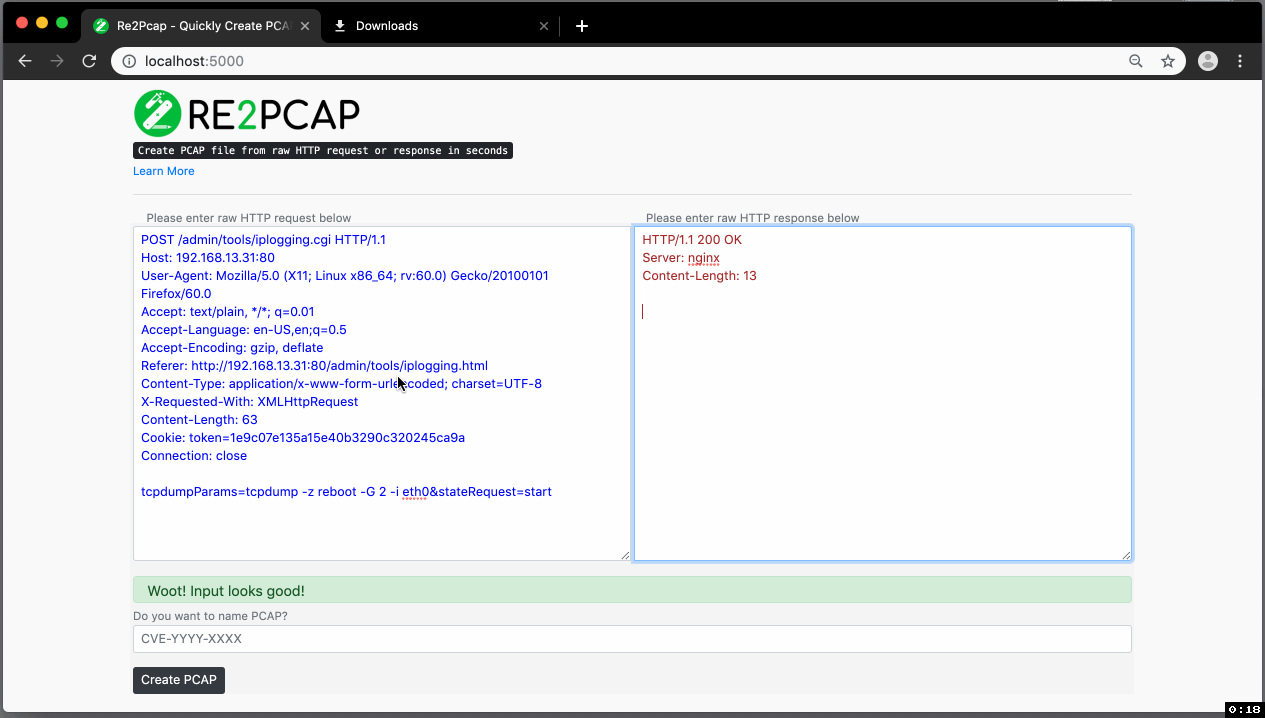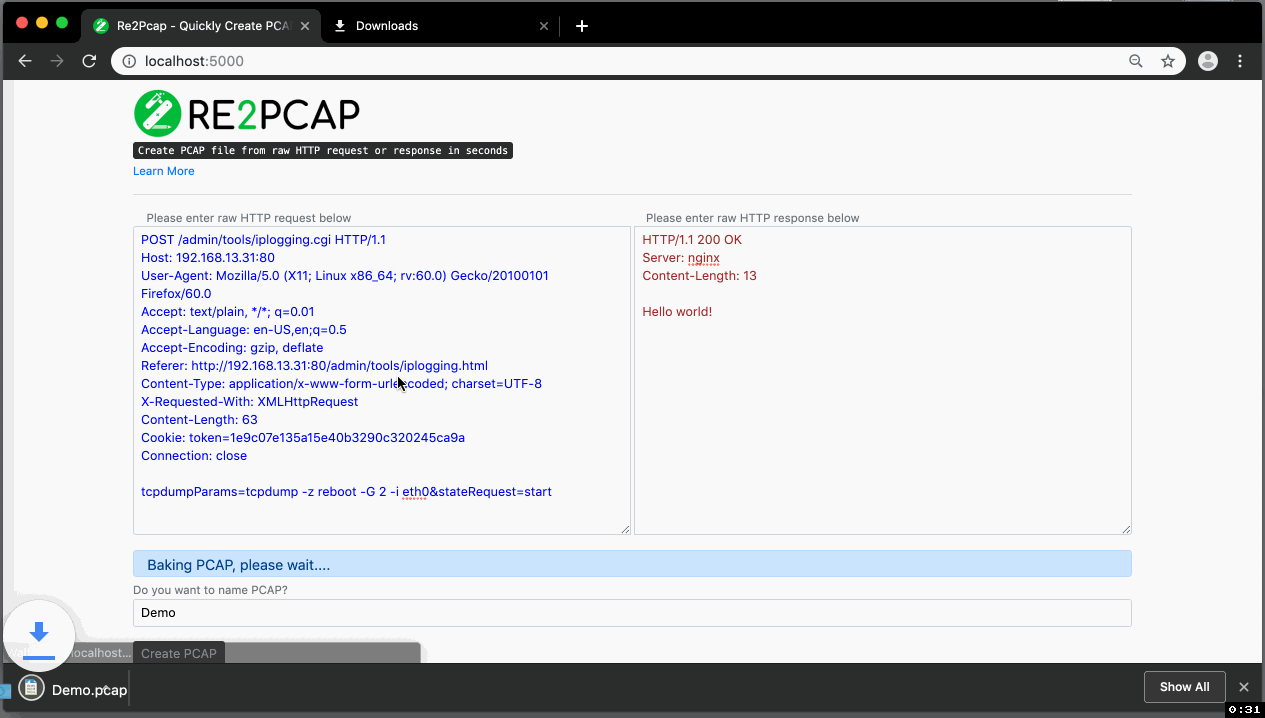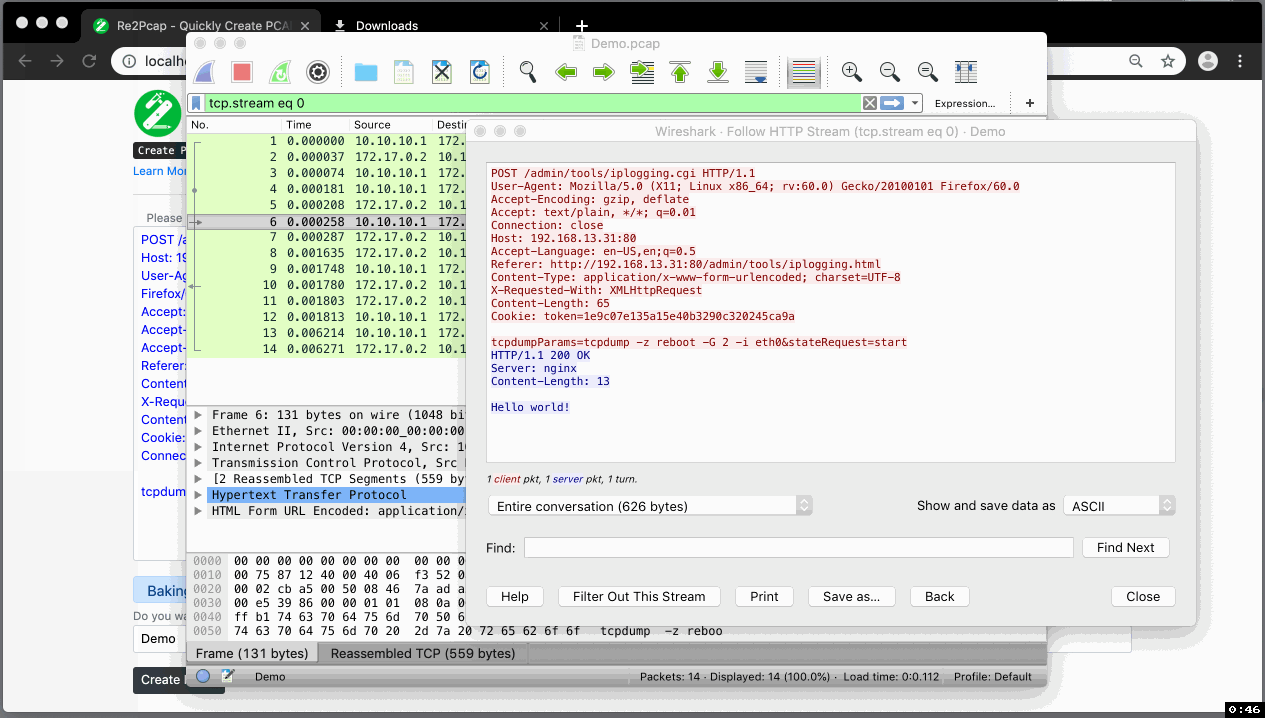 cisco-talos/re2pcap
Convert raw HTTP requests/responses into PCAP files for testing Snort IDS rules and network security analysis. Supports Docker deployment and…
 leonward/openfpc
OpenFPC, Open Source Full Packet Capture
 exbotanical/brutus
extensible exploitation framework shipped on a modular multi-tasking architecture
 unixpickle/cve-2018-4407
Crash macOS and iOS devices with one packet
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.








