
 #1
Tools for analyzing, monitoring, and securing network infrastructure and protocols.
Kitploit recommended
 azet/cve-2014-3466_poc
Proof of Concept for CVE-2014-3466 (GnuTLS buffer overflow: session id length check)
 atea-redteam/cve-2023-20198
CVE-2023-20198 Checkscript
 sobri3195/-pegasus-suite
A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.
 lupovis/honeypot-for-cve-2025-59287-wsus
Defensive PoC decoy for CVE-2025-59287 (WSUS) - emulates WSUS endpoints, captures request bodies and metadata, saves evidence for forensic analysis,…
 jgajek/killasa
Exploit tool for CVE-2016-1287 that tests Cisco ASA devices by sending crafted IKEv2 fragments with invalid lengths to trigger denial of service.
 jas502n/cve-2018-10933
libssh CVE-2018-10933
 corelight/zeek-spicy-openvpn
A Zeek OpenVPN protocol analyzer, based on Spicy.
 azurit/modsecurity-backdoor
This is a proof-of-concept of malicious software running inside of ModSecurity WAF.
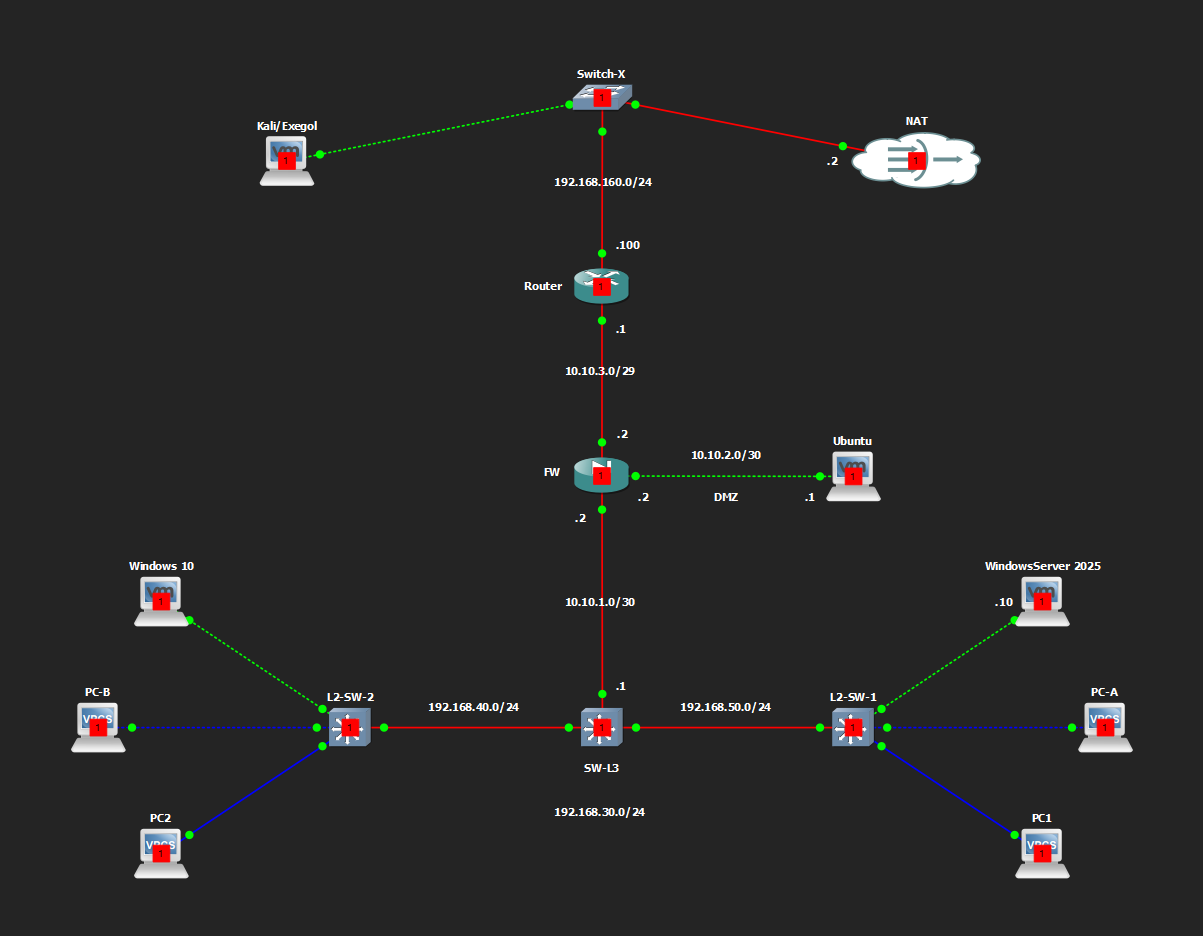 ko0ler/homelab
GNS3 home lab documenting a segmented network with Cisco ASAv firewall, L3 core, DMZ, and an Active Directory domain for practicing networking,…
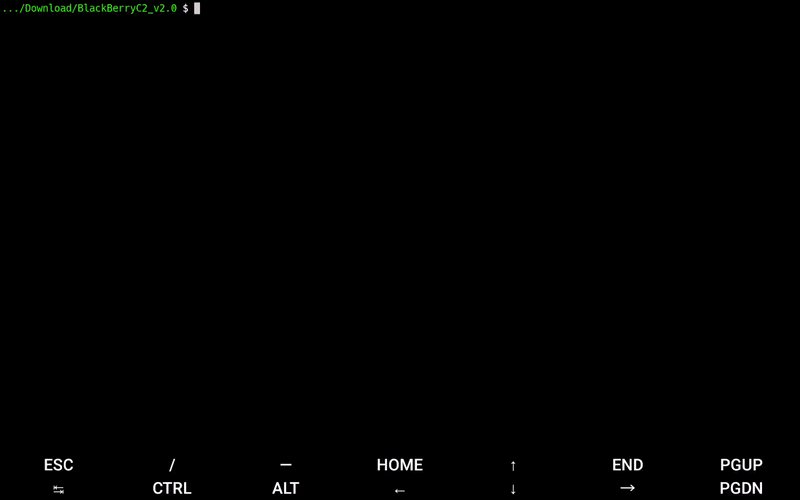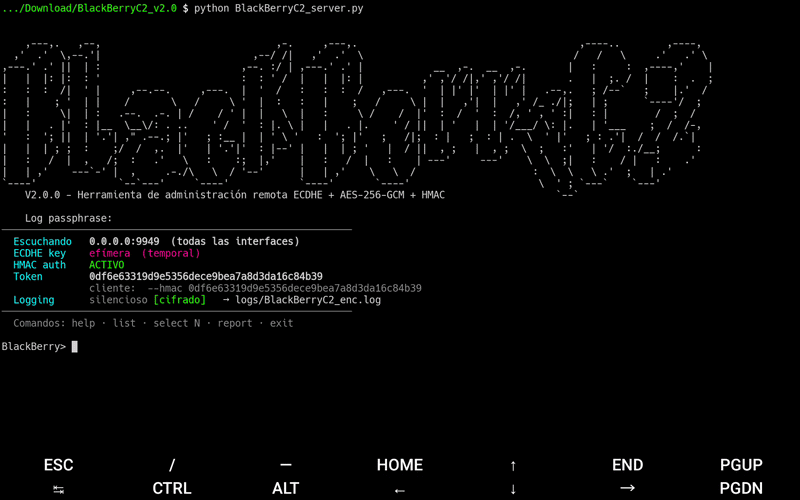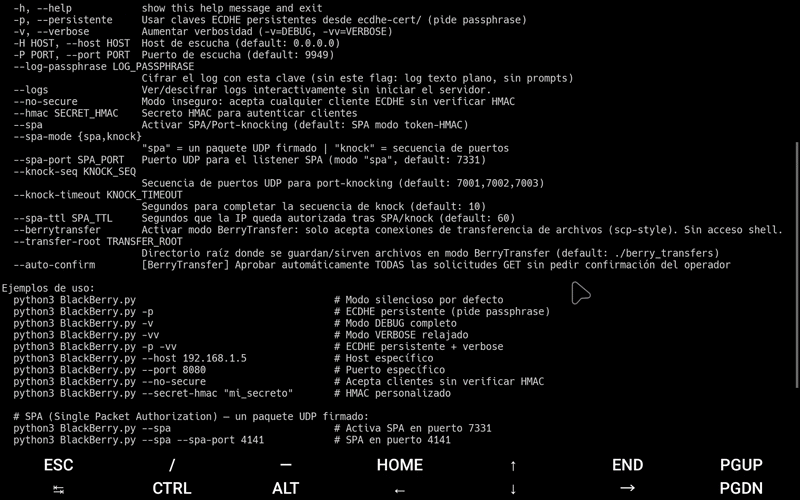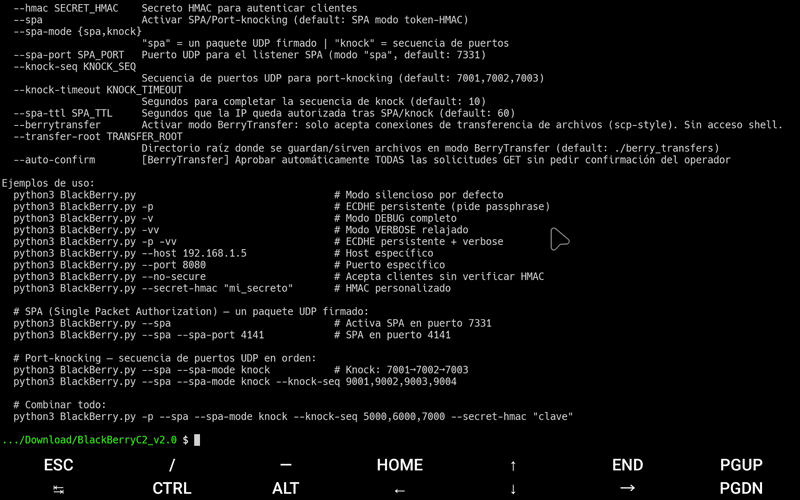 dereeqw/blackberryc2
Encrypted command‑and‑control (C2) research framework for cybersecurity education, red team labs, and secure client‑server communication experiments.
 guokers/aioscan_cve-2020-0796
基于asyncio(协程)的CVE-2020-0796 速度还是十分可观的,方便运维师傅们对内网做下快速检测。
 huntandhackett/antignis
Automates Windows host-based firewall management by importing network data into a central database, creating Active Directory groups, and generating…
 gryfman/dlpwn
Red Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…
 butrintkomoni/cve-2020-0796
Identifying and Mitigating the CVE-2020–0796 flaw in the fly
 noah4ever/sshconfig-lint
Rule-based linter for OpenSSH client config files that detects duplicate hosts, missing identity files, weak algorithms, wildcard ordering issues,…
 advanced-threat-research/cve-2020-16899
CVE-2020-16899 - Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
 0xeb-bp/cve-2020-16898
PoC BSOD for CVE-2020-16898 (badneighbor)
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation








