
 #1
Tools for assessing, testing, and exploiting mobile applications and devices (Android, iOS).
Kitploit recommended
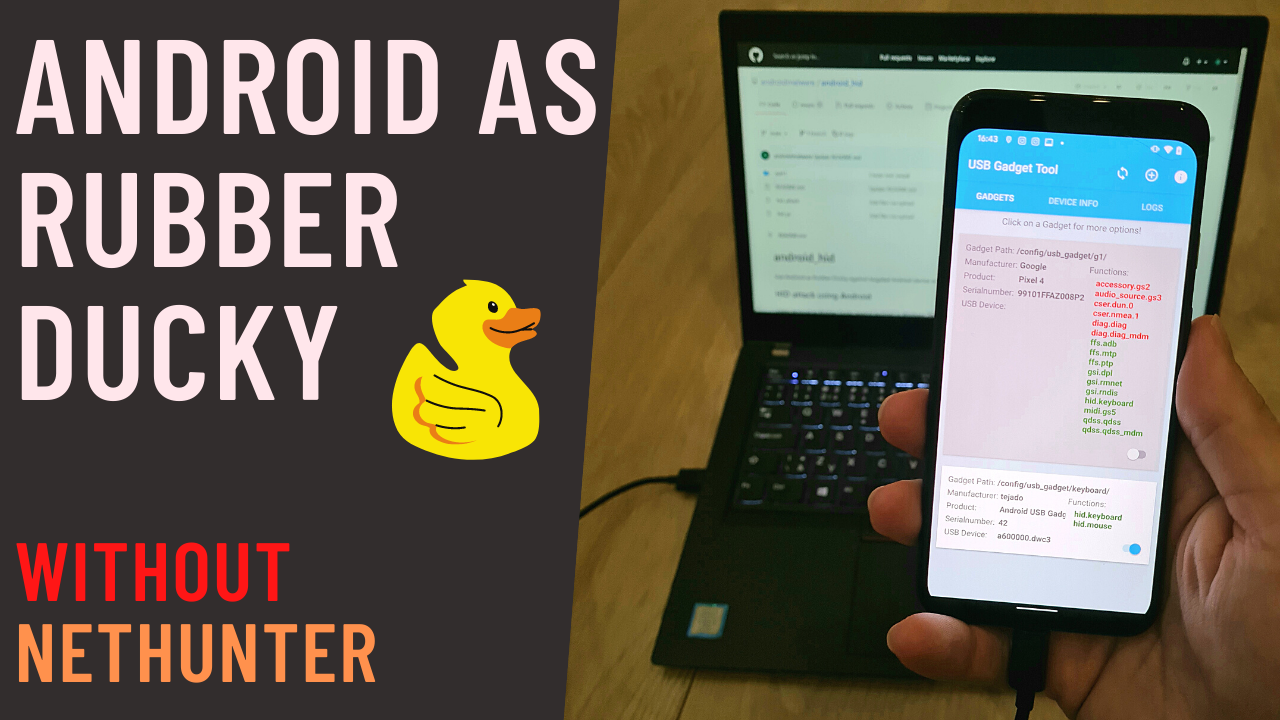
 androidmalware/android_hid
Use Android as Rubber Ducky against another Android device
 nowsecure/r2frida
Radare2 and Frida better together.
 nelenkov/android-backup-extractor
Extract and repack Android ADB backups (ICS+). Supports encrypted archives, tar conversion, and standard I/O for forensic analysis or data recovery.
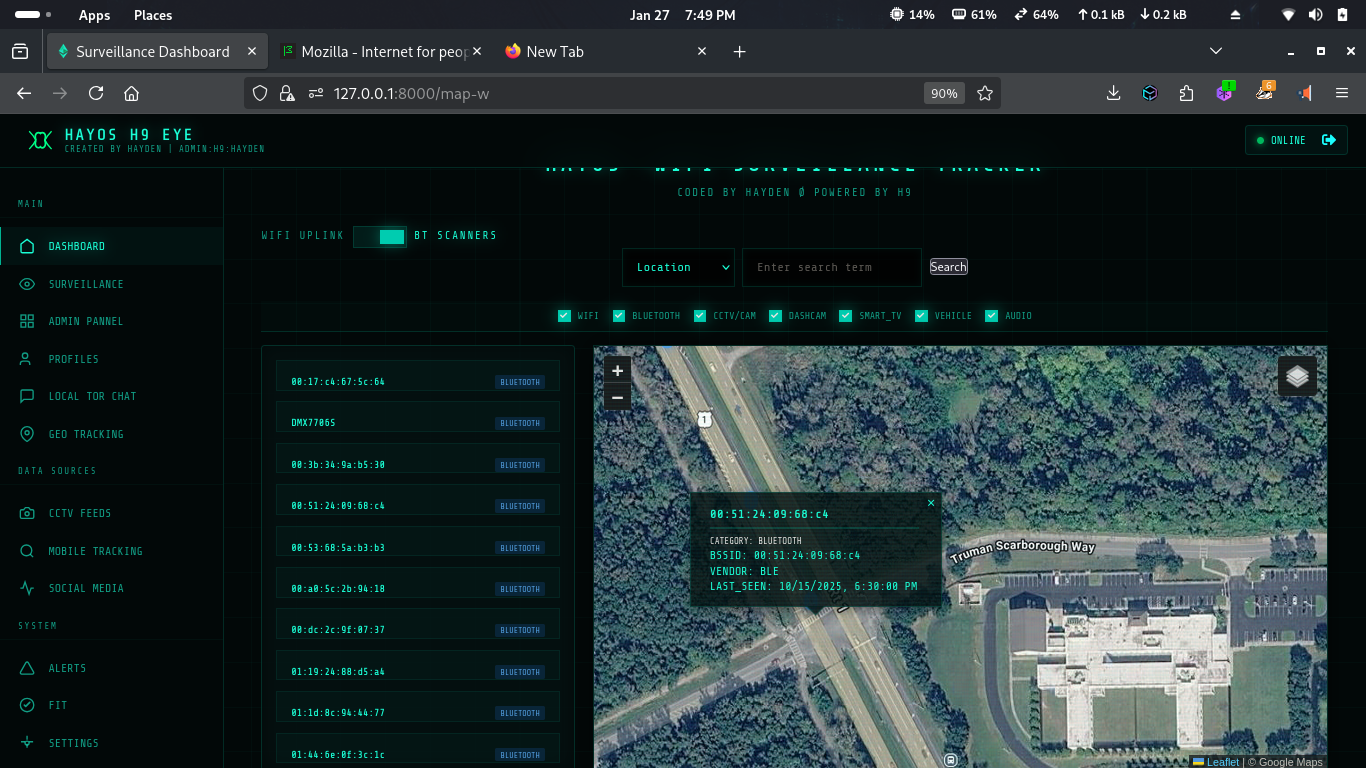 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
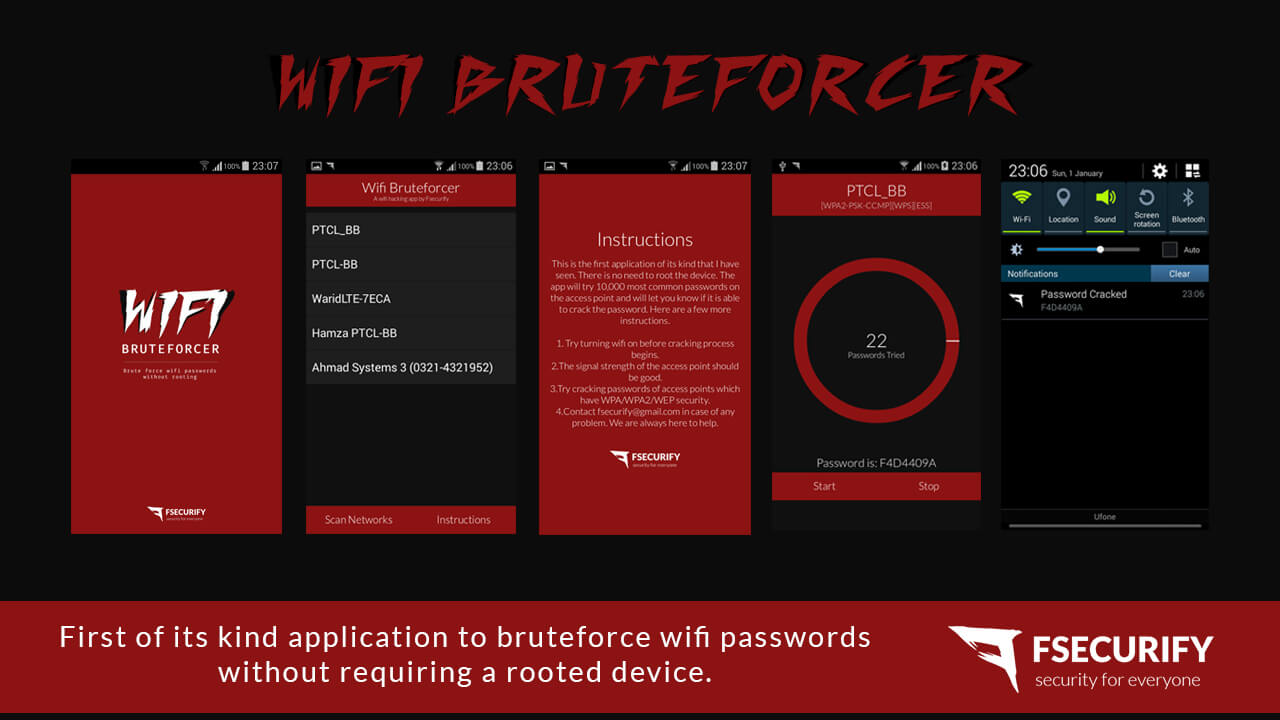 faizann24/wifi-bruteforcer-fsecurify
Android application to brute force WiFi passwords without requiring a rooted device.
 facebook/mariana-trench
A security focused static analysis tool for Android and Java applications.
 ax/apk.sh
Makes reverse engineering Android apps easier, automating repetitive tasks like pulling, decoding, rebuilding and patching an APK.
 nfcgate/nfcgate
An NFC research toolkit application for Android
 michalmalik/osx-re-101
A collection of resources for OSX/iOS reverse engineering.
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 blacktop/ipsw-diffs
Publishes per-build diffs of iOS, iPadOS, and macOS IPSW firmware releases, enabling binary-level comparison of system components across versions and…
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 noob-hackers/kalimux
Install And Use Kali Linux With Gui In Termux
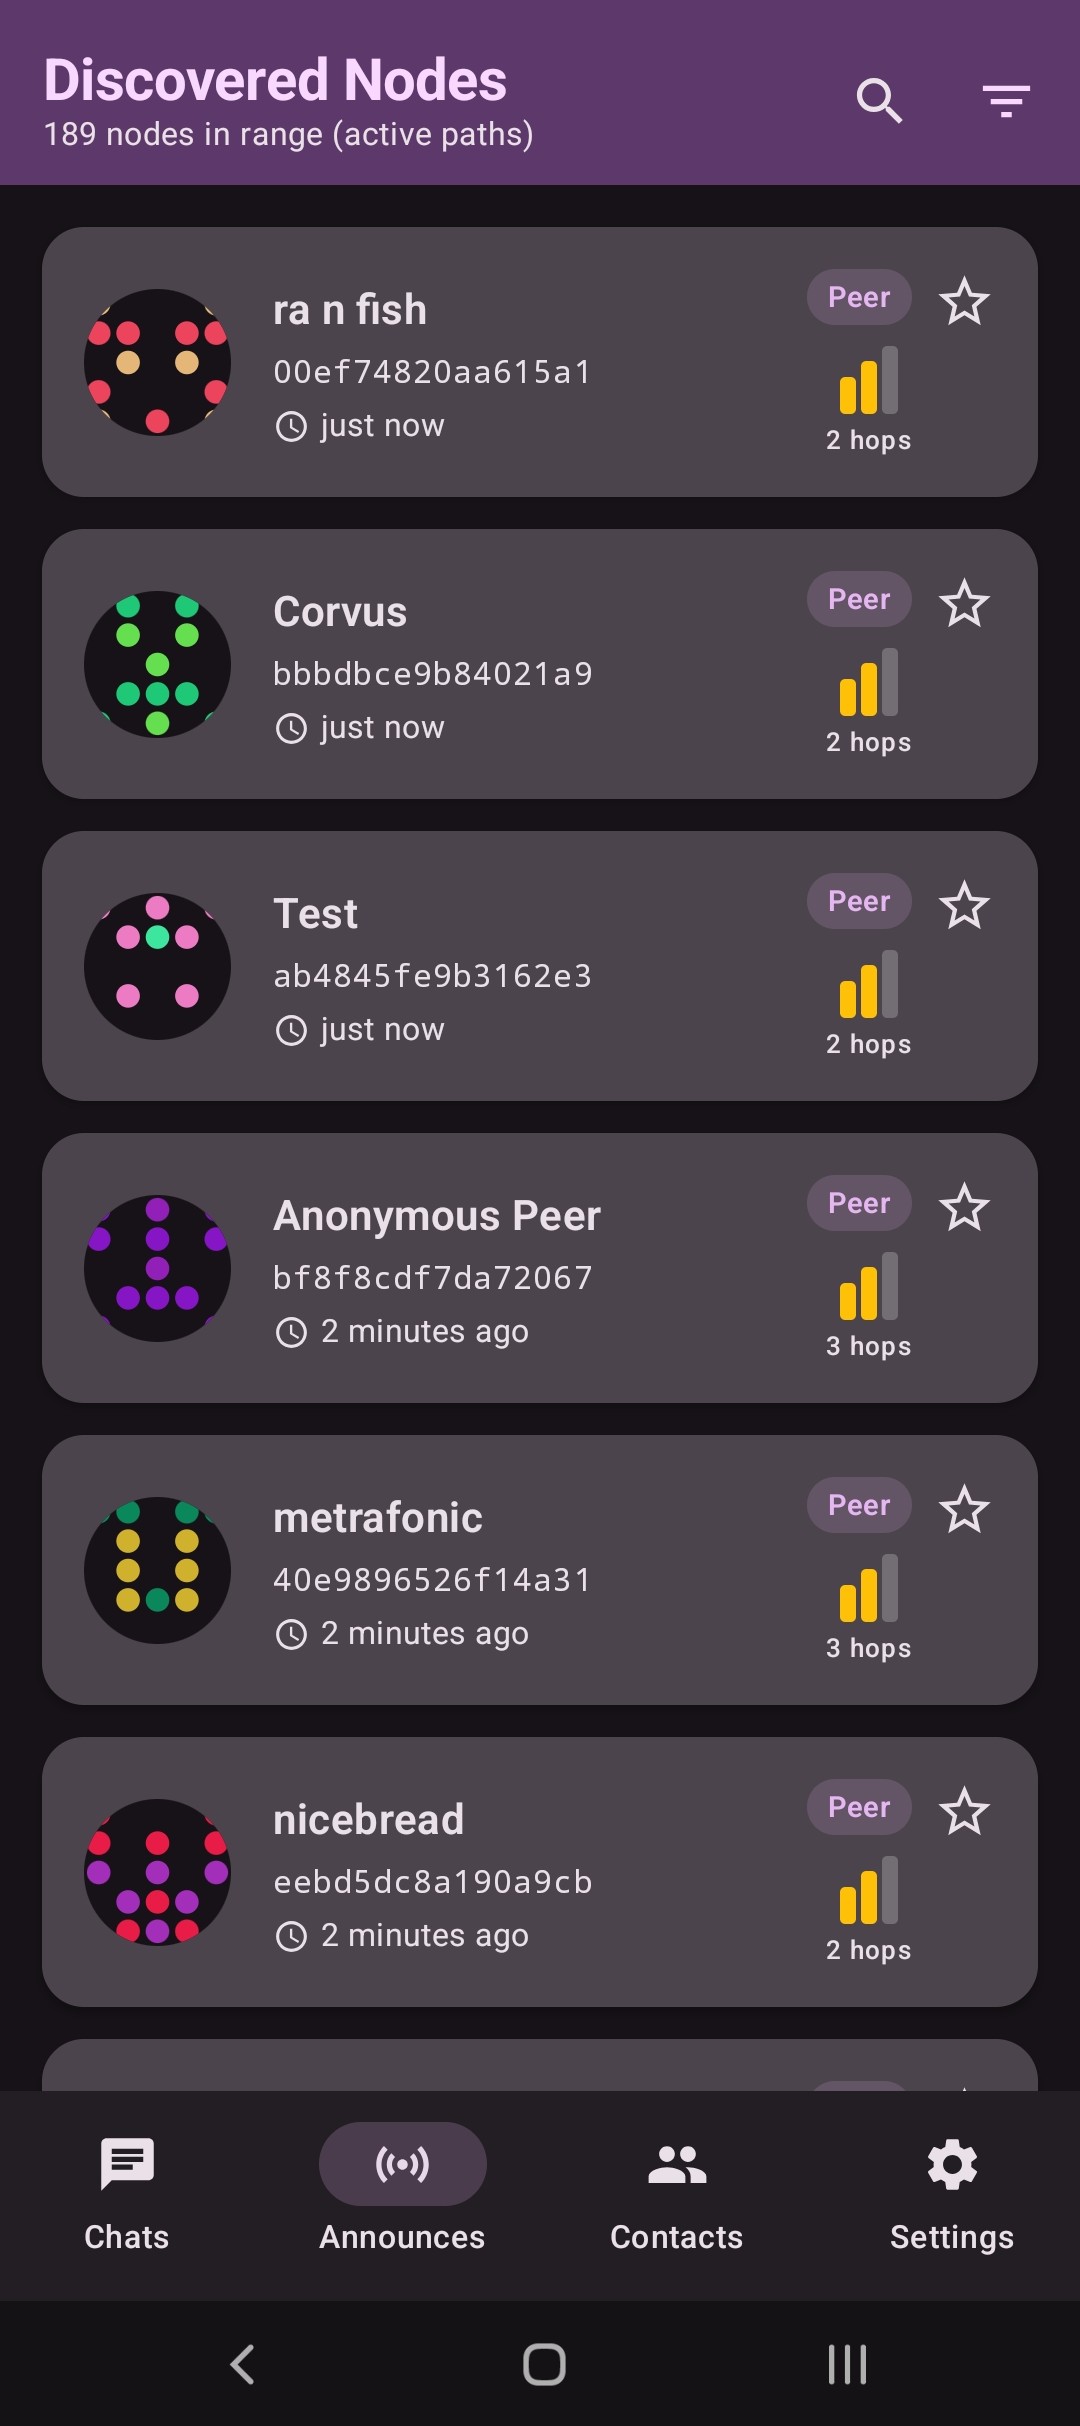 torlando-tech/columba
Native Android messaging app using Bluetooth LE, TCP, or RNode (LoRa) over LXMF and Reticulum
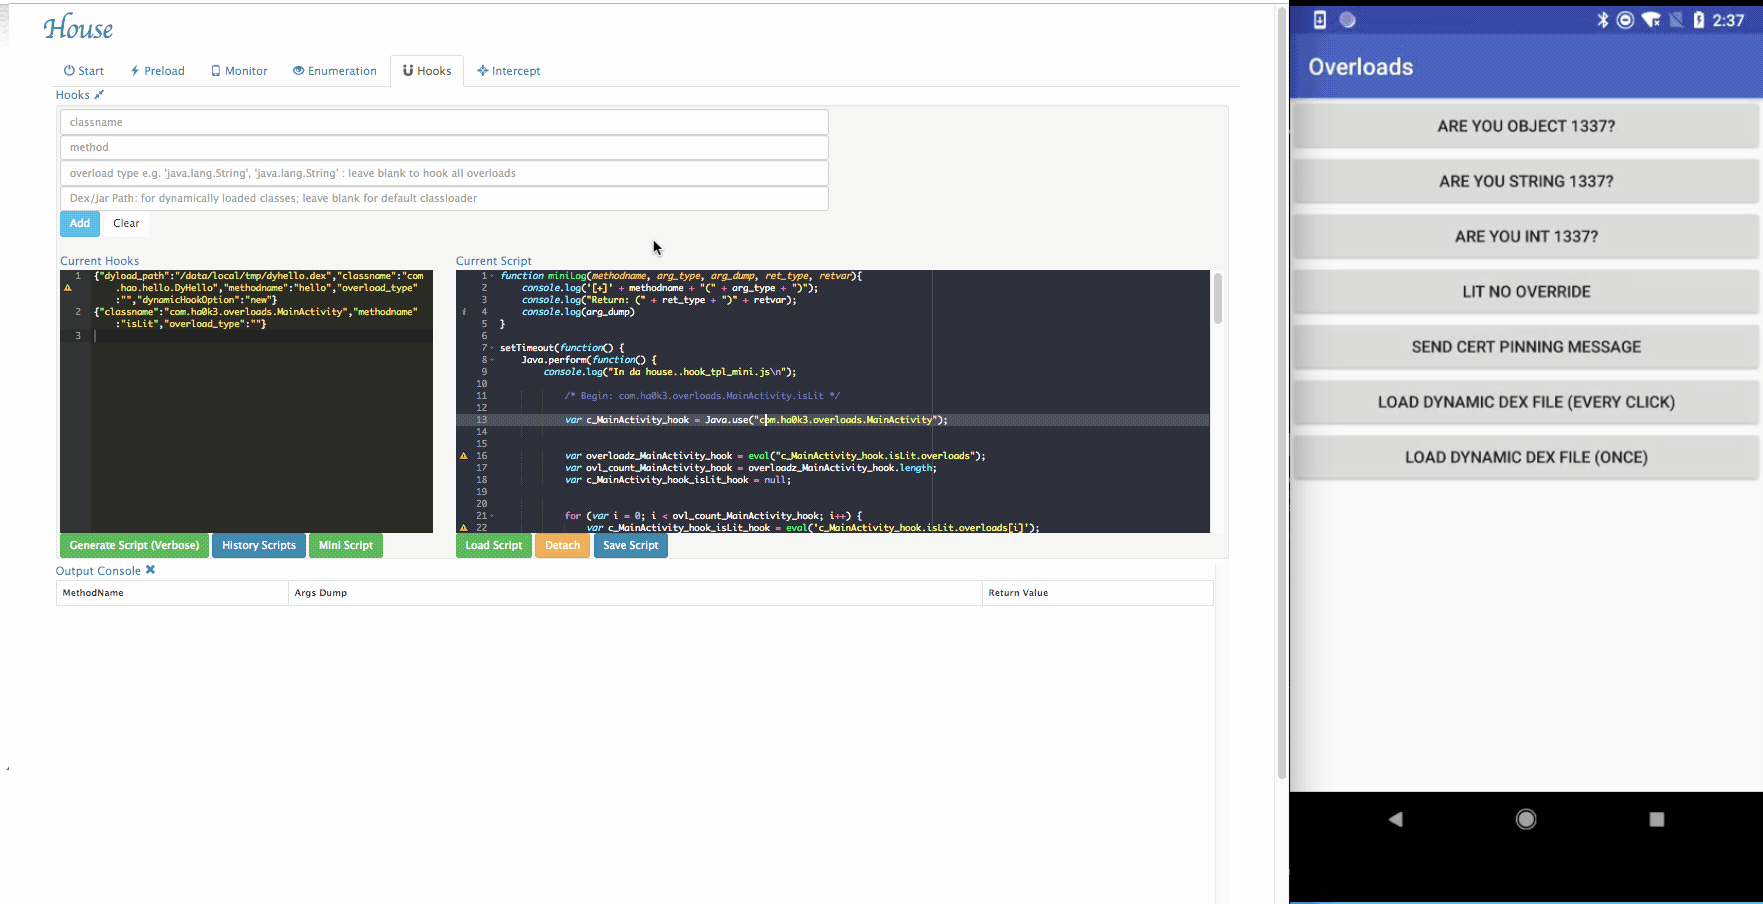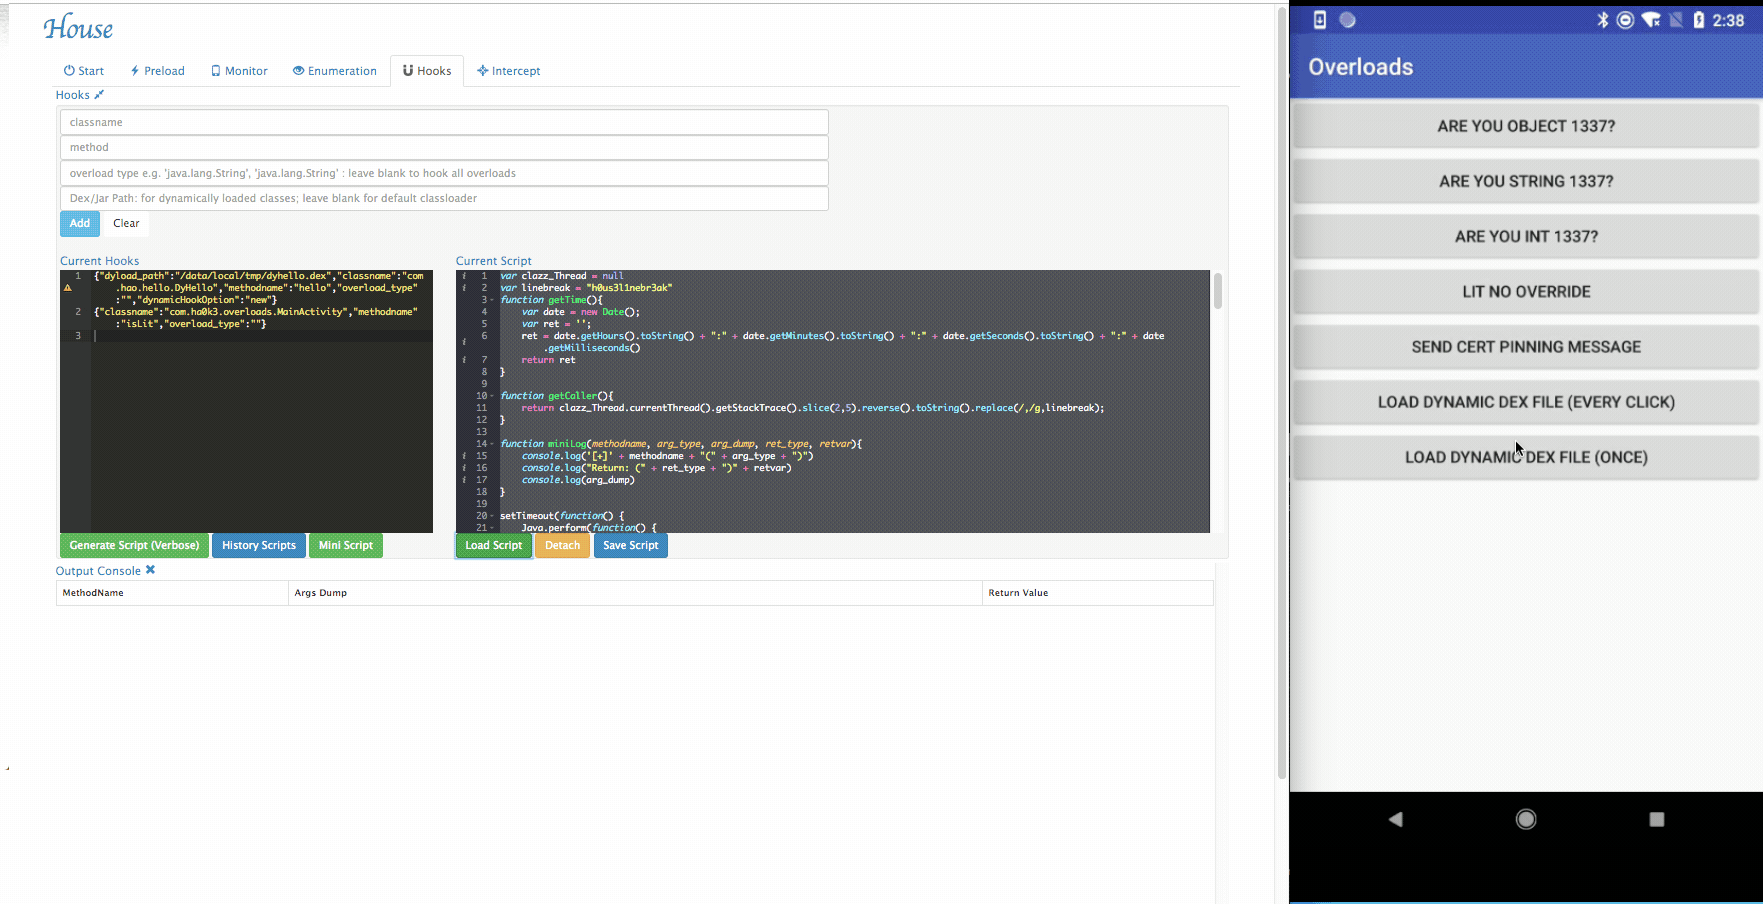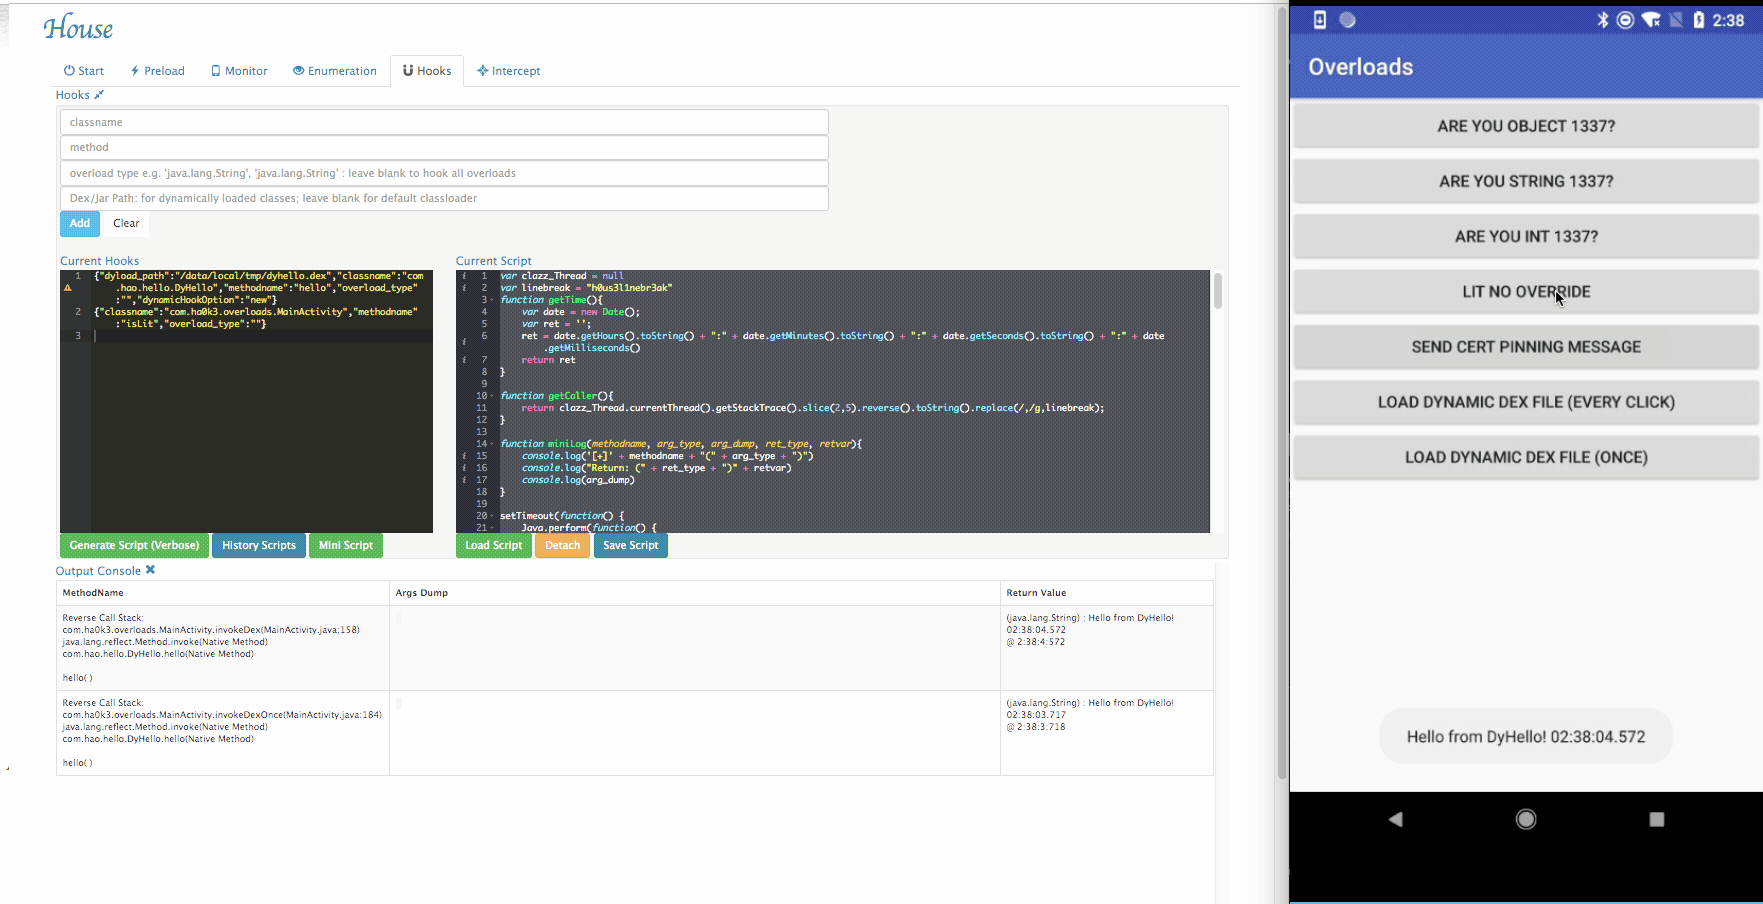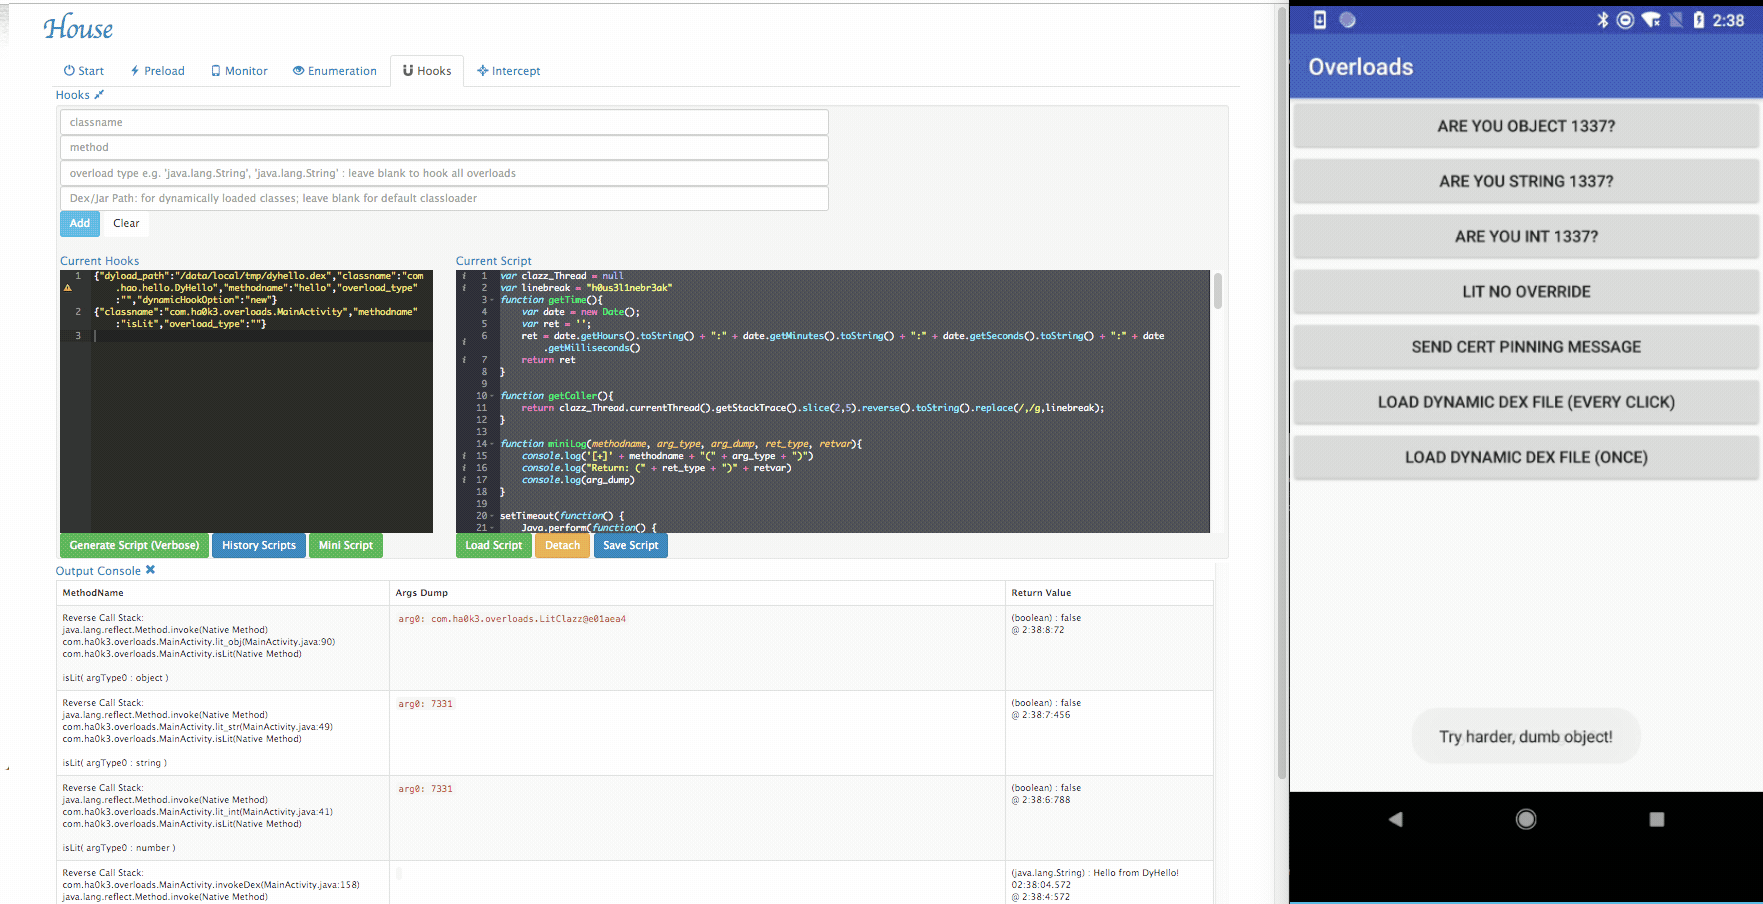 nccgroup/house
A runtime mobile application analysis toolkit with a Web GUI, powered by Frida, written in Python.
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 timwr/cve-2016-5195
CVE-2016-5195 (dirtycow/dirtyc0w) proof of concept for Android








