
 #1
Log parsing, SIEM, centralized logging, forensic timeline, and security event correlation tools.
Kitploit recommended
 linux-audit/audit-kernel
GitHub mirror of the Linux Kernel's audit repository
 jepaynemsft/weffles
Build a fast, free, and effective Threat Hunting/Incident Response Console with Windows Event Forwarding and PowerBI
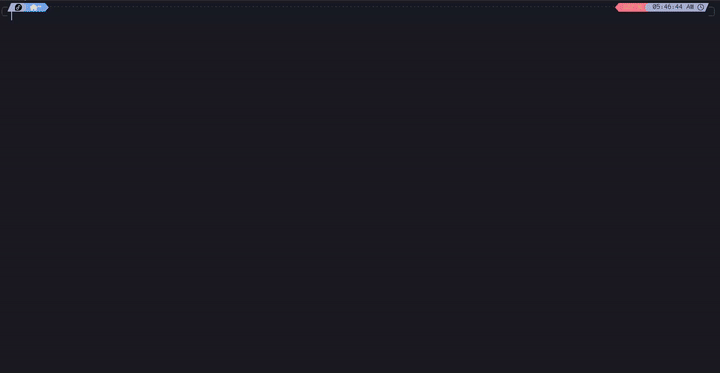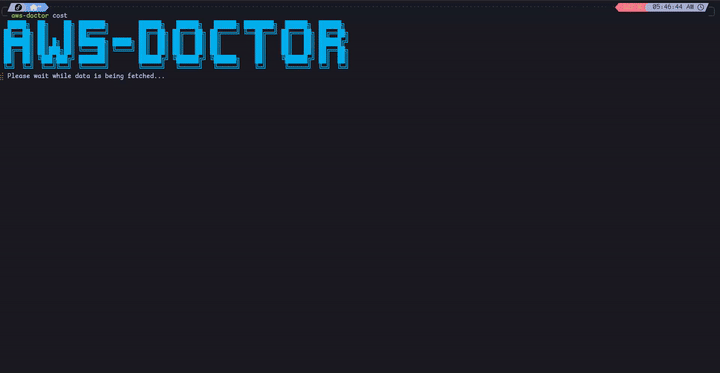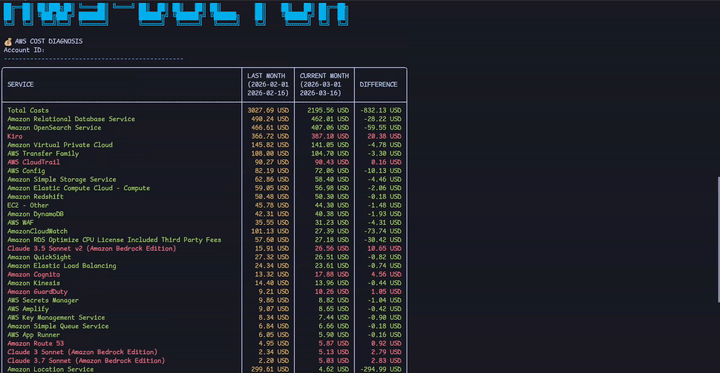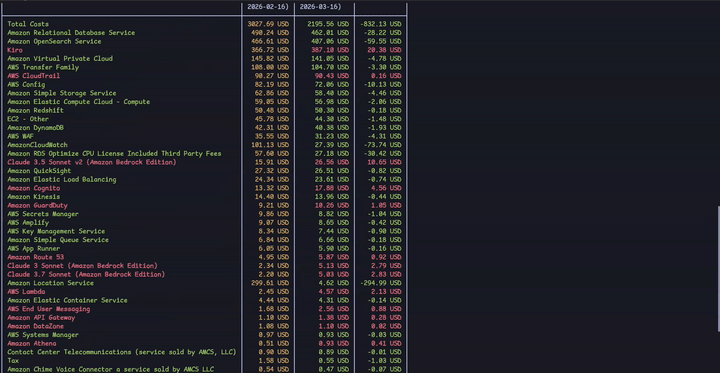 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️
 corelight/zeek-cheatsheets
Zeek Log Cheatsheets
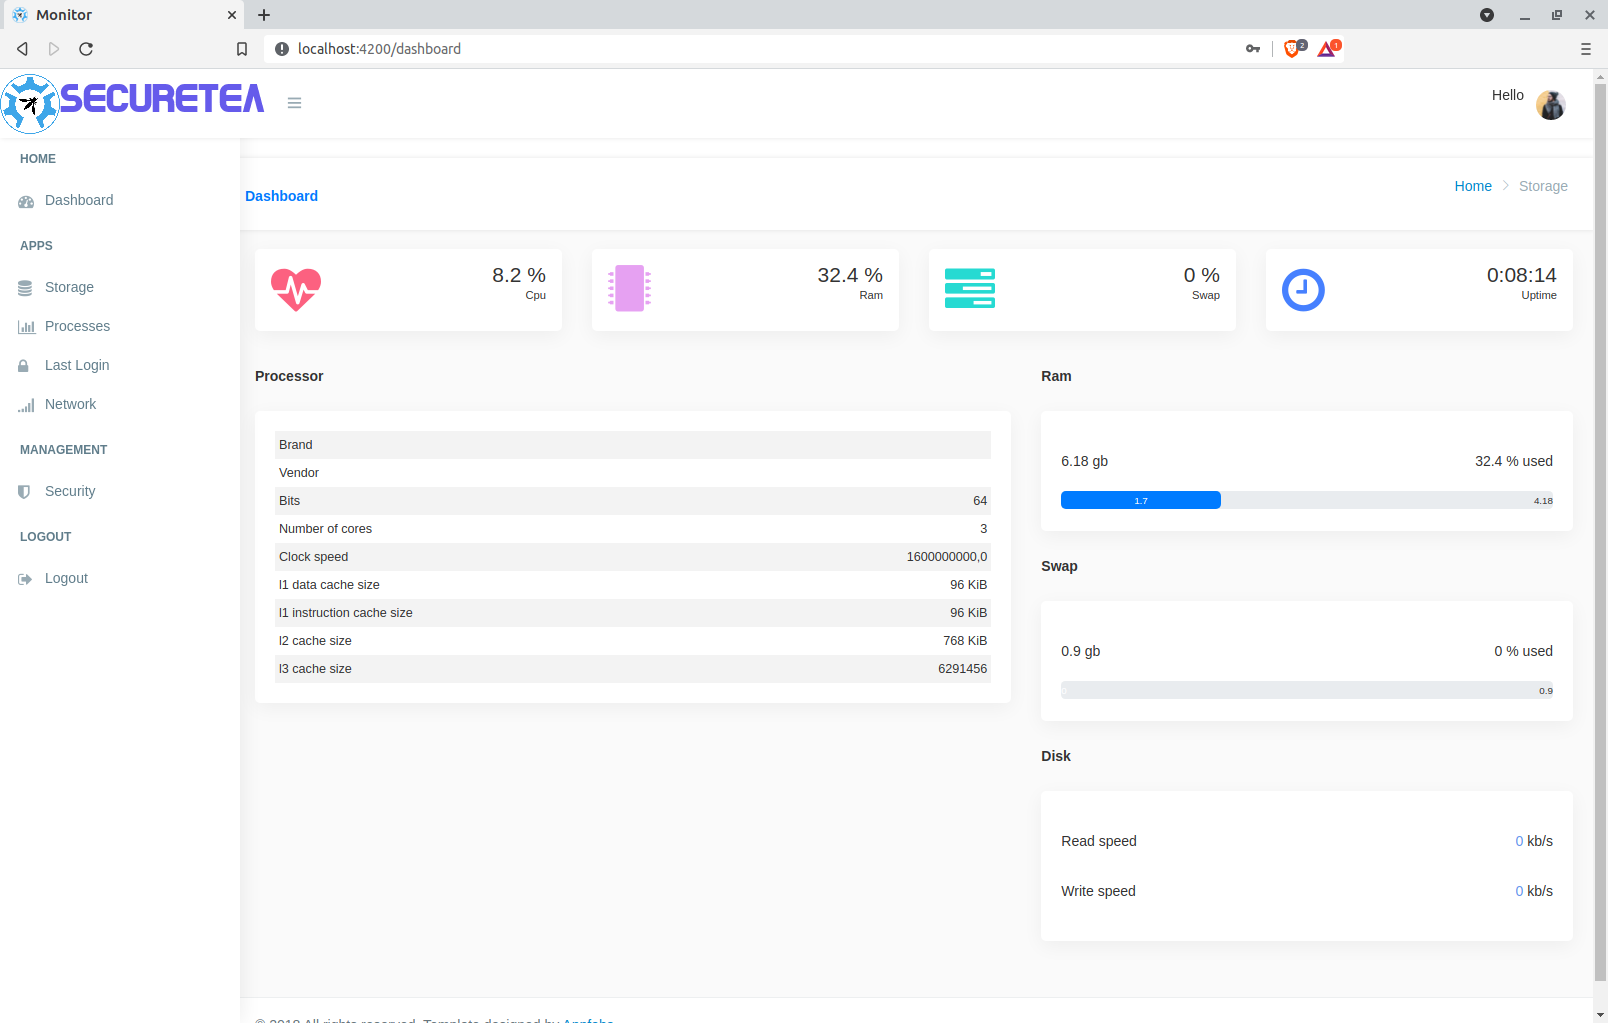 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
 mgreen27/detectraptor
A repository to share publicly available Velociraptor detection content
 ctxis/snitchdns
Database Driven DNS Server with a Web UI
 invictus-ir/alfa
Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…
 hubblestack/hubble
Hubble is a modular, open-source security compliance framework. The project provides on-demand profile-based auditing, real-time security event…
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 randomuserid/adama
Searches For Threat Hunting and Security Analytics
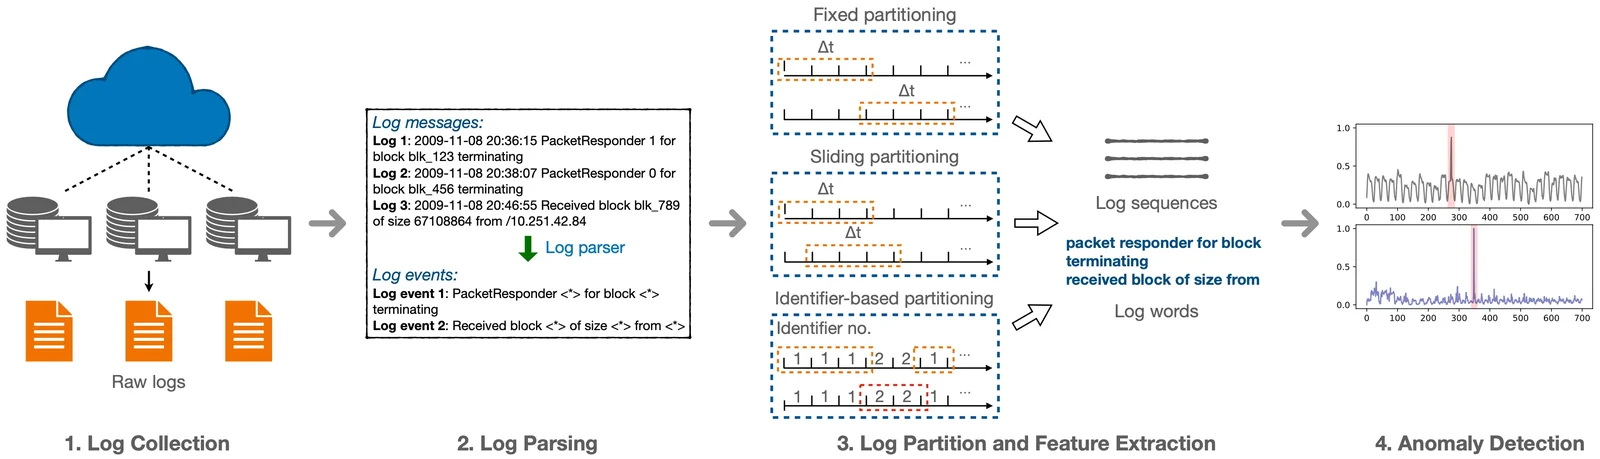 logpai/deep-loglizer
A deep learning toolkit for log-based anomaly detection
 t4d/phishingkithunter
Find phishing kits which use your brand/organization's files and image.
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
 the-dfir-report/sigma-rules
Rules generated from our investigations.
 anssi-fr/dfir-o365rc
PowerShell module for Office 365 and Azure log collection








