
 #1
Log parsing, SIEM, centralized logging, forensic timeline, and security event correlation tools.
Kitploit recommended

 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
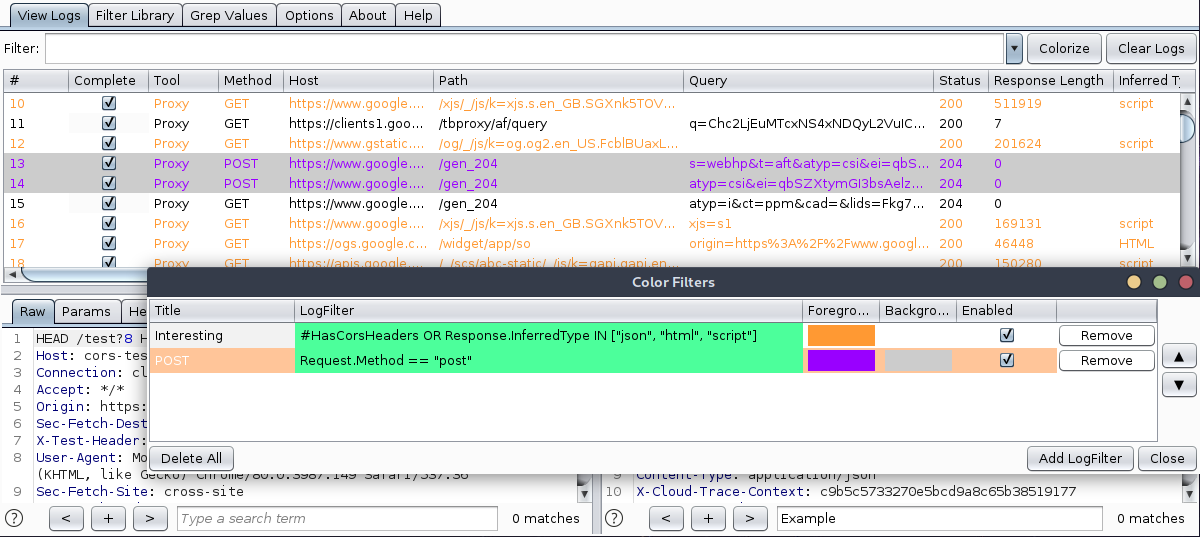 nccgroup/loggerplusplus
Advanced Burp Suite Logging Extension
 scarredmonk/sysmonsimulator
Sysmon event simulation utility which can be used to simulate the attacks to generate the Sysmon Event logs for testing the EDR detections and…
 mandiant/macos-unifiedlogs
A cross platform parser for Apple UnifiedLogs!
 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 neo23x0/loki-rs
🐍 High-performance, multi-threaded YARA & IOC scanner
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 darkquasar/azurehunter
A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365
 d3vl/l3mon
Web-based network monitoring system providing real-time bandwidth tracking, server performance metrics, and customizable alerts for proactive network…
 eshlomo1/microsoft-sentinel-secops
SOC operations content for Microsoft Sentinel, including hunting queries, incident response playbooks, and security event analysis for Azure cloud…
 securityjoes/masterparser
MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs
 nextronsystems/sysmon-config
Sysmon configuration file template with default high-quality event tracing
 justicerage/freedomfighting
A collection of scripts which may come in handy during your freedom fighting activities.
 back2root/log4shell-rex
PCRE RegEx matching Log4Shell CVE-2021-44228 IOC in your logs
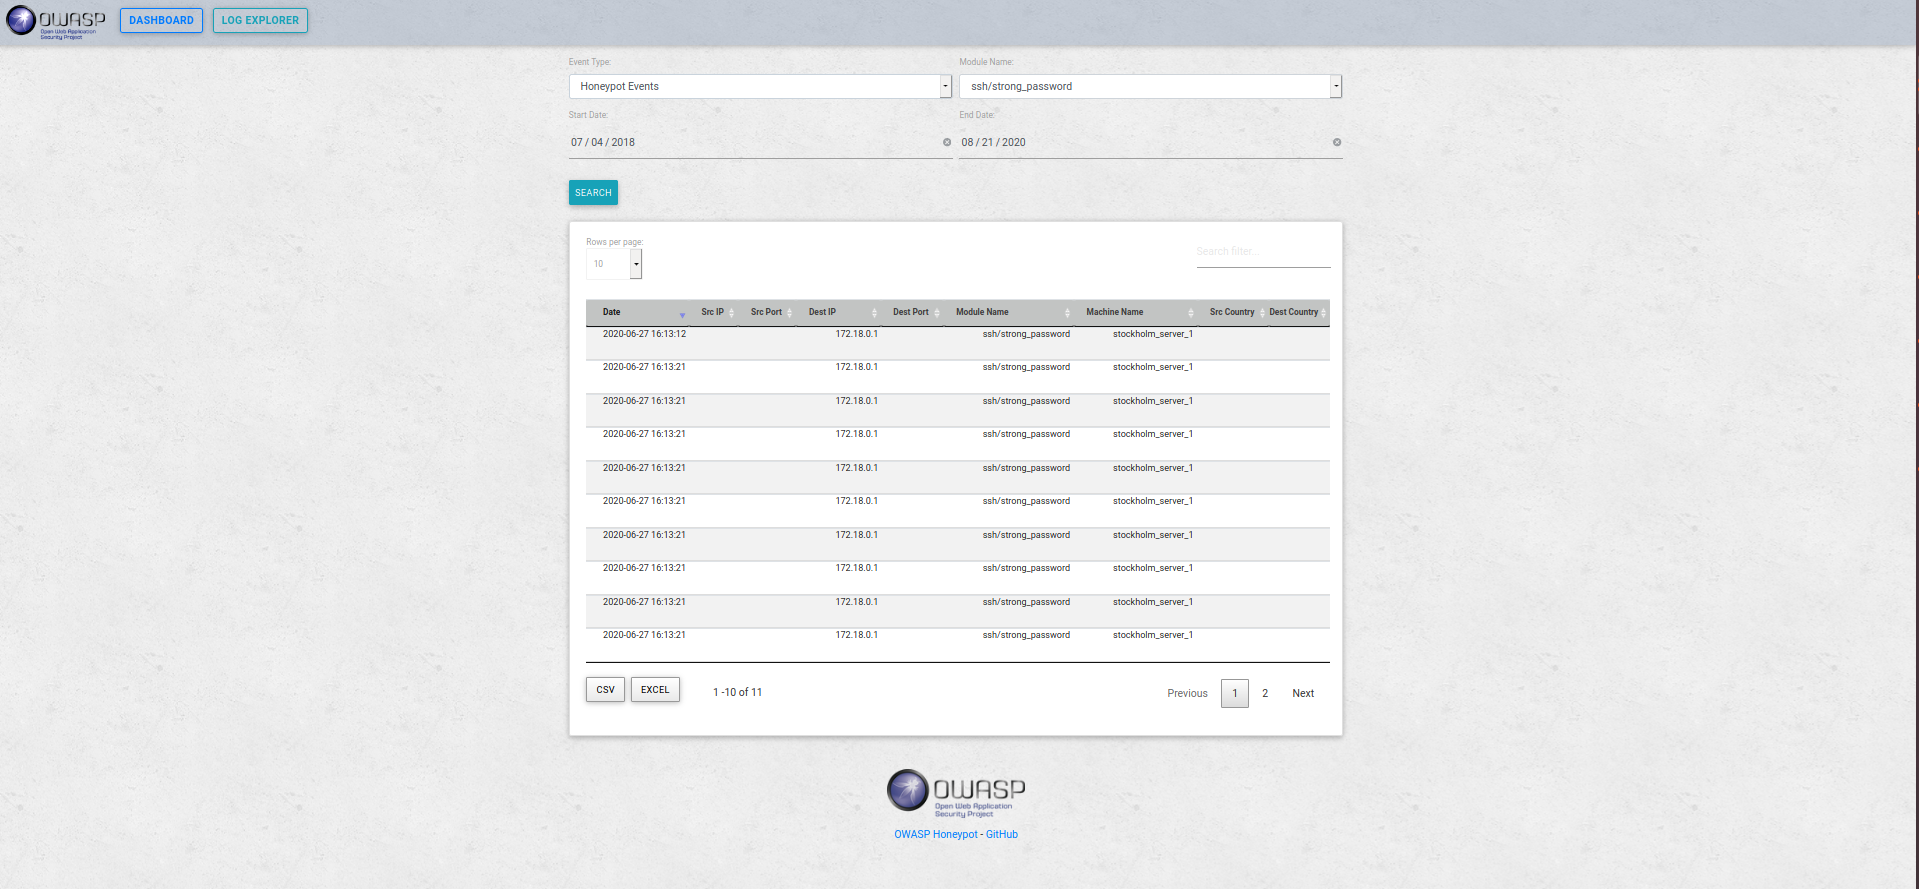 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.








