
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended

 secfigo/awesome-fuzzing
A curated list of fuzzing resources ( Books, courses - free and paid, videos, tools, tutorials and vulnerable applications to practice on ) for…
 dowonkwon/drupal-cve-2018-7600-poc
Proof-of-concept exploit for CVE-2018-7600 (Drupalgeddon 2) with a step-by-step lab environment setup and exploitation walkthrough using Docker and…
 ksgassama-lab/msteams---vulnerability---remediation
Automated remediation of CVE-2025-53783 (Teams RCE) using PowerShell
 lnwza0x0a/ctf_django_cve-2022-34265
Docker-based CTF challenge demonstrating SQL injection in Django's Trunc() and Extract() database functions (CVE-2022-34265) with UNION-based payload…
 lto7777777/cve-1999-0678
CVE-1999-0678- /doc directory browsable
 marcourbano/cve-2021-44228
PoC for CVE-2021-44228.
 matiasarenhard/rails-cve-2017-17917
Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…
 mbcrump/cve-2021-3156
Notes regarding CVE-2021-3156: Heap-Based Buffer Overflow in Sudo
 metehangelgi/cve-2020-1472-lab
Lab introduction to ZeroLogon
 mightysai1997/cve-2021-41773s
Docker-based vulnerable lab for CVE-2021-41773 Apache path traversal, providing PoC configurations for file read and remote code execution in a…
 mklinkj/log4j2-test
Log4j2 LDAP 취약점 테스트 (CVE-2021-44228)

 nekr0ff/needrestart-sudo-escalate-cve-2024-4890
PoC exploit for CVE-2024-4890: Sudo privilege escalation via neecdrestart (>=3.8). Ethical lab-only. Scripts in Python and C.
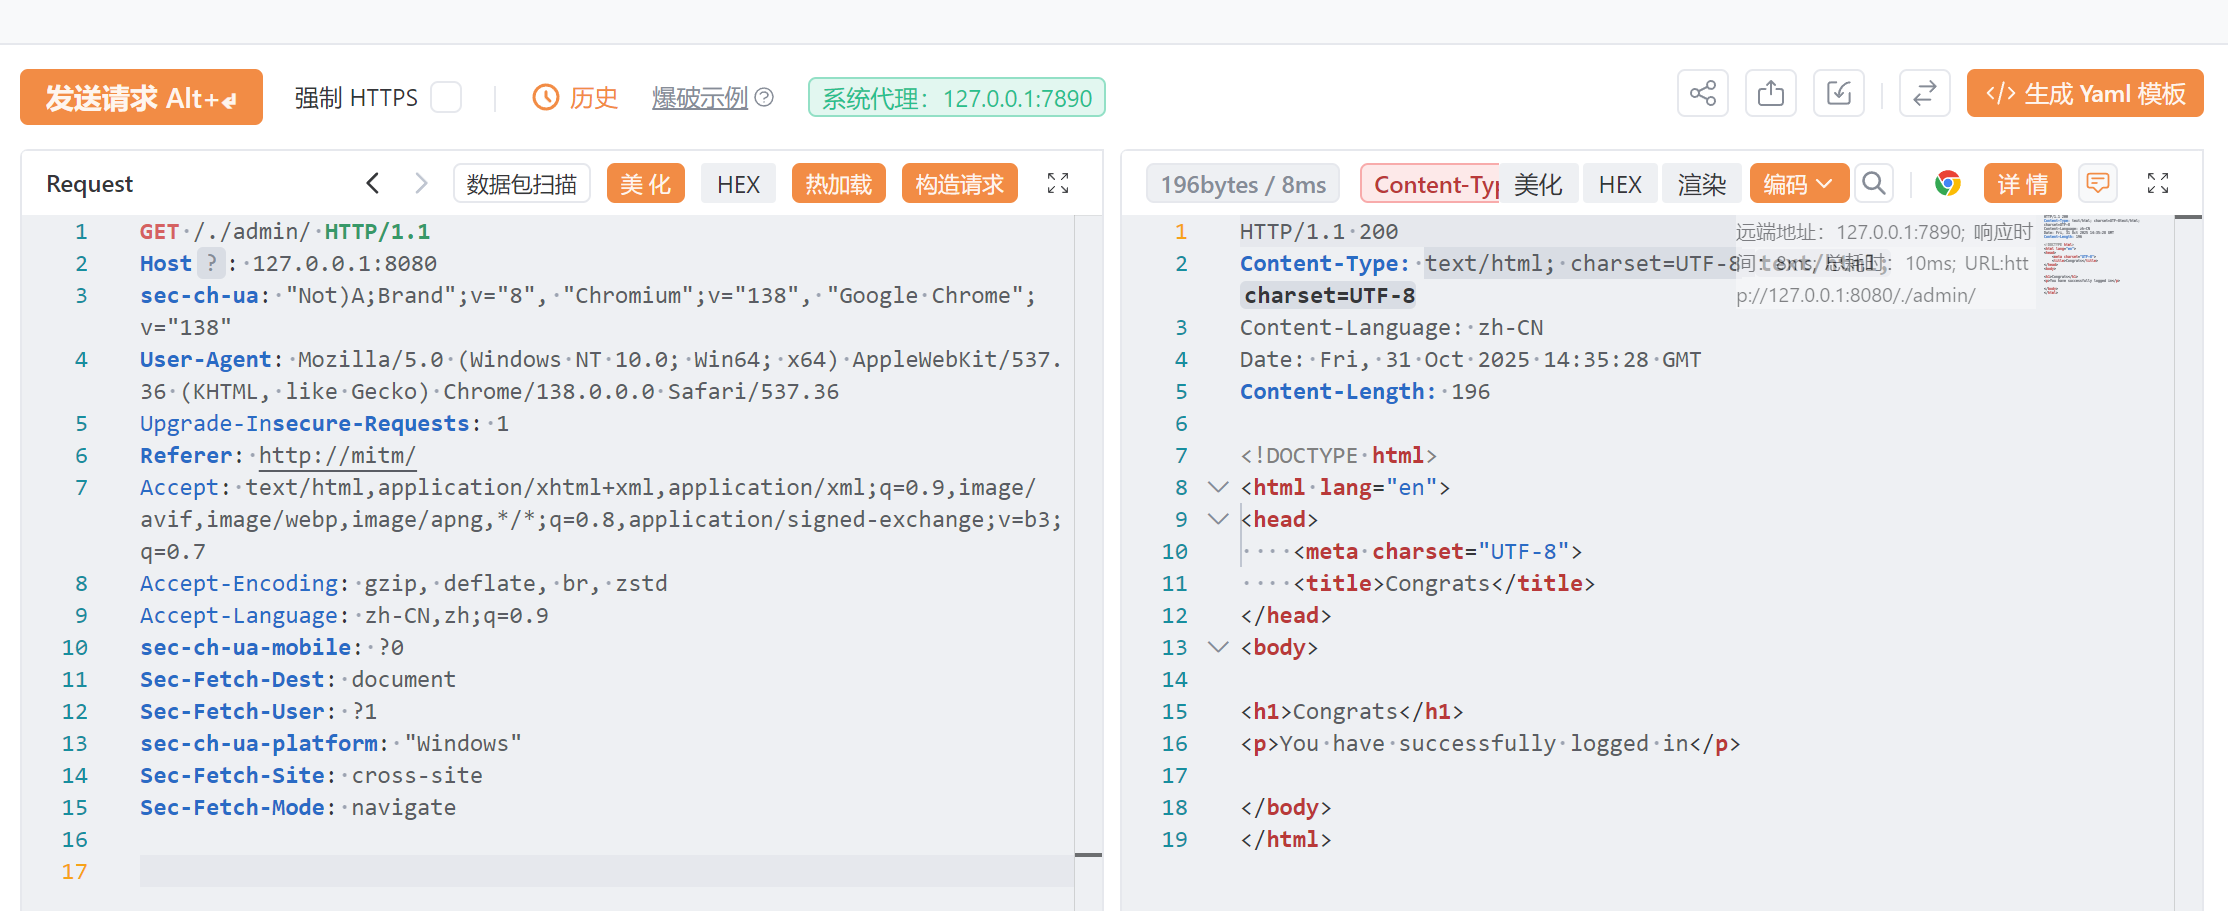 sh1inroot-alt/shiro-cve-2010-3863
shiro 路径穿越
 nickylimjj/cve-2019-12735
Docker image that lets me study the exploitation of the VIM exploit
 nikolas-charalambidis/cve-2021-44228
A simple simulation of the infamous CVE-2021-44228 issue.
 noflowpls/cve-2021-41773
CVE-2021-41773
 oocyginxoo/cve-2023-25690-poc
CVE 2023 25690 Proof of concept - mod_proxy vulnerable configuration on Apache HTTP Server versions 2.4.0 - 2.4.55 leads to HTTP Request Smuggling…








