
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended

 thecybergeek/cve-2026-3888-snap-confine-systemd-tmpfiles-lpe
Local privilege escalation exploit for CVE-2026-3888 targeting snap-confine and systemd-tmpfiles on Ubuntu, providing SUID and capabilities variants…
 sowatkheang/cve_2026_2576_poc
CVE-2026-2576 — Business Directory Plugin SQLi PoC (Local Setup). Unauthenticated Time-Based Blind SQL Injection Business Directory Plugin for…
 shreda/cve-2026-33032-nginx-ui-vuln-lab
Docker Compose setup to demonstrate the nginx-ui missing authentication vulnerability
 pinkarmor/cve-2025-1094-lab-setup
Hands-on lab to exploit CVE-2025-1094, a PostgreSQL psql SQL injection leading to RCE via COPY TO PROGRAM, with Docker setup and reverse shell…
 mkway/cve-2026-3304
Reproduction lab for CVE-2026-3304, a Multer async fileFilter race condition causing disk exhaustion via orphaned temp files. Includes vulnerable and…
 mehdi-ben-hamou/cve-2026-30498
Educational CSRF vulnerability demonstration with a controlled lab environment, including a proof-of-concept exploit and a fixed version with proper…
 pulentoski/cve-2026-31431
Modular framework for researching and exploiting a Linux kernel privilege escalation vulnerability using AF_ALG and page cache injection to modify…
 kondordevsecuritycorp/cve-2026-34197
Exploit for Apache ActiveMQ RCE via Jolokia API (CVE-2026-34197) with command output capture, mass scanning, and auto-exploitation.
 jakeswiz/telnet-inetutils-auth-bypass-cve-2026-24061
This is a simple PoC that allows you to highlight the severity of the ongoing and actively exploited Telnet bug that is going on right now. Why…
 ret0x2a/cve-2025-8625
Proof-of-concept exploit for CVE-2025-8625 targeting WordPress, with Docker-based isolated lab environment and demonstration web shell for…
 furkankayapinar/cve-2026-24061-telnet2root
Scanner and interactive exploit for CVE-2026-24061 in inetutils-telnetd, enabling pre-auth root access via crafted NEW-ENVIRON negotiation. Includes…
 feryaeljustice/log4shell
This repository is for Log4j 2021 (CVE-2021-44228) Vulnerability demonstration and mitigation.
 m96dg/cve-2021-41773-exercise
Hands-on lab to exploit Apache 2.4.49 path traversal (CVE-2021-41773) using Docker, Nmap scanning, and curl to retrieve a flag.
 dhiaelhak-rached/cve-2026-39987-lab-or-marimo-cve-lab
Educational Docker lab demonstrating CVE-2026-39987, a pre-auth RCE via WebSocket authentication bypass in marimo, with exploit script and patch…
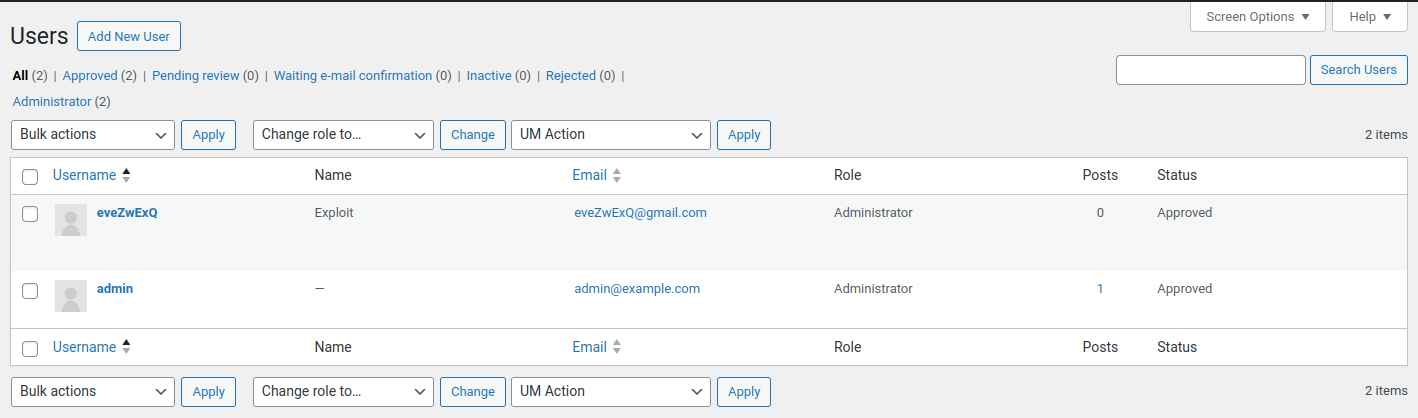 julienbrs/exploit-cve-2023-3460
Exploit and analysis of CVE-2023-3460, a critical privilege escalation in the Ultimate Member WordPress plugin, with reproduction environment and…
 jxerome/log4shell
Educational demonstration of the Log4Shell vulnerability (CVE-2021-44228) with JNDI LDAP payloads for experimental testing on your own systems.
 cryingn/cve-2026-44656
Reproduction environment for CVE-2026-44656, a Vim modeline command injection vulnerability. Includes Docker setup, PoC file, and exploit script to…
 shotafry/copyfail-exploits-cve-2026-31431
Multi-language educational exploit implementations for CVE-2026-31431, a Linux kernel local privilege escalation via the algif_aead module, with a…








