
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended
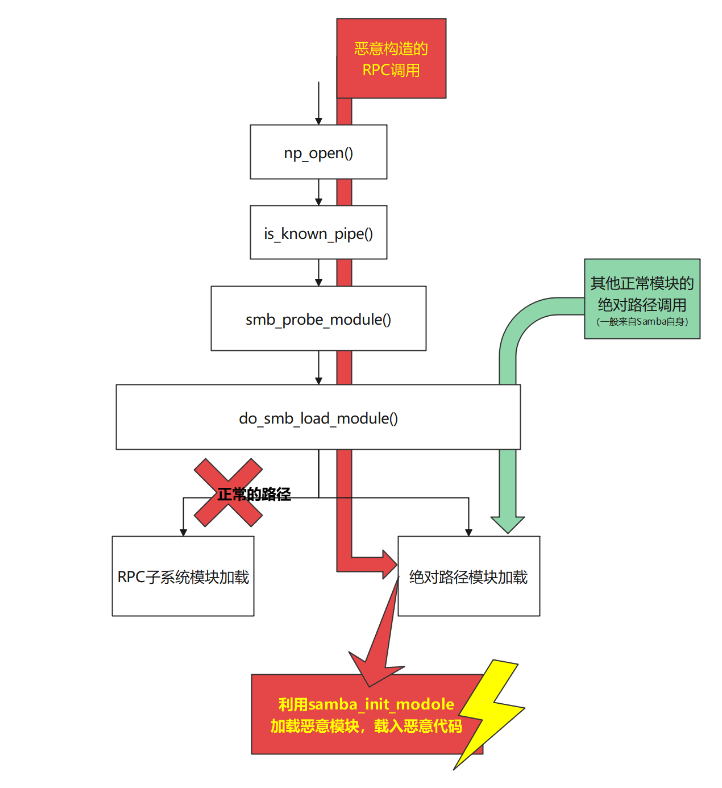
 i-rinka/bit-eternalblue-for-macos_linux
Exploit CVE-2017-7494 for Net Security course final Assignment. This would reveal the vulnerability of services that run in administrative priority…
 mym0us3r/dirty-frag-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) - Linux Local Privilege Escalation via page cache write
 laysakura/cve-2024-21626-demo
Demonstration of CVE-2024-21626 container escape exploit allowing host root access via malicious Docker image, with step-by-step attack scenario for…
 hophtien/cve-2025-54424
CVE-2025-54424: 1Panel TLS client cert bypass enables RCE via forged CN 'panel_client' using a bundled scanning and exploitation tool. Affected: <=…
 mikivirus0/sudoinjection
Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)
 eqstlab/cve-2026-42048
Langflow Arbitrary Directory Deletion
 devenes/text4shell-cve-2022-42889
Kubernetes Lab for CVE-2022-42889
 viz27/libssh2-exploit
Create an exploit to libssh2 vulnerabulity described in CVE-2019-13115
 pswalia2u/cve-2020-7246
Lab environment and exploit script for CVE-2020-7246, a PHP code injection vulnerability in qdPM 9.1. Includes Docker setup and Python2-based…
 n0bitaemon/cve-2026-26980-poc
Ghost CMS Content API Blind SQL Injection
 mightysai1997/cve-2021-41773s
Docker-based vulnerable lab for CVE-2021-41773 Apache path traversal, providing PoC configurations for file read and remote code execution in a…
 jayhutajulu1/cve-2026-43494-pintheft-poc
Proof-of-concept for CVE-2026-43494 (PinTheft): Linux LPE via RDS zerocopy refcount bug + io_uring fixed buffers → SUID page-cache overwrite.…
 hashdr1ft/soc_287
SOC287 - Arbitrary File Read on Checkpoint Security Gateway [CVE-2024-24919]
 seifeldienahmad/penetration-testing-on-metasploitable2
Hands-on pentest project using Kali Linux vs Metasploitable2. Includes full workflow: Nmap scanning, enumeration, Metasploit exploitation (Samba…
 cristhiansm0/txdxcristhian_2023-cve-38831
CVE-2023-38831 WinRAR lab: detection with Sysmon/Wazuh, reverse engineering with Ghidra, patch analysis, and remediation.
 rat5ak/cve-2026-61946-easy-appointments-idor
CVE-2026-61946: Unauthenticated IDOR in Easy Appointments <= 3.12.27
 h1n4mx0z/research-cve-2016-5195
Detailed technical analysis and proof-of-concept exploit for CVE-2016-5195 (Dirty COW), a Linux kernel privilege-escalation vulnerability using a…








