#1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended

 javokhir-sec/cve-poc-hub
🛡️ CVE Proof-of-Concept Hub — 4 PUBLISHED CVEs · 5 under review (VulnCheck) · SuiteCRM batch withdrawn
 tdevworks/cve-2020-0796-smbghost-exploit-demo
Educational proof-of-concept exploit for CVE-2020-0796 (SMBGhost) demonstrating pre-auth RCE on Windows SMBv3. Includes step-by-step lab setup,…

 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
 stealthsploit/oneruletorulethemstill
A revamped and updated version of my original OneRuleToRuleThemAll hashcat rule
 jas502n/2024informationsecurityengineer
2024年信息安全工程师、2024InformationSecurityEngineer
 hellboy3110/cve-2026-16219-croogo-lab
Safely demonstrates CVE-2026-16219 path traversal in Croogo CMS with a loopback-only PoC, technical analysis, remediation guidance, and standalone…
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 cved-sources/cve-2018-3811
Docker container providing a vulnerable environment for CVE-2018-3811, designed for security testing and exploit practice within the Cved vulnerable…
 wwwiesel/infosec-black-friday
All the deals for InfoSec related software/tools this Black Friday
 686f6c61/poc-aiowpm-cve-2026-19949
Reproducible Docker-based proof-of-concept for CVE-2026-19949, a second-order SQL injection in All-in-One WP Migration <= 7.109 that leaks the…
 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
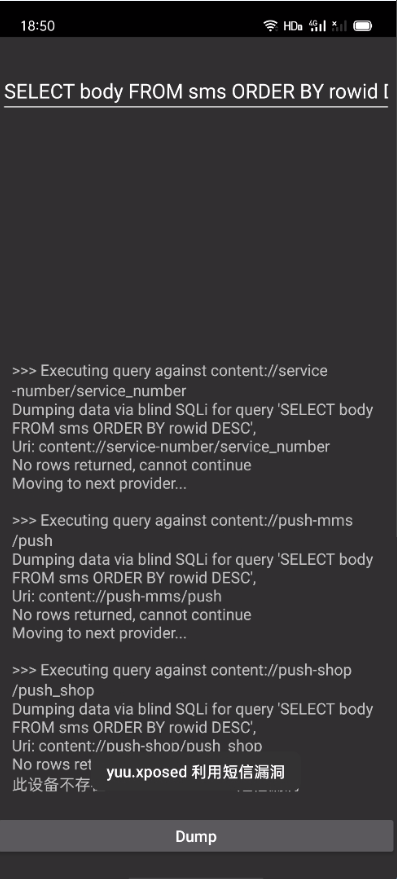 yuuouu/coloros-cve-2025-10184
ColorOS短信漏洞,以及用户自救方案
 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
 ramadhanamizudin/lazyweb
LazyWeb is a demonstration web application designed to showcase common server-side application vulnerabilities. Each vulnerability is categorized…
 gkrishnan724/cve-2021-38297
A Proof of concept scenario for exploitation of CVE2021-38297 GO WASM buffer-overflow