
 #1
Tools focused on testing, reversing, and securing iOS applications and the iOS operating system.
Kitploit recommended

 harryanon/poc-cve-2018-4327-and-cve-2018-4330
Proof-of-concept exploit for iOS Bluetooth stack vulnerabilities CVE-2018-4327 and CVE-2018-4330, enabling ARM PC register control on iPhone 6S via…
 rootkitsmm-zz/extra_recipe-ios-10.2
CVE-2017-2370
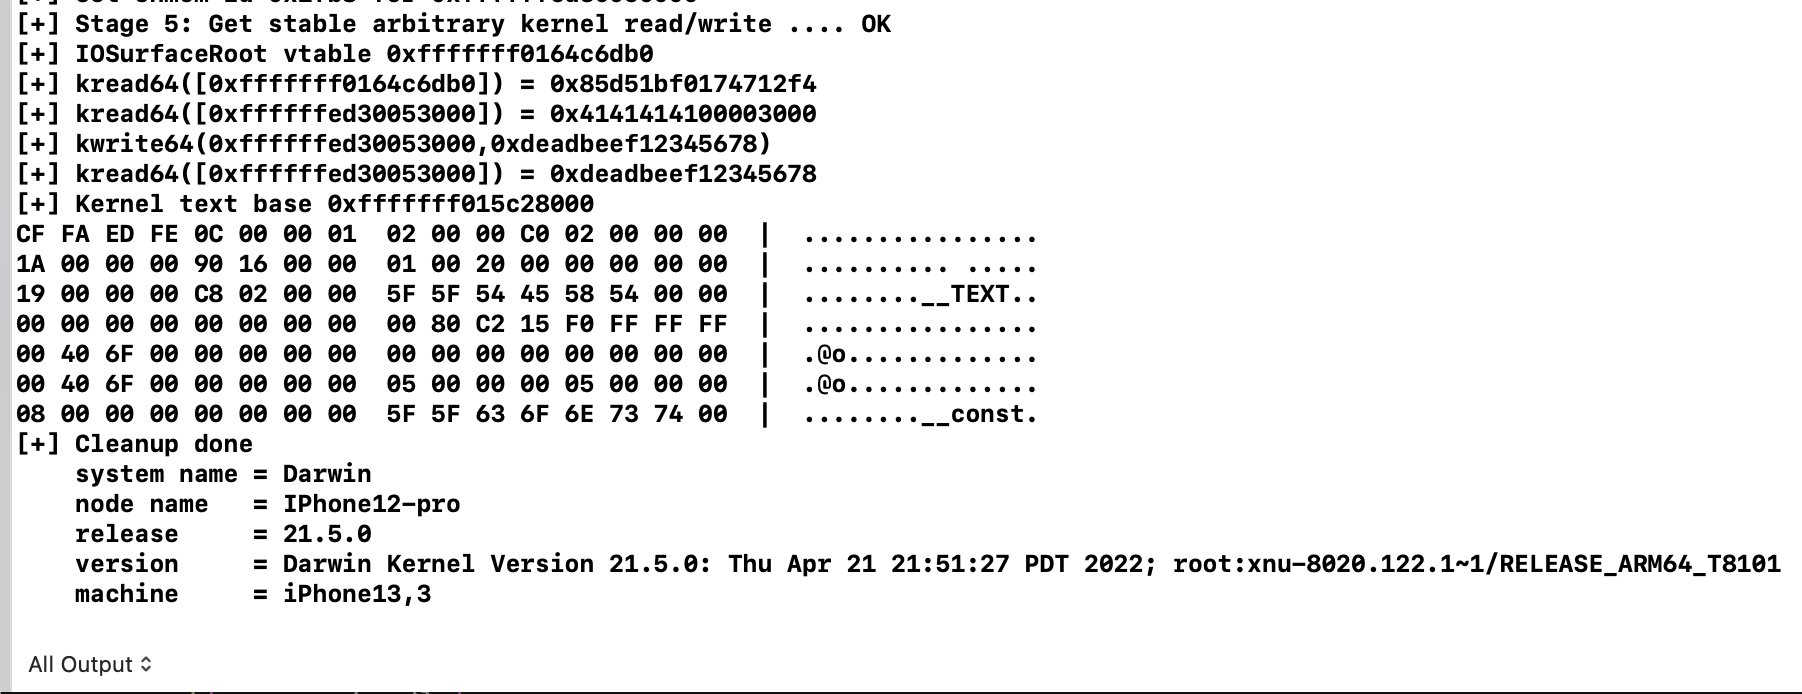 ox1111/cve-2022-32898
Technical analysis and exploit demonstration of CVE-2022-32898, a kernel memory corruption vulnerability in Apple Neural Engine driver, with detailed…
 iddoeldor/frida-snippets
Hand-crafted Frida examples
 michalmalik/osx-re-101
A collection of resources for OSX/iOS reverse engineering.
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 b1n4r1b01/n-days
Curated collection of iOS kernel and userland exploit PoCs and writeups for in-the-wild and researched CVEs, including binary-diffed vulnerability…
 potmdehex/multicast_bytecopy
kernel r/w exploit for iOS 15.0 - 15.1.1
 illusionofchaos/ios-nehelper-wifi-info-0day
iOS 15 0-day exploit (still works in 15.0.2)
 amrudesh1/morf
Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…
 thelicato/friman
Frida version management tool
 tihmstar/freepw_tc7200eploit
Technicolor TC7200 - Credentials Disclosure CVE : CVE-2014-1677
 owenpawl/cve-2026-84600
Information on the security content of Apple software updates
 verygenericname/cve-2021-30955-poc-ipa
Proof-of-concept IPA for CVE-2021-30955, targeting iOS 15.0-15.2b1, demonstrating a local privilege escalation vulnerability.
 realrodri/exploiteameesta
iOS app to check device compatibility with CVE-2021-30937 vulnerability, displaying alerts and popups during the process.
 alipay/ios-malicious-bithunter
iOS Malicious Bit Hunter is a malicious plug-in detection engine for iOS applications. It can analyze the head of the macho file of the injected…
 alterakey/trueseeing
Non-decompiling iOS/Android app vulnerability scanner (DC25 demo lab, CB17)
 rani-i/bluetoothdpoc
CVE-2018-4087 PoC








