
 #1
Tools for managing, sharing, and integrating Indicators of Compromise (IOCs) into security defenses.
Kitploit recommended
 c3-h2/log4j_attacker_iplist
Curated list of attacker IP addresses targeting the Log4j vulnerability (CVE-2021-44228) for threat intelligence, incident response, and network…
 dominic471/qub-network-security-cve-2023-20198
Analysis, detection, and mitigation of CVE-2023-20198 exploitation in Cisco IOS XE – QUB CSC3064 Network Security Assessment
 honeynet/log4shell-data
Data we are receiving from our honeypots about CVE-2021-44228
 michaael01/letsdefend--soc-342-cve-2025-53770-sharepoint-exploit-toolshell
Detailed walkthrough of CVE-2025-53770 (ToolShell) SharePoint zero-day exploitation, including RCE analysis, MachineKey exfiltration, payload…
 nivdolgin/cve-2018-13379
Hunting CVE-2018-13379
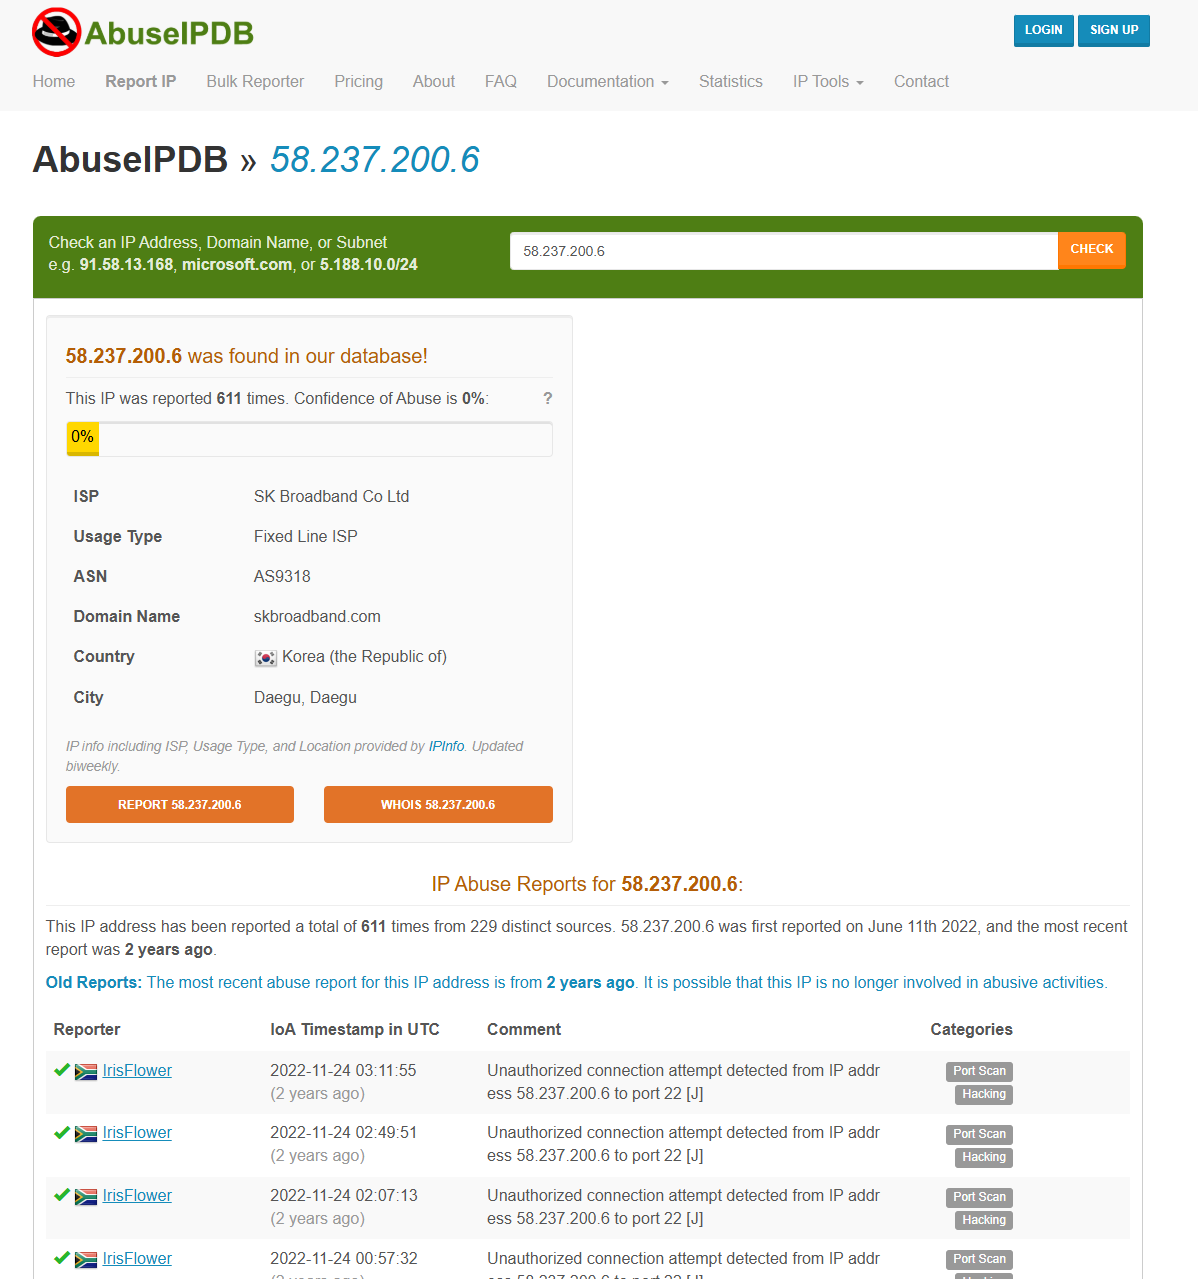 cyprianatsyor/letsdefend-cve-2022-41082-exploitation-attempt
Detailed incident report and educational analysis of CVE-2022-41082 (ProxyNotShell) exploitation attempt on Microsoft Exchange Server, including…
 bakedmuffinman/blacklotusdetection
Created to help detect IOCs for CVE-2022-21894: The BlackLotus campaign
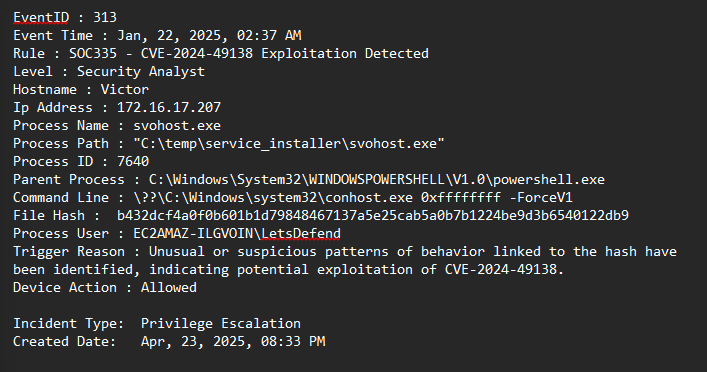 cyprianatsyor/letsdefend-cve-2024-49138-investigation
Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.
 ben-smash/l4j-info
Compiling links of value i find regarding CVE-2021-44228
 jmussmann/cve-2023-4966-iocs
Python script to search Citrix NetScaler logs for possible CVE-2023-4966 exploitation.
 hahasagined/cve-2024-3400
External Dynamic List (EDL) of IP addresses actively exploiting CVE-2024-3400, for use in firewall and SIEM blocklists to defend against ongoing…
 ernestak/sigma-rule-for-cve-2022-30190
Sigma rule for detecting exploitation of CVE-2022-30190 (Follina) via Windows process creation events, enabling SOC teams to identify malicious…
 niklasmato/fortileak-01-2025-be
This repository contains informaion about the Fortigate firewall vulnerability (CVE-2022-40684) and affected data that were publicly disclosed by the…
 tica506/siem-queries-for-cve-2021-44228
SIEM query collection for detecting Log4Shell (CVE-2021-44228) exploitation attempts. Provides ready-to-use detection rules for security monitoring…
 mikesxrs/cve-2023-21716_yara_results
Results of retrohunt for files matching YARA rules from https://github.com/AmgdGocha/Detection-Rules/blob/main/CVE-2023-21716.yar
 ncsc-nl/php2shell
Operational advisory repository tracking CVE-2026-109618 and CVE-2026-109619 PHP RCE flaws, with detection and mitigation guidance, affected software…
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 nextronsystems/iocs
Indicators of compromise from to analysis and research by Nextron Threat Research team








