
 #1
Tools for managing, sharing, and integrating Indicators of Compromise (IOCs) into security defenses.
Kitploit recommended

 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 cybershujin/prompt-injection-in-the-wild
Tracker of publicly reported prompt-injection techniques, broken down by delivery method, encoding, and propagation behavior, with confirmed models,…
 svtagan/wp-cve-2026-87902
Read-only PHP diagnostic script that checks WordPress version, core checksums, extra PHP files, and known plugin paths for CVE-2026-87902 exposure…
 itskill-jp/wordpress-upgrade-check
Read-only check of every WordPress core version on a server. Flags CVE-2026-87902 (fixed in 7.1.2 and backports), auto-updates turned off, and…
 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 asmitdesai/ubuntils
Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
 dmitry-matvienko/malware-analysis-fake-hwmonitor
Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor

 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…
 wadesweaponshed/cve-2026-93616_checks
Shell and SmartDashboard scripts that check Check Point management servers for indicators of compromise tied to CVE-2026-93616, including rogue…
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
 suominen/cve-2025-39682
Single-page tracker recording per-distribution patch status for CVE-2025-39682, a use-after-free in the Linux kernel kTLS receive path.
 suominen/cve-2026-53266
Single-page tracker recording which Linux distributions have shipped fixes for the CVE-2026-53266 netfilter ebtables SNAT ARP-rewrite page-cache…
 soc-irdoc/irdoc-app
Incident Response Documentation Platform
 basitsajidsoc/soc-investigation-cve-2024-49138
Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
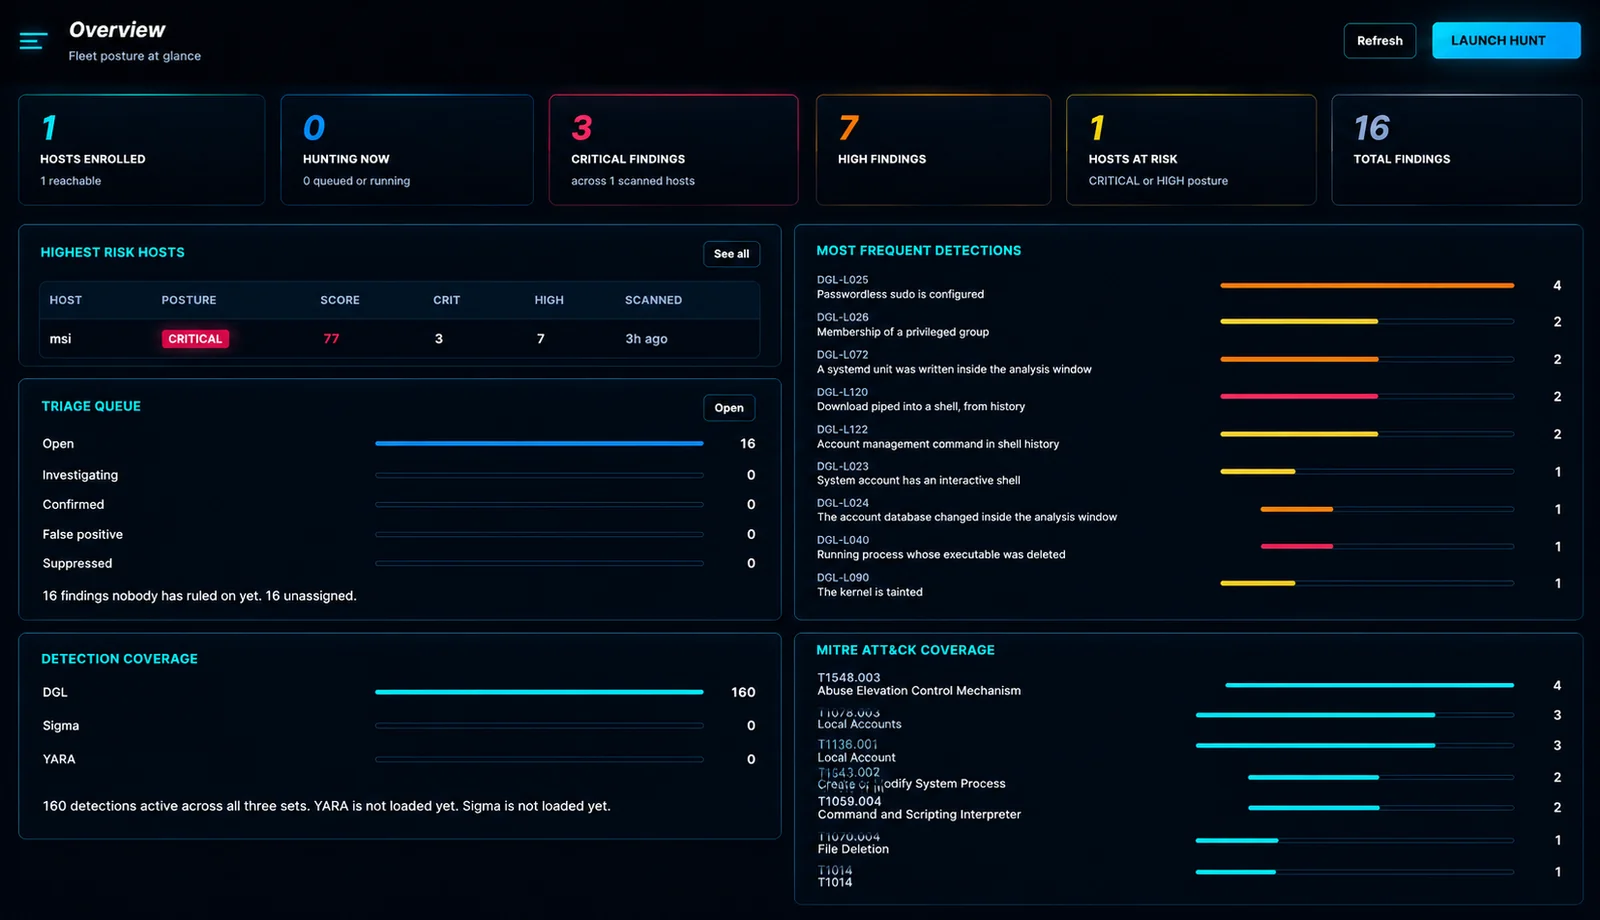 douglas-042/douglas-042-hq
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…








