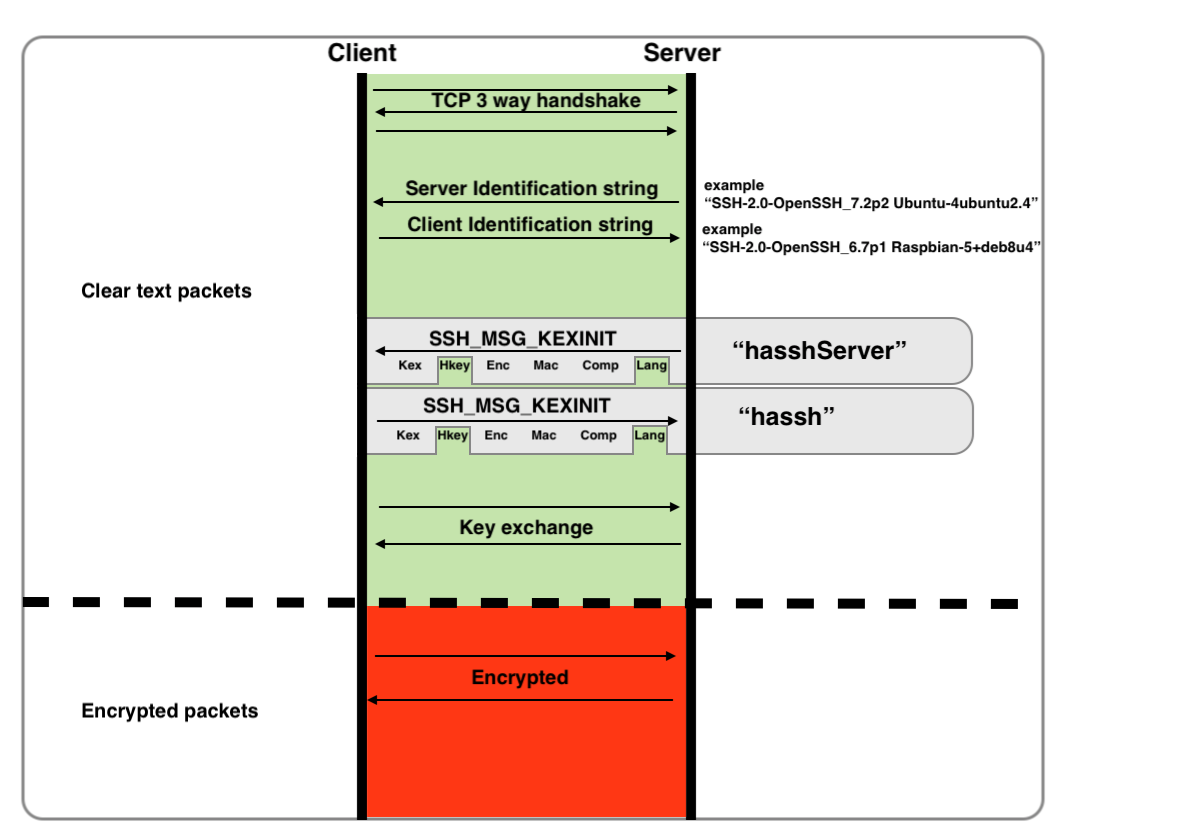
#1
IDS/IPS systems, network monitoring, anomaly-based detection, and threat alerting tools.
Kitploit recommended

 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
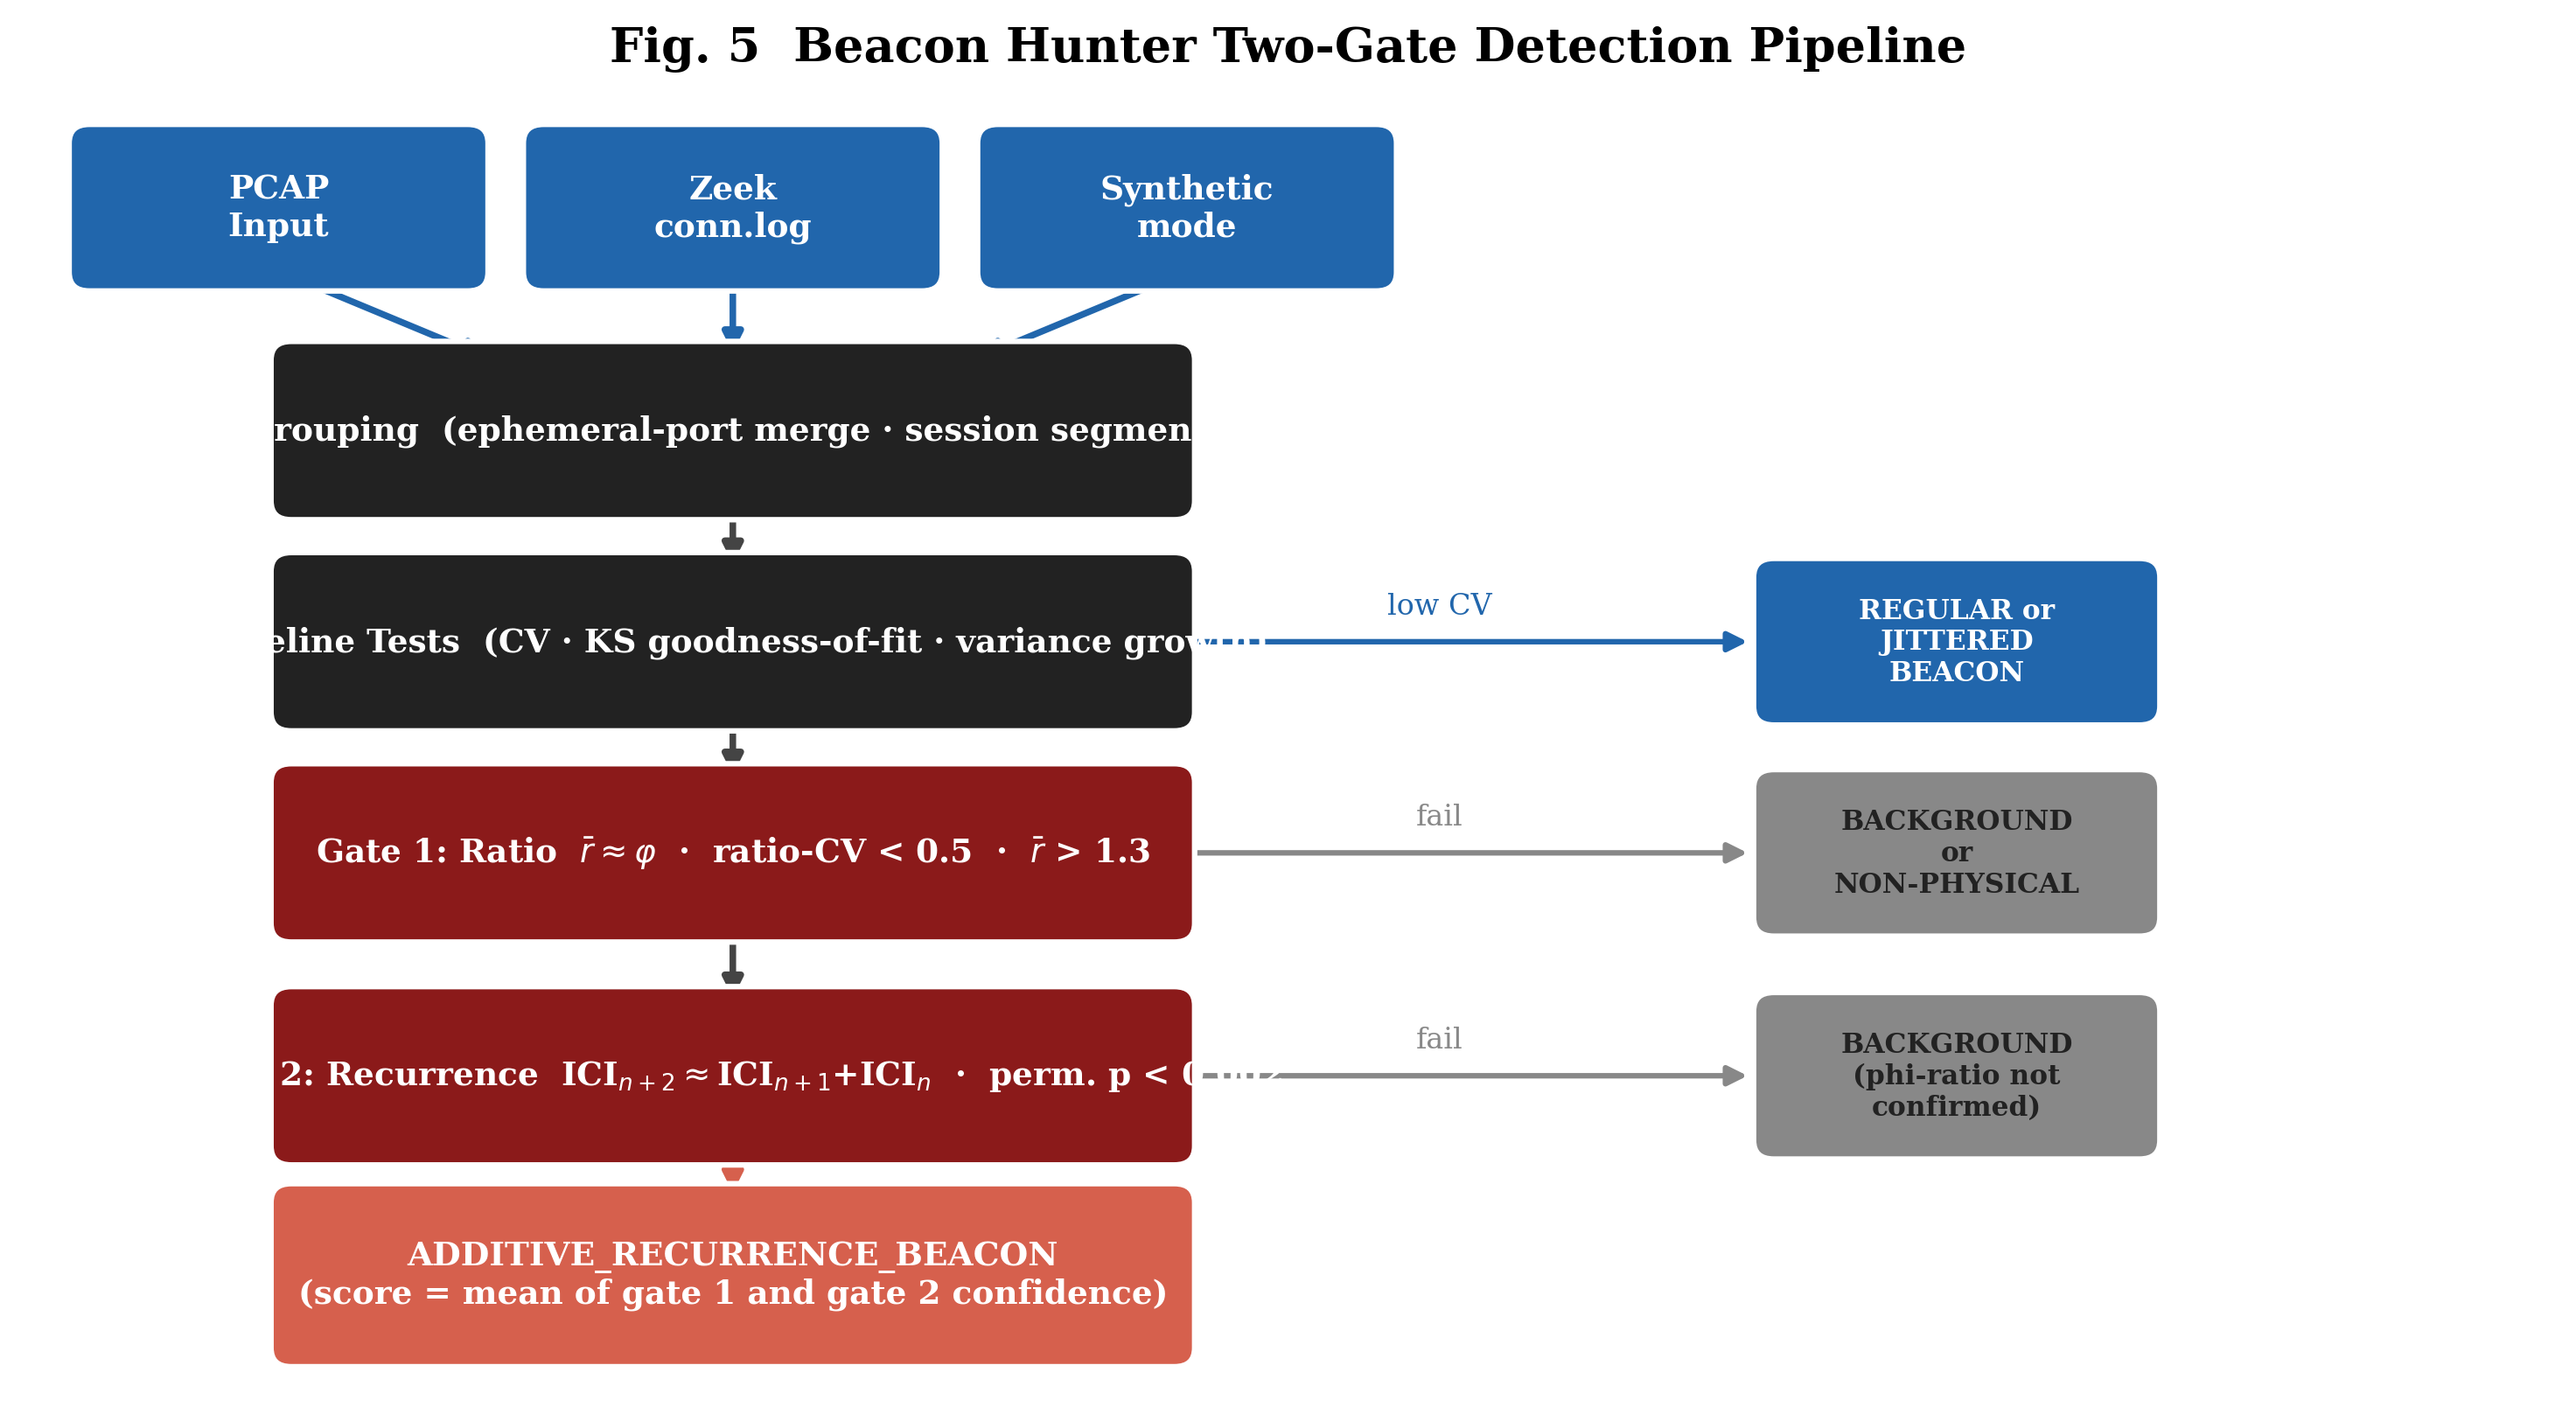 mrcord77/beacon-hunter
Detects phi-structured C2 beacons that evade RITA and standard regularity-based detectors
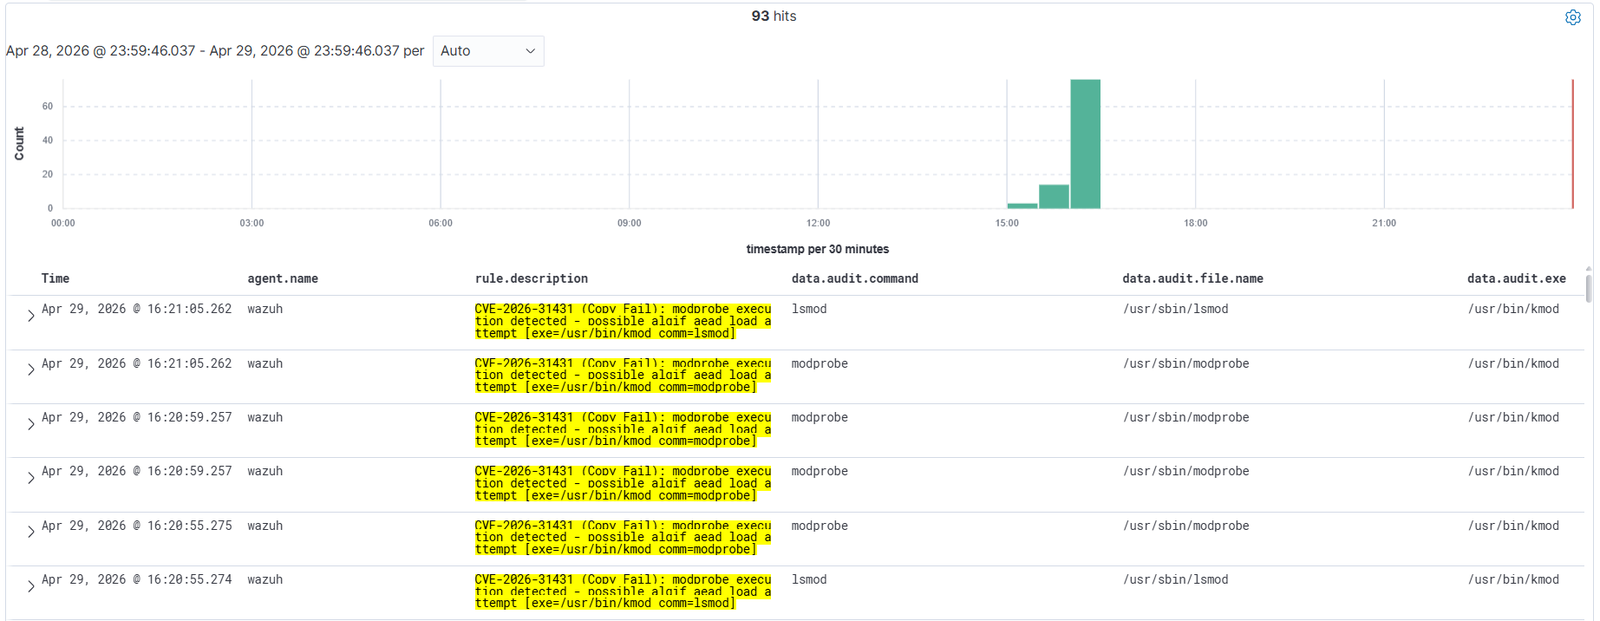 mym0us3r/copy-fail-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-31431 (Copy Fail) - Linux Local Privilege Escalation via authencesn page cache write
 atnetws/fail2ban-log4j
fail2ban filter that catches attacks againts log4j CVE-2021-44228
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 h4ckm310n/cve-2022-0847-ebpf
An eBPF program to detect attacks on CVE-2022-0847
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
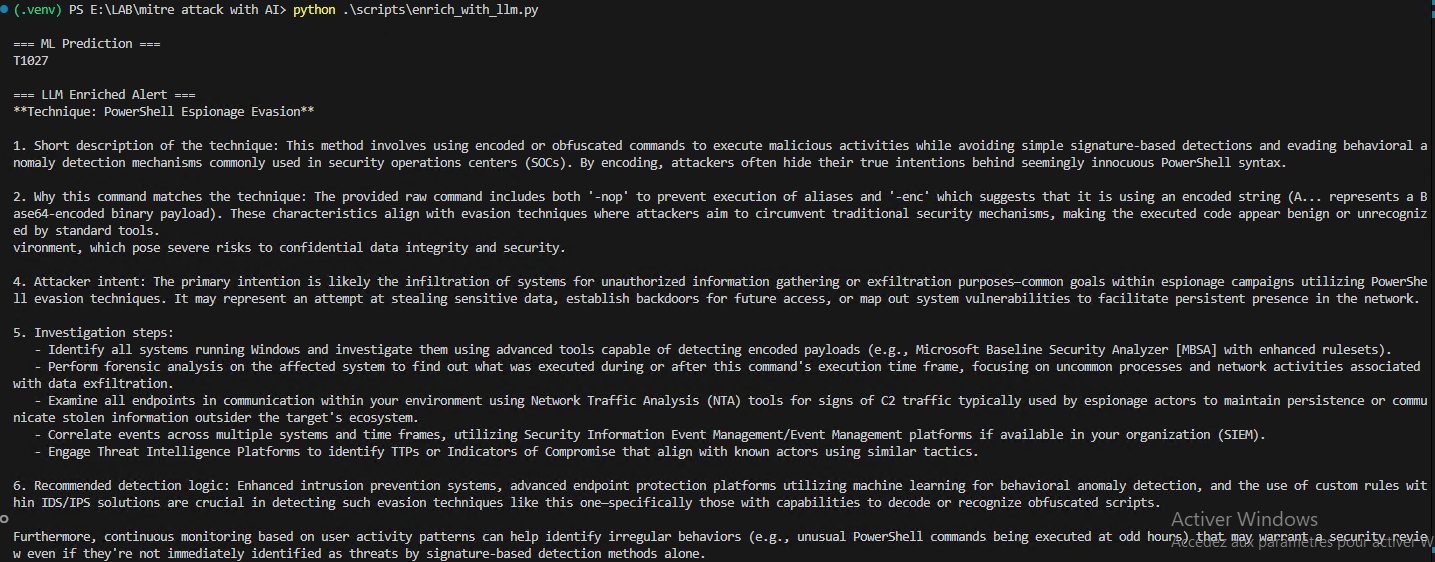 mouna23/ai-driven-mitre-attack
This repository demonstrates a machine learning pipeline for detecting MITRE ATT&CK techniques from logs and enriching the output using a local LLM.
 referefref/cupspot-2024-47177
PoC honeypot for detecting exploit attempts against CVE-2024-47177
 corelight/cve-2020-5902-f5bigip
A network detection package for CVE-2020-5902, a CVE10.0 vulnerability affecting F5 Networks, Inc BIG-IP devices.

 ndaal_open_source/ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 synacktiv/nmap-farewell
Automated Network Security with Rust: Detecting and Blocking Port Scanners