
 #1
IDS/IPS systems, network monitoring, anomaly-based detection, and threat alerting tools.
Kitploit recommended
 lucadibello/network-attack-detection
Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques
 corelight/pingback
A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.
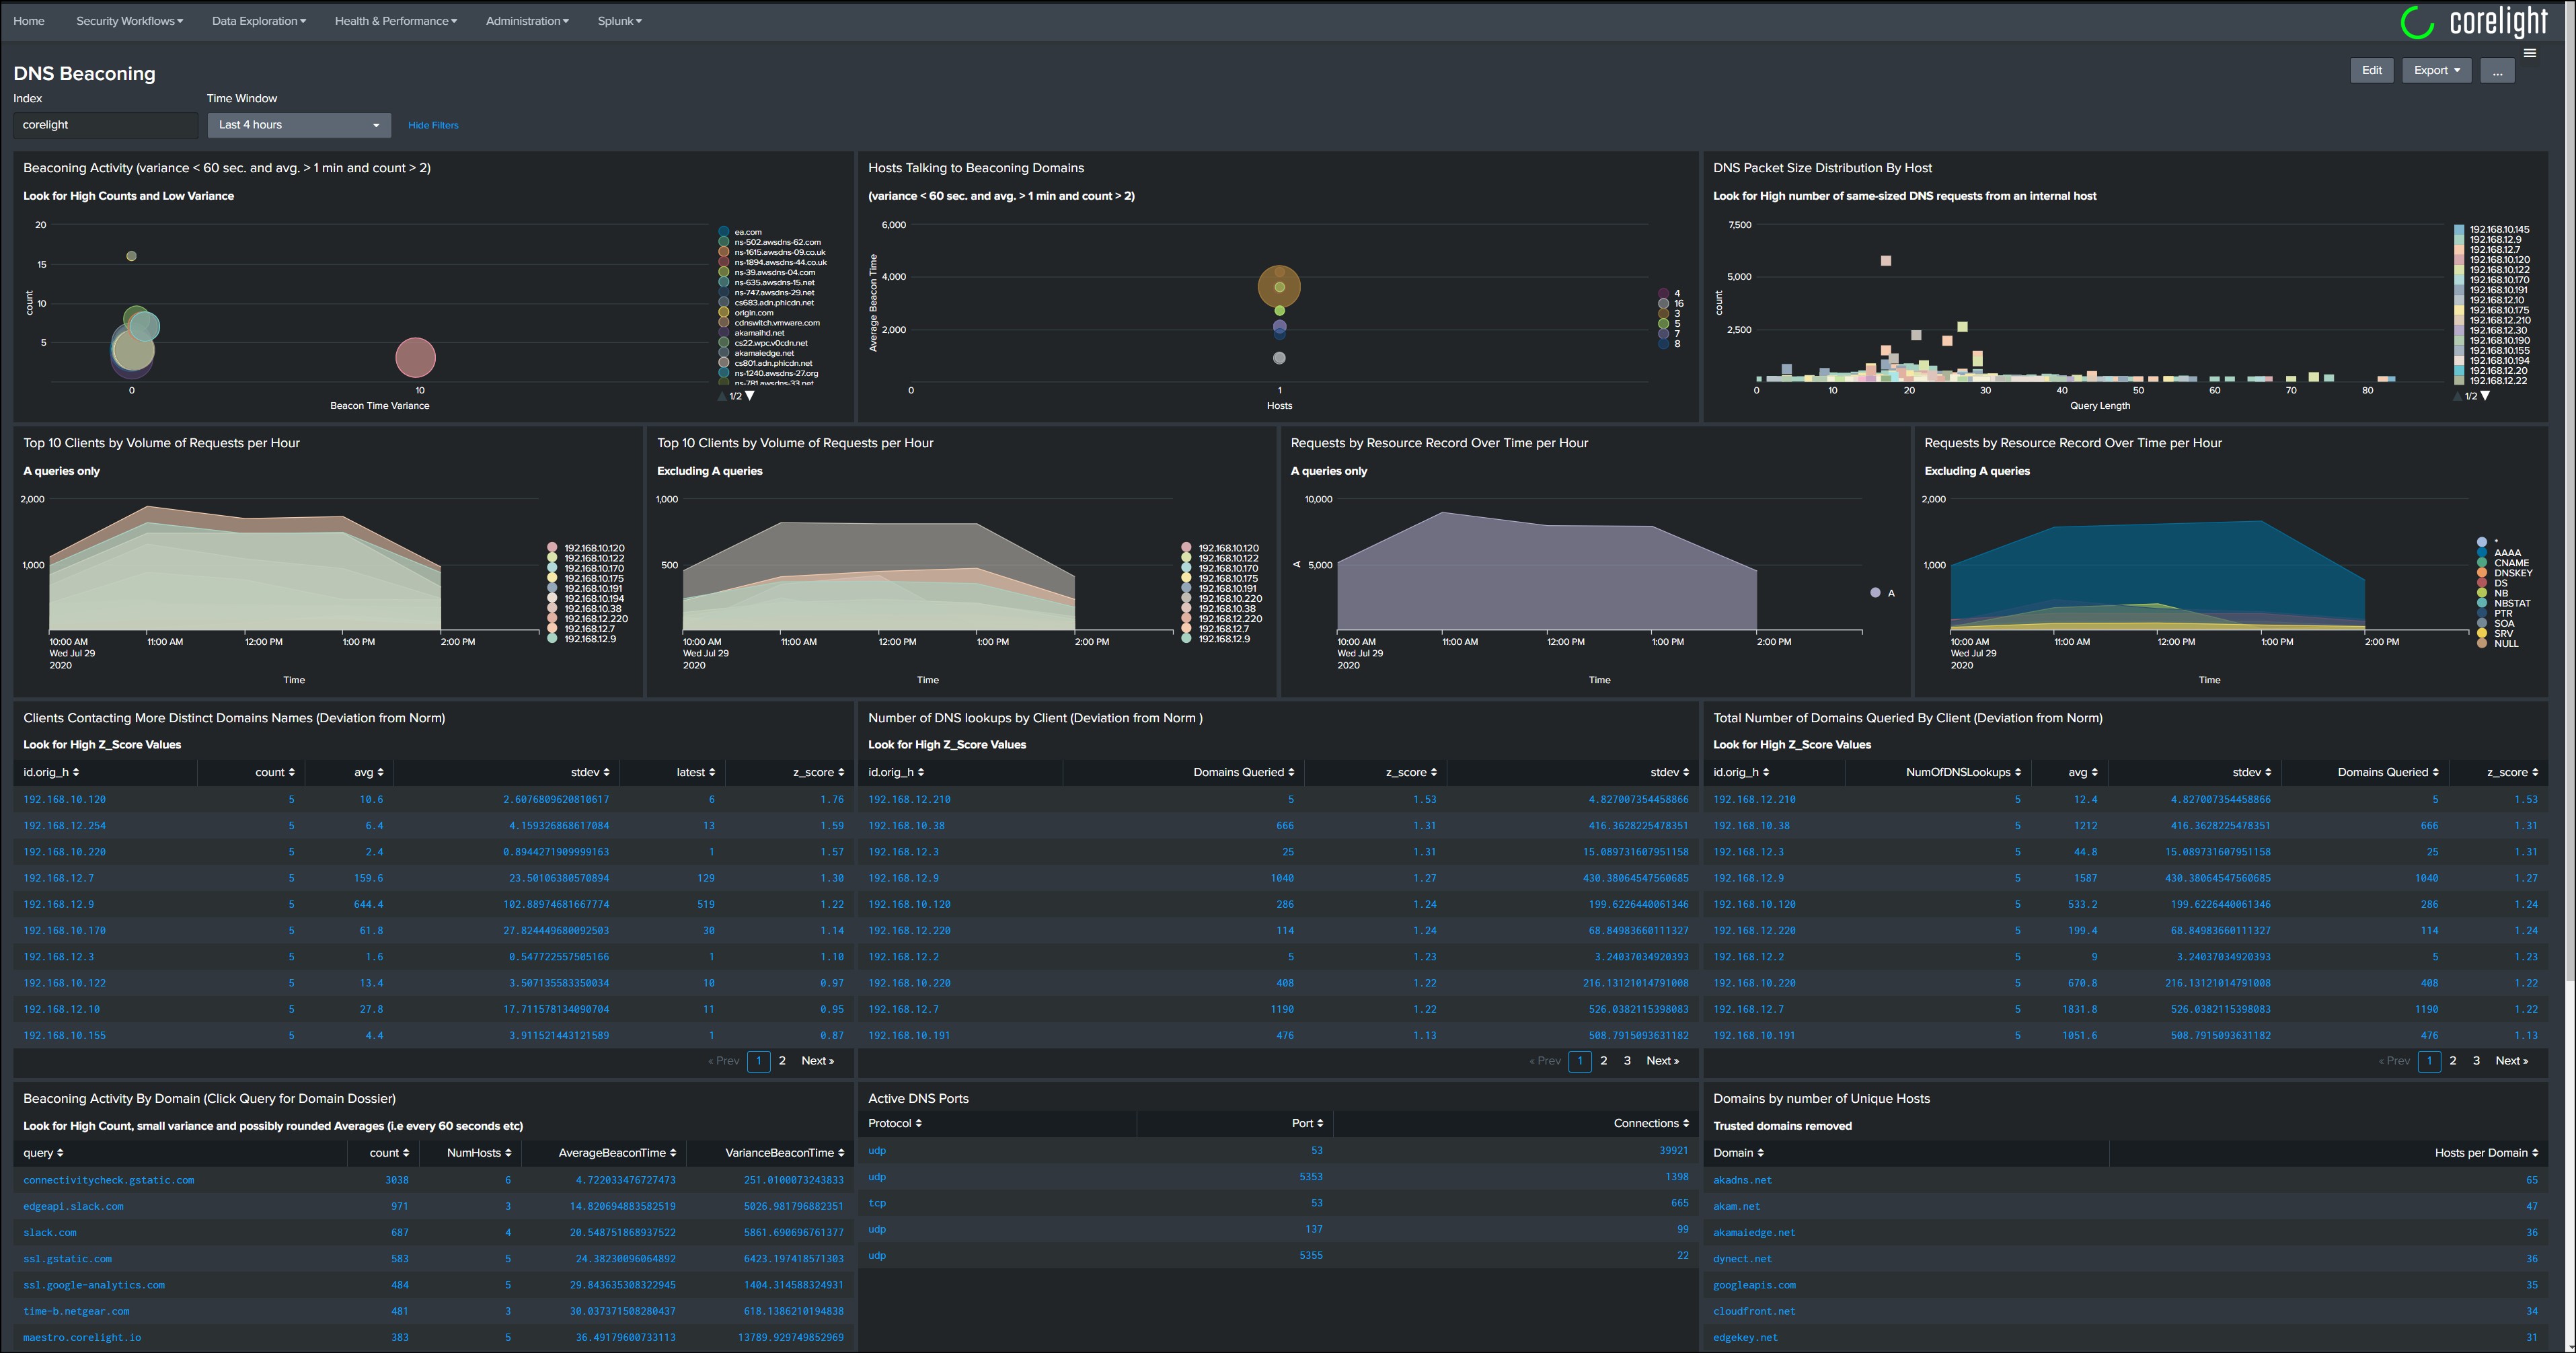 corelight/dashboards-splunk-dns-hunting-beaconing
DNS Dashboard for hunting and identifying beaconing
 johnearle/coalmine
Cloud Canary Object Orchestration Management Platform
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 corelight/callstranger-detector
Zeek plugin detecting CallStranger (CVE-2020-12695) exploitation via UPnP SUBSCRIBE/NOTIFY analysis, identifying DDoS amplification, data…
 codextf2/cobaltstrike-sleepmask-yara
Just a git repo for the sleepmask detection rule i found in https://codex-7.gitbook.io/codexs-terminal-window/blue-team/detecting-cobalt-strike/sleep-…
 corelight/phantom-playbooks
Automated security incident response playbooks for Splunk Phantom, integrating Zeek logs, DNS analysis, and VirusTotal threat intelligence to…
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 pushkarreddyy/radioguard
Zero-Trust Cellular Defense Sub-Service for Android (IMSI-Catcher, 2G SMS Blaster, and 4G aLTEr Detection & Safe Routing)
 corelight/zeek-elf
A Zeek ELF File Analyzer
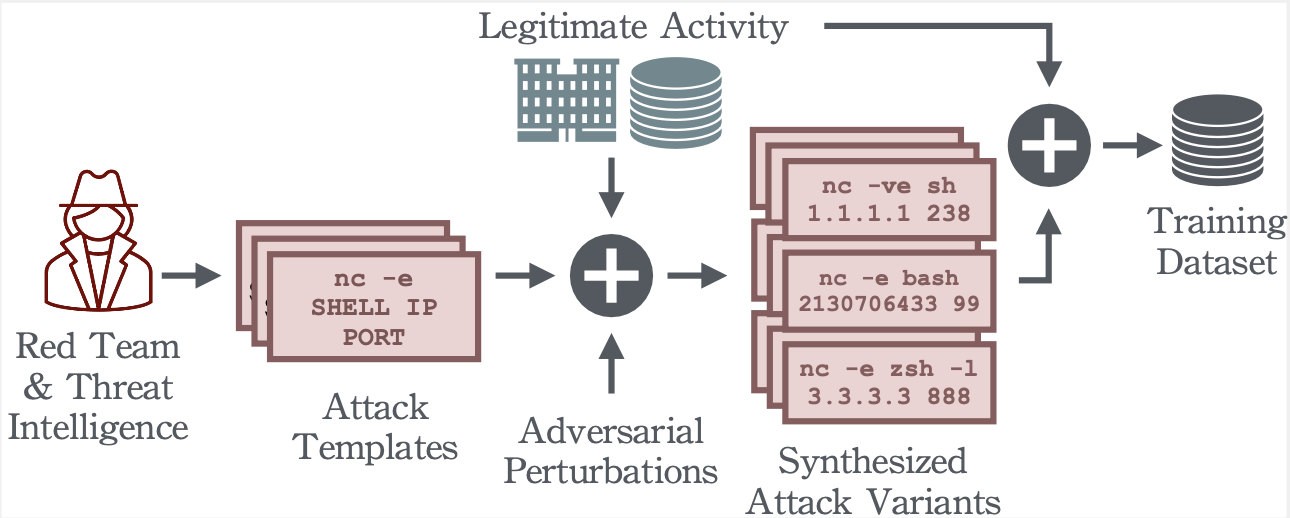 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 initconf/cve-2017-5638_struts
Bro/Zeek script for detecting Apache Struts CVE-2017-5638 reconnaissance, compromise, and malware download tracking with automated IP extraction.
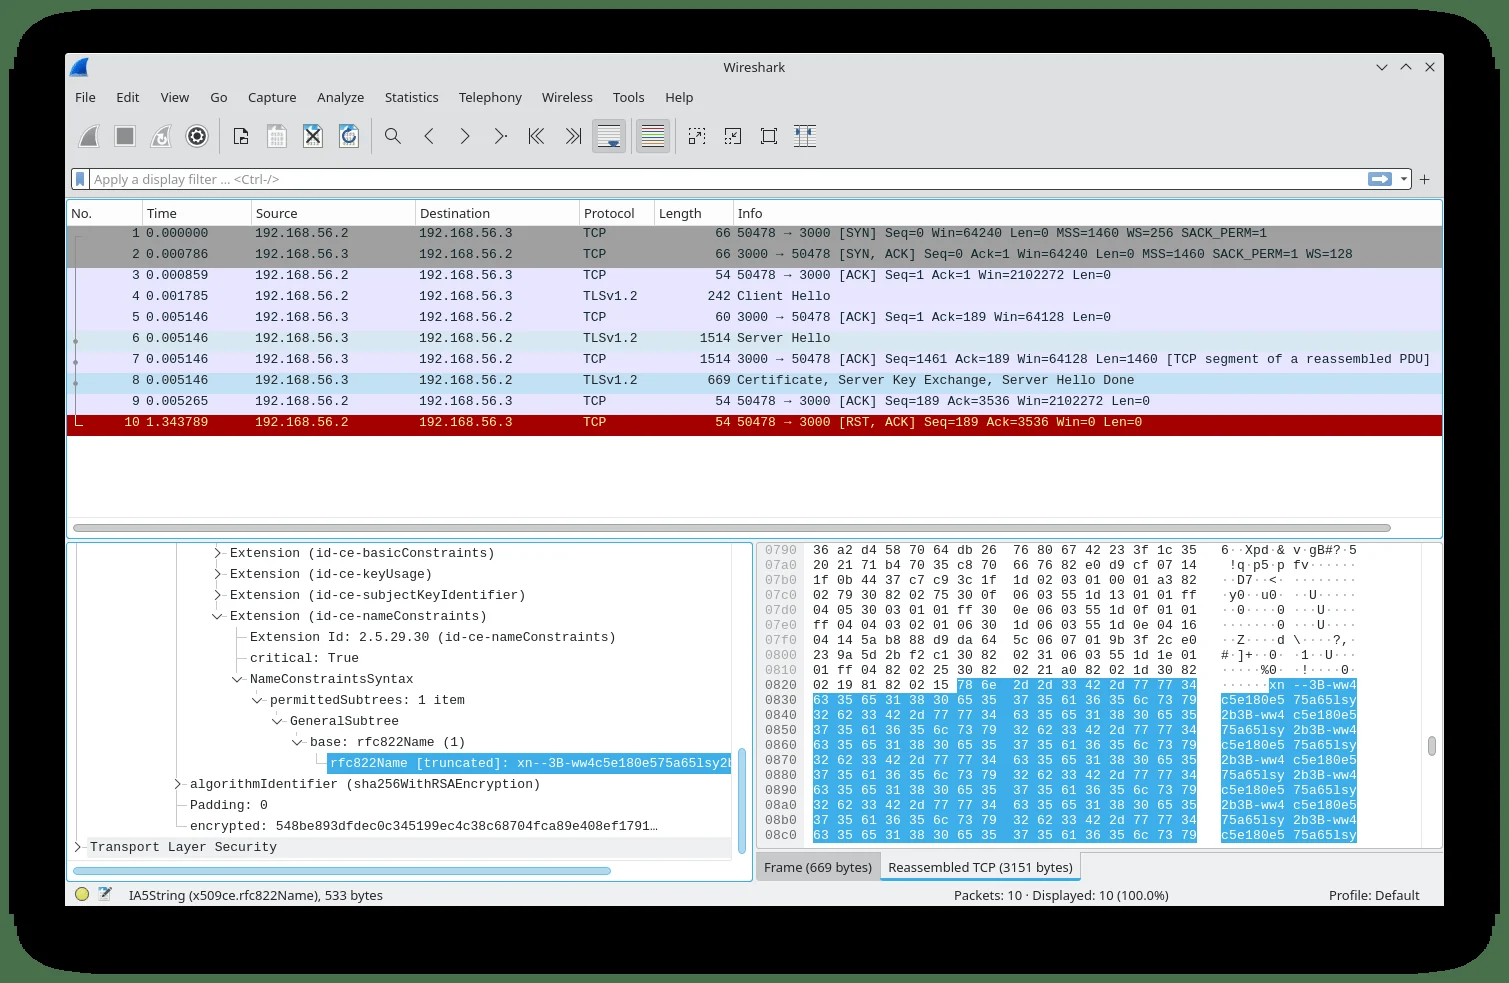 fox-it/spookyssl-pcaps
PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…
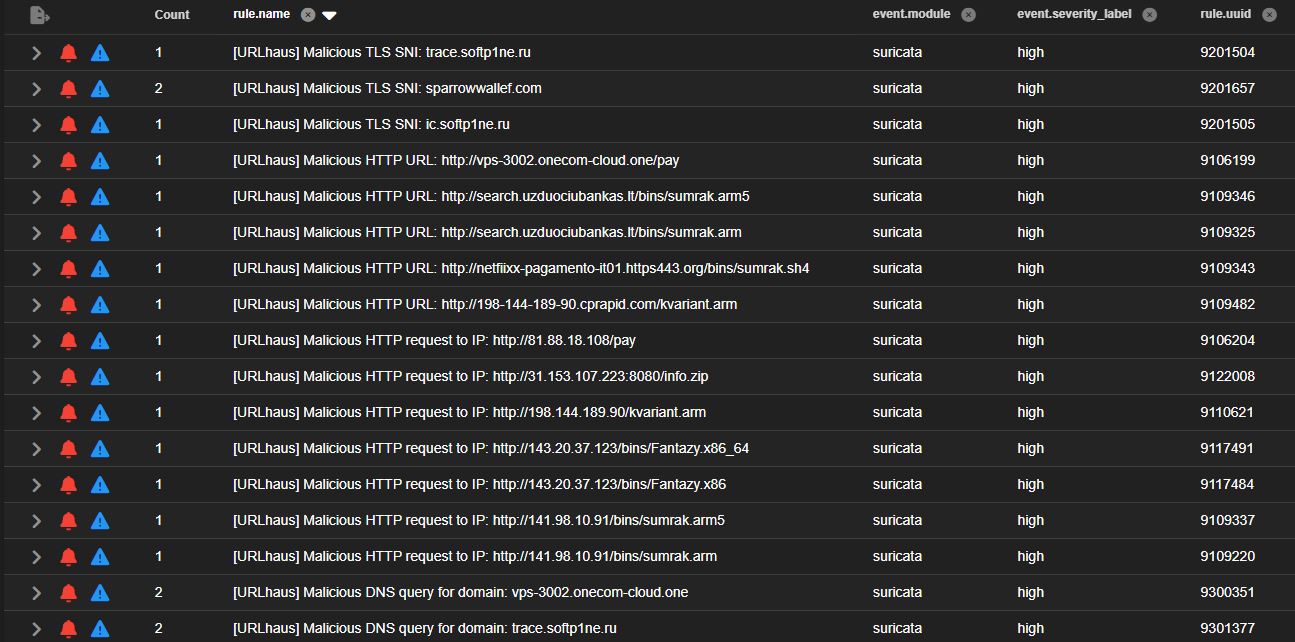 malvuln/sigint-hombre
Dynamically generated Suricata rules from real-time threat feeds
 corelight/cve-2020-16898
A network detection package for CVE-2020-16898 (Windows TCP/IP Remote Code Execution Vulnerability)
 muhammednihalmp/google-chrome-zero-day
CVE-2025-6554
 corelight/go-zeek-broker-ws
A Go library for using zeek broker's websocket API








