
 #1
IDS/IPS systems, network monitoring, anomaly-based detection, and threat alerting tools.
Kitploit recommended
 0x4d31/santamon
Lightweight macOS detection agent built on Santa’s Endpoint Security telemetry.
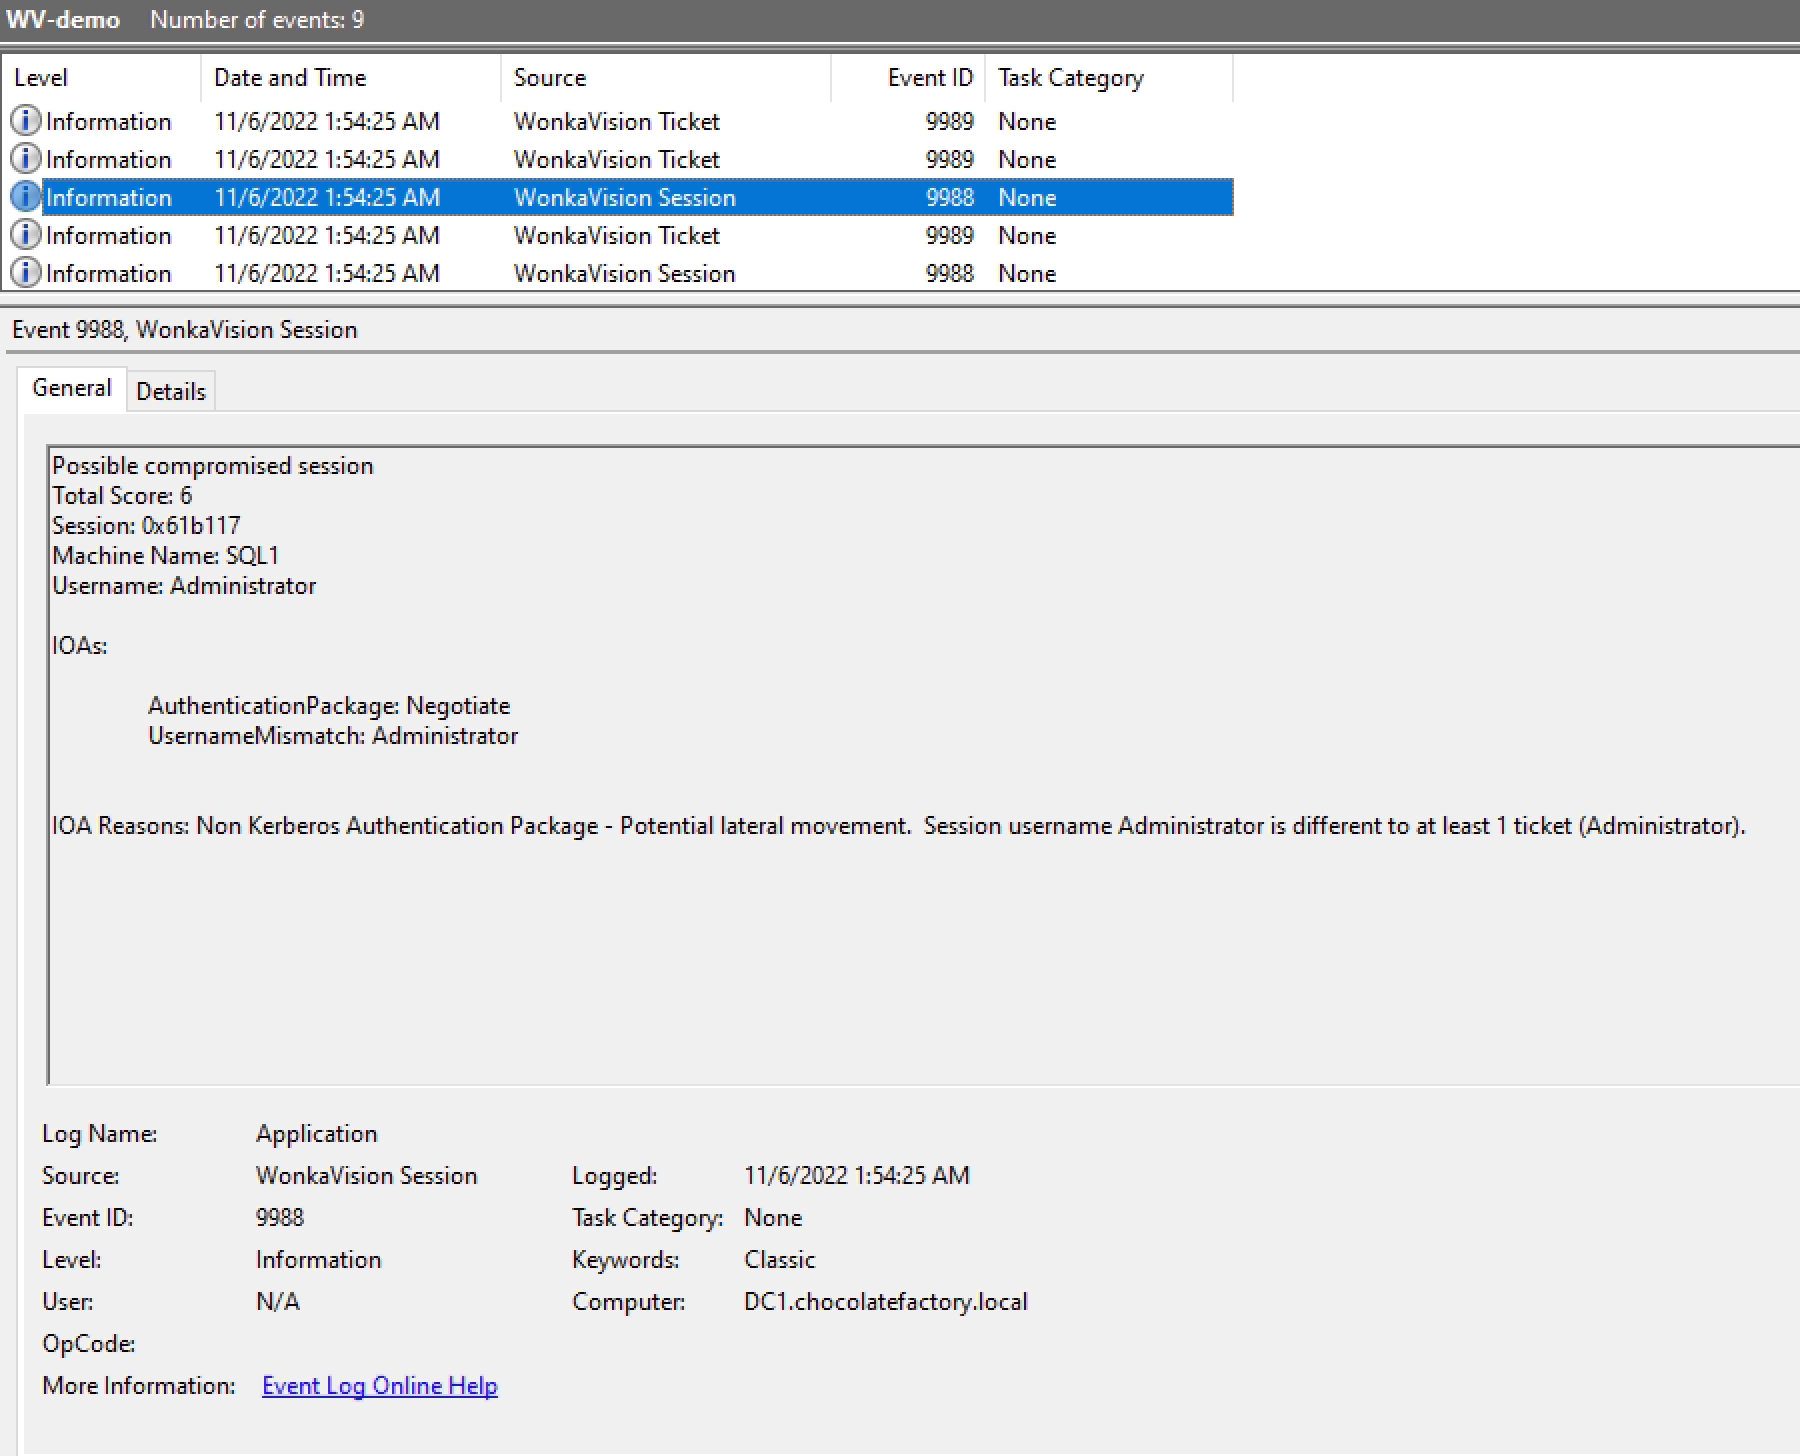 0xe7/wonkavision
Detects forged Kerberos tickets by dumping session and ticket data, scoring anomalies, and generating Windows event-log indicators for SIEM-based…
 matheuzsecurity/ksentinel
Linux kernel integrity monitor for detecting syscall hooking
 kube-tarian/tarian
eBPF-based runtime security agent for Kubernetes that detects unknown processes and file changes, enforces pre-registered constraints, and automates…
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
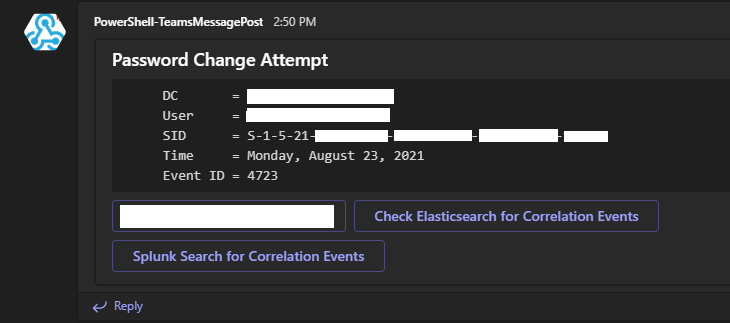 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 randomaccess3/detections
Curated repository of detection information and validation guidance for identifying malicious activity in enterprise environments.
 petabi/sniffles
Sniffles: Packet Capture Generator for IDS and Regular Expression Evaluation
 corelight/threat-hunting-guide
Structured guide to threat hunting using Zeek logs, aligned with MITRE ATT&CK framework for proactive detection of adversary tactics and techniques.
 nccgroup/ip-reputation-snort-rule-generator
A tool to generate Snort rules based on public IP reputation data
 ncsc-nl/citrix-2025
Digital forensics and incident response tool using YARA rules to scan Citrix NetScaler core dumps, disk images, and live hosts for signs of…
 fksvs/siper
XDP Based Lightweight and Fast Firewall
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
 alloysecuregroup/phantomfs
Windows honeypot using ProjFS to project decoy files that trigger Event Log and desktop alerts when accessed, with SMB remote session logging for…
 rushyo/vindicatetool
LLMNR/NBNS/mDNS Spoofing Detection Toolkit
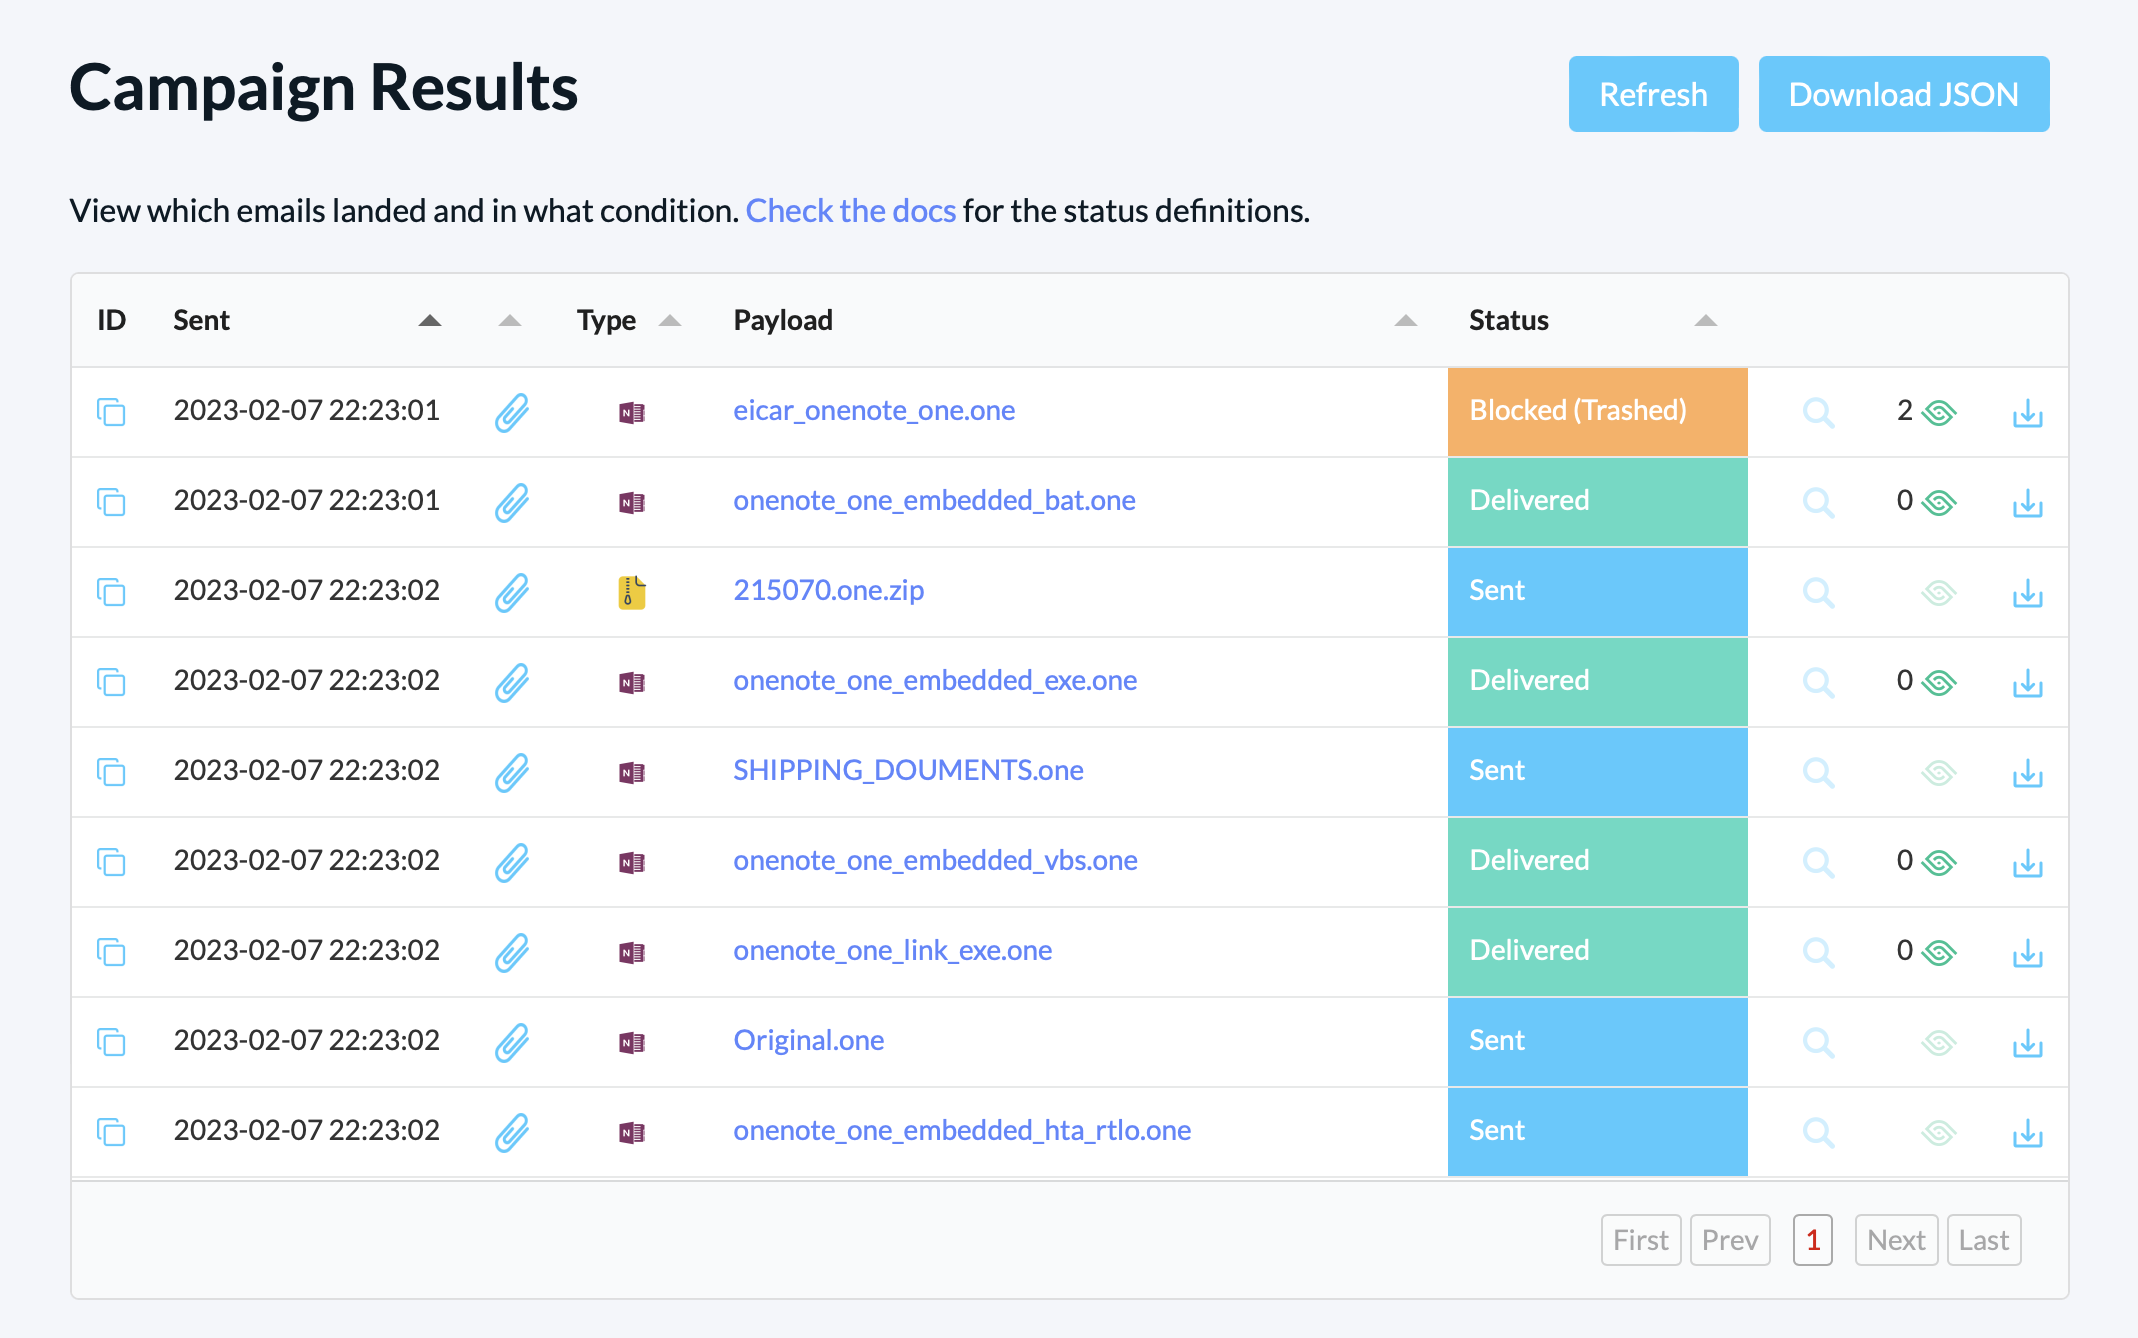 delivr-to/detections
A home for detection content developed by the delivr.to team
 corelight/zeek-long-connections
Zeek package for tracking long connections to report them before they have completed.
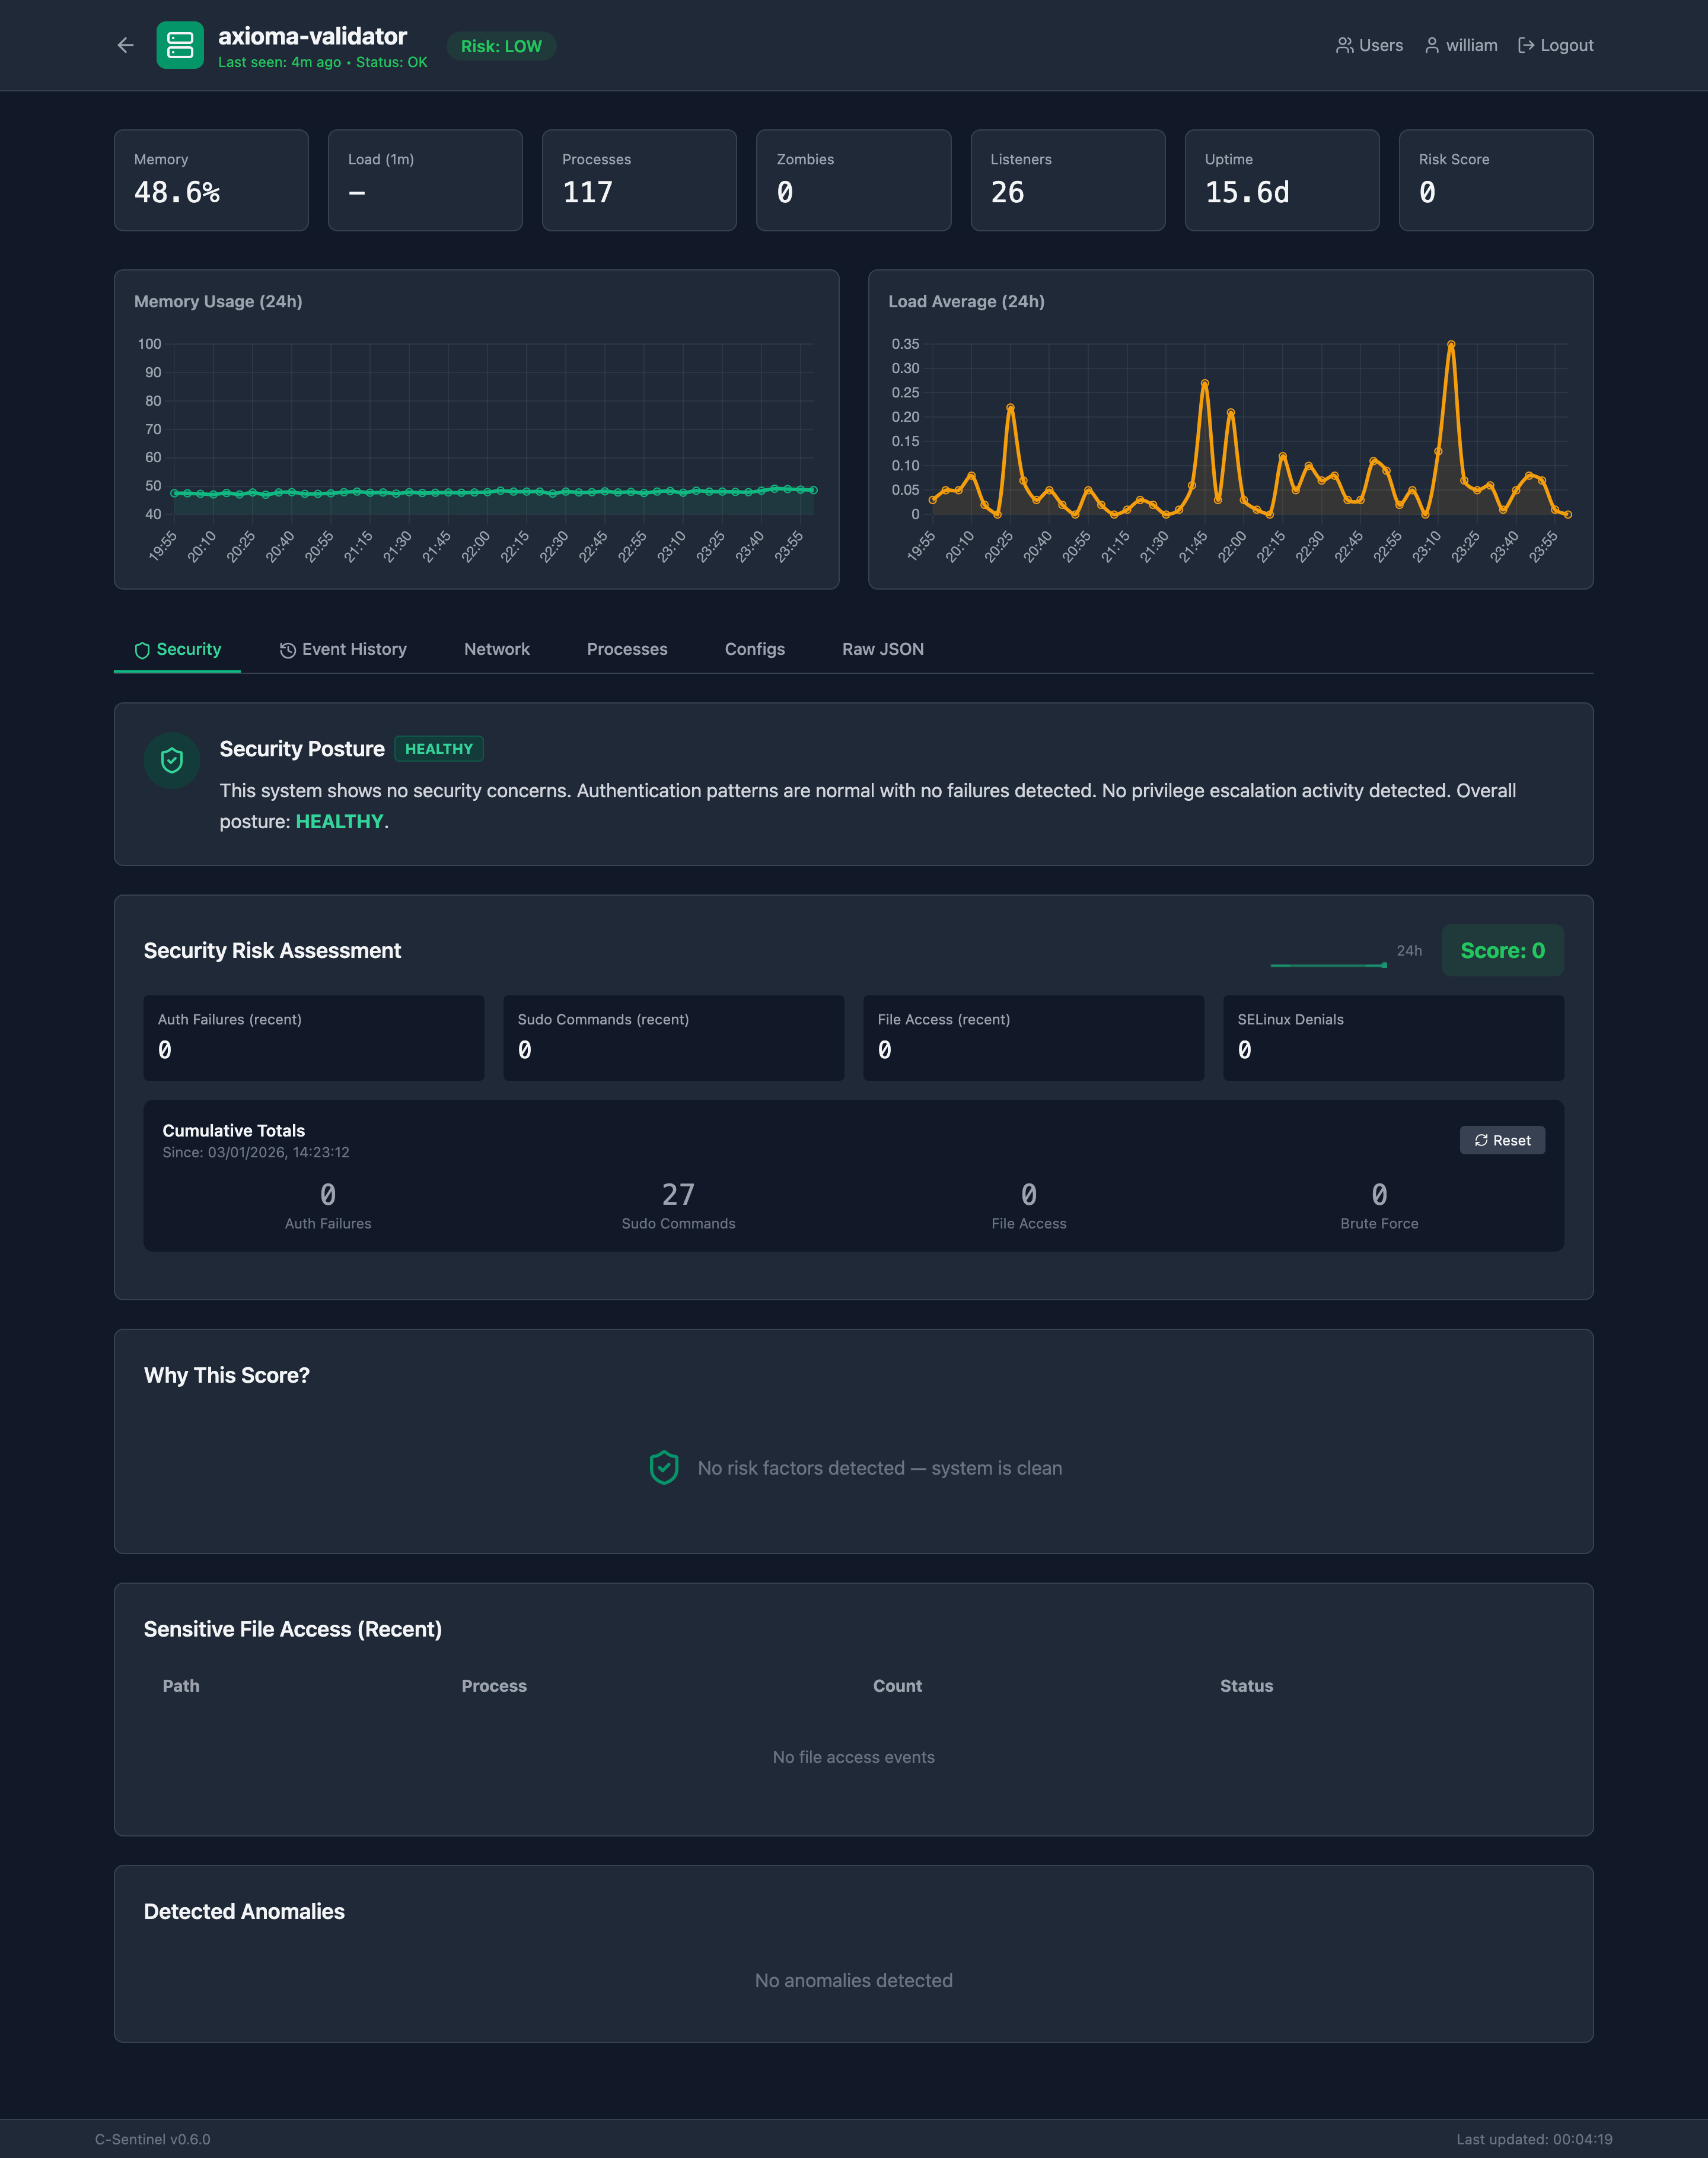 speytech/c-sentinel
Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis








