#1
 target/halogen
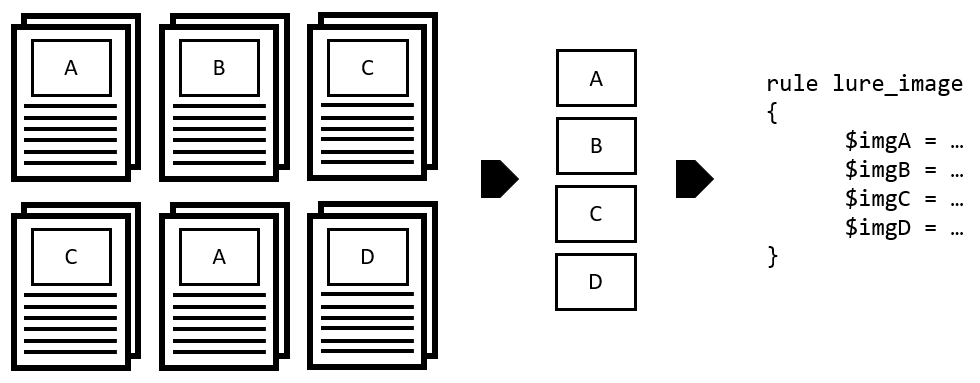
Automatically create YARA rules from malicious documents.
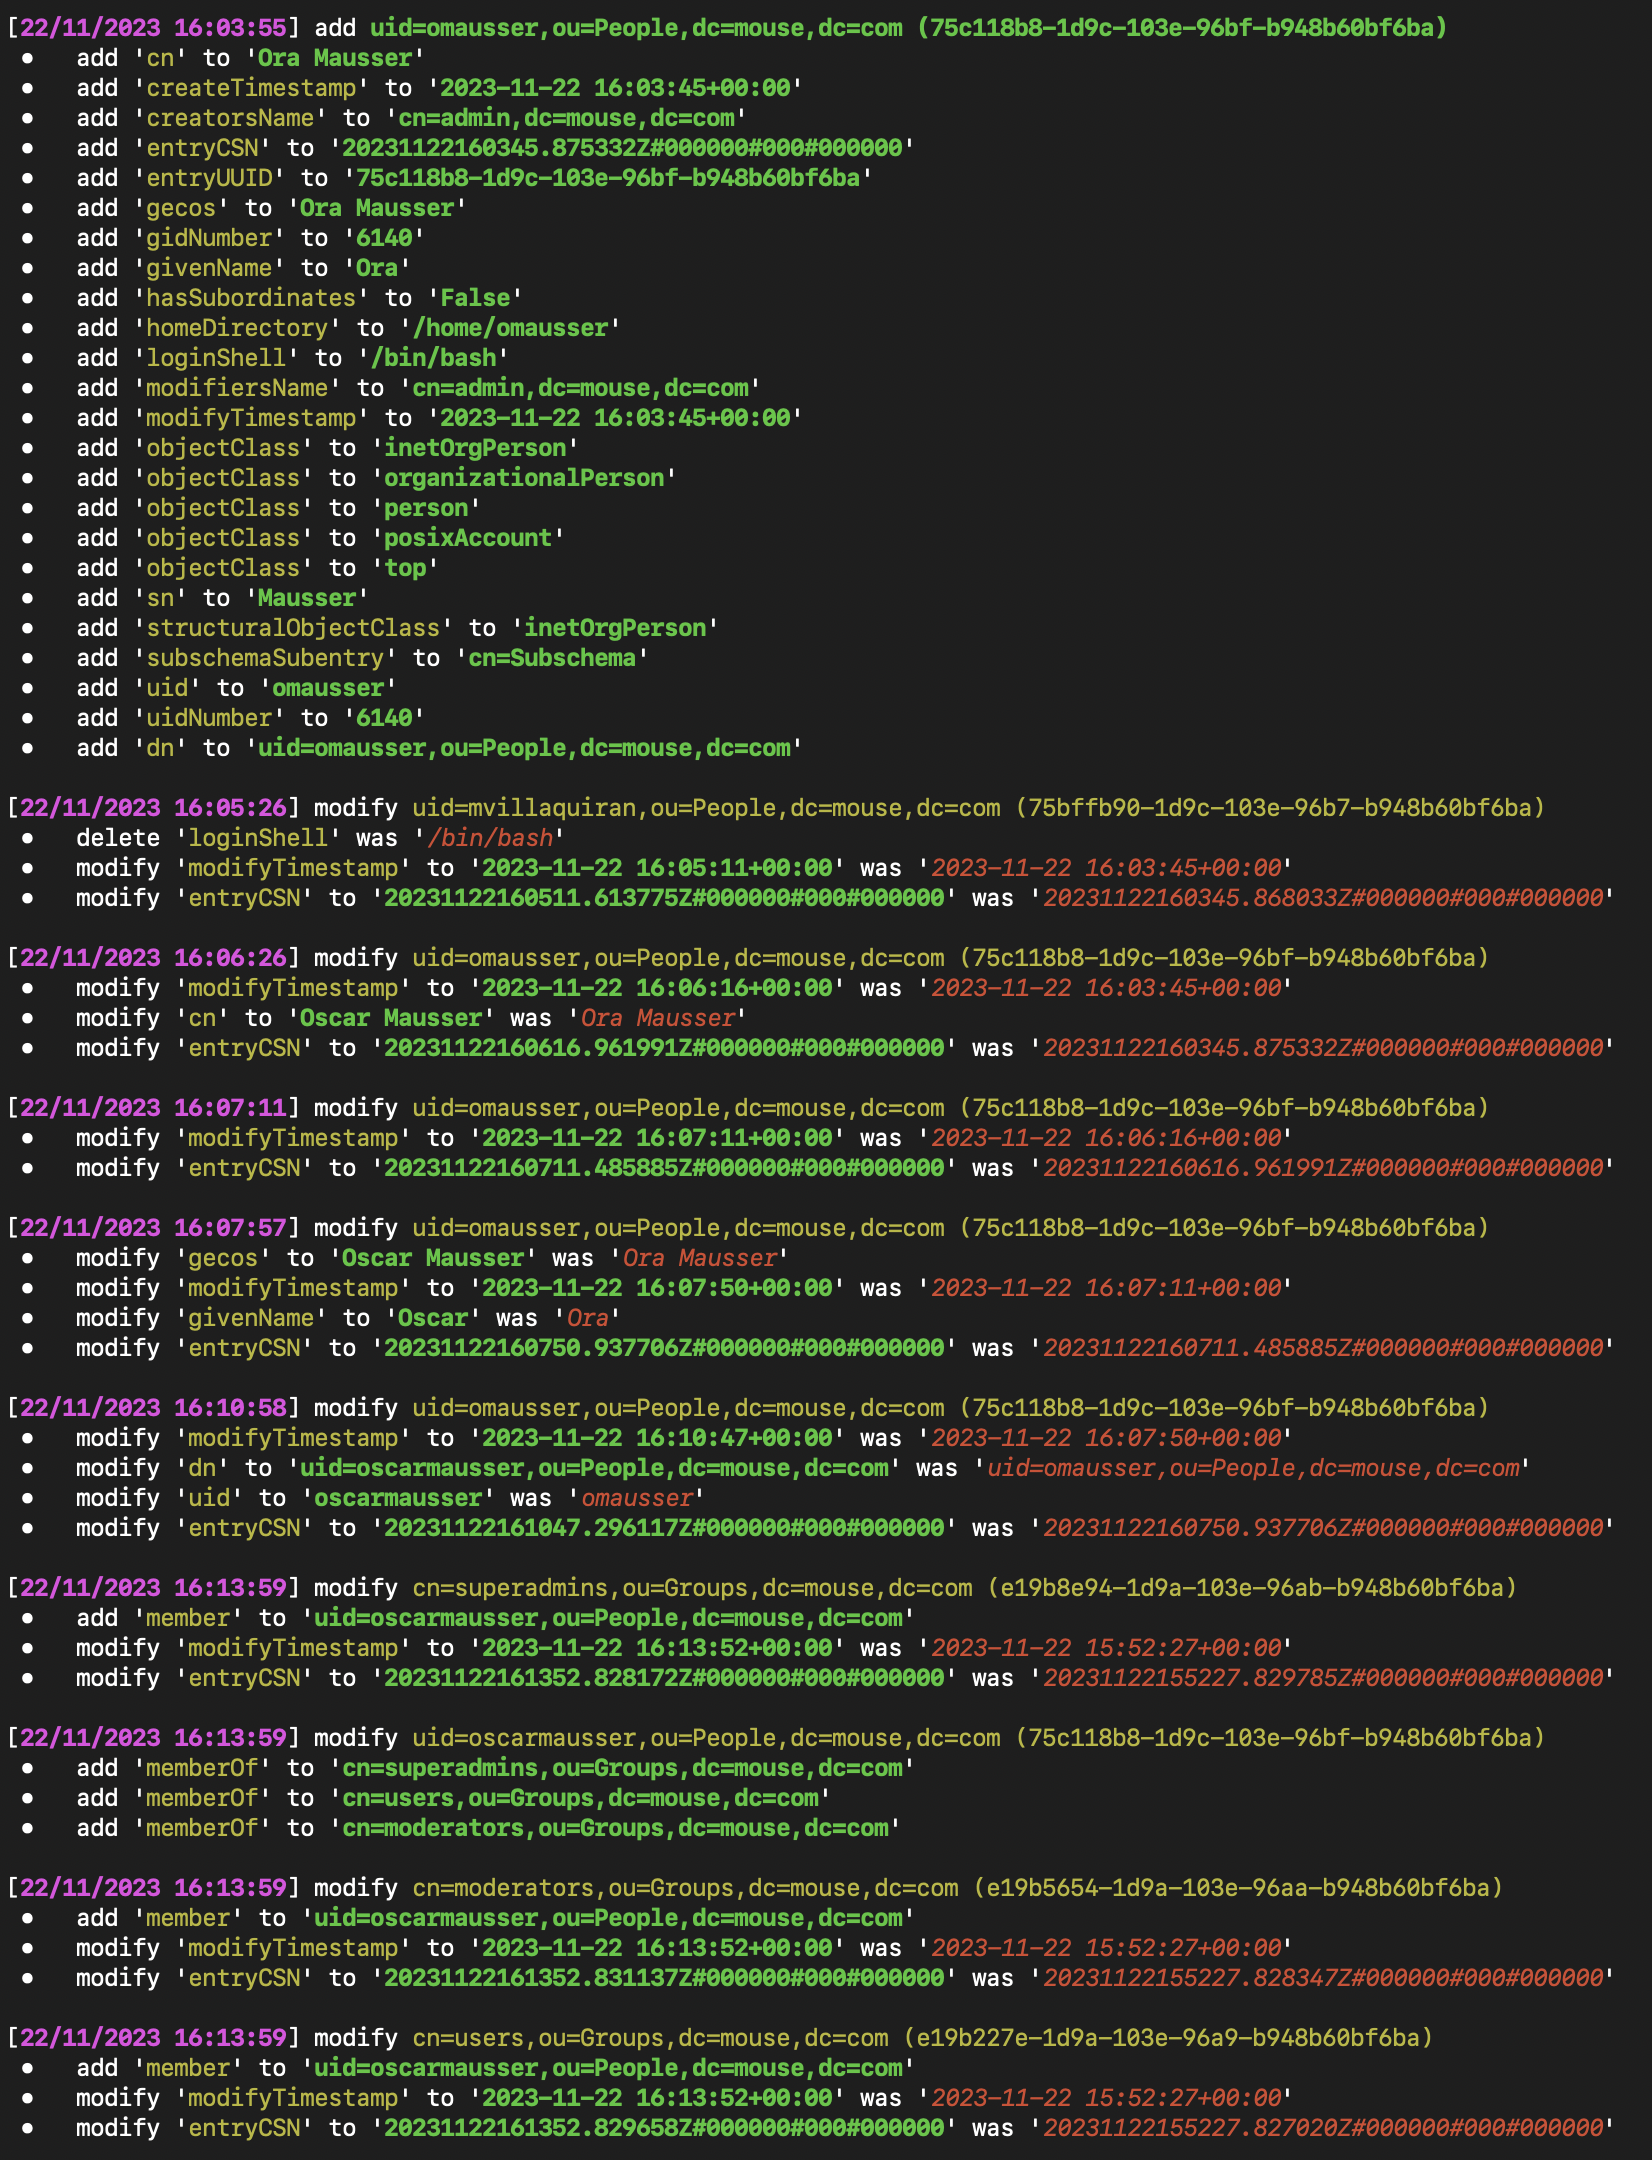 megamansec/ldap-monitoring-watchdog
LDAP Watchdog: A real-time linux-compatible LDAP monitoring tool for detecting directory changes, providing visibility into additions, modifications,…
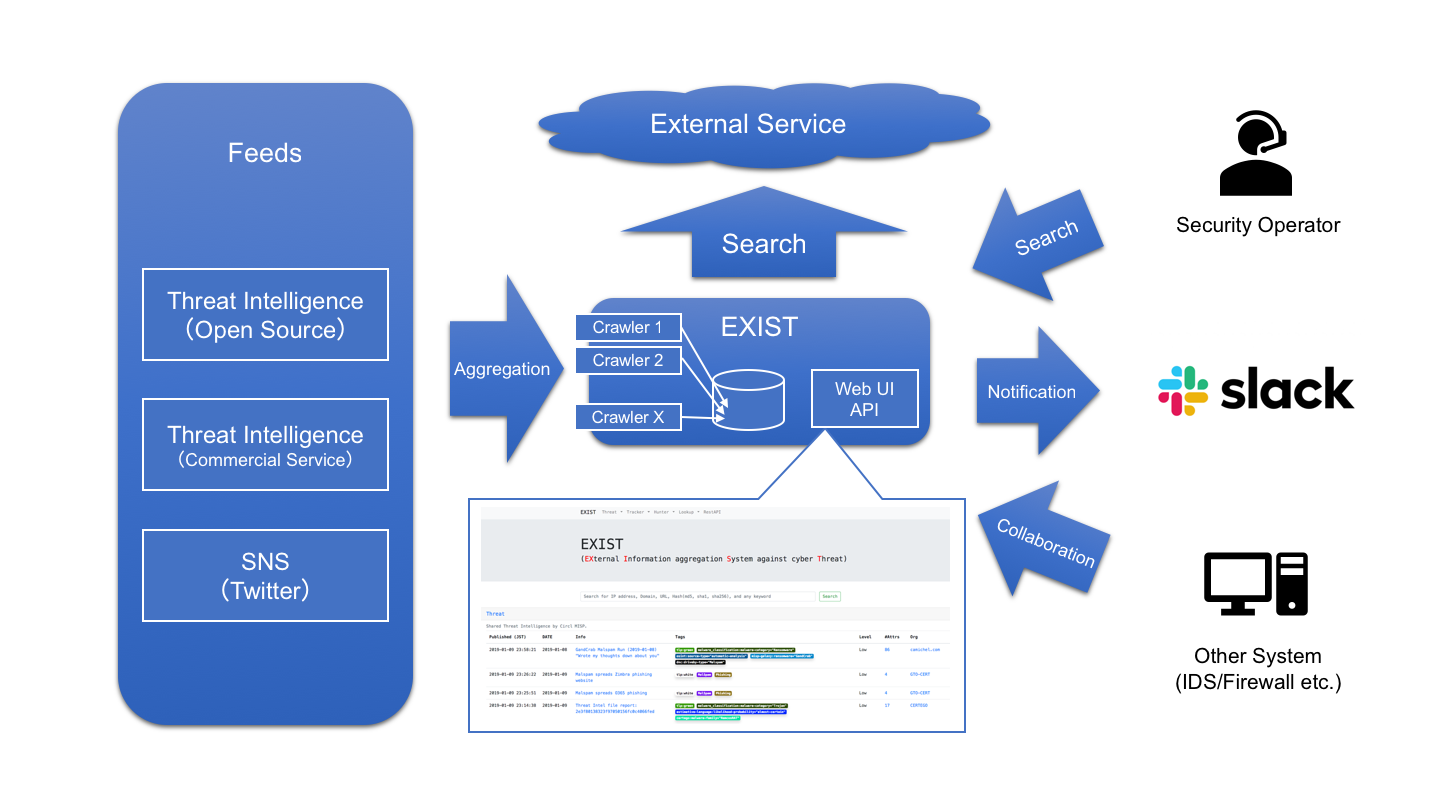 nict-csl/exist
EXIST is a web application for aggregating and analyzing cyber threat intelligence.
 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 0x0v1/audix
Audix is a PowerShell tool to quickly configure the Windows Event Audit Policies for security monitoring
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
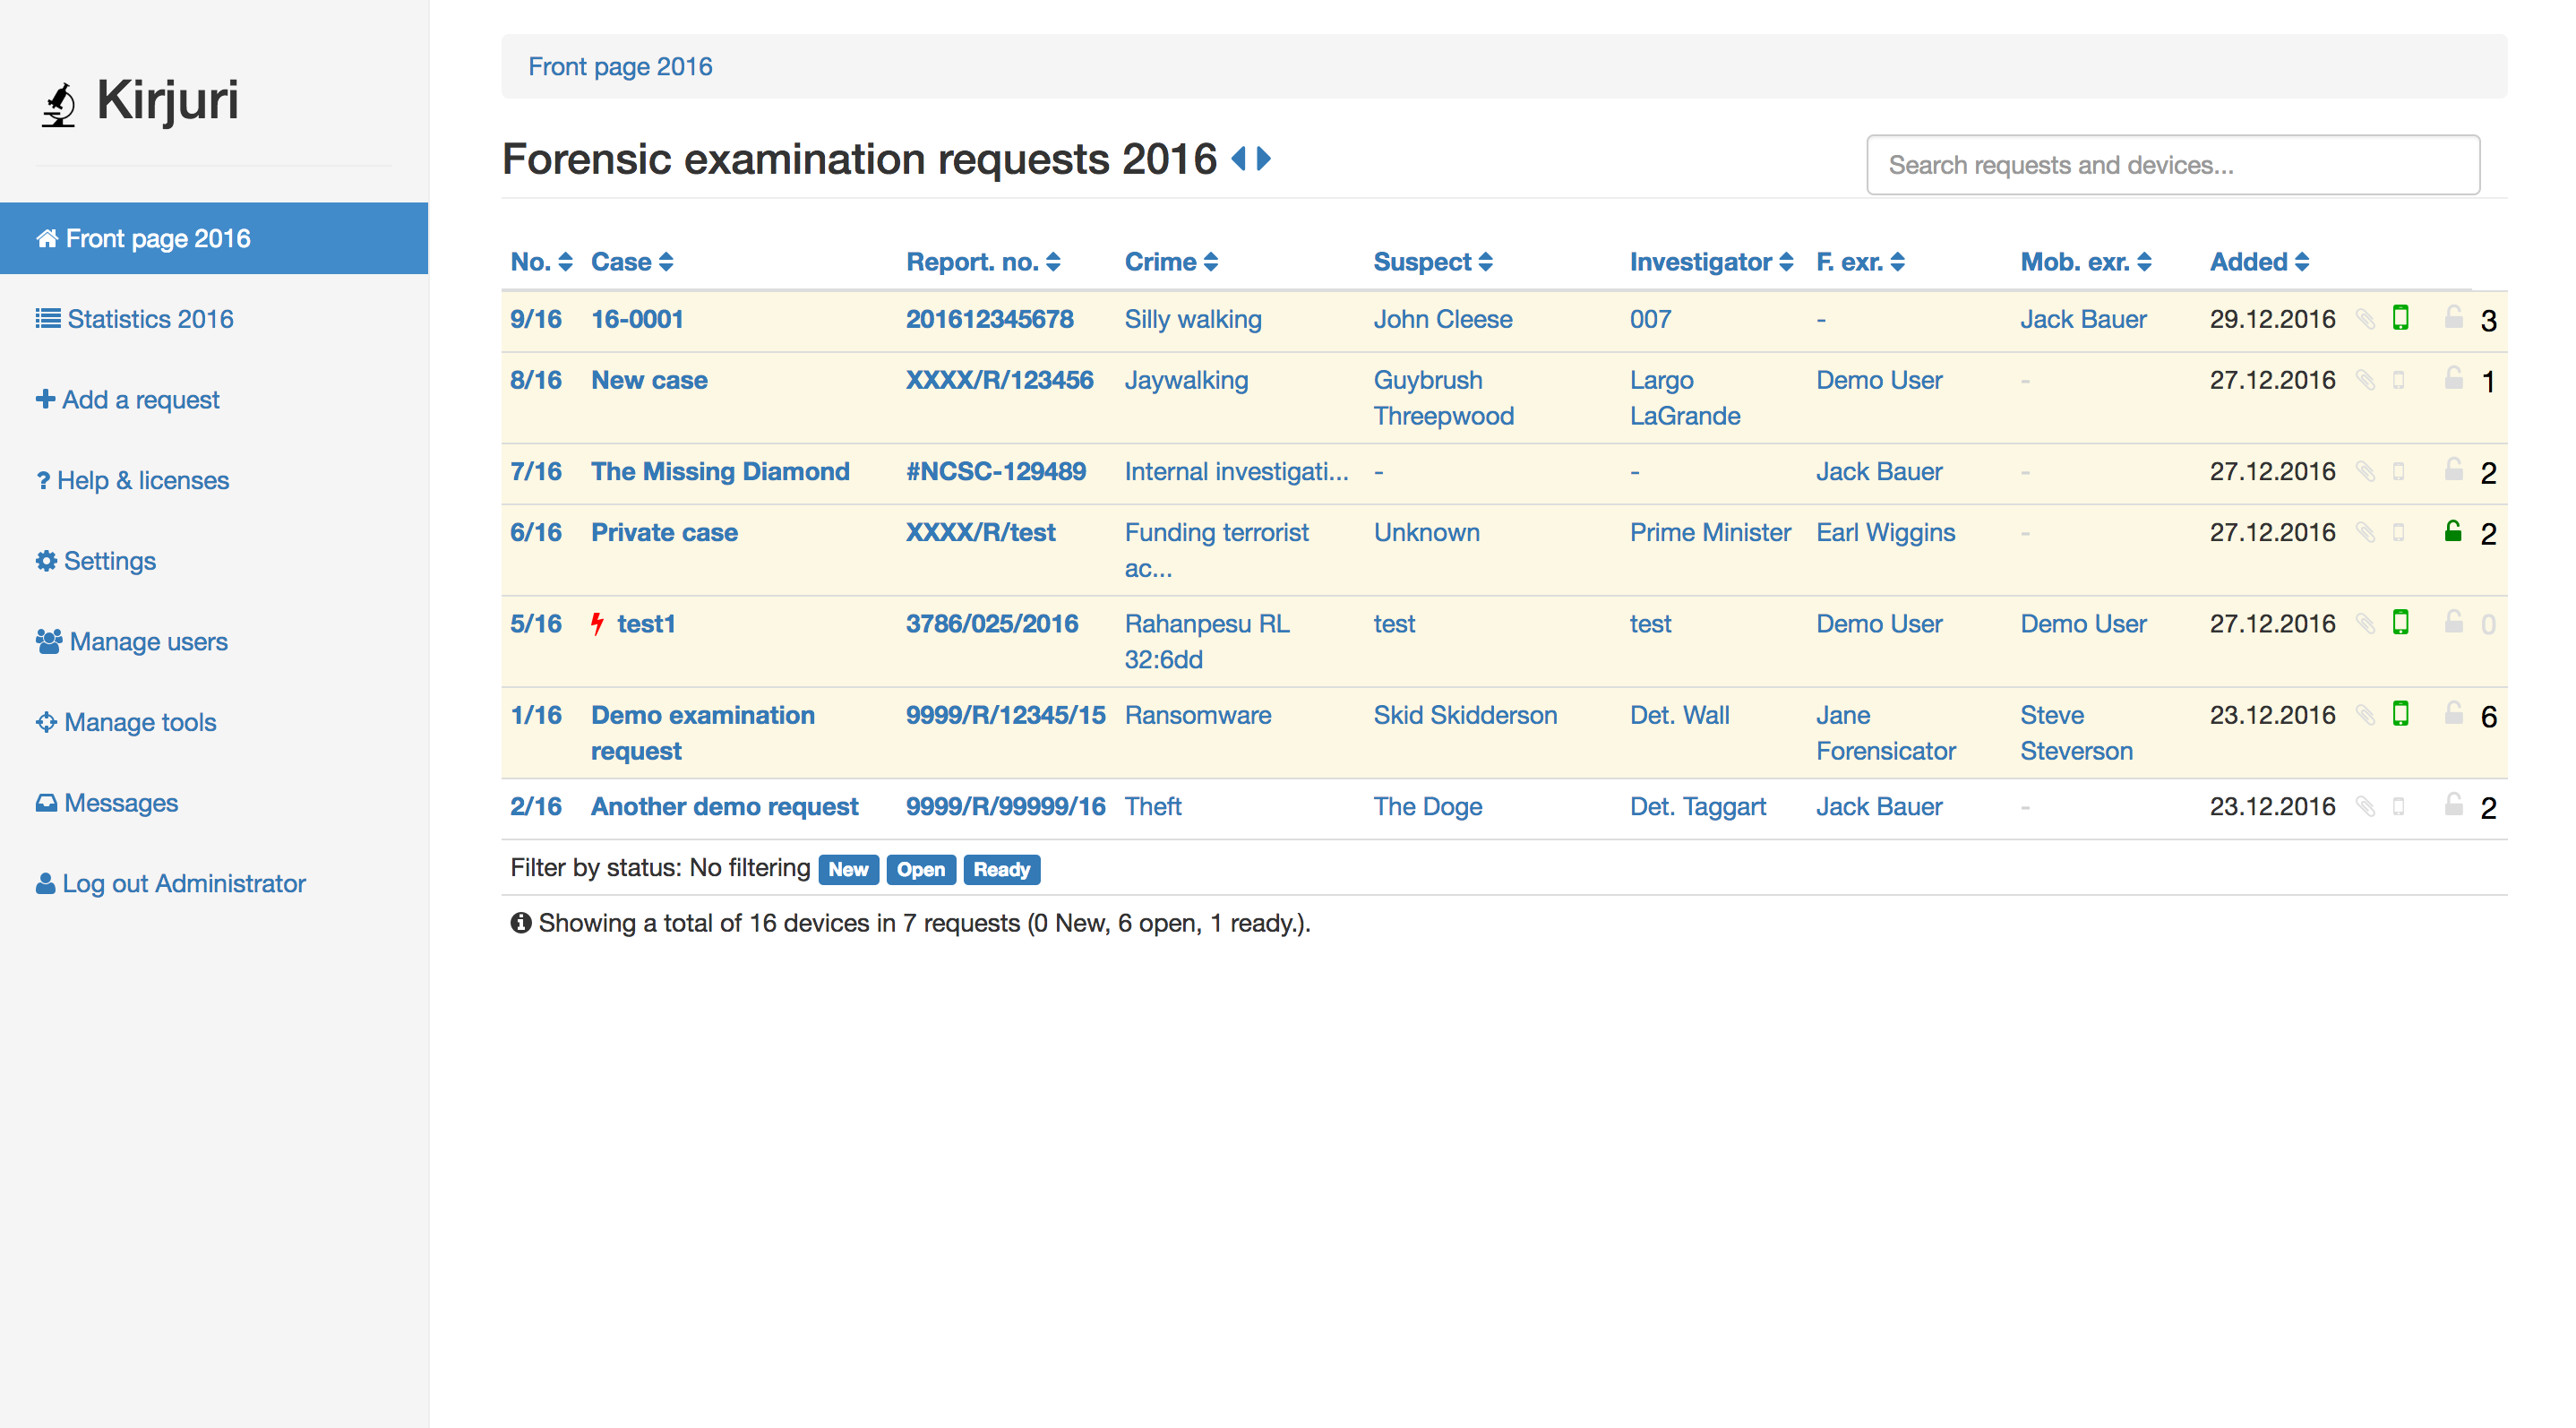 anttikurittu/kirjuri
Kirjuri is a web application for managing cases and physical forensic evidence items.
 simonis/log4jpatch
Deploys an agent to fix CVE-2021-44228 (Log4j RCE vulnerability) in a running JVM process
 cert-lv/exchange_webshell_detection
Detect webshells dropped on Microsoft Exchange servers exploited through "proxylogon" group of vulnerabilites (CVE-2021-26855, CVE-2021-26857,…
 mandiant/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 alexverboon/psmdatp
PowerShell Module for managing Microsoft Defender Advanced Threat Protection
 mandiant/citrix-ioc-scanner-cve-2023-3519
Bash-based scanner detecting indicators of compromise from CVE-2023-3519 exploitation on Citrix ADC appliances, supporting live and forensic image…
 deadbits/yara-rules
Collection of YARA signatures from individual research
 stripe/log4j-remediation-tools
Tools for remediating the recent log4j2 RCE vulnerability (CVE-2021-44228)