#1
IR playbooks, triage, case management, evidence collection, and incident management tools.
Kitploit recommended
 notawful/cve-2017-0199-fix
Quick and dirty fix to OLE2 executing code via .hta
 opensourcesec/cirtkit
Tools for the Computer Incident Response Team :computer:
 504ensicslabs/damm
Differential Analysis of Malware in Memory
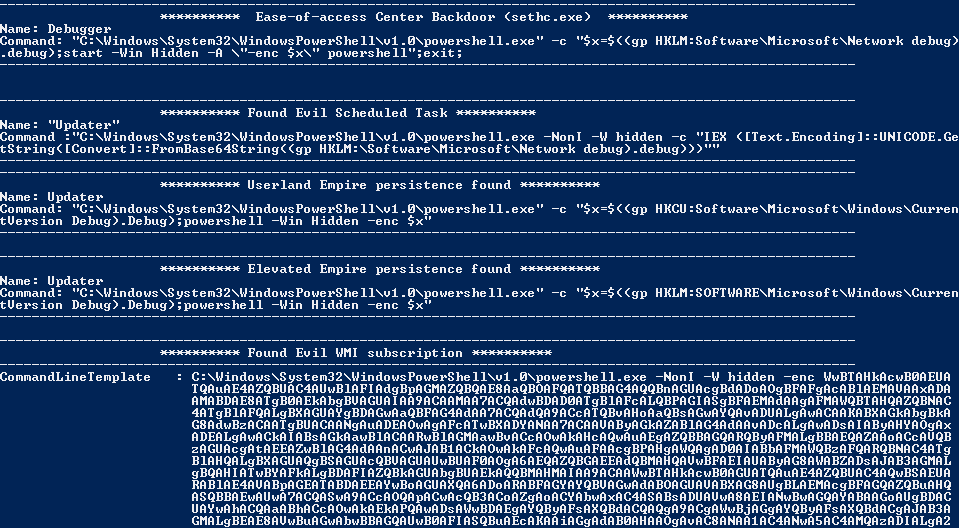 n00py/norknork
Powershell Empire Persistence finder
 nccgroup/ransomware-simulator
NCC Group Ransomware Simulator
 ajmartel/irtriage
Incident Response Triage - Windows Evidence Collection for Forensic Analysis
 dbrant/bios_memimage
RAM imaging utility.

 alphadelta/secure-desktop
Anti-keylogger/anti-rat application for Windows
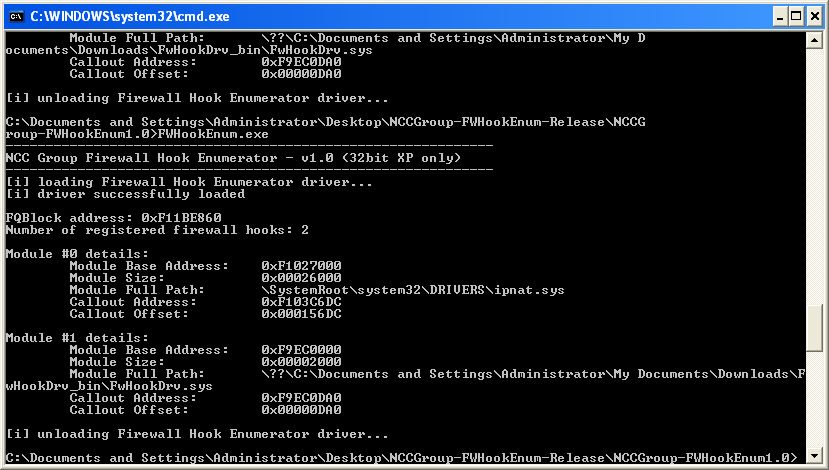 nccgroup/windowsfirewallhookdriverenumeration
Tools to enumerate Windows Firewall Hook Drivers on Windows 2000, XP and 2003
 helpsystems/embarcadero-workaround
This is a workaround for CVE-2014-0993 and CVE-2014-0994 that patches on memory without the need to recompile your vulnerable software. This is not…
 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces
 nccgroup/windowsjoblock
Windows Process Lockdown Tool using Job Objects
 tarunyadav/fix-cve-2013-2094
Generates portable SystemTap kernel modules to mitigate CVE-2013-2094 on Enterprise Linux systems, with automated build and deployment scripts for…