#1
IR playbooks, triage, case management, evidence collection, and incident management tools.
Kitploit recommended
 dropbox/securitybot
Distributed alerting for the masses!
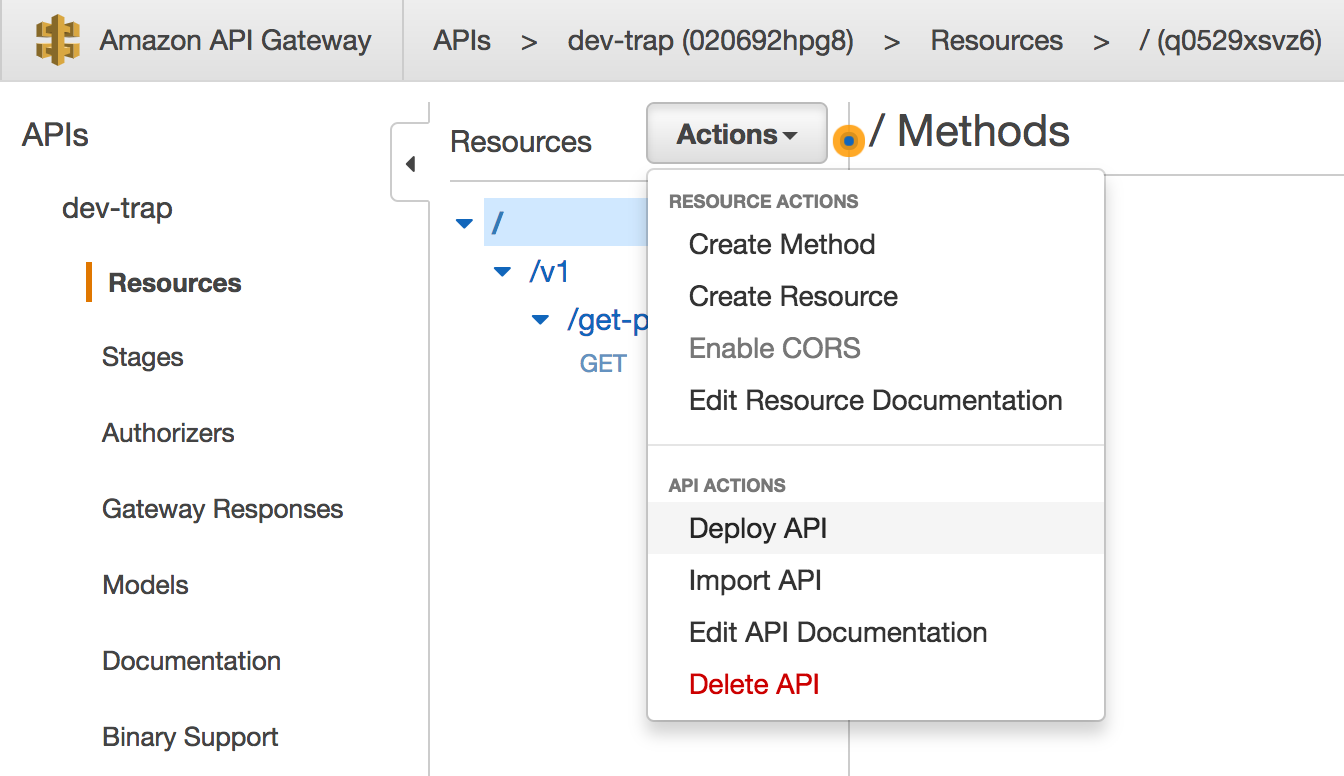 0x4d31/honeylambda
honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…
 cymmetria/micros_honeypot
MICROS Honeypot is a low interaction honeypot to detect CVE-2018-2636 in the Oracle Hospitality Simphony component of Oracle Hospitality Applications…
 withsecurelabs/volatility-plugins
Volatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
 aws-alchemy/squidmagic
analyze a web-based network traffic 🕶 to detect central command and control servers
 withsecurelabs/memory-carving-scripts
Scripts for extracting useful information from infected memory dumps
 hestat/drupal-check
Tool to dive Apache logs for evidence of exploitation of CVE-2018-7600
 bedazzlinghex/memory-analysis
Contains tools to perform malware and forensic analysis in Memory
 danielbohannon/invoke-dosfuscation
Cmd.exe Command Obfuscation Generator & Detection Test Harness
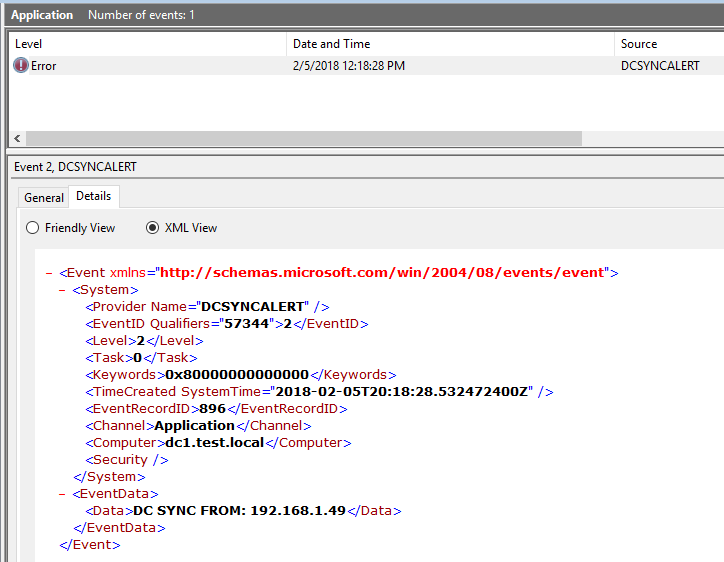 shellster/dcsyncmonitor
Monitors for DCSYNC and DCSHADOW attacks and create custom Windows Events for these events.
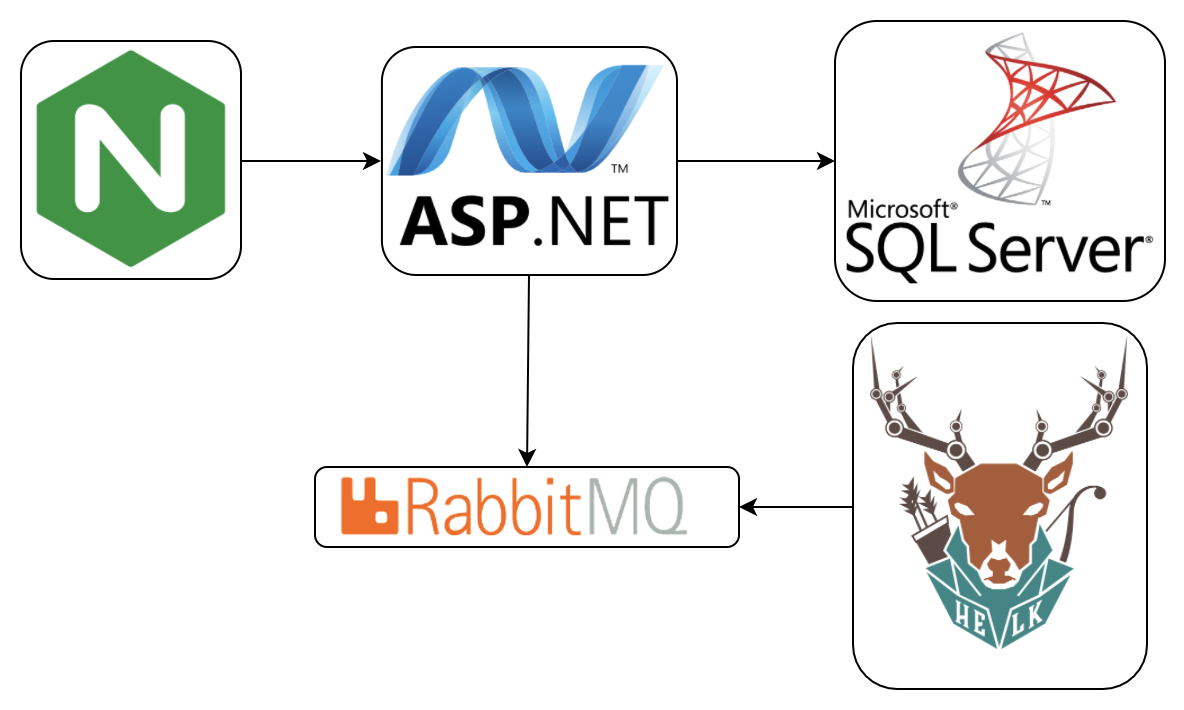 invoke-ir/ace
Automated, Collection, and Enrichment Platform
 jepaynemsft/weffles
Build a fast, free, and effective Threat Hunting/Incident Response Console with Windows Event Forwarding and PowerBI
 magoo/redteam-plan
Issues to consider when planning a red team exercise.
 homjxi0e/cve-2017-0290-
Exploit script for CVE-2017-0290 targeting Windows Defender on Windows 8.1/10, designed to disable or bypass the built-in antivirus protection.
 withsecurelabs/doublepulsar-detection-script
A python2 script for sweeping a network to find windows systems compromised with the DOUBLEPULSAR implant.
 jenkinsci-cert/security-218
Disables Jenkins CLI/Remoting subsystem as a mitigation against unauthenticated remote code execution vulnerabilities SECURITY-218 and SECURITY-360,…