#1
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
 deepfence/packetstreamer
⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐
 captaingeech42/ransomwatch
Ransomware leak site monitoring
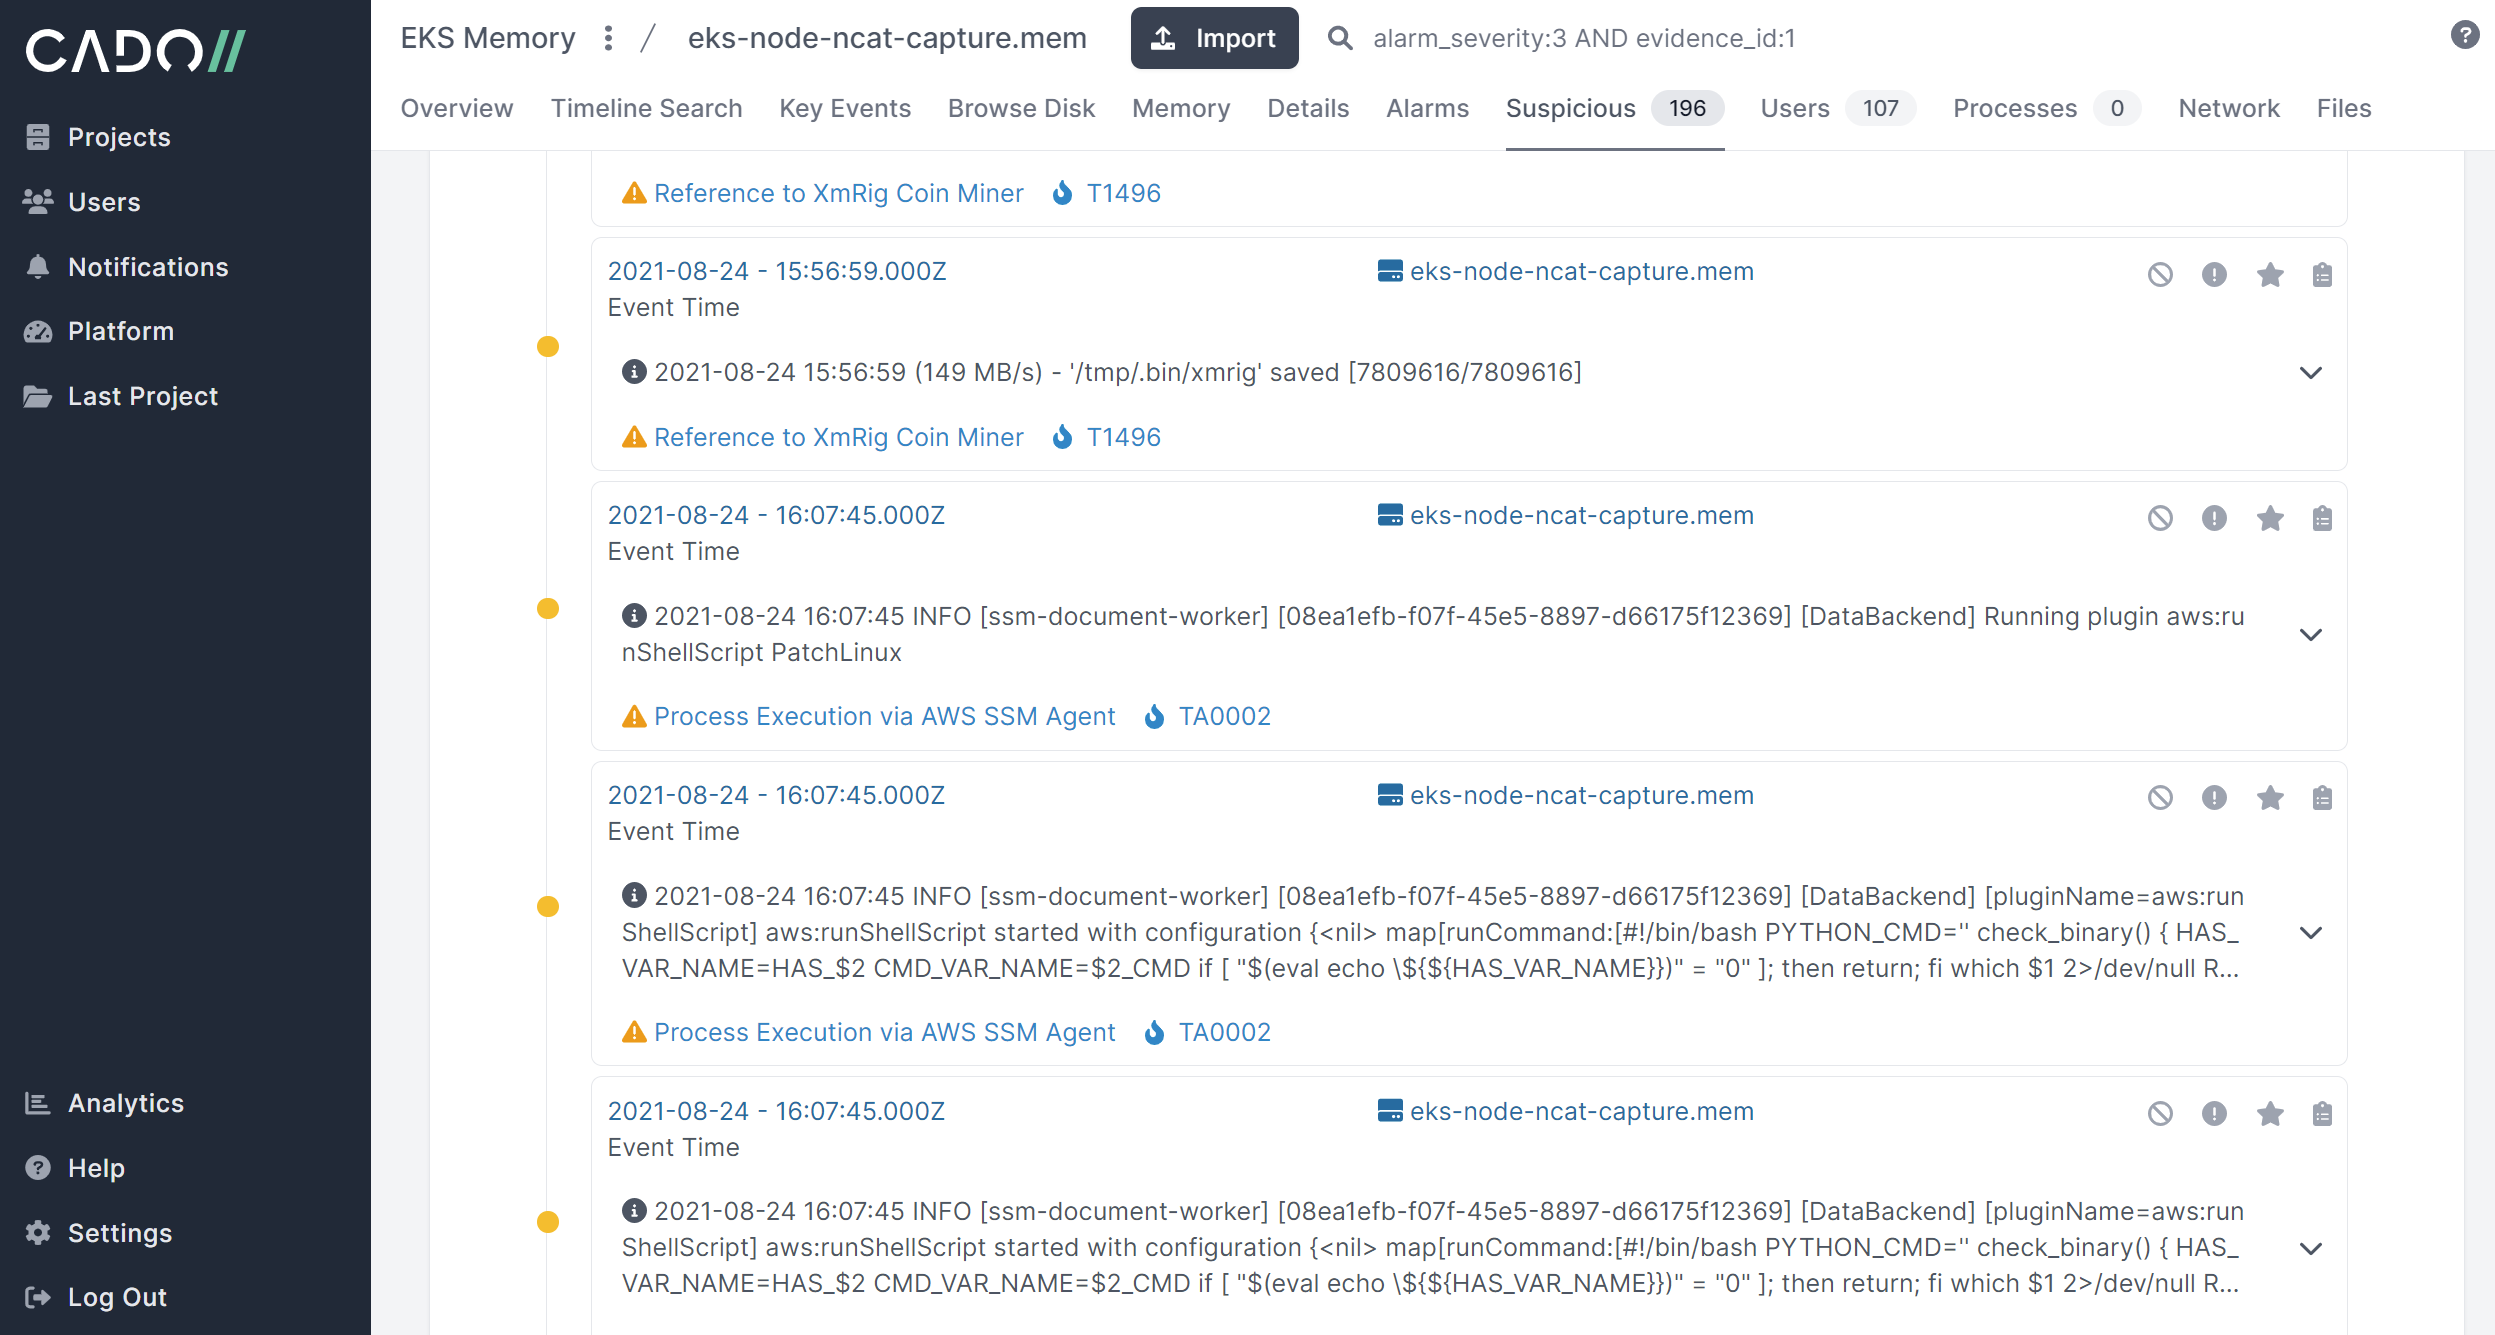 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
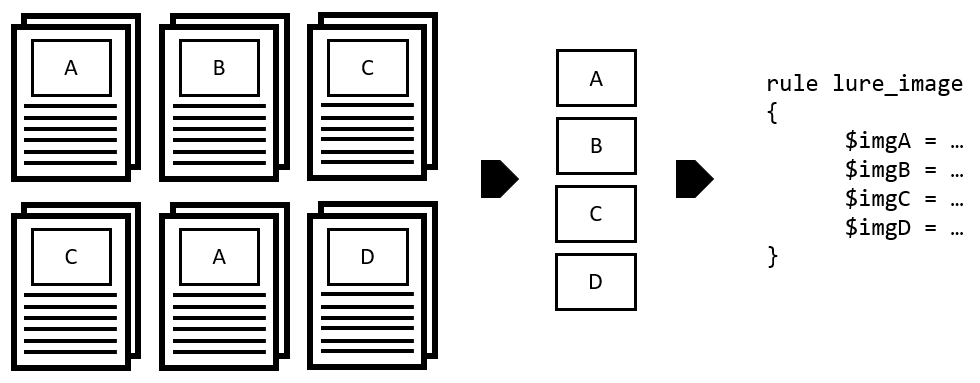 target/halogen
Automatically create YARA rules from malicious documents.
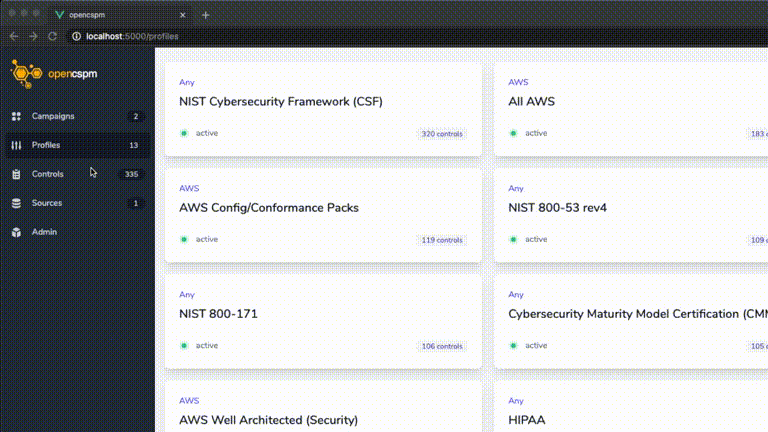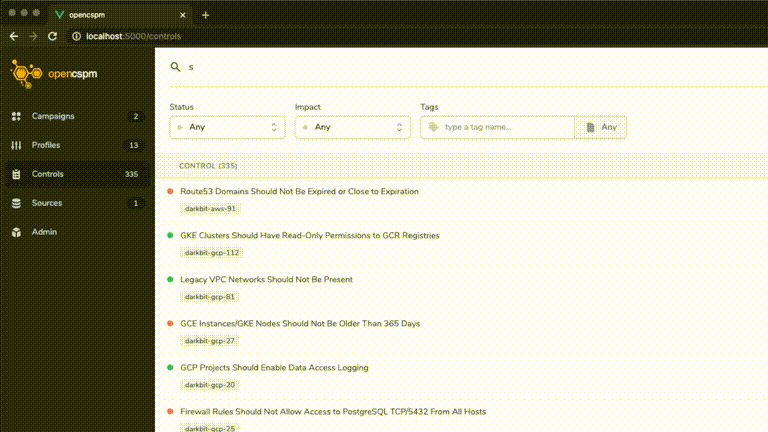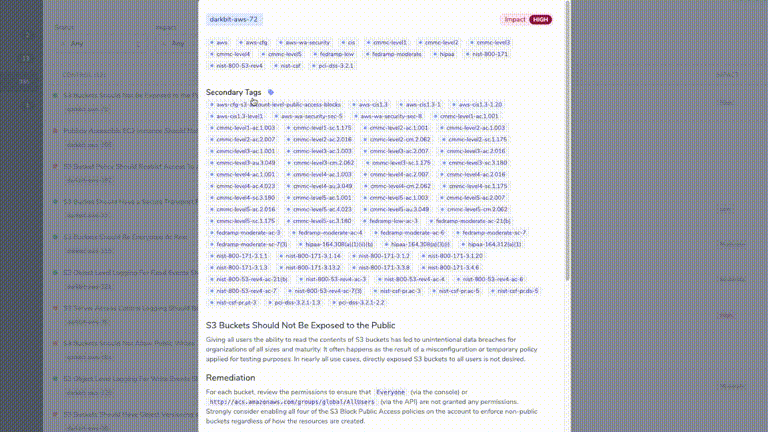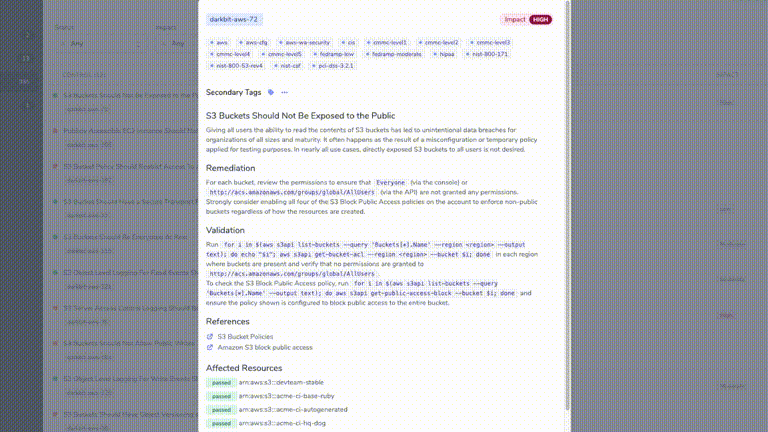 opencspm/opencspm
Open Cloud Security Posture Management Engine
 alexverboon/psmdatp
PowerShell Module for managing Microsoft Defender Advanced Threat Protection
 trailofbits/sinter
A user-mode application authorization system for MacOS written in Swift
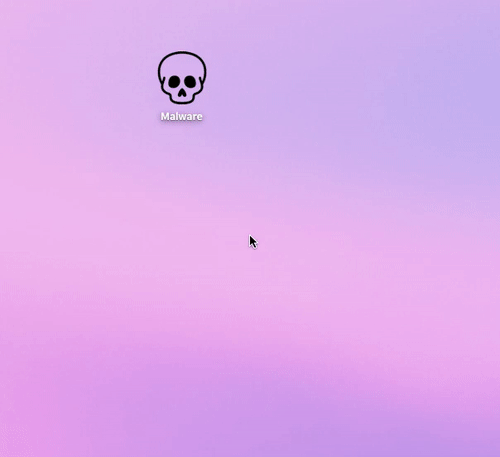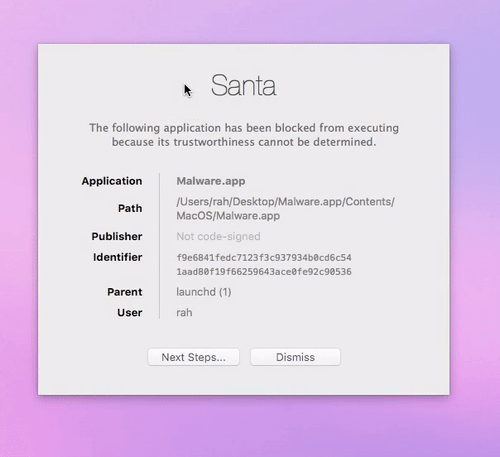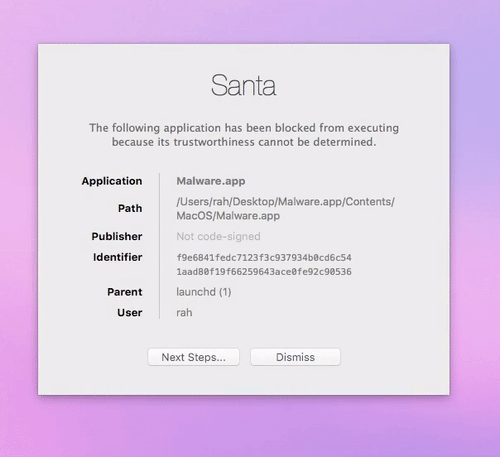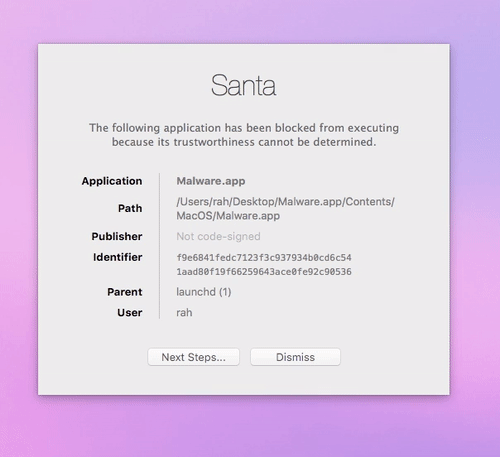 google/santa
A binary authorization and monitoring system for macOS
 cloudflare/mitmengine
A MITM (monster-in-the-middle) detection tool. Used to build MALCOLM:
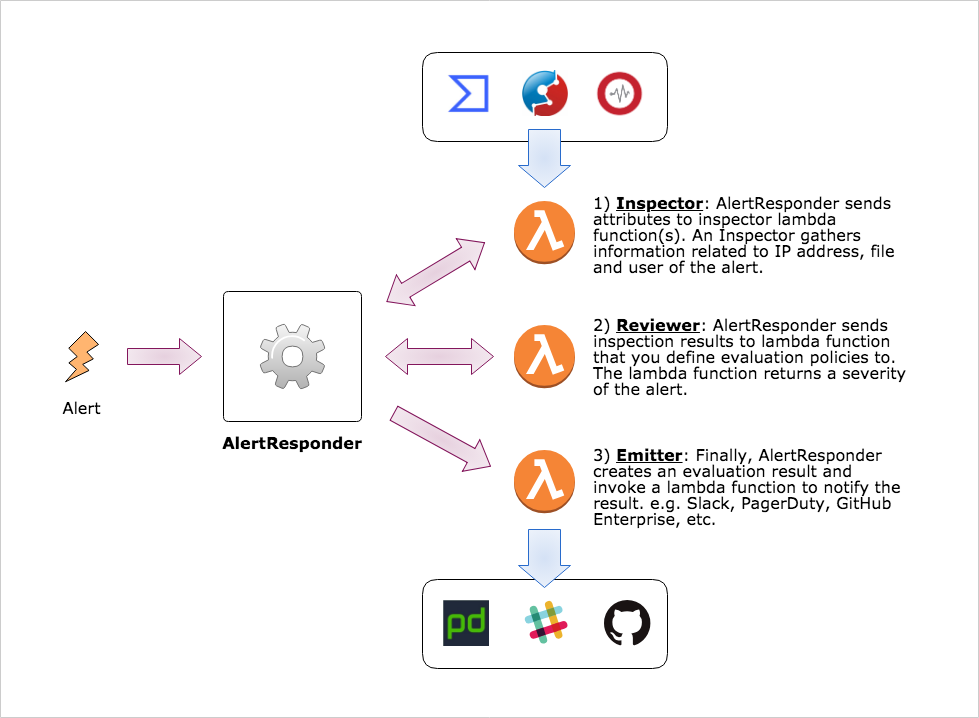 m-mizutani/alertresponder
Automatic security alert response framework by AWS Serverless Application Model
 ebwi11/agentsmith-hids
By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.
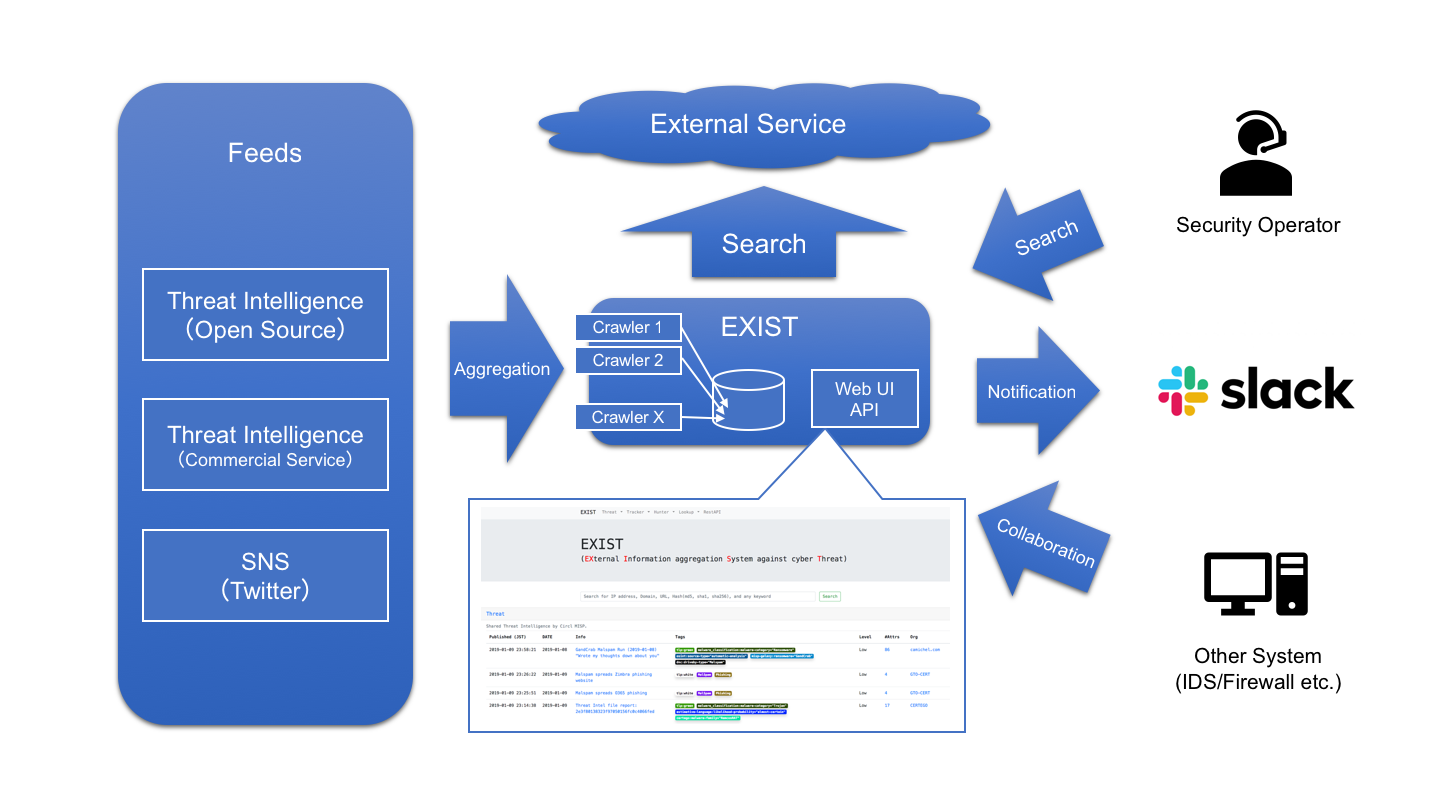 nict-csl/exist
EXIST is a web application for aggregating and analyzing cyber threat intelligence.
 defensepointsecurity/threat_note
DPS' Lightweight Investigation Notebook