#1
IR playbooks, triage, case management, evidence collection, and incident management tools.
Kitploit recommended
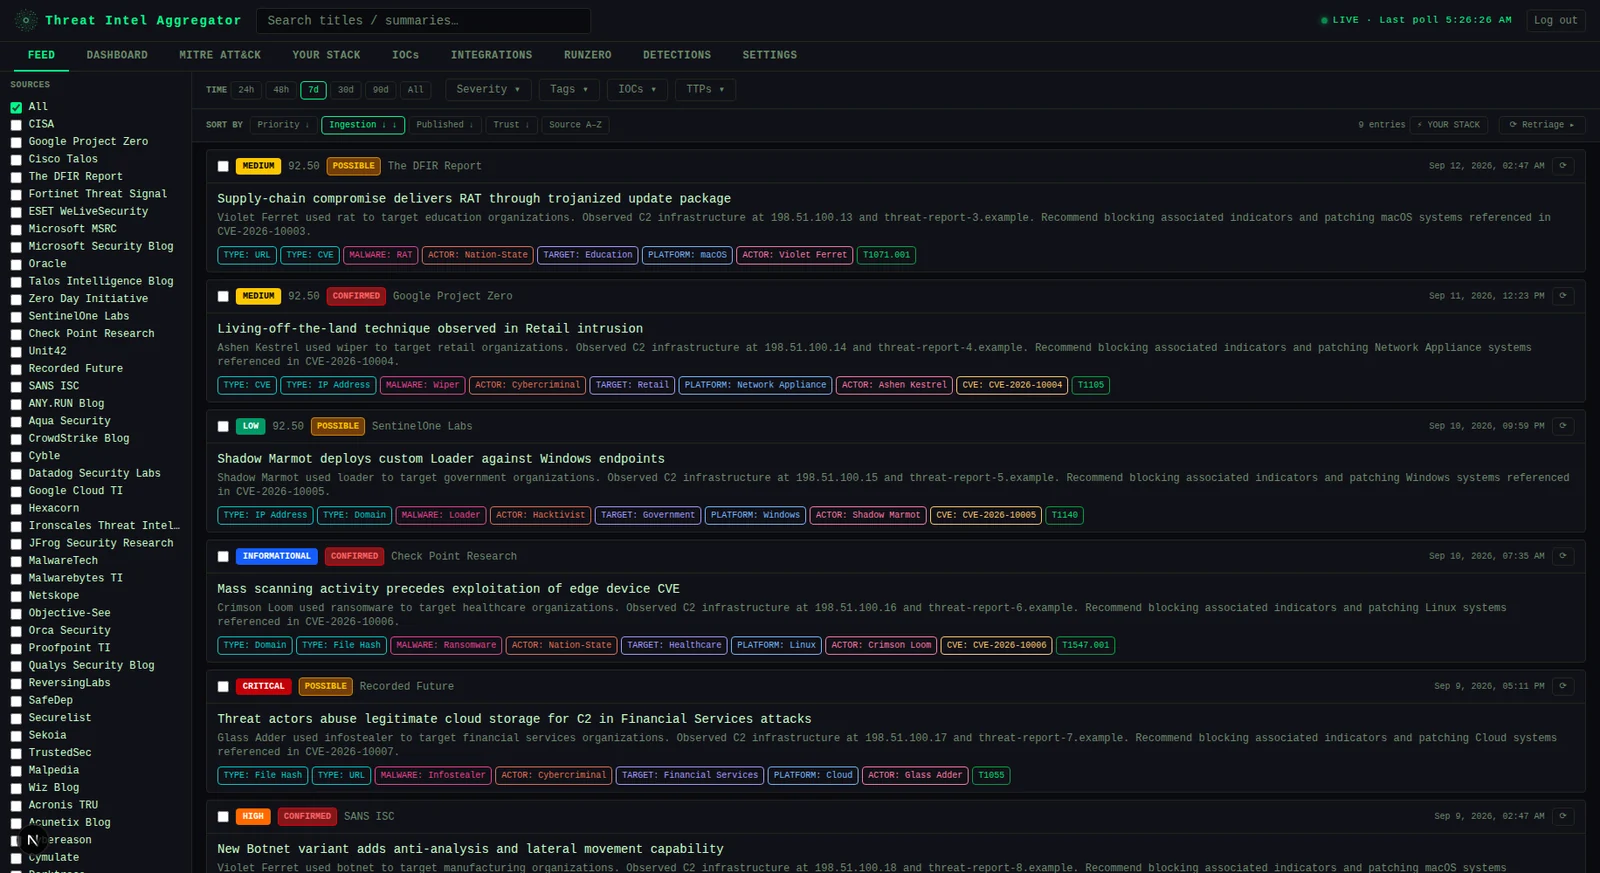
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 fevar54/cve-2026-76461-detection-kit-
Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…
 raniaemran/cve-2024-36401-security-simulator
Educational Python simulator modeling a fictional security incident inspired by CVE-2024-36401 to demonstrate vulnerability management, segmentation,…
 l1lf1ng3r/heartbleed-vulnerability-exploitation
hands on investigation of the heartbleed vulnerability (CVE-2014-0160).
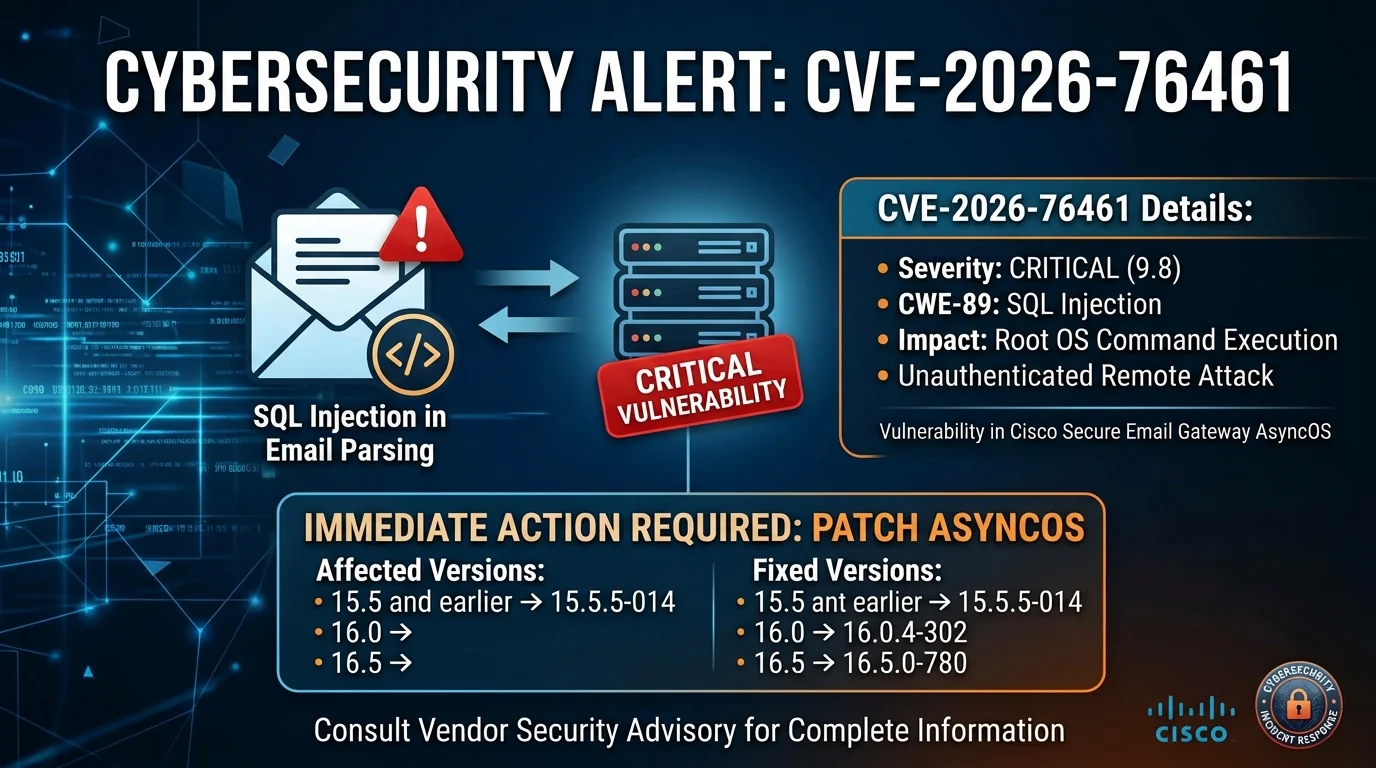 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 falconforceteam/falcondash
Azure workbook dashboard that visualizes and explores detection performance metrics, helping security teams measure and proactively maintain their…
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
 borsch-appreciator/soc235---atlassian-confluence-broken-access-control-0-day-cve-2023-22515
SOC analyst walkthrough triaging a Confluence CVE-2023-22515 broken access control exploitation attempt, covering log analysis, MITRE ATT&CK mapping,…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 het-p301204/afterlife
Revocation persistence detection lab: when the password reset succeeds but the attacker never leaves. Reproduces the Strapi CVE-2026-22706…
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…