
 #1
Tools for managing user identities, authentication, authorization, and access controls within systems and networks.
Kitploit recommended
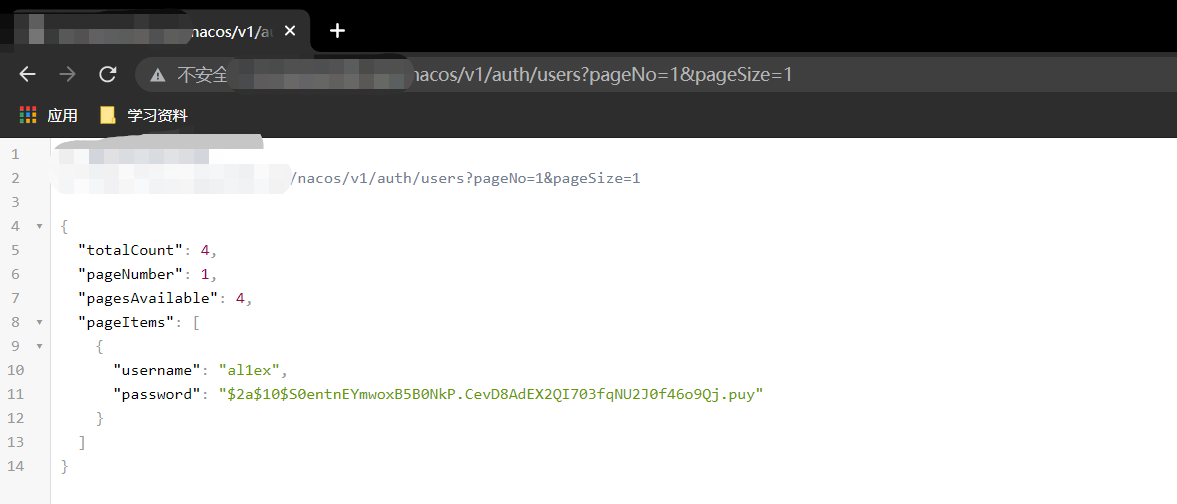
 al1ex/alibab-nacos-unauthorized-reset-pwd
Alibab-Nacos-Unauthorized-Reset PWD
 henry4e36/cve-2022-33174
Powertek PDU身份绕过
 hakaioffsec/cve-2026-16764
Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…
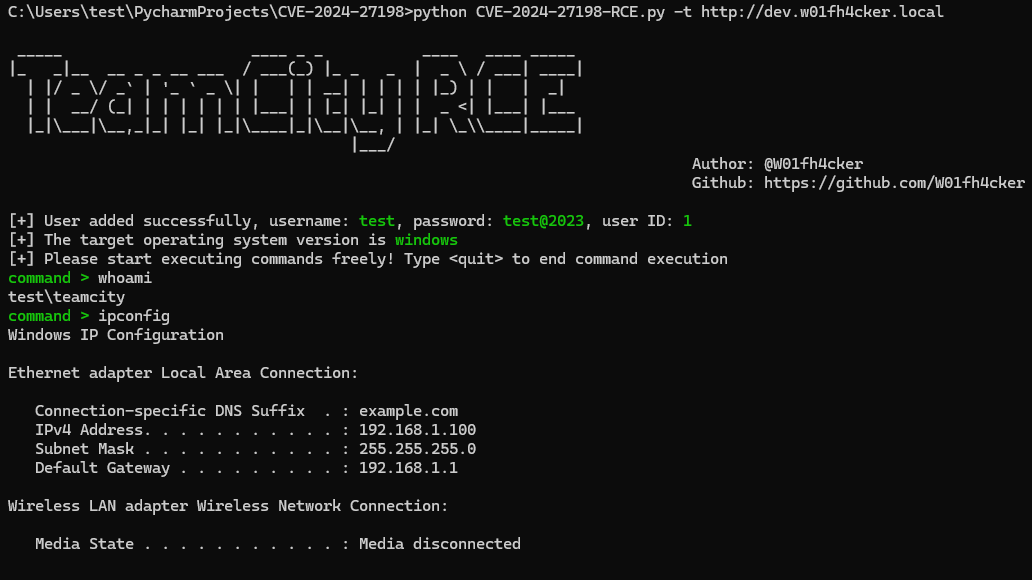 passwa11/cve-2024-27198-rce
Exploit for JetBrains TeamCity authentication bypass (CVE-2024-27198/27199) enabling remote code execution. Includes dork queries for asset discovery…
 murataydemir/cve-2020-14882
[CVE-2020-14882] Oracle WebLogic Server Authentication Bypass
 himash/cve-2018-19410-poc
Proof of concept for the vulnerability CVE-2018-19410
 gotr00t0day/cve-2022-1388
A remote code execution vulnerability exists in the iControl REST API feature of F5's BIG-IP product. An unauthenticated, remote attacker can exploit…
 fork-bombed/cve-2022-23131
CVE-2022-23131 Zabbix Server SAML authentication exploit
 abraxas/hyperswitch-payout-confirm-secret
Proof-of-concept and lab for a Hyperswitch payout confirm flaw: a dummy client_secret plus amount in POST /payouts/{id}/confirm raises the stored…
 jackson5sec/cve-2022-1040
This vulnerability allows an attacker to gain unauthorized access to the firewall management space by bypassing authentication
 artemy-ccrsky/cve-2024-41276
PIN-based Authentication Bypass vulnerability in Kaiten
 ricardojoserf/cve-2019-19033
CVE-2019-19033 description and scripts to check the vulnerability in Jalios JCMS 10 (Authentication Bypass)
 abraxas/superset-g3-v0-import-sql-plant
Proof-of-concept lab for an Apache Superset 6.1.0 authorization flaw where a Gamma dashboard editor plants dataset SQL via unversioned v0 dashboard…
 abdurahmon3236/cve-2024-38473
Proof-of-concept demonstrating an encoding flaw in Apache HTTP Server mod_proxy that can bypass authentication via crafted encoded URLs.
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 motikan2010/cve-2021-34646
CVE-2021-34646 PoC
 bridgeralderson/cve-2026-58424
A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…
 strikoder-premium/cve-2026-29000-pac4j-jwt
CVE-2026-29000 PoC: pac4j-jwt PlainJWT-in-JWE authentication bypass.








