
 #1
Hardware security modules, TPM, secure enclave, and hardware trust tools.
Kitploit recommended
 bp2008/hikpasswordhelper
A tool which exploits a backdoor in Hikvision camera firmwares circa 2014-2016 to help the owner change a forgotten password.
 nccgroup/tpmgenie
TPM Genie is an I2C bus interposer for discrete Trusted Platform Modules
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 midstall/aegis
Open source FPGA silicon
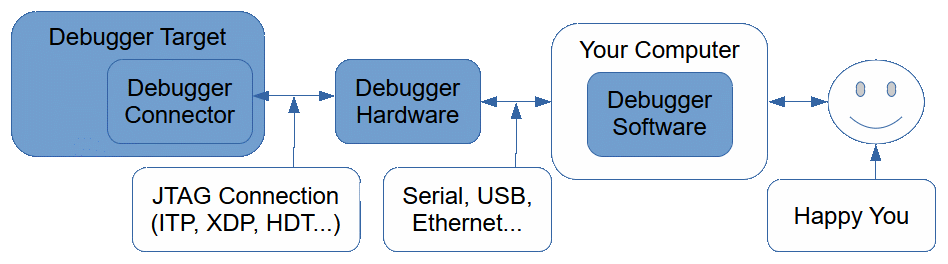 x86-jtag-open-research/x86-jtag-information
Documents Intel and AMD x86 JTAG debugger hardware, connectors, probe software, and target platforms for low-level system debugging and firmware…
 nevesnunes/z80-sans
OpenType font that disassembles Z80 instructions
 idov31/novahypervisor
Windows hypervisor for Intel x64: defensive host hypervisor for Windows designed to mitigate kernel-level attacks including BYOVD, compatible with…
 megamansec/gixy-next
Gixy-Next: NGINX Configuration Security Scanner & Performance Checker
 owasp/iot-security-verification-standard-isvs
OWASP IoT Security Verification Standard (ISVS)
 cmc-labo/tinyos-rtos
Ultra-lightweight RTOS for IoT with preemptive scheduling, TLS/DTLS, MQTT, CoAP, POSIX compatibility, and MPU-based memory protection. Kernel under…
 redrum0381/ataboy
ATAboy is a user-friendly bridge that allows legacy CHS only style IDE (PATA) hard drives to be connected to a modern computer as a standard USB Mass…
 denandz/lpc_sniffer_tpm
A low pin count sniffer for ICEStick - targeting TPM chips
 schumilo/vusbf
A QEMU/KVM-based USB fuzzing framework that finds device-driver bugs via reproducible VM execution, multiprocessing, and XML testcase generation.
 scriptingxss/embedos
EmbedOS - Embedded security testing virtual machine
 alfarom256/cve-2022-3699
Lenovo Diagnostics Driver EoP - Arbitrary R/W
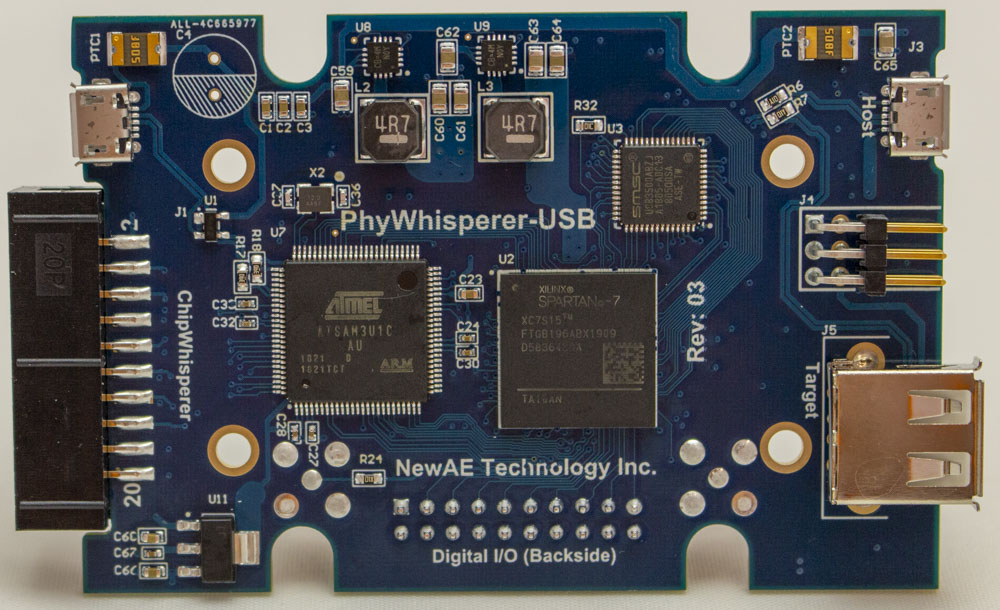 newaetech/phywhispererusb
PhyWhisperer-USB: Hardware USB Trigger
 raspberrypi/rp2350_hacking_challenge
Raspberry Pi RP2350 hacking challenge: extract a 128-bit OTP secret protected by secure boot and OTP lock, with setup scripts and firmware for Pico 2…
 syss-research/nrf24-playset
Software tools for Nordic Semiconductor nRF24-based devices like wireless keyboards, mice, and presenters








